
































The advent of artificial intelligence (AI) heralds a significant transformation, poised to redefine industries, human interactions, and problem-solving methodologies.
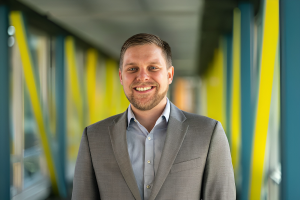
In an insightful conversation between Augustin Kurian, Editor-in-Chief of The Cyber Express, and Ryan Davis, Chief Information Security Officer at NS1, the profound implications and evolutionary trajectory of AI were brought to the forefront.
With over 15 years of experience in IT and security management, Davis elucidates that the unfolding AI revolution presents both challenges and abundant opportunities. AI is on track to replace or augment certain jobs within the next 5 to 15 years.
However, this transformation serves as a conduit to human progression, enabling us to tackle more intricate problems and streamline fundamental processes through technological advancements.
At its core, AI revolves around pattern recognition—utilizing algorithms designed to emulate and enhance human cognition and capabilities.
The imperative here is not to strive for perfection but rather to focus on progress, evolution, and the mitigation of inherent and lurking cyber risks. Delaying acceptance and adaptation to AI only serves to benefit malicious entities, propelling them forward in this technological race.

Davis’s journey into cybersecurity commenced at the tender age of three. Growing up in the 80s, his early exposure to computers fueled his curiosity, propelling him into the realms of exploration, understanding, and even circumvention of computer systems.
This initial dalliance with computers evolved into a deep-seated passion and unwavering commitment to cybersecurity. Ryan’s professional journey led him to prestigious institutions such as MIT Lincoln Laboratories, and his experience spans work with the Department of Defense, culminating in his current role at NS1.
Security, AI Revolution, and Risk Management
The significance of AI lies in its capacity to redefine industries, reminiscent of the Industrial Revolution and the advent of the internal combustion engine. Ryan posits that AI is the harbinger of a fundamental societal and human operations shift. The choice is stark—we either embrace or reject AI, and the repercussions are profound.
Deepfakes serve as a stark illustration of AI’s dual nature, capable of crafting convincing counterfeit content that blurs the line between reality and fiction. In the realm of security, the decision boils down to embracing AI or courting failure by turning a blind eye to its existence.
AI integration is an inevitability, demanding a balanced approach from security experts who must continuously assess the associated risks and rewards. The stance on AI is not fixed; it evolves in tandem with the ever-changing technological landscape.
Davis underscores that his primary mission is risk mitigation. With AI permeating our technological landscape, the strategy is to establish guardrails. This involves setting expectations and protocols for AI utilization, safeguarding intellectual property rights, and fortifying against vulnerabilities.
It’s about charting a structured and secure course that aligns with human behavior while enabling the safe harnessing of technology’s power without exacerbating inherent risks.
Davis, on the other hand, approaches new technologies with optimism, believing that despite their potential for harm, there is inherent good to be derived from them. He envisions an AI revolution unfolding in the next 5 to 15 years, during which entire job landscapes may be reshaped or augmented by AI.
This transformative period offers humanity unprecedented opportunities to address both new and longstanding challenges as technology delves deeper into fundamental issues.
He further highlighted that the deployment of AI not only promises innovative solutions but also demands a revaluation of our problem-solving approach. The convergence of human intelligence and technology could unlock uncharted potential for tackling challenges previously deemed insurmountable.
Yet, the monumental impact of AI comes with inherent risks and uncertainties. The ongoing rapid development and integration of AI across various sectors necessitate careful consideration of its ethical implications, the establishment of robust regulatory frameworks, and perhaps even the creation of new governance models.
AI in Critical Infrastructure & Security Concerns
The discussion delved deeper into the realm of critical infrastructure, an area where Davis boasts extensive experience. The focal point revolved around the protective measures now in place within the medical infrastructure.
Until recently, security was often an afterthought—a ‘nice-to-have’ rather than a necessity. However, the tides are changing. Security is now integral and indispensable, not just for governments but for everyone.
Davis stressed that regulatory bodies have come to recognize the paramount importance of security. With the introduction of regulations such as General Data Protection Regulation (GDPR) and Central Consumer Protection Authority (CCPA), there has been an intensified focus on safeguarding personal data.
However, the advent of AI necessitates a more profound examination within regulatory frameworks, particularly considering AI’s capacity to generate content that could compromise individual identities.
The potential misuse of AI-generated content raises crucial questions about personal identity and privacy, bringing to the forefront issues that current regulations have yet to address.
Furthermore, concerns linger regarding the deployment of AI in critical infrastructure, a domain that has received limited scrutiny concerning the implications of AI.
Reflection on AI Advancements and Misconceptions
Davis delved deeper into the conversation, shedding light on both its impressive strides and underlying pitfalls. Notably, he highlighted the swift progress in AI, citing innovations like ChatGPT as prime examples of technological advancement.
The AI’s capacity to craft entire lesson plans serves as a testament to its transformative potential. However, nestled within these technological marvels are fallacies that beckon caution. A society that leans heavily on AI for information and decision-making may encounter formidable challenges if these AI systems churn out biased or factually incorrect data.
Davis’s reflections extend beyond the confines of AI itself, drawing intriguing parallels with the evolution of Wikipedia during the late ’90s and early 2000s. During its nascent stages, Wikipedia faced skepticism primarily due to its open-source nature.
Over time, however, the platform adopted governance structures, trusted editors, and rigorous fact-checking mechanisms, ultimately earning credibility among its users. In stark contrast, AI currently lacks such robust governance, resulting in a lingering cloud of mistrust and skepticism that hampers its seamless integration into society.
Navigating the Future: AI Governance and Industry Standards
As the conversation progressed, Davis underscored the urgent need for the industry to set standards and expectations to govern the use of AI, especially in critical infrastructure. Given the slow-paced evolution of government regulations, industries should proactively define operating standards and agree upon the ethical use of AI.
Davis highlighted the pressing need for government interventions and regulations surrounding Artificial Intelligence (AI). He noted that it’s high time for government bodies to institute regulations around AI, echoing the sentiments of companies like OpenAI, which recently advocated for policies to govern AI development and utilization.
In addition, Davis pointed out the crucial significance of the ongoing dialogue about AI regulation, highlighting the fact that even CEOs have testified before Congress about its urgency. Nevertheless, he expressed deep concerns about the limited understanding of the technology exhibited by many politicians.
Davis emphasized that industries and cybersecurity professionals must take the lead in shaping the discourse on regulatory frameworks due to their familiarity with the potential risks associated with emerging technologies.
Drawing parallels with previous revolutionary technological advancements, Davis recounted the historical shifts in computing, from mainframes to distributed computing, and reflected on the cyclical nature of technological progress.
He underlined that the experiences of security professionals offer invaluable insights into proactively identifying and mitigating potential pitfalls associated with this groundbreaking technology.
Ransomware: Organizational Structures, Reputation, and Trust
Turning our focus to a critical facet of cybersecurity, Davis delves into the evolving reputation and organizational frameworks of ransomware groups. He highlights a notable trend where these criminal syndicates are gaining recognition for their reliability in promptly releasing data once the ransom is met.
Davis points out the intriguing shift in trust dynamics, with businesses increasingly inclined to comply with ransom demands, placing faith in the “reliability” of these unlawful organizations. Notably, some affected companies seek advice from previous victims, often learning that the transactions were straightforward, with data returned upon payment.
This emerging landscape, where trust is bestowed upon criminal entities, presents a complex challenge. Companies often perceive payment as the quickest resolution to such predicaments. However, Davis contends that this problem is not new; it has persistently plagued the digital realm. He references initiatives like the ‘No More Ransom’ project, aimed at curbing the ransomware epidemic by discouraging ransom payments.
Davis underscores the need to undermine the profitability of ransomware as a business model. He calls for society to recognize the intricacies of computer security and acknowledge that security breaches are inevitable, ranging from basic phishing emails to sophisticated state-sponsored attacks.
Ransomware Profitability and Cybersecurity Insurance
Expanding on the ransomware discussion, Davis emphasizes its lucrative nature and how it has led companies to view paying ransoms as the quickest remedy. He notes that cybersecurity insurance companies are taking proactive measures by incorporating specific provisions for ransomware and establishing prerequisites for coverage.
To render ransomware an ineffective business model, Davis argues for a collective resolution to resist ransom demands. He stresses the importance of companies openly addressing their security vulnerabilities rather than concealing them, as every company is susceptible to breaches at some point.
Davis highlights the alarming rise in ransomware attacks, fuelling the growth of an illicit industry. Companies that acquiesce to monetary demands only perpetuate this cycle of attacks. This situation calls for a paradigm shift in how we approach ransomware, marked by an urgent need for awareness, resilience, and collaborative efforts against these criminal actors.
Government Intervention and AI Regulation
Davis underlines the pressing need for government intervention and regulation in the realm of AI. He aligns his perspective with that of OpenAI, which took the bold step of releasing its technology early to catalyze policy development and legislative action around these potent technologies.
Davis emphasizes the pivotal role of AI organizations in shaping conversations about regulations, citing OpenAI’s CEO testifying before Congress on the necessity and implications of AI regulation.
Davis expresses concern about the limited technological expertise of politicians and underscores the importance of industry professionals leading the way in fostering understanding and shaping policy.
He posits that security professionals, well-aware of the dangers posed by emerging technologies, must take a proactive role in these discussions to formulate pre-emptive measures against potential threats. Davis likens the transformative impact of AI to previous technological shifts and advocates for informed security measures to counter possible pitfalls.
The Paradox of Trustworthy Criminals
The conversation takes a deep dive into the enigmatic world of ransomware gangs and their unexpected reputation for reliability. Davis sheds light on the burgeoning organizational structures within the criminal underworld, where reputation reigns supreme.
Remarkably, companies now find themselves relying on the experiences of previous victims to gauge the trustworthiness of these criminal entities, creating a peculiar paradox where criminals are deemed dependable.
Contrary to the belief that ransomware is a mounting threat, Davis argues that it has persistently plagued the cybersecurity landscape. He points to the “No More Ransom” project, a collaborative effort aimed at combatting ransomware, as a potential solution to this enduring problem.
He underscores the imperative for victims to resist paying ransoms, as this only bolsters the ransomware operators’ business model.
Davis also delves into the importance of transparency and honesty when dealing with security breaches. He critiques attempts to obscure the details surrounding security incidents and urges companies to openly share their experiences, fostering collective learning and resilience within the industry.
He sheds light on the evolution of cyber insurance, noting its role in limiting liabilities and requiring evidence of protective measures.
The Evolution of Attack Surfaces and the Role of AI
Davis navigates the evolving terrain of attack surfaces and the pivotal role played by AI in this shifting landscape. He paints a vivid picture of algorithms being weaponized, advancing at a pace that often outstrips our capacity to detect and counteract them.
He emphasizes the pressing need for robust detection mechanisms, all the while highlighting the inherent challenges in distinguishing algorithm-generated content from human-created content.
Davis issues a stark warning about a future where viruses could evolve faster than our ability to define them, posing substantial challenges to established cybersecurity paradigms.
Nevertheless, he presents a balanced perspective, exploring the potential of harnessing AI for proactive defense mechanisms. He also shines a light on the ongoing race to employ AI for security, an arena where malevolent applications often precede benevolent ones.
In contemplating the inherent limitations of AI, Davis underscores the need to refine our approach to pattern recognition. In conclusion, he issues a resounding call to arms, urging us to fortify our defenses and continuously enhance our technologies, lest we allow malicious entities to perpetually outpace us.
AI Revolution: Paving for a Secure Future
In summary, Davis highlights AI’s potential in pattern recognition and its role in enhancing human capabilities. He emphasizes the need to strategically integrate AI into security measures, continually assessing risks.
Davis also discusses the changing perception of security in critical infrastructure, calling for updated regulations and resistance against ransomware attacks.
Davis underscores the importance of proactive collaboration, informed governance, and technology evolution in the AI-cybersecurity intersection. We must focus on ethical alignment, strong governance, and effective risk management. This discussion encourages stakeholders and regulators to shape a secure technological future collaboratively.





