
















• Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
The Cyber Express
  • MagazineDownload
  • Firewall Daily
    • All
    • Bug Bounty & Rewards
    • Dark Web News
    • Data Breach News
    • Hacker News
    • Ransomware News
    • Vulnerabilities
    weekly roundup

    The Cyber Express Weekly Roundup: FBI Blames North Korea for $6B Binance Hack, Hackers Turn Up the Heat on Europe’s Fridges and More

    Stockal cyberattack

    Stockal Confirms Unauthorized Trades in 13 Customer Accounts

    Alpine Linux servers

    Alpine Linux SSH Flaw Lets Attackers Log In Without a Password

    Queens Public Library ransomware attack

    Ransomware Just Took New York’s Queens Library Offline, and It’s Not the First

    Amadeus cybersecurity incident

    Airline Data Breach Widens as Singapore Airlines Reports 46,000 Affected Records

    refrigeration cyberattacks

    After Supermarket Freezers, Hackers Turn Up the Heat on France’s Blood Supply

    university supercomputer hacking

    Two Canadians Accused of Turning US University Supercomputers Into Crypto Miners

    investment fraud

    Europol Seizes 100+ Servers Running Fake Trading Platforms

    UTA cyberattack

    UTA Investigates Suspected Cyberattack After MachForms Service Disruption

    Trending Tags

    • blackbyte ransomware
    • Ransomware
    • lapsus$ ransomware
    • Apple
    • Apple vulnerability
  • Essentials
    • All
    • Compliance
    • Governance
    • Policy Updates
    • Regulations
    ASD Essentials

    The Essential Eight Is Being Replaced: What Australian Organisations Need to Know

    SICW 2026

    AI Is Now Fighting on Both Sides of the Cyber War, Singapore Warns

    Morocco cybersecurity strategy

    Morocco Flags AI Threats, Prioritizes Critical Infrastructure Defense

    European Police Chiefs Convention 2026

    Europe’s Police Chiefs Face Growing Threat of AI-Driven Crime

    AI service security

    Hackers Are Stealing AI Keys. The Cost Can Reach $600,000

    AI security risks

    Sam Altman at UN Security Council: 6 AI Security Risks the World Cannot Ignore

    AI-enabled cyber attacks

    AI Gives Hackers an Edge Defenders Still Can’t Match, NCSC Warns

    Fraudulent SIM cards

    India’s DoT Warns Citizens Over SIM Fraud and IMEI Tampering

    EU cybersecurity incidents

    EU Cybersecurity Response Hampered by Critical Information Gaps

    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
    • All
    • How to
    • What is
    Infostealer Intelligence

    The 2026 Infostealer Intelligence Shortlist: Top 10 Vendors Security Teams Should Know

    Google Chrome

    How to Remove Saved Passwords From Google Chrome (And Why You Should)

    DPDP Rules, Cyble, DPDP Act, Cyble Vantage

    How Cyble’s Front-Row Vantage Can Help You in Complying to India’s DPDP Act

    Cybersecurity Countries

    The Top 8 Countries Leading the Cyber Defense Race in 2025

    link building

    The Link Building Secrets Your Competitors Don’t Want You to Know

    Supply Chain Attack

    Supply Chain Resilience and Physical Security: Lessons for 2025

    Healthcare cybersecurity trends of 2024

    Healthcare Cybersecurity: 2024 Was Tough, 2025 May Be Better

    CEO's Guide to Take-Down Services

    Shield Your Organization: CEO’s Perspective on Take-Down Services

    Azure sign-in Microsoft

    Microsoft Announces Mandatory MFA for Azure Sign-ins to Bolster Cloud Defenses

  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • All
    • Appointments
    • Budgets
    • Mergers & Aquisitions
    • Partnerships
    • Press Release
    • Startups
    Kerala Police Signs MoU With Cyble

    Kerala Police Signs MoU With Cyble to Use Threat Intelligence in Cybercrime Probes

    Gemini 4 Argon

    Gemini 4 Argon Restricted Over Cybersecurity Misuse Risks

    weekly roundup September 18 2026

    The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

    threat intelligence

    Cyble, UAE Cyber Security Council Unite Against Rising Cyber Threats

    Ukraine cybersecurity

    Zelensky Appoints Ihor Klymenko to Lead Ukraine’s Cybersecurity Center

    UK cyberattack rate

    UK Small Firms Bear Brunt of Rising Cyberattacks, Hiscox Finds

    Cyber Yodha Campaign

    Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

    UK Ukraine AI partnership

    Britain Gains Access to Ukraine’s ‘Goldmine’ of Battlefield AI Data

    Hims & Hers lawsuit

    FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices

    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
No Result
View All Result
  • MagazineDownload
  • Firewall Daily
    • All
    • Bug Bounty & Rewards
    • Dark Web News
    • Data Breach News
    • Hacker News
    • Ransomware News
    • Vulnerabilities
    weekly roundup

    The Cyber Express Weekly Roundup: FBI Blames North Korea for $6B Binance Hack, Hackers Turn Up the Heat on Europe’s Fridges and More

    Stockal cyberattack

    Stockal Confirms Unauthorized Trades in 13 Customer Accounts

    Alpine Linux servers

    Alpine Linux SSH Flaw Lets Attackers Log In Without a Password

    Queens Public Library ransomware attack

    Ransomware Just Took New York’s Queens Library Offline, and It’s Not the First

    Amadeus cybersecurity incident

    Airline Data Breach Widens as Singapore Airlines Reports 46,000 Affected Records

    refrigeration cyberattacks

    After Supermarket Freezers, Hackers Turn Up the Heat on France’s Blood Supply

    university supercomputer hacking

    Two Canadians Accused of Turning US University Supercomputers Into Crypto Miners

    investment fraud

    Europol Seizes 100+ Servers Running Fake Trading Platforms

    UTA cyberattack

    UTA Investigates Suspected Cyberattack After MachForms Service Disruption

    Trending Tags

    • blackbyte ransomware
    • Ransomware
    • lapsus$ ransomware
    • Apple
    • Apple vulnerability
  • Essentials
    • All
    • Compliance
    • Governance
    • Policy Updates
    • Regulations
    ASD Essentials

    The Essential Eight Is Being Replaced: What Australian Organisations Need to Know

    SICW 2026

    AI Is Now Fighting on Both Sides of the Cyber War, Singapore Warns

    Morocco cybersecurity strategy

    Morocco Flags AI Threats, Prioritizes Critical Infrastructure Defense

    European Police Chiefs Convention 2026

    Europe’s Police Chiefs Face Growing Threat of AI-Driven Crime

    AI service security

    Hackers Are Stealing AI Keys. The Cost Can Reach $600,000

    AI security risks

    Sam Altman at UN Security Council: 6 AI Security Risks the World Cannot Ignore

    AI-enabled cyber attacks

    AI Gives Hackers an Edge Defenders Still Can’t Match, NCSC Warns

    Fraudulent SIM cards

    India’s DoT Warns Citizens Over SIM Fraud and IMEI Tampering

    EU cybersecurity incidents

    EU Cybersecurity Response Hampered by Critical Information Gaps

    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
    • All
    • How to
    • What is
    Infostealer Intelligence

    The 2026 Infostealer Intelligence Shortlist: Top 10 Vendors Security Teams Should Know

    Google Chrome

    How to Remove Saved Passwords From Google Chrome (And Why You Should)

    DPDP Rules, Cyble, DPDP Act, Cyble Vantage

    How Cyble’s Front-Row Vantage Can Help You in Complying to India’s DPDP Act

    Cybersecurity Countries

    The Top 8 Countries Leading the Cyber Defense Race in 2025

    link building

    The Link Building Secrets Your Competitors Don’t Want You to Know

    Supply Chain Attack

    Supply Chain Resilience and Physical Security: Lessons for 2025

    Healthcare cybersecurity trends of 2024

    Healthcare Cybersecurity: 2024 Was Tough, 2025 May Be Better

    CEO's Guide to Take-Down Services

    Shield Your Organization: CEO’s Perspective on Take-Down Services

    Azure sign-in Microsoft

    Microsoft Announces Mandatory MFA for Azure Sign-ins to Bolster Cloud Defenses

  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • All
    • Appointments
    • Budgets
    • Mergers & Aquisitions
    • Partnerships
    • Press Release
    • Startups
    Kerala Police Signs MoU With Cyble

    Kerala Police Signs MoU With Cyble to Use Threat Intelligence in Cybercrime Probes

    Gemini 4 Argon

    Gemini 4 Argon Restricted Over Cybersecurity Misuse Risks

    weekly roundup September 18 2026

    The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

    threat intelligence

    Cyble, UAE Cyber Security Council Unite Against Rising Cyber Threats

    Ukraine cybersecurity

    Zelensky Appoints Ihor Klymenko to Lead Ukraine’s Cybersecurity Center

    UK cyberattack rate

    UK Small Firms Bear Brunt of Rising Cyberattacks, Hiscox Finds

    Cyber Yodha Campaign

    Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

    UK Ukraine AI partnership

    Britain Gains Access to Ukraine’s ‘Goldmine’ of Battlefield AI Data

    Hims & Hers lawsuit

    FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices

    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
No Result
View All Result
The Cyber Express
No Result
View All Result

CERT-In Urges Firms to Patch Critical Vulnerabilities Within 12 Hours Amid AI Threat Surge

Ashish Khaitan by Ashish Khaitan
May 27, 2026
in Firewall Daily, Cyber News
0
CERT-In
585
SHARES
3.2k
VIEWS
Share on LinkedInShare on Twitter

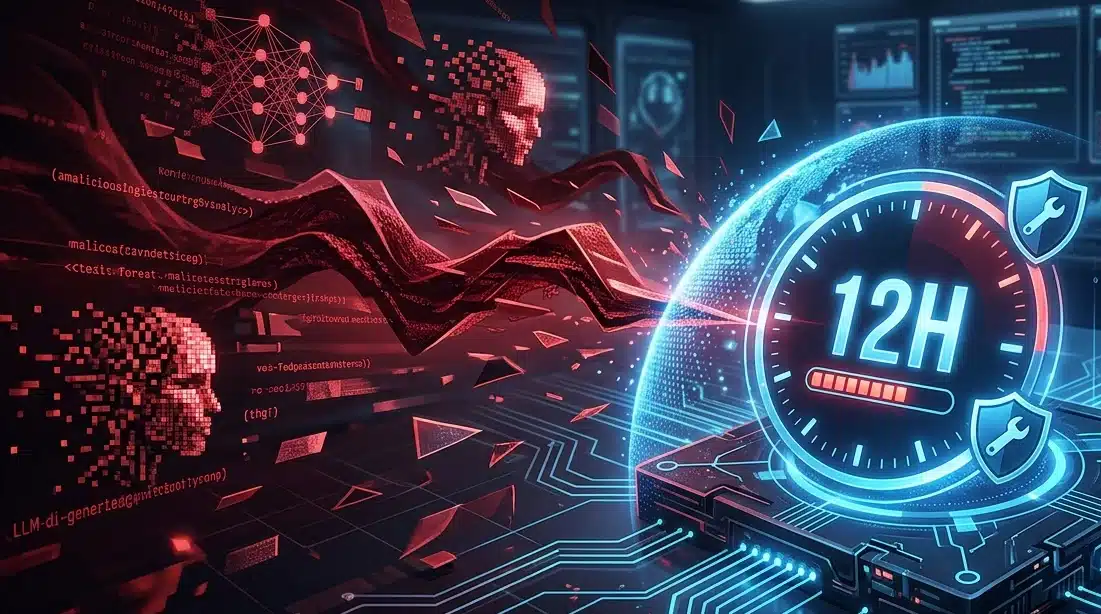
India’s Computer Emergency Response Team, Indian Computer Emergency Response Team, has introduced a new cybersecurity framework urging organizations to patch critical security vulnerabilities in internet-facing systems within 12 hours of detection whenever feasible. The recommendation comes amid growing concerns that cybercriminals are increasingly using artificial intelligence tools and large language models (LLMs) to accelerate cyber attacks, automate exploit development, and scale malicious operations more efficiently.

The guidance was published in a 38-page blueprint released on Monday and reflects mounting fears around AI-assisted cyber exploitation. According to CERT-In, the rapid adoption of AI and LLMs by threat actors is significantly shrinking the time between the discovery of security vulnerabilities and active exploitation.

“AI-assisted cyber exploitation reduces the time required for adversaries to identify, weaponize, and exploit vulnerabilities, exposed services, weak identities, insecure APIs, and misconfigured systems,” CERT-In stated in the document.

AI and LLMs Are Reshaping Cyber Attack Timelines 

CERT-In warned that as organizations become more dependent on cloud ecosystems, interconnected infrastructure, operational technology, software supply chains, and AI-enabled platforms, the risks associated with AI-driven attacks continue to rise across industries.

The agency noted that attackers are already using AI and LLMs for a broad range of malicious activities, including attack surface mapping, exploit analysis, phishing campaigns, malware creation, and automated reconnaissance. The use of AI allows attackers to compress traditional attack preparation timelines and evade some conventional security controls.

The blueprint also highlighted that AI-enabled environments themselves can become targets. Threat actors may exploit weaknesses through prompt injection attacks, model manipulation, jailbreaking methods, data leakage vulnerabilities, training data poisoning, model theft, and orchestration pipeline compromises. Such attacks can undermine the confidentiality, integrity, and reliability of AI systems.

According to CERT-In, organizations should prepare for a future where cyberattacks become autonomous, and exploitation timelines collapse further due to advancements in AI and LLMs. The agency said this shift requires stronger operational readiness, proactive patching strategies, continuous threat assessment, and aggressive exposure reduction practices.

CERT-In Calls for Stronger Defenses Against Security Vulnerabilities 

To counter AI-assisted attacks and reduce exposure to security vulnerabilities, CERT-In outlined several defensive principles that organizations should adopt. 

One of the key recommendations is the assumption that breaches are inevitable. Organizations are encouraged to prepare for rapid detection, containment, and recovery during compromise scenarios. The blueprint also stresses the adoption of Zero Trust security models that enforce continuous verification and least-privilege access controls. 

CERT-In further recommended implementing defense-in-depth strategies with layered protections across infrastructure to minimize the impact of successful breaches and eliminate single points of failure. The agency emphasized continuous monitoring and remediation of security vulnerabilities, along with integrating secure-by-design practices into applications, infrastructure, and AI workflows. 

The framework also advises organizations to maintain operational continuity during cyber incidents and ensure the protection of sensitive and operationally critical data throughout its lifecycle. Another major focus area is software supply chain security. CERT-In urged enterprises to reduce risks linked to third-party software, AI models, and dependencies through Software Bills of Materials (SBOMs), provenance validation, and security assessments. 

To evaluate the effectiveness of cybersecurity controls, the agency recommended regular red teaming exercises, vulnerability assessments, penetration testing, and independent audits. It also advised organizations to prioritize controls based on operational importance and threat exposure while establishing formal governance frameworks for AI usage and maintaining visibility into AI systems and integrations. 

“Organizations should implement layered, risk-based, and continuously validated technical controls to reduce exposure to AI-assisted cyber threats,” CERT-In said. “Controls should prioritize protection of internet-facing systems, critical business applications, identities, cloud environments, APIs, sensitive data, AI-enabled systems, and operational infrastructure.” 

New Patching Deadlines Introduced for Critical Flaws 

A major component of the blueprint focuses on vulnerability management and patching timelines. CERT-In urged organizations to adopt continuous, risk-based vulnerability and patch management practices to reduce risks associated with security vulnerabilities, insecure APIs, misconfigurations, publicly exposed services, and weak identities. 

Under the new recommendations, known exploited vulnerabilities affecting internet-facing and critical systems should be remediated within 12 hours wherever applicable. The agency also introduced additional remediation timelines based on severity and exposure levels. 

Critical externally exposed vulnerabilities should be addressed within one day. Known exploited vulnerabilities impacting internal systems should also be remediated within one day unless alternative mitigation measures are implemented and documented. Critical internal vulnerabilities affecting high-value systems should be patched within three days, while high-severity vulnerabilities should be resolved within five days based on risk prioritization. 

CERT-In acknowledged that immediate patching may not always be possible. In situations where fixes are unavailable, the agency advised organizations to deploy temporary mitigations such as system isolation, restricted access controls, web application firewall (WAF) or API protections, enhanced monitoring, and feature disablement until official patches are released. 

The new recommendations reflect growing global concerns about the role of AI and LLMs in modern cyber warfare. As threat actors continue to automate the discovery and exploitation of security vulnerabilities, cybersecurity agencies and enterprises are facing pressure to strengthen patching practices, reduce exposure windows, and improve resilience against rapidly evolving digital threats.
Share this:

  • Share on LinkedIn (Opens in new window) LinkedIn
  • Share on Reddit (Opens in new window) Reddit
  • Share on X (Opens in new window) X
  • Share on Facebook (Opens in new window) Facebook
  • More
  • Email a link to a friend (Opens in new window) Email
  • Share on WhatsApp (Opens in new window) WhatsApp

Related

Tags: CERT-Ininternet-facingLLMsSecurity VulnerabilitiesThe Cyber ExpressThe Cyber Express News
Previous Post

OverlayPhantom Android Banking Trojan Targets 180+ Financial Apps Across 10 Countries

Next Post

Notepad++ Patches High-Severity RCE Flaws in Version 8.9.6.1

Next Post
CVE-2026-48770

Notepad++ Patches High-Severity RCE Flaws in Version 8.9.6.1

Q1 2026 Threat Reports

❮ ❯
Cyble-Vision


Follow Us On Google News

Categories

  • Privacy Statement
  • Terms of Use
  • Write For Us

© 2026 The Cyber Express - Cybersecurity News and Magazine.

Welcome Back!

Login to your account below

Forgotten Password?

Retrieve your password

Please enter your username or email address to reset your password.

Log In

Add New Playlist

No Result
View All Result
  • Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board

© 2026 The Cyber Express - Cybersecurity News and Magazine.

-
00:00
00:00

Queue

Update Required Flash plugin
-
00:00
00:00



