




















• Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
The Cyber Express
  • MagazineDownload
  • Firewall Daily
    • All
    • Bug Bounty & Rewards
    • Dark Web News
    • Data Breach News
    • Hacker News
    • Ransomware News
    • Vulnerabilities
    weekly roundup

    The Cyber Express Weekly Roundup: FBI Blames North Korea for $6B Binance Hack, Hackers Turn Up the Heat on Europe’s Fridges and More

    Stockal cyberattack

    Stockal Confirms Unauthorized Trades in 13 Customer Accounts

    Alpine Linux servers

    Alpine Linux SSH Flaw Lets Attackers Log In Without a Password

    Queens Public Library ransomware attack

    Ransomware Just Took New York’s Queens Library Offline, and It’s Not the First

    Amadeus cybersecurity incident

    Airline Data Breach Widens as Singapore Airlines Reports 46,000 Affected Records

    refrigeration cyberattacks

    After Supermarket Freezers, Hackers Turn Up the Heat on France’s Blood Supply

    university supercomputer hacking

    Two Canadians Accused of Turning US University Supercomputers Into Crypto Miners

    investment fraud

    Europol Seizes 100+ Servers Running Fake Trading Platforms

    UTA cyberattack

    UTA Investigates Suspected Cyberattack After MachForms Service Disruption

    Trending Tags

    • blackbyte ransomware
    • Ransomware
    • lapsus$ ransomware
    • Apple
    • Apple vulnerability
  • Essentials
    • All
    • Compliance
    • Governance
    • Policy Updates
    • Regulations
    ASD Essentials

    The Essential Eight Is Being Replaced: What Australian Organisations Need to Know

    SICW 2026

    AI Is Now Fighting on Both Sides of the Cyber War, Singapore Warns

    Morocco cybersecurity strategy

    Morocco Flags AI Threats, Prioritizes Critical Infrastructure Defense

    European Police Chiefs Convention 2026

    Europe’s Police Chiefs Face Growing Threat of AI-Driven Crime

    AI service security

    Hackers Are Stealing AI Keys. The Cost Can Reach $600,000

    AI security risks

    Sam Altman at UN Security Council: 6 AI Security Risks the World Cannot Ignore

    AI-enabled cyber attacks

    AI Gives Hackers an Edge Defenders Still Can’t Match, NCSC Warns

    Fraudulent SIM cards

    India’s DoT Warns Citizens Over SIM Fraud and IMEI Tampering

    EU cybersecurity incidents

    EU Cybersecurity Response Hampered by Critical Information Gaps

    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
    • All
    • How to
    • What is
    Infostealer Intelligence

    The 2026 Infostealer Intelligence Shortlist: Top 10 Vendors Security Teams Should Know

    Google Chrome

    How to Remove Saved Passwords From Google Chrome (And Why You Should)

    DPDP Rules, Cyble, DPDP Act, Cyble Vantage

    How Cyble’s Front-Row Vantage Can Help You in Complying to India’s DPDP Act

    Cybersecurity Countries

    The Top 8 Countries Leading the Cyber Defense Race in 2025

    link building

    The Link Building Secrets Your Competitors Don’t Want You to Know

    Supply Chain Attack

    Supply Chain Resilience and Physical Security: Lessons for 2025

    Healthcare cybersecurity trends of 2024

    Healthcare Cybersecurity: 2024 Was Tough, 2025 May Be Better

    CEO's Guide to Take-Down Services

    Shield Your Organization: CEO’s Perspective on Take-Down Services

    Azure sign-in Microsoft

    Microsoft Announces Mandatory MFA for Azure Sign-ins to Bolster Cloud Defenses

  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • All
    • Appointments
    • Budgets
    • Mergers & Aquisitions
    • Partnerships
    • Press Release
    • Startups
    Kerala Police Signs MoU With Cyble

    Kerala Police Signs MoU With Cyble to Use Threat Intelligence in Cybercrime Probes

    Gemini 4 Argon

    Gemini 4 Argon Restricted Over Cybersecurity Misuse Risks

    weekly roundup September 18 2026

    The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

    threat intelligence

    Cyble, UAE Cyber Security Council Unite Against Rising Cyber Threats

    Ukraine cybersecurity

    Zelensky Appoints Ihor Klymenko to Lead Ukraine’s Cybersecurity Center

    UK cyberattack rate

    UK Small Firms Bear Brunt of Rising Cyberattacks, Hiscox Finds

    Cyber Yodha Campaign

    Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

    UK Ukraine AI partnership

    Britain Gains Access to Ukraine’s ‘Goldmine’ of Battlefield AI Data

    Hims & Hers lawsuit

    FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices

    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
No Result
View All Result
  • MagazineDownload
  • Firewall Daily
    • All
    • Bug Bounty & Rewards
    • Dark Web News
    • Data Breach News
    • Hacker News
    • Ransomware News
    • Vulnerabilities
    weekly roundup

    The Cyber Express Weekly Roundup: FBI Blames North Korea for $6B Binance Hack, Hackers Turn Up the Heat on Europe’s Fridges and More

    Stockal cyberattack

    Stockal Confirms Unauthorized Trades in 13 Customer Accounts

    Alpine Linux servers

    Alpine Linux SSH Flaw Lets Attackers Log In Without a Password

    Queens Public Library ransomware attack

    Ransomware Just Took New York’s Queens Library Offline, and It’s Not the First

    Amadeus cybersecurity incident

    Airline Data Breach Widens as Singapore Airlines Reports 46,000 Affected Records

    refrigeration cyberattacks

    After Supermarket Freezers, Hackers Turn Up the Heat on France’s Blood Supply

    university supercomputer hacking

    Two Canadians Accused of Turning US University Supercomputers Into Crypto Miners

    investment fraud

    Europol Seizes 100+ Servers Running Fake Trading Platforms

    UTA cyberattack

    UTA Investigates Suspected Cyberattack After MachForms Service Disruption

    Trending Tags

    • blackbyte ransomware
    • Ransomware
    • lapsus$ ransomware
    • Apple
    • Apple vulnerability
  • Essentials
    • All
    • Compliance
    • Governance
    • Policy Updates
    • Regulations
    ASD Essentials

    The Essential Eight Is Being Replaced: What Australian Organisations Need to Know

    SICW 2026

    AI Is Now Fighting on Both Sides of the Cyber War, Singapore Warns

    Morocco cybersecurity strategy

    Morocco Flags AI Threats, Prioritizes Critical Infrastructure Defense

    European Police Chiefs Convention 2026

    Europe’s Police Chiefs Face Growing Threat of AI-Driven Crime

    AI service security

    Hackers Are Stealing AI Keys. The Cost Can Reach $600,000

    AI security risks

    Sam Altman at UN Security Council: 6 AI Security Risks the World Cannot Ignore

    AI-enabled cyber attacks

    AI Gives Hackers an Edge Defenders Still Can’t Match, NCSC Warns

    Fraudulent SIM cards

    India’s DoT Warns Citizens Over SIM Fraud and IMEI Tampering

    EU cybersecurity incidents

    EU Cybersecurity Response Hampered by Critical Information Gaps

    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
    • All
    • How to
    • What is
    Infostealer Intelligence

    The 2026 Infostealer Intelligence Shortlist: Top 10 Vendors Security Teams Should Know

    Google Chrome

    How to Remove Saved Passwords From Google Chrome (And Why You Should)

    DPDP Rules, Cyble, DPDP Act, Cyble Vantage

    How Cyble’s Front-Row Vantage Can Help You in Complying to India’s DPDP Act

    Cybersecurity Countries

    The Top 8 Countries Leading the Cyber Defense Race in 2025

    link building

    The Link Building Secrets Your Competitors Don’t Want You to Know

    Supply Chain Attack

    Supply Chain Resilience and Physical Security: Lessons for 2025

    Healthcare cybersecurity trends of 2024

    Healthcare Cybersecurity: 2024 Was Tough, 2025 May Be Better

    CEO's Guide to Take-Down Services

    Shield Your Organization: CEO’s Perspective on Take-Down Services

    Azure sign-in Microsoft

    Microsoft Announces Mandatory MFA for Azure Sign-ins to Bolster Cloud Defenses

  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • All
    • Appointments
    • Budgets
    • Mergers & Aquisitions
    • Partnerships
    • Press Release
    • Startups
    Kerala Police Signs MoU With Cyble

    Kerala Police Signs MoU With Cyble to Use Threat Intelligence in Cybercrime Probes

    Gemini 4 Argon

    Gemini 4 Argon Restricted Over Cybersecurity Misuse Risks

    weekly roundup September 18 2026

    The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

    threat intelligence

    Cyble, UAE Cyber Security Council Unite Against Rising Cyber Threats

    Ukraine cybersecurity

    Zelensky Appoints Ihor Klymenko to Lead Ukraine’s Cybersecurity Center

    UK cyberattack rate

    UK Small Firms Bear Brunt of Rising Cyberattacks, Hiscox Finds

    Cyber Yodha Campaign

    Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

    UK Ukraine AI partnership

    Britain Gains Access to Ukraine’s ‘Goldmine’ of Battlefield AI Data

    Hims & Hers lawsuit

    FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices

    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
No Result
View All Result
The Cyber Express
No Result
View All Result

Malware Analysis and Detection Techniques

Malware analysis and detection techniques include employing a malware honeypot, machine learning behavioral analysis, or using Nmap to help detect and mitigate it.

Editorial by Editorial
April 9, 2023
in Firewall Daily, Learning & Development, Malware News
0
Malware Analysis and Detection Techniques
585
SHARES
3.2k
VIEWS
Share on LinkedInShare on Twitter

In 1982, Elk Cloner, the first malware, was detected in a Mac device. From then on, malware attacks have continued to increase and become more sophisticated. With over 10 million malware attacks witnessed within a year, it is imperative to have a robust team of experts working on malware analysis and detection.

Malware analysis and detection techniques include employing a malware honeypot, machine learning behavioral analysis, or using Nmap to help detect and mitigate it.

The first stealth virus, ‘Brain’ capable of hiding itself, was found in the 1990s, followed by others with increased capabilities. Now, nearly 560,000 new malware is detected every day, which makes analysis of the same a tedious task for the forensic department.

Evolution of malware and its detection techniques

Traditionally, malware analysis is done mostly manually however, new tools and techniques come in handy in faster research of the software. Efficient malware analysis helps in creating malware detection and prevention software.

Static analysis, dynamic analysis, and reverse engineering are some of the methods or stages of malware analysis and detection techniques. It unfolds the type, functionality, and impact of malicious software that may be a virus, worm, ransomware, or Trojan.

The time taken for malware analysis is increasing with features added to newly found samples on a regular basis. However, apt malware analysis and detection techniques are essential to curb its spread and threat.

Here are the most commonly used malware analysis and detection techniques

Static Malware Analysis

Static malware analysis is the study of malicious software without having to execute it (in a safe environment.) This is a fairly manually performed task that involves understanding the source code of the malware to find the data structure and used functions.

Otherwise, the found data gets lost when the source code gets compiled into a binary executable. Some types of static malware analysis are –

  • File fingerprinting – It involves testing it and conducting operations on the file including the computation of a cryptographic hash. This malware analysis technique helps find whether it was modified and if it has any similarities with its counterparts.
  • Disassembly – Here, the machine code is reversed using tools to assembly language like IDA Pro. The reconstructed assembly code is then used to find the program logic and intended malicious function as programmed by its developer.
  • AV scanning – AV scanners help detect if the malware binary belongs to the more commonly used ones.
  • File format – To find the magic number of the UNIX systems to determine the file type and find the file type, the metadata of the malware is examined.
  • Packer detection – Static analysis is hindered by the loss of metadata of malware which is often obfuscated using a packer. To prevent this loss during the packing process, unpackers such as PEiD2 can help to some extent in examining the malware.
Dynamic Malware Analysis

Dynamic analysis is the study of a file in its execution process. The malware is run in a safe environment to understand its malicious capabilities. A benefit of dynamic analysis against static analysis is that it offers the observation of the actual behavior of the software during runtime and when it unpacks itself.

Moreover, extra detailing is offered in terms of its analysis as this process is largely automated. However, the ‘dormant code’ allows monitoring only one execution path offering incomplete code coverage.

Following are the two main types of dynamic malware analysis –

  • Analyzing the malware between defined points – Upon executing the malware for a specific time frame, the changes to the system are monitored from start to end.
  • Monitoring runtime behavior – It is simply the monitoring of the malware during runtime using specialized tools. Some of the malware analysis tools are Anubis, CWSandbox, and Norman Sandbox.

Machine learning and deep learning techniques for malware analysis

Malware evolved from ‘ILOVEYOU’ in 2000, which attacked millions of Windows-based devices to ‘Anna Kournikova’ which infected with emails. Malware detection also went through an overhaul.

A malware analysis and detection technique using Machine Learning Algorithms soon came to the fore. To thoroughly gauge the workings of a Polymorphic malware that can change its signature to evade detection, machine learning techniques were created. These techniques offer a high detection ratio with clear results measuring false positives and false negatives.

It also uses models to detect malware behavior including Bagging, Gradient Boost and AdaBoost, MLP classifier, Hybrid Model, and Restricted Boltzmann Machine model. It offers different levels of accuracy in understanding malware features along with losing valuable data in runtime.

Data mining techniques using machine learning approaches for malware analysis and detection

Data mining involves two broad approaches namely the signature-based detection and behavior-based detection of malware. It is a machine-learning method for detecting malware. It works on malware and benign examples.
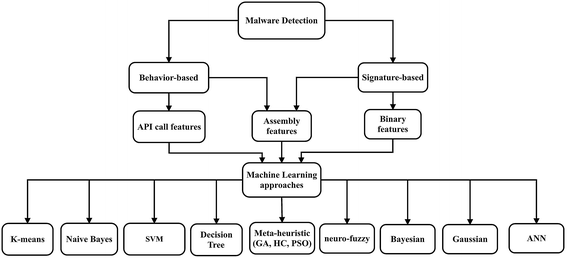
Malware Analysis and Detection Techniques
Taxonomy of malware detection (Photo: SpringerOpen)
  • Signature-based malware detection technique

The signature-based detection method focuses on conducting static investigations for learning the code-structure of the infection chain. For this the method looks for interruptions against a predefined set of known assault capabilities.

Although this method follows a thorough execution pattern it is not considered the best detection method as it misses important functions of the malware while working on standard marks covered by portable malware.

  • Behavior-based malware detection technique

Behavior-based malware detection technique requires running it in a sandboxed environment to check it during runtime. It offers better results of how the malware was created and developed to run on a machine. Following the dynamic analysis method, malware is monitored for its malicious features by its code and structure.

Share this:

  • Share on LinkedIn (Opens in new window) LinkedIn
  • Share on Reddit (Opens in new window) Reddit
  • Share on X (Opens in new window) X
  • Share on Facebook (Opens in new window) Facebook
  • More
  • Email a link to a friend (Opens in new window) Email
  • Share on WhatsApp (Opens in new window) WhatsApp

Related

Tags: machine learning malware detectionMalware analysis and detection techniquesstatic malware analysisThe Cyber ExpressThe Cyber Express News
Previous Post

Phishing as a Service Emerges as New Cybercrime Trend on Telegram

Next Post

Top 5 Trends For Digital Forensics in 2023

Next Post
Top 5 Trends For Digital Forensics in 2023

Top 5 Trends For Digital Forensics in 2023

Q1 2026 Threat Reports

❮ ❯
Cyble-Vision


Follow Us On Google News

Categories

  • Privacy Statement
  • Terms of Use
  • Write For Us

© 2026 The Cyber Express - Cybersecurity News and Magazine.

Welcome Back!

Login to your account below

Forgotten Password?

Retrieve your password

Please enter your username or email address to reset your password.

Log In

Add New Playlist

No Result
View All Result
  • Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board

© 2026 The Cyber Express - Cybersecurity News and Magazine.

-
00:00
00:00

Queue

Update Required Flash plugin
-
00:00
00:00



