
















• Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
The Cyber Express
  • MagazineDownload
  • Firewall Daily
    • All
    • Bug Bounty & Rewards
    • Dark Web News
    • Data Breach News
    • Hacker News
    • Ransomware News
    • Vulnerabilities
    weekly roundup October 30

    The Cyber Express Weekly Roundup: Binance Hit by $6.3 Billion Security Incident, South Korea Busts AI-Powered Hacking Ring and More

    Binance Data Breach

    Binance Security Incident Affects $6.3 Billion in Crypto Assets, $3 Billion Frozen

    Cyberattacks on Japan

    Three Cyberattack Campaigns Target Japan, Exposing AI’s Growing Role

    Ukrainian ransomware affiliate

    Ransomware Attacks on Hospitals and Businesses Lead to 70-Month Sentence

    FBI seizes Virtualine

    FBI Seizes Bulletproof Hosting Domain Linked to Cybercrime

    ASD Cyber Threat Report

    Australian Data Breach Incidents Up 66% as AI Sharpens Scams

    INJ3CTOR3

    INJ3CTOR3 Malware Steals FreePBX Credentials, Enabling Toll Fraud After Cleanup

    Discoverable Servers

    Discord to Let Google Index Public Server Messages, Raising Privacy Concerns

    Columbia University cyberattack

    Columbia University Settles $16.1M Data Breach Lawsuit After 2025 Cyberattack

    Trending Tags

    • blackbyte ransomware
    • Ransomware
    • lapsus$ ransomware
    • Apple
    • Apple vulnerability
  • Essentials
    • All
    • Compliance
    • Governance
    • Policy Updates
    • Regulations
    ASD Essentials

    The Essential Eight Is Being Replaced: What Australian Organisations Need to Know

    SICW 2026

    AI Is Now Fighting on Both Sides of the Cyber War, Singapore Warns

    Morocco cybersecurity strategy

    Morocco Flags AI Threats, Prioritizes Critical Infrastructure Defense

    European Police Chiefs Convention 2026

    Europe’s Police Chiefs Face Growing Threat of AI-Driven Crime

    AI service security

    Hackers Are Stealing AI Keys. The Cost Can Reach $600,000

    AI security risks

    Sam Altman at UN Security Council: 6 AI Security Risks the World Cannot Ignore

    AI-enabled cyber attacks

    AI Gives Hackers an Edge Defenders Still Can’t Match, NCSC Warns

    Fraudulent SIM cards

    India’s DoT Warns Citizens Over SIM Fraud and IMEI Tampering

    EU cybersecurity incidents

    EU Cybersecurity Response Hampered by Critical Information Gaps

    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
    • All
    • How to
    • What is
    Infostealer Intelligence

    The 2026 Infostealer Intelligence Shortlist: Top 10 Vendors Security Teams Should Know

    Google Chrome

    How to Remove Saved Passwords From Google Chrome (And Why You Should)

    DPDP Rules, Cyble, DPDP Act, Cyble Vantage

    How Cyble’s Front-Row Vantage Can Help You in Complying to India’s DPDP Act

    Cybersecurity Countries

    The Top 8 Countries Leading the Cyber Defense Race in 2025

    link building

    The Link Building Secrets Your Competitors Don’t Want You to Know

    Supply Chain Attack

    Supply Chain Resilience and Physical Security: Lessons for 2025

    Healthcare cybersecurity trends of 2024

    Healthcare Cybersecurity: 2024 Was Tough, 2025 May Be Better

    CEO's Guide to Take-Down Services

    Shield Your Organization: CEO’s Perspective on Take-Down Services

    Azure sign-in Microsoft

    Microsoft Announces Mandatory MFA for Azure Sign-ins to Bolster Cloud Defenses

  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • All
    • Appointments
    • Budgets
    • Mergers & Aquisitions
    • Partnerships
    • Press Release
    • Startups
    Kerala Police Signs MoU With Cyble

    Kerala Police Signs MoU With Cyble to Use Threat Intelligence in Cybercrime Probes

    Gemini 4 Argon

    Gemini 4 Argon Restricted Over Cybersecurity Misuse Risks

    weekly roundup September 18 2026

    The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

    threat intelligence

    Cyble, UAE Cyber Security Council Unite Against Rising Cyber Threats

    Ukraine cybersecurity

    Zelensky Appoints Ihor Klymenko to Lead Ukraine’s Cybersecurity Center

    UK cyberattack rate

    UK Small Firms Bear Brunt of Rising Cyberattacks, Hiscox Finds

    Cyber Yodha Campaign

    Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

    UK Ukraine AI partnership

    Britain Gains Access to Ukraine’s ‘Goldmine’ of Battlefield AI Data

    Hims & Hers lawsuit

    FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices

    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
No Result
View All Result
The Cyber Express
No Result
View All Result

CISA Launches CI Fortify to Defend Critical Infrastructure From Nation-State Cyber Threats

Samiksha Jain by Samiksha Jain
May 7, 2026
in Cyber News, Firewall Daily, Ransomware News, Vulnerabilities
0
CI Fortify
585
SHARES
3.2k
VIEWS
Share on LinkedInShare on Twitter

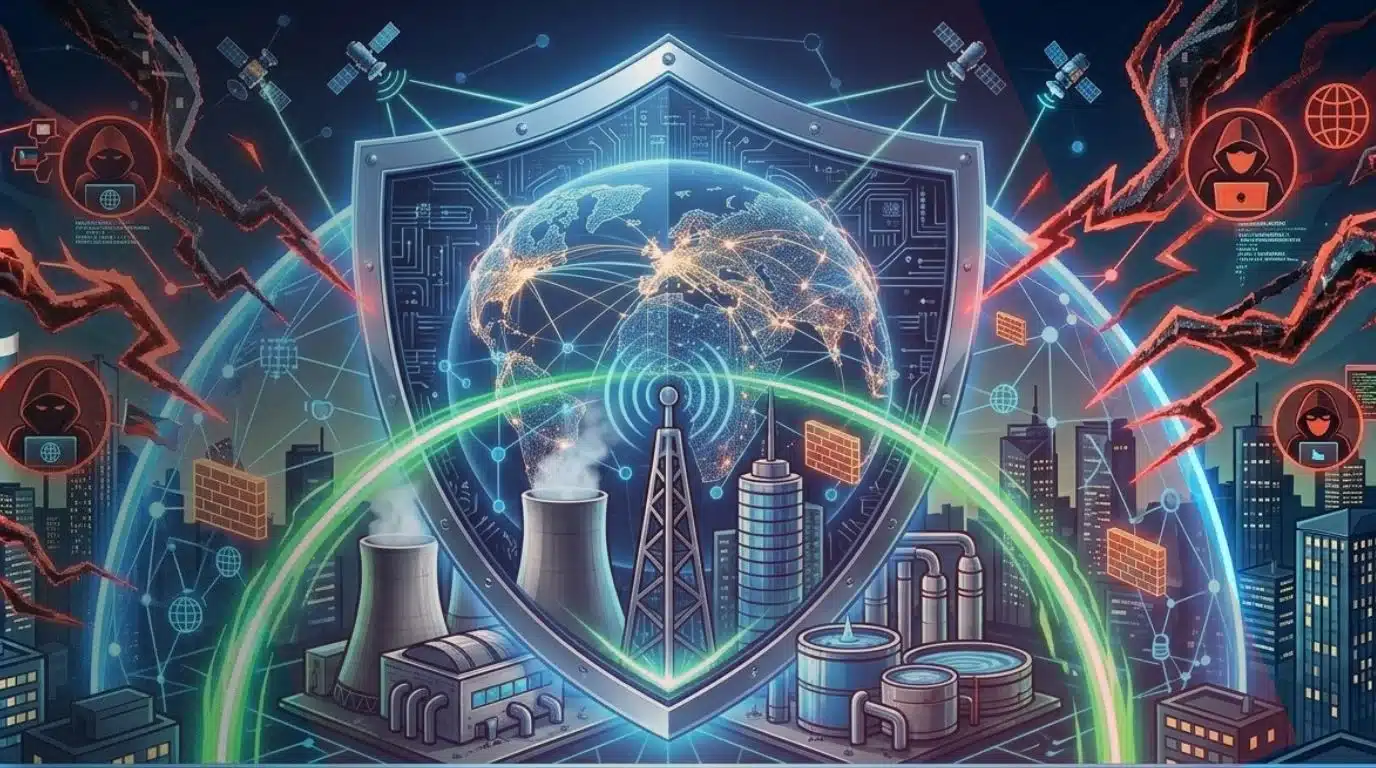
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has launched a new initiative called “CI Fortify” aimed at helping critical infrastructure operators prepare for disruptive cyberattacks linked to geopolitical conflicts. The initiative comes amid growing concerns over nation-state cyber threats targeting operational technology (OT) systems that support essential services across the United States.

The CI Fortify initiative focuses on improving critical infrastructure resilience through two key objectives: isolation and recovery. CISA said the effort is designed to help operators maintain essential operations even if adversaries compromise telecommunications networks, internet services, or industrial control systems.

According to the agency, nation-state actors are no longer limiting their activities to espionage. Instead, threat groups have increasingly been pre-positioning themselves inside critical infrastructure environments to potentially disrupt or destroy systems during future geopolitical conflicts.

CI Fortify Initiative Focuses on Isolation and Recovery

Under the CI Fortify initiative, CISA is urging critical infrastructure organizations to assume that third-party communications and service providers may become unreliable during a crisis. Operators are also being asked to plan under the assumption that threat actors may already have some level of access to OT networks.

Nick Andersen, Acting Director at CISA, emphasized the need for organizations to prepare for worst-case operational scenarios.

“In a geopolitical crisis, the critical infrastructure organizations Americans rely on must be able to continue delivering, at a minimum, crucial services,” Andersen said. “They must be able to isolate vital systems from harm, continue operating in that isolated state, and quickly recover any systems that an adversary may successfully compromise.”

The isolation strategy outlined under CI Fortify involves proactively disconnecting operational technology systems from external business networks and third-party connections. CISA said this approach is intended to prevent cyber impacts from spreading into OT environments while allowing organizations to continue delivering essential services in a degraded communications environment.

The agency advised operators to identify critical customers, including military infrastructure and other lifeline services, and determine the minimum operational capabilities needed to support them during emergencies.

CISA also recommended updating engineering processes and business continuity plans to support safe operations for extended periods while systems remain isolated.

Recovery Planning Central to Critical Infrastructure Resilience

Alongside isolation, the CI Fortify initiative places strong emphasis on recovery planning. CISA urged operators to maintain updated system documentation, create secure backups of critical files, and regularly practice system replacement or manual operational transitions.

The agency noted that organizations should also identify communications dependencies that could complicate recovery efforts, such as licensing servers, remote vendor access, or upstream network connections.

CISA encouraged operators to work closely with managed service providers, system integrators, and vendors to understand potential failure points and establish alternative recovery pathways.

The initiative also highlights broader benefits of emergency planning beyond cybersecurity incidents. According to CISA, the same planning processes can help organizations maintain operations during weather-related disruptions, equipment failures, and safety emergencies.

The agency said isolation planning can help cut off command-and-control access to compromised systems, while strong recovery preparation can reduce incident response costs and shorten recovery timelines.

Security Vendors and Service Providers Asked to Support CI Fortify

The CI Fortify initiative extends beyond infrastructure operators and calls on cybersecurity vendors, industrial automation suppliers, and managed service providers to support resilience planning efforts.

Industrial control system vendors are being encouraged to identify barriers that could interfere with isolation and recovery procedures, including licensing restrictions and server dependency issues.

Managed service providers and integrators are expected to assist organizations in engineering updates, local backup collection, and recovery documentation planning.

Meanwhile, security vendors are being asked to support threat monitoring and provide intelligence if nation-state actors shift from espionage-focused activity to destructive cyber operations.

CISA also requested vendors share information related to tactics that could undermine recovery or bypass isolation protections, including malicious firmware updates and vulnerabilities affecting software-based data diodes.

Volt Typhoon Cyberattacks Continue to Shape U.S. Cybersecurity Strategy

The launch of CI Fortify is closely tied to ongoing concerns surrounding the Volt Typhoon cyberattacks, which U.S. officials have linked to Chinese state-sponsored threat actors.

CISA’s initiative specifically references the Volt Typhoon campaign as an example of how adversaries have attempted to establish long-term access inside U.S. critical infrastructure systems to potentially support disruptive actions during military conflicts.

The Volt Typhoon operation first became public in 2023, when U.S. authorities revealed that Chinese hackers had infiltrated multiple sectors of American critical infrastructure.

Former CISA Director Jen Easterly stated in 2024 that the agency had identified and removed Volt Typhoon intrusions across several sectors. She later reiterated in 2025 that efforts continued to focus on identifying and evicting Chinese cyber actors from critical infrastructure environments.

Despite these operations, cybersecurity researchers and some government officials have warned that Chinese threat actors may still retain access to portions of critical infrastructure networks. Several experts have argued that nation-state groups remain deeply embedded in certain environments despite years of remediation efforts.

With the CI Fortify initiative, CISA appears to be shifting focus toward operational resilience, recognizing that prevention alone may not be sufficient against sophisticated nation-state cyber threats targeting U.S. critical infrastructure.

Share this:

  • Share on LinkedIn (Opens in new window) LinkedIn
  • Share on Reddit (Opens in new window) Reddit
  • Share on X (Opens in new window) X
  • Share on Facebook (Opens in new window) Facebook
  • More
  • Email a link to a friend (Opens in new window) Email
  • Share on WhatsApp (Opens in new window) WhatsApp

Related

Tags: critical infrastructureCritical Infrastructure Resilienceremote vendor accessThe Cyber ExpressThe Cyber Express NewsU.S. Cybersecurity StrategyVolt Typhoon Cyberattacks
Previous Post

PAN-OS Flaw CVE-2026-0300 Exposes Firewalls to Remote Code Execution

Next Post

Salesforce Marketing Cloud Vulnerabilities Expose Cross-Tenant Subscriber Data Risks

Next Post
Salesforce AMPScript

Salesforce Marketing Cloud Vulnerabilities Expose Cross-Tenant Subscriber Data Risks

Cyble-Vision


Follow Us On Google News

Categories

Q1 2026 Threat Reports

❮ ❯
  • Privacy Statement
  • Terms of Use
  • Write For Us

© 2026 The Cyber Express - Cybersecurity News and Magazine.

Welcome Back!

Login to your account below

Forgotten Password?

Retrieve your password

Please enter your username or email address to reset your password.

Log In

Add New Playlist

No Result
View All Result
  • Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board

© 2026 The Cyber Express - Cybersecurity News and Magazine.

-
00:00
00:00

Queue

Update Required Flash plugin
-
00:00
00:00


