• About Us
  • Contact Us
  • Editorial Calendar
  • Careers
  • The Cyber Express by Cyble Vulnerability Disclosure Policy
  • Cyble Trust Portal
The Cyber Express
  • MagazineDownload
  • Firewall Daily
    • All
    • Bug Bounty & Rewards
    • Dark Web News
    • Data Breach News
    • Hacker News
    • Ransomware News
    • Vulnerabilities
    Operation Serengeti III

    INTERPOL’s Operation Serengeti III Disrupts 10,909 Malicious Networks

    AI cyberattack simulations

    Japan AI Cyberattack Simulations Planned as PHP Flaws Disrupt Services

    Yonsei University cyberattack

    Yonsei University Cyberattack Hits 10,000 Students, Months After Sogang Breach

    CVE-2026-109618

    PHP2Shell Patch Rush Takes Wikipedia, Govt Sites Offline

    SafePay ransomware

    FBI, CISA Warn SafePay Ransomware Has Hit 600+ Victims

    BAE Systems cyberattack

    BAE Systems Cyberattack Halts Bankruptcy Notices at Every U.S. Federal Court

    fake driving licence

    No Lessons, No Test, No Travel: Dubai Police Bust AED 10,000 Licence Scheme

    generative AI in research

    AI Can’t Judge Your Paper: EU Updates Guidelines on Peer Review and AI Agents

    ASD Essentials

    The Essential Eight Is Being Replaced: What Australian Organisations Need to Know

    Trending Tags

    • blackbyte ransomware
    • Ransomware
    • lapsus$ ransomware
    • Apple
    • Apple vulnerability
  • Essentials
    • All
    • Compliance
    • Governance
    • Policy Updates
    • Regulations
    ASD Essentials

    The Essential Eight Is Being Replaced: What Australian Organisations Need to Know

    SICW 2026

    AI Is Now Fighting on Both Sides of the Cyber War, Singapore Warns

    Morocco cybersecurity strategy

    Morocco Flags AI Threats, Prioritizes Critical Infrastructure Defense

    European Police Chiefs Convention 2026

    Europe’s Police Chiefs Face Growing Threat of AI-Driven Crime

    AI service security

    Hackers Are Stealing AI Keys. The Cost Can Reach $600,000

    AI security risks

    Sam Altman at UN Security Council: 6 AI Security Risks the World Cannot Ignore

    AI-enabled cyber attacks

    AI Gives Hackers an Edge Defenders Still Can’t Match, NCSC Warns

    Fraudulent SIM cards

    India’s DoT Warns Citizens Over SIM Fraud and IMEI Tampering

    EU cybersecurity incidents

    EU Cybersecurity Response Hampered by Critical Information Gaps

    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
    • All
    • How to
    • What is
    Infostealer Intelligence

    The 2026 Infostealer Intelligence Shortlist: Top 10 Vendors Security Teams Should Know

    Google Chrome

    How to Remove Saved Passwords From Google Chrome (And Why You Should)

    DPDP Rules, Cyble, DPDP Act, Cyble Vantage

    How Cyble’s Front-Row Vantage Can Help You in Complying to India’s DPDP Act

    Cybersecurity Countries

    The Top 8 Countries Leading the Cyber Defense Race in 2025

    link building

    The Link Building Secrets Your Competitors Don’t Want You to Know

    Supply Chain Attack

    Supply Chain Resilience and Physical Security: Lessons for 2025

    Healthcare cybersecurity trends of 2024

    Healthcare Cybersecurity: 2024 Was Tough, 2025 May Be Better

    CEO's Guide to Take-Down Services

    Shield Your Organization: CEO’s Perspective on Take-Down Services

    Azure sign-in Microsoft

    Microsoft Announces Mandatory MFA for Azure Sign-ins to Bolster Cloud Defenses

  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • All
    • Appointments
    • Budgets
    • Mergers & Aquisitions
    • Partnerships
    • Press Release
    • Startups
    Kerala Police Signs MoU With Cyble

    Kerala Police Signs MoU With Cyble to Use Threat Intelligence in Cybercrime Probes

    Gemini 4 Argon

    Gemini 4 Argon Restricted Over Cybersecurity Misuse Risks

    weekly roundup September 18 2026

    The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

    threat intelligence

    Cyble, UAE Cyber Security Council Unite Against Rising Cyber Threats

    Ukraine cybersecurity

    Zelensky Appoints Ihor Klymenko to Lead Ukraine’s Cybersecurity Center

    UK cyberattack rate

    UK Small Firms Bear Brunt of Rising Cyberattacks, Hiscox Finds

    Cyber Yodha Campaign

    Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

    UK Ukraine AI partnership

    Britain Gains Access to Ukraine’s ‘Goldmine’ of Battlefield AI Data

    Hims & Hers lawsuit

    FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices

    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
No Result
View All Result
The Cyber Express
No Result
View All Result
Home Firewall Daily

Have You Patched Mitsubishi MELSEC Controller Vulnerability?

The successful exploitation of the Mitsubishi MELSEC iQ-F controller vulnerability in the MELSEC Series CPU module could lead to severe consequences.

Editorial by Editorial
May 29, 2023
in Firewall Daily, Vulnerabilities
0
Mitsubishi MELSEC controller vulnerability
623
SHARES
3.5k
VIEWS
Share on LinkedInShare on Twitter

The Cybersecurity and Infrastructure Security Agency (CISA) issued a special advisory on Mitsubishi MELSEC controller vulnerability CVE-2023-1424, apart from the list of ICS vulnerability alerts issued two days before that.

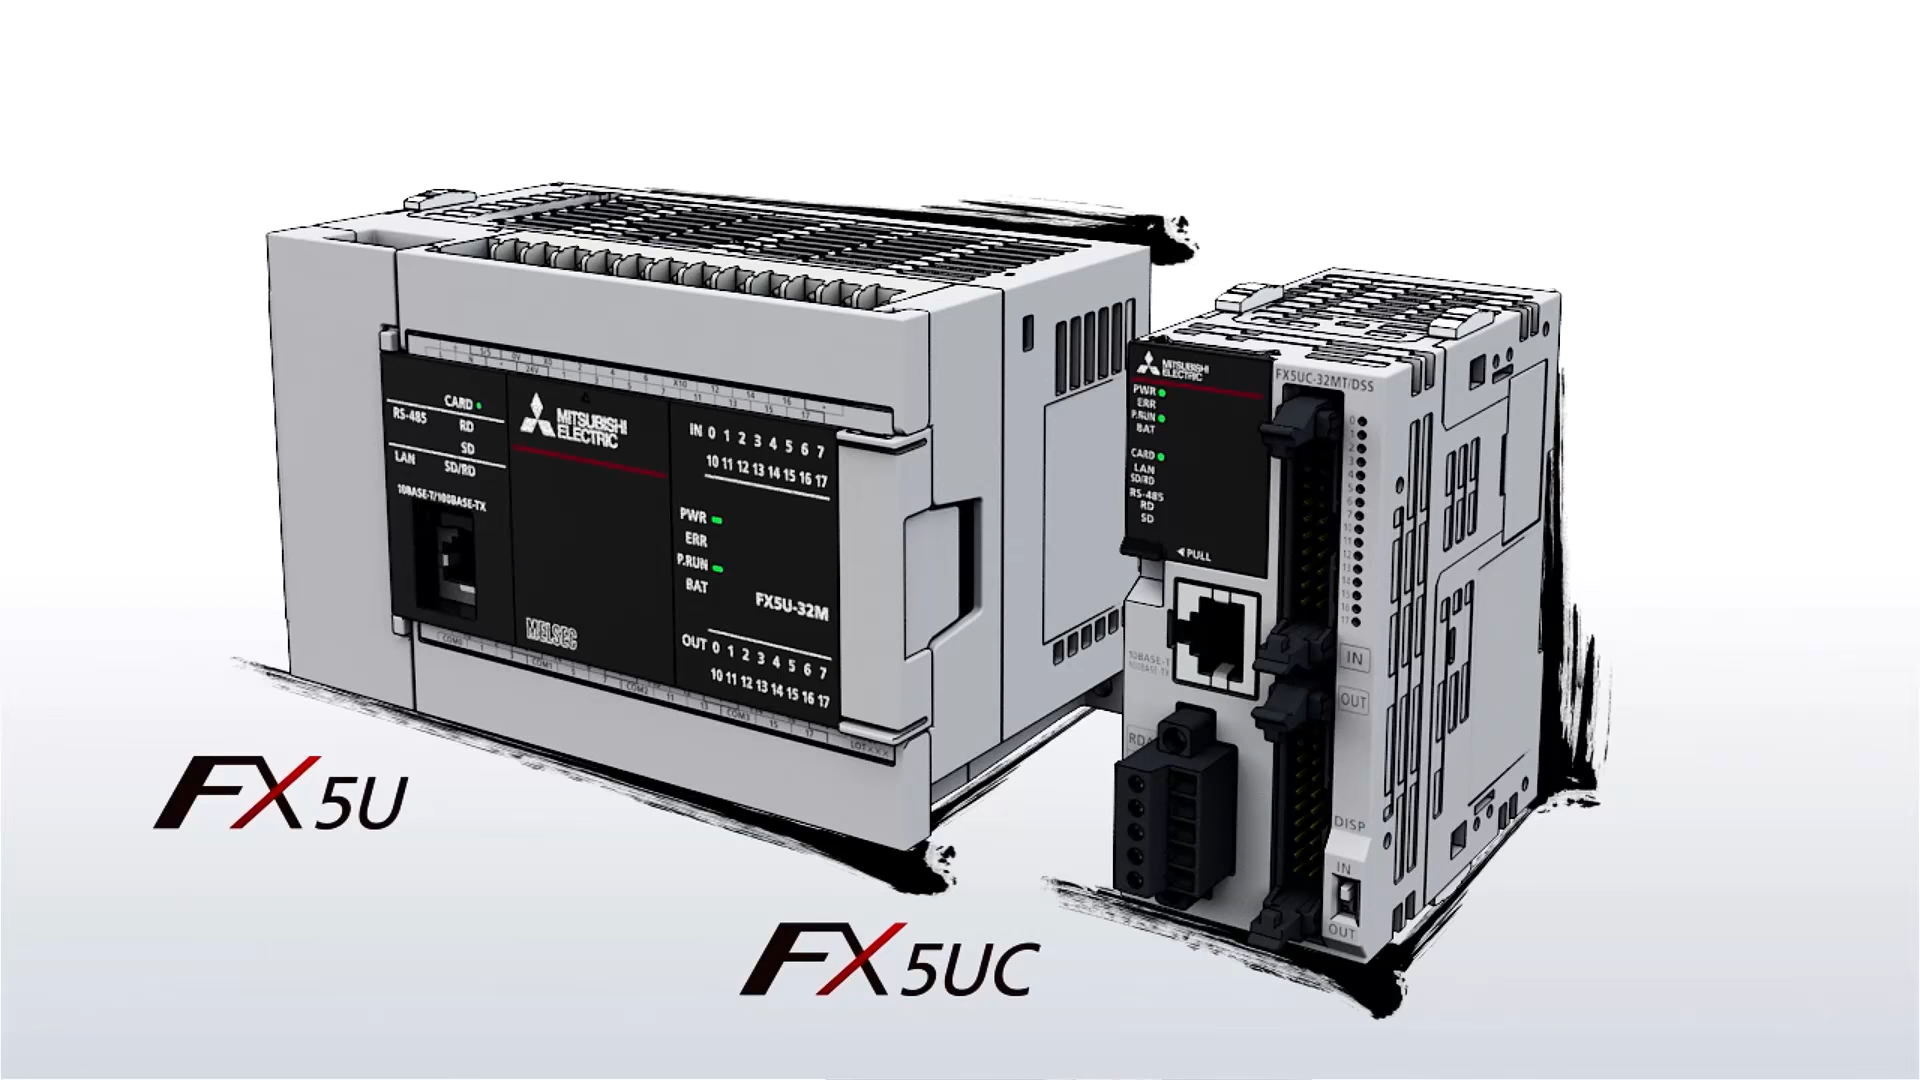
Cisco Talos found this critical vulnerability CVE-2023-1424 in the Mitsubishi MELSEC iQ-F FX5U programmable logic controller, resulting from a buffer overflow condition.

The affected device, part of Mitsubishi’s MELSEC PLC line, combines a processor, power supply, Ethernet, and I/O points.

Exploiting the vulnerability involves sending a specially crafted network packet to the device’s MELSOFT Direct functionality.

This buffer overflow can lead to a denial-of-service situation in the parsing task of the MELSOFT Direct protocol, potentially enabling remote code execution by malicious actors.

To address the issue posed by this vulnerability CVE-2023-1424, Mitsubishi released updates (version 1.240 and 1.260) for affected customers, urging immediate installation.
Industrial Automation relies on Control Systems to regulate the functioning of devices in real-time.

These systems, such as RTUs (Remote Terminal Units), PLCs (Programmable Logic Controllers), and DCSs (Distributed Control Systems), employ closed-loop control mechanisms.

Mitsubishi MELSEC controller vulnerability
Image courtesy: youtube.com/@MitsubishiFAEU

Mitsubishi MELSEC controller vulnerability: In a nutshell

“The iQ-F FX5U is one offering in Mitsubishi’s MELSEC PLC line of hardware that comes with a built-in processor, power supply, Ethernet and 16 I/O points,” said a CISO Talos assessment report of the vulnerability.

Users can configure this PLC to host multiple network services, such as an HTTP Server, FTP Server, FTP Client, MODBUS/TCP interface and other Mitsubishi-specific protocols.

On May 23, 2023, Mitsubishi Electric Corporation disclosed a critical vulnerability in their MELSEC Series CPU module.

The vulnerability, rated with a CVSS v3 score of 10.0, poses a significant threat as it can be exploited remotely with low attack complexity.

The issue stems from classic buffer overflow vulnerabilities present in the module. Mitsubishi Electric Corporation is actively addressing this vulnerability and recommends immediate attention to mitigate potential risks.

“A remote attacker may cause a denial of service (DoS) condition or execute malicious code on a target product by sending specially crafted packets,” said the Mitsubishi vulnerability alert.

“However, the attacker needs to understand the internal structure of products to execute malicious code,” it added.

Although the execution of malicious code requires a deep understanding of the product’s internal structure, the impact could be significant.

Risk evaluation of the Mitsubishi MELSEC controller vulnerability

The successful exploitation of the Mitsubishi MELSEC controller vulnerability in the MELSEC Series CPU module could lead to severe consequences. Remote attackers can disrupt the normal operation of the targeted product or execute malicious code.

“This buffer overflow condition could lead to a denial-of-service condition within the RTOS task responsible for parsing the MELSOFT Direct protocol, and potentially give the adversary the ability to execute remote code on the targeted device,” said the CISCO Talos report.

While executing malicious code is challenging due to the requirement of understanding the product’s internal structure, the potential impact and risk associated with this vulnerability should not be ignored.

“Users are encouraged to update these affected products as soon as possible: Mitsubishi Electric Corp. MELSEC iQ-F FX5U, versions 1.240 and 1.260,” urged the CISCO Talos report.

“Talos tested and confirmed these versions of the controller could be exploited by this vulnerability, however, Mitsubishi also stated in its advisory that versions 1.220 and later are affected.”

Mitsubishi MELSEC controller vulnerability: Technical details

The vulnerability affects specific models of the MELSEC Series, including FX5U-xMy/z and FX5UC-xMy/z. These models must have a serial number of 17X**** or later and firmware version 1.220 and later.

The vulnerability stems from a classic buffer overflow, where input buffers are copied without proper size checks. Exploiting this vulnerability may result in a denial-of-service condition or allow the execution of malicious code.

The vulnerability has been assigned CVE-2023-1424, and its CVSS v3 base score is 10.0.

Mitsubishi Electric has responded swiftly by developing firmware version 1.290 to address the vulnerability.

The company recommended users to update their MELSEC Series CPU modules with this firmware release. Additionally, the company recommended mitigation measures such as employing firewalls or virtual private networks (VPNs) to prevent unauthorized access when connected.

It also suggested operating the affected product within a secure local area network (LAN) environment and configuring firewalls to block access from untrusted networks and hosts.

Utilizing the IP filter function to restrict access from untrusted hosts and restricting physical access to LANs connected to the vulnerable products are also advised.

Cybersecurity and Infrastructure Security Agency (CISA) further encourages adherence to their control systems security best practices, available on the official ICS webpage at cisa.gov/ics.
Share this:

  • Share on LinkedIn (Opens in new window) LinkedIn
  • Share on Reddit (Opens in new window) Reddit
  • Share on X (Opens in new window) X
  • Share on Facebook (Opens in new window) Facebook
  • More
  • Email a link to a friend (Opens in new window) Email
  • Share on WhatsApp (Opens in new window) WhatsApp

Related

Tags: Mitsubishi MELSEC iQ-F Controller Vulnerability
Previous Post

CERT-In Issues Alert on Two High-Severity iTunes Vulnerabilities

Next Post

10 Essential Google Hacks Every Cybersecurity Professional Should Know

Next Post
Google Hacks

10 Essential Google Hacks Every Cybersecurity Professional Should Know

Q1 2026 Threat Reports

❮ ❯
Cyble-Vision


Follow Us On Google News

Latest Cyber News

Operation Serengeti III
Firewall Daily

INTERPOL’s Operation Serengeti III Disrupts 10,909 Malicious Networks

October 23, 2026
AI cyberattack simulations
Firewall Daily

Japan AI Cyberattack Simulations Planned as PHP Flaws Disrupt Services

October 23, 2026
software supply chain security
Cyber News

Why Fintechs Must Treat Software Supply Chain Security as an Enterprise Risk

October 23, 2026
AI-built websites
Cyber News

Live API Keys Found in Public Code of AI-Built Websites, Cyble Research Shows

October 22, 2026

Categories

Web Stories

Do This on Telegram, Your Bank Account Will Become Zero
If You Install the iOS 18 Beta, Your iPhone Could Be Hacked
Cricket World Cup Ticketing Systems Under Cybersecurity
Cyber Threats and Online Ticket Scams During the NBA Finals
Biometric Data Security: Protecting Sensitive Information

About

The Cyber Express

#1 Trending Cybersecurity News and Magazine

The Cyber Express is a handbook for all stakeholders of the internet that provides information security professionals with the latest news, updates and knowledge they need to combat cyber threats.


Contact

For editorial queries: [email protected]

For marketing and Sales: [email protected]


Quick Links

  • About Us
  • Contact Us
  • Editorial Calendar
  • Careers
  • The Cyber Express by Cyble Vulnerability Disclosure Policy
  • Cyble Trust Portal

Our Address

We’re remote friendly, with office locations around the world:

San Francisco, Atlanta, Rome,
Dubai, Mumbai, Bangalore, Hyderabad,  Singapore, Jakarta, Sydney, and Melbourne


Headquarters:

The Cyber Express LLC
10080 North Wolfe Road, Suite SW3-200, Cupertino, CA, US 95014


India Office:

Cyber Express Media Network
HD-021, 4th Floor, C Wing, Building No.4. Nesco IT Park, WE Highway, Goregaon East, Mumbai, Maharashtra, India – 4000063

  • Privacy Statement
  • Terms of Use
  • Write For Us

© 2026 The Cyber Express - Cybersecurity News and Magazine.

Welcome Back!

Login to your account below

Forgotten Password?

Retrieve your password

Please enter your username or email address to reset your password.

Log In

Add New Playlist

No Result
View All Result
  • Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board

© 2026 The Cyber Express - Cybersecurity News and Magazine.

Are you sure want to unlock this post?
Unlock left : 0
Are you sure want to cancel subscription?
-
00:00
00:00

Queue

Update Required Flash plugin
-
00:00
00:00
Do This on Telegram, Your Bank Account Will Become Zero If You Install the iOS 18 Beta, Your iPhone Could Be Hacked Cricket World Cup Ticketing Systems Under Cybersecurity Cyber Threats and Online Ticket Scams During the NBA Finals Biometric Data Security: Protecting Sensitive Information