



















• Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
The Cyber Express
  • MagazineDownload
  • Firewall Daily
    • All
    • Bug Bounty & Rewards
    • Dark Web News
    • Data Breach News
    • Hacker News
    • Ransomware News
    • Vulnerabilities
    weekly roundup

    The Cyber Express Weekly Roundup: FBI Blames North Korea for $6B Binance Hack, Hackers Turn Up the Heat on Europe’s Fridges and More

    Stockal cyberattack

    Stockal Confirms Unauthorized Trades in 13 Customer Accounts

    Alpine Linux servers

    Alpine Linux SSH Flaw Lets Attackers Log In Without a Password

    Queens Public Library ransomware attack

    Ransomware Just Took New York’s Queens Library Offline, and It’s Not the First

    Amadeus cybersecurity incident

    Airline Data Breach Widens as Singapore Airlines Reports 46,000 Affected Records

    refrigeration cyberattacks

    After Supermarket Freezers, Hackers Turn Up the Heat on France’s Blood Supply

    university supercomputer hacking

    Two Canadians Accused of Turning US University Supercomputers Into Crypto Miners

    investment fraud

    Europol Seizes 100+ Servers Running Fake Trading Platforms

    UTA cyberattack

    UTA Investigates Suspected Cyberattack After MachForms Service Disruption

    Trending Tags

    • blackbyte ransomware
    • Ransomware
    • lapsus$ ransomware
    • Apple
    • Apple vulnerability
  • Essentials
    • All
    • Compliance
    • Governance
    • Policy Updates
    • Regulations
    ASD Essentials

    The Essential Eight Is Being Replaced: What Australian Organisations Need to Know

    SICW 2026

    AI Is Now Fighting on Both Sides of the Cyber War, Singapore Warns

    Morocco cybersecurity strategy

    Morocco Flags AI Threats, Prioritizes Critical Infrastructure Defense

    European Police Chiefs Convention 2026

    Europe’s Police Chiefs Face Growing Threat of AI-Driven Crime

    AI service security

    Hackers Are Stealing AI Keys. The Cost Can Reach $600,000

    AI security risks

    Sam Altman at UN Security Council: 6 AI Security Risks the World Cannot Ignore

    AI-enabled cyber attacks

    AI Gives Hackers an Edge Defenders Still Can’t Match, NCSC Warns

    Fraudulent SIM cards

    India’s DoT Warns Citizens Over SIM Fraud and IMEI Tampering

    EU cybersecurity incidents

    EU Cybersecurity Response Hampered by Critical Information Gaps

    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
    • All
    • How to
    • What is
    Infostealer Intelligence

    The 2026 Infostealer Intelligence Shortlist: Top 10 Vendors Security Teams Should Know

    Google Chrome

    How to Remove Saved Passwords From Google Chrome (And Why You Should)

    DPDP Rules, Cyble, DPDP Act, Cyble Vantage

    How Cyble’s Front-Row Vantage Can Help You in Complying to India’s DPDP Act

    Cybersecurity Countries

    The Top 8 Countries Leading the Cyber Defense Race in 2025

    link building

    The Link Building Secrets Your Competitors Don’t Want You to Know

    Supply Chain Attack

    Supply Chain Resilience and Physical Security: Lessons for 2025

    Healthcare cybersecurity trends of 2024

    Healthcare Cybersecurity: 2024 Was Tough, 2025 May Be Better

    CEO's Guide to Take-Down Services

    Shield Your Organization: CEO’s Perspective on Take-Down Services

    Azure sign-in Microsoft

    Microsoft Announces Mandatory MFA for Azure Sign-ins to Bolster Cloud Defenses

  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • All
    • Appointments
    • Budgets
    • Mergers & Aquisitions
    • Partnerships
    • Press Release
    • Startups
    Kerala Police Signs MoU With Cyble

    Kerala Police Signs MoU With Cyble to Use Threat Intelligence in Cybercrime Probes

    Gemini 4 Argon

    Gemini 4 Argon Restricted Over Cybersecurity Misuse Risks

    weekly roundup September 18 2026

    The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

    threat intelligence

    Cyble, UAE Cyber Security Council Unite Against Rising Cyber Threats

    Ukraine cybersecurity

    Zelensky Appoints Ihor Klymenko to Lead Ukraine’s Cybersecurity Center

    UK cyberattack rate

    UK Small Firms Bear Brunt of Rising Cyberattacks, Hiscox Finds

    Cyber Yodha Campaign

    Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

    UK Ukraine AI partnership

    Britain Gains Access to Ukraine’s ‘Goldmine’ of Battlefield AI Data

    Hims & Hers lawsuit

    FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices

    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
No Result
View All Result
  • MagazineDownload
  • Firewall Daily
    • All
    • Bug Bounty & Rewards
    • Dark Web News
    • Data Breach News
    • Hacker News
    • Ransomware News
    • Vulnerabilities
    weekly roundup

    The Cyber Express Weekly Roundup: FBI Blames North Korea for $6B Binance Hack, Hackers Turn Up the Heat on Europe’s Fridges and More

    Stockal cyberattack

    Stockal Confirms Unauthorized Trades in 13 Customer Accounts

    Alpine Linux servers

    Alpine Linux SSH Flaw Lets Attackers Log In Without a Password

    Queens Public Library ransomware attack

    Ransomware Just Took New York’s Queens Library Offline, and It’s Not the First

    Amadeus cybersecurity incident

    Airline Data Breach Widens as Singapore Airlines Reports 46,000 Affected Records

    refrigeration cyberattacks

    After Supermarket Freezers, Hackers Turn Up the Heat on France’s Blood Supply

    university supercomputer hacking

    Two Canadians Accused of Turning US University Supercomputers Into Crypto Miners

    investment fraud

    Europol Seizes 100+ Servers Running Fake Trading Platforms

    UTA cyberattack

    UTA Investigates Suspected Cyberattack After MachForms Service Disruption

    Trending Tags

    • blackbyte ransomware
    • Ransomware
    • lapsus$ ransomware
    • Apple
    • Apple vulnerability
  • Essentials
    • All
    • Compliance
    • Governance
    • Policy Updates
    • Regulations
    ASD Essentials

    The Essential Eight Is Being Replaced: What Australian Organisations Need to Know

    SICW 2026

    AI Is Now Fighting on Both Sides of the Cyber War, Singapore Warns

    Morocco cybersecurity strategy

    Morocco Flags AI Threats, Prioritizes Critical Infrastructure Defense

    European Police Chiefs Convention 2026

    Europe’s Police Chiefs Face Growing Threat of AI-Driven Crime

    AI service security

    Hackers Are Stealing AI Keys. The Cost Can Reach $600,000

    AI security risks

    Sam Altman at UN Security Council: 6 AI Security Risks the World Cannot Ignore

    AI-enabled cyber attacks

    AI Gives Hackers an Edge Defenders Still Can’t Match, NCSC Warns

    Fraudulent SIM cards

    India’s DoT Warns Citizens Over SIM Fraud and IMEI Tampering

    EU cybersecurity incidents

    EU Cybersecurity Response Hampered by Critical Information Gaps

    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
    • All
    • How to
    • What is
    Infostealer Intelligence

    The 2026 Infostealer Intelligence Shortlist: Top 10 Vendors Security Teams Should Know

    Google Chrome

    How to Remove Saved Passwords From Google Chrome (And Why You Should)

    DPDP Rules, Cyble, DPDP Act, Cyble Vantage

    How Cyble’s Front-Row Vantage Can Help You in Complying to India’s DPDP Act

    Cybersecurity Countries

    The Top 8 Countries Leading the Cyber Defense Race in 2025

    link building

    The Link Building Secrets Your Competitors Don’t Want You to Know

    Supply Chain Attack

    Supply Chain Resilience and Physical Security: Lessons for 2025

    Healthcare cybersecurity trends of 2024

    Healthcare Cybersecurity: 2024 Was Tough, 2025 May Be Better

    CEO's Guide to Take-Down Services

    Shield Your Organization: CEO’s Perspective on Take-Down Services

    Azure sign-in Microsoft

    Microsoft Announces Mandatory MFA for Azure Sign-ins to Bolster Cloud Defenses

  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • All
    • Appointments
    • Budgets
    • Mergers & Aquisitions
    • Partnerships
    • Press Release
    • Startups
    Kerala Police Signs MoU With Cyble

    Kerala Police Signs MoU With Cyble to Use Threat Intelligence in Cybercrime Probes

    Gemini 4 Argon

    Gemini 4 Argon Restricted Over Cybersecurity Misuse Risks

    weekly roundup September 18 2026

    The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

    threat intelligence

    Cyble, UAE Cyber Security Council Unite Against Rising Cyber Threats

    Ukraine cybersecurity

    Zelensky Appoints Ihor Klymenko to Lead Ukraine’s Cybersecurity Center

    UK cyberattack rate

    UK Small Firms Bear Brunt of Rising Cyberattacks, Hiscox Finds

    Cyber Yodha Campaign

    Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

    UK Ukraine AI partnership

    Britain Gains Access to Ukraine’s ‘Goldmine’ of Battlefield AI Data

    Hims & Hers lawsuit

    FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices

    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
No Result
View All Result
The Cyber Express
No Result
View All Result

MiningDropper Turns Android Apps Into Multi-Stage Malware Delivery Systems

Ashish Khaitan by Ashish Khaitan
April 16, 2026
in Firewall Daily, Cyber News, Dark Web News
0
MiningDropper
585
SHARES
3.2k
VIEWS
Share on LinkedInShare on Twitter

Researchers have uncovered an Android malware framework dubbed the MiningDropper. Security researchers at Cyble Research and Intelligence Labs (CRIL) have identified a sharp increase in campaigns using MiningDropper, a modular platform capable of distributing multiple types of malicious payloads, including cryptocurrency miners, infostealers, Remote Access Trojans (RATs), and banking malware.  

A notable aspect of this campaign is its abuse of the open-source Lumolight application, which has been repurposed as a trojanized entry point. 

A Modular Android Malware Framework at Scale

MiningDropper is not a conventional malware strain. Instead, it operates as a multi-stage delivery framework designed to evade detection and dynamically deploy payloads. Its architecture integrates XOR-based obfuscation, AES-encrypted payload staging, dynamic DEX loading, and anti-emulation techniques. These layers collectively delay analysis and reduce the likelihood of detection by traditional antivirus solutions. 

Over 1,500 MiningDropper samples have been observed in the wild within a single month, with more than 50% showing minimal antivirus detection. Notably, around 668 samples registered only three antivirus detections, indicating widespread distribution with low visibility. 

Lumolight as the Initial Infection Vector 

A recent variant of MiningDropper uses a trojanized version of Lumolight as its initial payload. Victims unknowingly install this compromised application through phishing links, fraudulent websites, or social media campaigns. Once installed, the malicious application triggers a native library, “librequisitionerastomous.so”, which begins the execution chain.

This native layer decrypts XOR-obfuscated strings at runtime and checks whether the app is running in an emulator or rooted environment. If such conditions are detected, the malware halts execution to avoid analysis. Otherwise, it proceeds to decrypt and load the first-stage payload from the app’s assets. 

Multi-Stage Payload Delivery Mechanism 
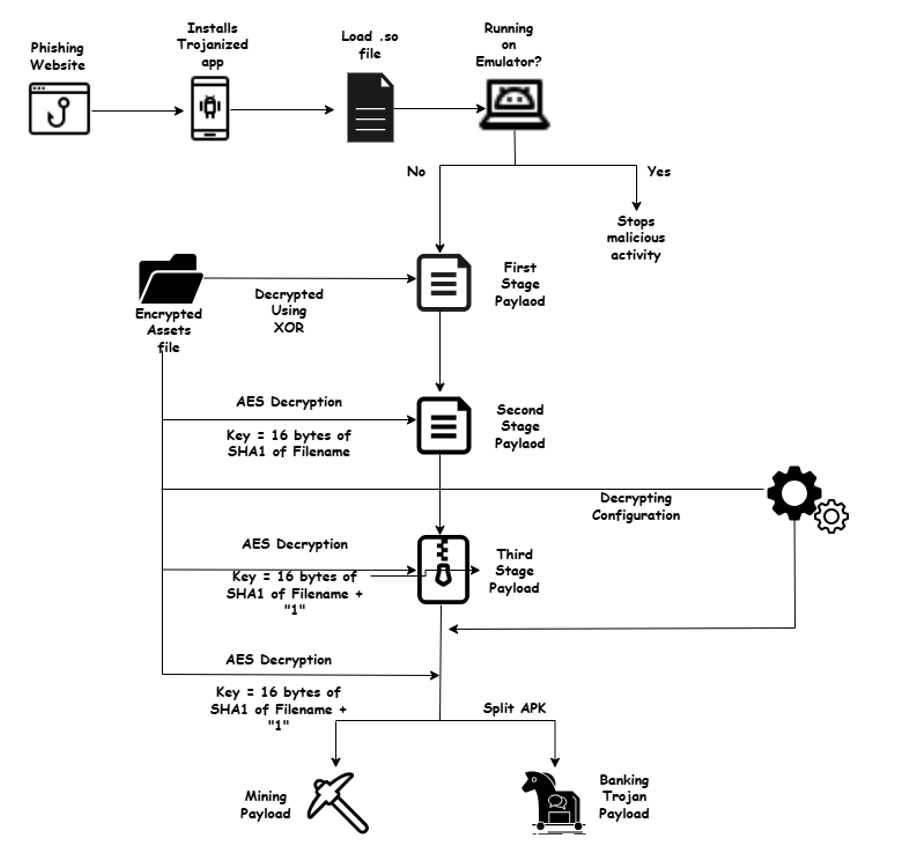
MiningDropper attack chain
MiningDropper attack chain (Source: Cyble)

MiningDropper’s infection chain unfolds across multiple stages: 

  • Initial Stage: The native code decrypts an embedded asset using a hardcoded XOR key, producing a DEX file. This file is dynamically loaded using DexClassLoader and executes a bootstrap component. 
  • First Stage: The bootstrap loader decrypts a second-stage payload using AES encryption. The AES key is derived from the SHA-1 hash of the file name, making it harder for analysts to extract static keys. 
  • Second Stage: This stage presents a fake Google Play update interface, a social engineering tactic designed to maintain user trust. Behind the scenes, it decrypts additional payloads and configuration files. The malware can operate in two modes: a cryptocurrency miner or a user-defined malicious payload. 

Configuration files such as “norweyanlinkediting” (miner path) and “udela” (user payload path) dictate the behavior. These configurations include parameters like remote control capabilities, payload splits, and subscription timelines. 

  • Third Stage: The malware extracts a ZIP archive containing further DEX files and native libraries. Acting as a split-APK installer, it reconstructs and installs the final payload based on the configuration. 

Campaigns Targeting Multiple Regions 

CRIL identified two primary campaign clusters leveraging MiningDropper: 

  • Infostealer Campaign (India): This campaign targets Indian users by impersonating trusted entities such as Regional Transport Office (RTO) services, banks, telecom providers, and popular apps. In October 2025, a campaign using RTO-themed lures distributed malicious APK files that ultimately deployed infostealers to harvest sensitive financial and personal data. 
  • BTMOB RAT Campaign (Global): Another campaign distributes MiningDropper across Europe, Latin America, and Asia. In this case, the final payload is BTMOB RAT, a powerful Android trojan first identified in February 2024 as a variant of SpySolr malware. It supports credential theft, real-time remote control, device takeover, and financial fraud operations. 

Interestingly, while BTMOB RAT was initially distributed without obfuscation and detected by multiple antivirus engines, its integration with MiningDropper has reduced detection rates to as low as one to three engines. 

Final Payload Capabilities 

The final payload delivered by MiningDropper depends on the configuration: 

  • Infostealers: Extract sensitive data such as login credentials and financial information.
  • RATs (e.g., BTMOB RAT): Enable full device compromise, including screen monitoring, file access, audio recording, and command execution via WebSocket-based communication.
  • Banking Trojans: Facilitate financial fraud through credential harvesting and transaction manipulation. 
  • Cryptocurrency Miners: Utilize device resources for unauthorized mining operations.

The malware also abuses Android Accessibility Services to gain extensive control over infected devices, allowing it to simulate user interactions and grant additional permissions. 

A Scalable Malware-as-a-Framework Model 

MiningDropper demonstrates a shift toward malware frameworks that prioritize scalability and adaptability. Its ability to switch between payloads using configuration changes, without altering the core architecture, makes it highly reusable across campaigns. This modularity enables threat actors to rapidly expand operations while maintaining low detection rates. 

MiningDropper is more than just another Android malware strain. By combining advanced obfuscation, multi-stage execution, and the exploitation of legitimate projects like Lumolight, it represents a threat model capable of sustaining large-scale, global campaigns.
Share this:

  • Share on LinkedIn (Opens in new window) LinkedIn
  • Share on Reddit (Opens in new window) Reddit
  • Share on X (Opens in new window) X
  • Share on Facebook (Opens in new window) Facebook
  • More
  • Email a link to a friend (Opens in new window) Email
  • Share on WhatsApp (Opens in new window) WhatsApp

Related

Tags: Android Malwarebanking malwareLumolightMiningDropperThe Cyber ExpressThe Cyber Express News
Previous Post

Age Verification App Set for Rollout as EU Tightens Child Protection Online

Next Post

Targeted Cyberattack on Northern Ireland Schools Exposes Personal Data

Next Post
Education Authority cyberattack

Targeted Cyberattack on Northern Ireland Schools Exposes Personal Data

Q1 2026 Threat Reports

❮ ❯
Cyble-Vision


Follow Us On Google News

Categories

  • Privacy Statement
  • Terms of Use
  • Write For Us

© 2026 The Cyber Express - Cybersecurity News and Magazine.

Welcome Back!

Login to your account below

Forgotten Password?

Retrieve your password

Please enter your username or email address to reset your password.

Log In

Add New Playlist

No Result
View All Result
  • Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board

© 2026 The Cyber Express - Cybersecurity News and Magazine.

-
00:00
00:00

Queue

Update Required Flash plugin
-
00:00
00:00



