



















• Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
The Cyber Express
  • MagazineDownload
  • Firewall Daily
    • All
    • Bug Bounty & Rewards
    • Dark Web News
    • Data Breach News
    • Hacker News
    • Ransomware News
    • Vulnerabilities
    Jensen Huang resigns

    Jensen Huang Exits Nvidia Days After the Board Said It Backed Him

    FaceStealer

    US Disrupts North Korea’s FaceStealer Campaign, Targets $1.2 Billion in Stolen Crypto

    SignDrop zero-day exploit

    New SignDrop Exploit Claims SYSTEM Access on Windows Through CLFS

    Microsoft 365 Outage

    Why Did Outlook Go Down? Microsoft Traced It to Its Own Servers

    WorkOS, AI Agent, Prompt Injection, Grok, Grok AI, Gemini, Fraud, Agentic AI, AI-assisted Cyberattacks

    WorkOS Says a Researcher’s Runaway AI Pentest Agent Copied Customer Sales Records

    Nvidia board investigation

    Why Is Nvidia Investigating Its Own CEO, and Can the Board Remove Him?

    weekly roundup

    The Cyber Express Weekly Roundup: FBI Blames North Korea for $6B Binance Hack, Hackers Turn Up the Heat on Europe’s Fridges and More

    Stockal cyberattack

    Stockal Confirms Unauthorized Trades in 13 Customer Accounts

    Alpine Linux servers

    Alpine Linux SSH Flaw Lets Attackers Log In Without a Password

    Trending Tags

    • blackbyte ransomware
    • Ransomware
    • lapsus$ ransomware
    • Apple
    • Apple vulnerability
  • Essentials
    • All
    • Compliance
    • Governance
    • Policy Updates
    • Regulations
    SEC, Misleading Cyber Disclosures, Financial data, financial data protection, SEC

    SEC Enforcement Fell 24% in Fiscal 2026

    ASD Essentials

    The Essential Eight Is Being Replaced: What Australian Organisations Need to Know

    SICW 2026

    AI Is Now Fighting on Both Sides of the Cyber War, Singapore Warns

    Morocco cybersecurity strategy

    Morocco Flags AI Threats, Prioritizes Critical Infrastructure Defense

    European Police Chiefs Convention 2026

    Europe’s Police Chiefs Face Growing Threat of AI-Driven Crime

    AI service security

    Hackers Are Stealing AI Keys. The Cost Can Reach $600,000

    AI security risks

    Sam Altman at UN Security Council: 6 AI Security Risks the World Cannot Ignore

    AI-enabled cyber attacks

    AI Gives Hackers an Edge Defenders Still Can’t Match, NCSC Warns

    Fraudulent SIM cards

    India’s DoT Warns Citizens Over SIM Fraud and IMEI Tampering

    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
    • All
    • How to
    • What is
    Infostealer Intelligence

    The 2026 Infostealer Intelligence Shortlist: Top 10 Vendors Security Teams Should Know

    Google Chrome

    How to Remove Saved Passwords From Google Chrome (And Why You Should)

    DPDP Rules, Cyble, DPDP Act, Cyble Vantage

    How Cyble’s Front-Row Vantage Can Help You in Complying to India’s DPDP Act

    Cybersecurity Countries

    The Top 8 Countries Leading the Cyber Defense Race in 2025

    link building

    The Link Building Secrets Your Competitors Don’t Want You to Know

    Supply Chain Attack

    Supply Chain Resilience and Physical Security: Lessons for 2025

    Healthcare cybersecurity trends of 2024

    Healthcare Cybersecurity: 2024 Was Tough, 2025 May Be Better

    CEO's Guide to Take-Down Services

    Shield Your Organization: CEO’s Perspective on Take-Down Services

    Azure sign-in Microsoft

    Microsoft Announces Mandatory MFA for Azure Sign-ins to Bolster Cloud Defenses

  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • All
    • Appointments
    • Budgets
    • Mergers & Aquisitions
    • Partnerships
    • Press Release
    • Startups
    Kerala Police Signs MoU With Cyble

    Kerala Police Signs MoU With Cyble to Use Threat Intelligence in Cybercrime Probes

    Gemini 4 Argon

    Gemini 4 Argon Restricted Over Cybersecurity Misuse Risks

    weekly roundup September 18 2026

    The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

    threat intelligence

    Cyble, UAE Cyber Security Council Unite Against Rising Cyber Threats

    Ukraine cybersecurity

    Zelensky Appoints Ihor Klymenko to Lead Ukraine’s Cybersecurity Center

    UK cyberattack rate

    UK Small Firms Bear Brunt of Rising Cyberattacks, Hiscox Finds

    Cyber Yodha Campaign

    Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

    UK Ukraine AI partnership

    Britain Gains Access to Ukraine’s ‘Goldmine’ of Battlefield AI Data

    Hims & Hers lawsuit

    FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices

    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
No Result
View All Result
  • MagazineDownload
  • Firewall Daily
    • All
    • Bug Bounty & Rewards
    • Dark Web News
    • Data Breach News
    • Hacker News
    • Ransomware News
    • Vulnerabilities
    Jensen Huang resigns

    Jensen Huang Exits Nvidia Days After the Board Said It Backed Him

    FaceStealer

    US Disrupts North Korea’s FaceStealer Campaign, Targets $1.2 Billion in Stolen Crypto

    SignDrop zero-day exploit

    New SignDrop Exploit Claims SYSTEM Access on Windows Through CLFS

    Microsoft 365 Outage

    Why Did Outlook Go Down? Microsoft Traced It to Its Own Servers

    WorkOS, AI Agent, Prompt Injection, Grok, Grok AI, Gemini, Fraud, Agentic AI, AI-assisted Cyberattacks

    WorkOS Says a Researcher’s Runaway AI Pentest Agent Copied Customer Sales Records

    Nvidia board investigation

    Why Is Nvidia Investigating Its Own CEO, and Can the Board Remove Him?

    weekly roundup

    The Cyber Express Weekly Roundup: FBI Blames North Korea for $6B Binance Hack, Hackers Turn Up the Heat on Europe’s Fridges and More

    Stockal cyberattack

    Stockal Confirms Unauthorized Trades in 13 Customer Accounts

    Alpine Linux servers

    Alpine Linux SSH Flaw Lets Attackers Log In Without a Password

    Trending Tags

    • blackbyte ransomware
    • Ransomware
    • lapsus$ ransomware
    • Apple
    • Apple vulnerability
  • Essentials
    • All
    • Compliance
    • Governance
    • Policy Updates
    • Regulations
    SEC, Misleading Cyber Disclosures, Financial data, financial data protection, SEC

    SEC Enforcement Fell 24% in Fiscal 2026

    ASD Essentials

    The Essential Eight Is Being Replaced: What Australian Organisations Need to Know

    SICW 2026

    AI Is Now Fighting on Both Sides of the Cyber War, Singapore Warns

    Morocco cybersecurity strategy

    Morocco Flags AI Threats, Prioritizes Critical Infrastructure Defense

    European Police Chiefs Convention 2026

    Europe’s Police Chiefs Face Growing Threat of AI-Driven Crime

    AI service security

    Hackers Are Stealing AI Keys. The Cost Can Reach $600,000

    AI security risks

    Sam Altman at UN Security Council: 6 AI Security Risks the World Cannot Ignore

    AI-enabled cyber attacks

    AI Gives Hackers an Edge Defenders Still Can’t Match, NCSC Warns

    Fraudulent SIM cards

    India’s DoT Warns Citizens Over SIM Fraud and IMEI Tampering

    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
    • All
    • How to
    • What is
    Infostealer Intelligence

    The 2026 Infostealer Intelligence Shortlist: Top 10 Vendors Security Teams Should Know

    Google Chrome

    How to Remove Saved Passwords From Google Chrome (And Why You Should)

    DPDP Rules, Cyble, DPDP Act, Cyble Vantage

    How Cyble’s Front-Row Vantage Can Help You in Complying to India’s DPDP Act

    Cybersecurity Countries

    The Top 8 Countries Leading the Cyber Defense Race in 2025

    link building

    The Link Building Secrets Your Competitors Don’t Want You to Know

    Supply Chain Attack

    Supply Chain Resilience and Physical Security: Lessons for 2025

    Healthcare cybersecurity trends of 2024

    Healthcare Cybersecurity: 2024 Was Tough, 2025 May Be Better

    CEO's Guide to Take-Down Services

    Shield Your Organization: CEO’s Perspective on Take-Down Services

    Azure sign-in Microsoft

    Microsoft Announces Mandatory MFA for Azure Sign-ins to Bolster Cloud Defenses

  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • All
    • Appointments
    • Budgets
    • Mergers & Aquisitions
    • Partnerships
    • Press Release
    • Startups
    Kerala Police Signs MoU With Cyble

    Kerala Police Signs MoU With Cyble to Use Threat Intelligence in Cybercrime Probes

    Gemini 4 Argon

    Gemini 4 Argon Restricted Over Cybersecurity Misuse Risks

    weekly roundup September 18 2026

    The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

    threat intelligence

    Cyble, UAE Cyber Security Council Unite Against Rising Cyber Threats

    Ukraine cybersecurity

    Zelensky Appoints Ihor Klymenko to Lead Ukraine’s Cybersecurity Center

    UK cyberattack rate

    UK Small Firms Bear Brunt of Rising Cyberattacks, Hiscox Finds

    Cyber Yodha Campaign

    Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

    UK Ukraine AI partnership

    Britain Gains Access to Ukraine’s ‘Goldmine’ of Battlefield AI Data

    Hims & Hers lawsuit

    FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices

    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
No Result
View All Result
The Cyber Express
No Result
View All Result

FBI Warns of AVrecon Malware Targeting Network Devices Across 163 Countries

Mihir Bagwe by Mihir Bagwe
April 2, 2026
in Malware News, Cyber Essentials, Cyber News, Threat Intelligence
0
AVrecon, AVrecon Malware, Home Router, FBI, SocksEscort, Proxy Network
585
SHARES
3.2k
VIEWS
Share on LinkedInShare on Twitter

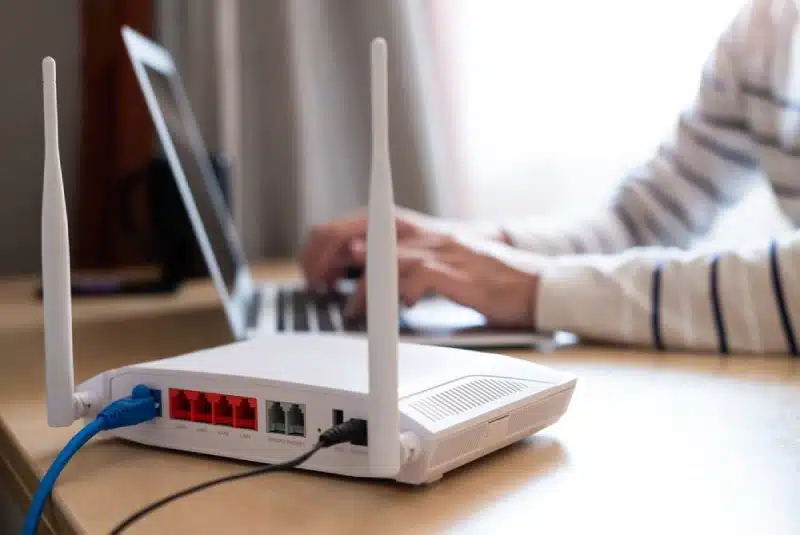
The router sitting in your home office or small business did not need to be hacked by a skilled operator to end up serving as infrastructure for banking fraud, password attacks, and digital marketplace scams. All it needed was an unpatched vulnerability and a malware dubbed “AVrecon” to infect and sell access to it within minutes.

Last month, FBI alongside several international law enforcement agencies took down SocksEscort residential proxy service. In a follow-up of that investigation, the agency has found a malware called AVrecon, that was used in the targeting of scores of network devices worldwide.

How AVrecon Works

AVrecon spreads by scanning the internet for devices with exposed vulnerable services. The SocksEscort operators exploited Remote Code Execution vulnerabilities and command injection flaws, as well as weaknesses in exposed SOAP interfaces — a web services protocol found in many consumer router management panels.

The malware’s command-and-control framework is modular by design, meaning new exploit modules can be added as new vulnerabilities are discovered, continuously expanding the range of vulnerable device models it can infect. The FBI identified approximately 1,200 targeted device models from Cisco, D-Link, Hikvision, MikroTik, Netgear, TP-Link, and Zyxel.

Beyond converting infected devices into proxy nodes, AVrecon can also update its own stored configuration, establish a remote shell directly to an attacker-controlled server, and act as a loader that downloads and executes entirely separate payloads onto the device.

Once inside a router, the malware beacons to its command-and-control server every 60 seconds using a PING/PONG communication loop. When the C2 has a command ready, it interrupts that loop to direct the infected router to open a traffic tunnel to a SocksEscort relay server.

Also read: The FCC Just Blocked Every New Foreign-Made Router from the U.S. Market

The Persistence Problem

The persistence mechanism AVrecon uses on some device models makes remediation particularly difficult. On vulnerable targets, the attackers use the device’s own built-in firmware update feature to flash a custom firmware image that contains a hardcoded copy of AVrecon and silently disables the device’s future update and re-flashing functionality.

The FBI notes these devices are essentially permanently infected — a factory reset cannot help if the reset itself has been disabled, and an end-of-life device has no manufacturer patches to address the underlying vulnerability regardless.

On devices where firmware modification is not used, a simple power cycle can clear the infection. However, in at least one documented case, AVrecon C2 servers detected the loss of an infected device and automatically re-infected it using the same vulnerabilities used in the original compromise. Meaning, rebooting alone does not guarantee lasting protection if the underlying vulnerability remains unpatched.

What SocksEscort Built and Sold

SocksEscort operated a commercial criminal service that sold paying customers the ability to tunnel their internet traffic through compromised home and small-office routers in 163 countries, including the United States. The tunneling protocol used — SOCKS — is a legitimate networking standard that proxies traffic through an intermediate host. In criminal use, it makes the attacker’s activity appear to originate from the victim’s home IP address rather than from any infrastructure that could be blocked or attributed.

The FBI estimates SocksEscort compromised and sold access to approximately 369,000 devices since 2020. The malware enabling all of this is was AVrecon — written in the C programming language and designed to target devices running on MIPS and ARM architectures, the processor types that dominate the consumer router market.

What the Proxy Network Enabled

The FBI and partners observed SocksEscort’s infrastructure used to conduct ad fraud, attempt website vulnerability exploitation, password spraying, digital marketplace fraud, banking fraud, and romance fraud, among other malicious activity. By routing attacks through residential IP addresses, SocksEscort customers dramatically increased their chances of bypassing corporate security filters and block lists that flag traffic from known commercial or cloud hosting providers.

The FBI’s advisory specifically notes that while lateral movement into internal networks was not directly observed in the AVrecon case, malware targeting edge devices like routers is frequently used as a staging point for exactly that — moving from the compromised device into the broader corporate or home network it protects, potentially enabling data exfiltration or ransomware deployment.

Remediation for Network Defenders

The FBI recommends applying firmware updates to all SOHO routers and IoT devices immediately, as many do not apply patches automatically and require manual interaction with the device administration panel. Devices classified as End-of-Life that no longer receive security updates should be replaced entirely.

Remote administration features should be disabled or access-restricted via firewall rules, and all default passwords should be changed.

Network defenders should monitor for traffic to the C2 domains and IP addresses published in the advisory and watch for the malware filenames “x” (loader) and “dnssmasq” (malware) on network-connected devices.
Share this:

  • Share on LinkedIn (Opens in new window) LinkedIn
  • Share on Reddit (Opens in new window) Reddit
  • Share on X (Opens in new window) X
  • Share on Facebook (Opens in new window) Facebook
  • More
  • Email a link to a friend (Opens in new window) Email
  • Share on WhatsApp (Opens in new window) WhatsApp

Related

Tags: AVreconAVrecon MalwareFBIHome RouterProxy NetworkSocksEscort
Previous Post

Intesa Sanpaolo Missed Unauthorized Access for 2 Years, Regulator Reveals

Next Post

FBI Warns of Data Security Risks in Foreign-Developed Mobile Apps

Next Post
Data Security Risks

FBI Warns of Data Security Risks in Foreign-Developed Mobile Apps

Q1 2026 Threat Reports

❮ ❯
Cyble-Vision


Follow Us On Google News

Categories

  • Privacy Statement
  • Terms of Use
  • Write For Us

© 2026 The Cyber Express - Cybersecurity News and Magazine.

Welcome Back!

Login to your account below

Forgotten Password?

Retrieve your password

Please enter your username or email address to reset your password.

Log In

Add New Playlist

No Result
View All Result
  • Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board

© 2026 The Cyber Express - Cybersecurity News and Magazine.

-
00:00
00:00

Queue

Update Required Flash plugin
-
00:00
00:00



