



















• Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
The Cyber Express
  • MagazineDownload
  • Firewall Daily
    • All
    • Bug Bounty & Rewards
    • Dark Web News
    • Data Breach News
    • Hacker News
    • Ransomware News
    • Vulnerabilities
    weekly roundup

    The Cyber Express Weekly Roundup: FBI Blames North Korea for $6B Binance Hack, Hackers Turn Up the Heat on Europe’s Fridges and More

    Stockal cyberattack

    Stockal Confirms Unauthorized Trades in 13 Customer Accounts

    Alpine Linux servers

    Alpine Linux SSH Flaw Lets Attackers Log In Without a Password

    Queens Public Library ransomware attack

    Ransomware Just Took New York’s Queens Library Offline, and It’s Not the First

    Amadeus cybersecurity incident

    Airline Data Breach Widens as Singapore Airlines Reports 46,000 Affected Records

    refrigeration cyberattacks

    After Supermarket Freezers, Hackers Turn Up the Heat on France’s Blood Supply

    university supercomputer hacking

    Two Canadians Accused of Turning US University Supercomputers Into Crypto Miners

    investment fraud

    Europol Seizes 100+ Servers Running Fake Trading Platforms

    UTA cyberattack

    UTA Investigates Suspected Cyberattack After MachForms Service Disruption

    Trending Tags

    • blackbyte ransomware
    • Ransomware
    • lapsus$ ransomware
    • Apple
    • Apple vulnerability
  • Essentials
    • All
    • Compliance
    • Governance
    • Policy Updates
    • Regulations
    ASD Essentials

    The Essential Eight Is Being Replaced: What Australian Organisations Need to Know

    SICW 2026

    AI Is Now Fighting on Both Sides of the Cyber War, Singapore Warns

    Morocco cybersecurity strategy

    Morocco Flags AI Threats, Prioritizes Critical Infrastructure Defense

    European Police Chiefs Convention 2026

    Europe’s Police Chiefs Face Growing Threat of AI-Driven Crime

    AI service security

    Hackers Are Stealing AI Keys. The Cost Can Reach $600,000

    AI security risks

    Sam Altman at UN Security Council: 6 AI Security Risks the World Cannot Ignore

    AI-enabled cyber attacks

    AI Gives Hackers an Edge Defenders Still Can’t Match, NCSC Warns

    Fraudulent SIM cards

    India’s DoT Warns Citizens Over SIM Fraud and IMEI Tampering

    EU cybersecurity incidents

    EU Cybersecurity Response Hampered by Critical Information Gaps

    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
    • All
    • How to
    • What is
    Infostealer Intelligence

    The 2026 Infostealer Intelligence Shortlist: Top 10 Vendors Security Teams Should Know

    Google Chrome

    How to Remove Saved Passwords From Google Chrome (And Why You Should)

    DPDP Rules, Cyble, DPDP Act, Cyble Vantage

    How Cyble’s Front-Row Vantage Can Help You in Complying to India’s DPDP Act

    Cybersecurity Countries

    The Top 8 Countries Leading the Cyber Defense Race in 2025

    link building

    The Link Building Secrets Your Competitors Don’t Want You to Know

    Supply Chain Attack

    Supply Chain Resilience and Physical Security: Lessons for 2025

    Healthcare cybersecurity trends of 2024

    Healthcare Cybersecurity: 2024 Was Tough, 2025 May Be Better

    CEO's Guide to Take-Down Services

    Shield Your Organization: CEO’s Perspective on Take-Down Services

    Azure sign-in Microsoft

    Microsoft Announces Mandatory MFA for Azure Sign-ins to Bolster Cloud Defenses

  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • All
    • Appointments
    • Budgets
    • Mergers & Aquisitions
    • Partnerships
    • Press Release
    • Startups
    Kerala Police Signs MoU With Cyble

    Kerala Police Signs MoU With Cyble to Use Threat Intelligence in Cybercrime Probes

    Gemini 4 Argon

    Gemini 4 Argon Restricted Over Cybersecurity Misuse Risks

    weekly roundup September 18 2026

    The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

    threat intelligence

    Cyble, UAE Cyber Security Council Unite Against Rising Cyber Threats

    Ukraine cybersecurity

    Zelensky Appoints Ihor Klymenko to Lead Ukraine’s Cybersecurity Center

    UK cyberattack rate

    UK Small Firms Bear Brunt of Rising Cyberattacks, Hiscox Finds

    Cyber Yodha Campaign

    Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

    UK Ukraine AI partnership

    Britain Gains Access to Ukraine’s ‘Goldmine’ of Battlefield AI Data

    Hims & Hers lawsuit

    FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices

    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
No Result
View All Result
  • MagazineDownload
  • Firewall Daily
    • All
    • Bug Bounty & Rewards
    • Dark Web News
    • Data Breach News
    • Hacker News
    • Ransomware News
    • Vulnerabilities
    weekly roundup

    The Cyber Express Weekly Roundup: FBI Blames North Korea for $6B Binance Hack, Hackers Turn Up the Heat on Europe’s Fridges and More

    Stockal cyberattack

    Stockal Confirms Unauthorized Trades in 13 Customer Accounts

    Alpine Linux servers

    Alpine Linux SSH Flaw Lets Attackers Log In Without a Password

    Queens Public Library ransomware attack

    Ransomware Just Took New York’s Queens Library Offline, and It’s Not the First

    Amadeus cybersecurity incident

    Airline Data Breach Widens as Singapore Airlines Reports 46,000 Affected Records

    refrigeration cyberattacks

    After Supermarket Freezers, Hackers Turn Up the Heat on France’s Blood Supply

    university supercomputer hacking

    Two Canadians Accused of Turning US University Supercomputers Into Crypto Miners

    investment fraud

    Europol Seizes 100+ Servers Running Fake Trading Platforms

    UTA cyberattack

    UTA Investigates Suspected Cyberattack After MachForms Service Disruption

    Trending Tags

    • blackbyte ransomware
    • Ransomware
    • lapsus$ ransomware
    • Apple
    • Apple vulnerability
  • Essentials
    • All
    • Compliance
    • Governance
    • Policy Updates
    • Regulations
    ASD Essentials

    The Essential Eight Is Being Replaced: What Australian Organisations Need to Know

    SICW 2026

    AI Is Now Fighting on Both Sides of the Cyber War, Singapore Warns

    Morocco cybersecurity strategy

    Morocco Flags AI Threats, Prioritizes Critical Infrastructure Defense

    European Police Chiefs Convention 2026

    Europe’s Police Chiefs Face Growing Threat of AI-Driven Crime

    AI service security

    Hackers Are Stealing AI Keys. The Cost Can Reach $600,000

    AI security risks

    Sam Altman at UN Security Council: 6 AI Security Risks the World Cannot Ignore

    AI-enabled cyber attacks

    AI Gives Hackers an Edge Defenders Still Can’t Match, NCSC Warns

    Fraudulent SIM cards

    India’s DoT Warns Citizens Over SIM Fraud and IMEI Tampering

    EU cybersecurity incidents

    EU Cybersecurity Response Hampered by Critical Information Gaps

    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
    • All
    • How to
    • What is
    Infostealer Intelligence

    The 2026 Infostealer Intelligence Shortlist: Top 10 Vendors Security Teams Should Know

    Google Chrome

    How to Remove Saved Passwords From Google Chrome (And Why You Should)

    DPDP Rules, Cyble, DPDP Act, Cyble Vantage

    How Cyble’s Front-Row Vantage Can Help You in Complying to India’s DPDP Act

    Cybersecurity Countries

    The Top 8 Countries Leading the Cyber Defense Race in 2025

    link building

    The Link Building Secrets Your Competitors Don’t Want You to Know

    Supply Chain Attack

    Supply Chain Resilience and Physical Security: Lessons for 2025

    Healthcare cybersecurity trends of 2024

    Healthcare Cybersecurity: 2024 Was Tough, 2025 May Be Better

    CEO's Guide to Take-Down Services

    Shield Your Organization: CEO’s Perspective on Take-Down Services

    Azure sign-in Microsoft

    Microsoft Announces Mandatory MFA for Azure Sign-ins to Bolster Cloud Defenses

  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • All
    • Appointments
    • Budgets
    • Mergers & Aquisitions
    • Partnerships
    • Press Release
    • Startups
    Kerala Police Signs MoU With Cyble

    Kerala Police Signs MoU With Cyble to Use Threat Intelligence in Cybercrime Probes

    Gemini 4 Argon

    Gemini 4 Argon Restricted Over Cybersecurity Misuse Risks

    weekly roundup September 18 2026

    The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

    threat intelligence

    Cyble, UAE Cyber Security Council Unite Against Rising Cyber Threats

    Ukraine cybersecurity

    Zelensky Appoints Ihor Klymenko to Lead Ukraine’s Cybersecurity Center

    UK cyberattack rate

    UK Small Firms Bear Brunt of Rising Cyberattacks, Hiscox Finds

    Cyber Yodha Campaign

    Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

    UK Ukraine AI partnership

    Britain Gains Access to Ukraine’s ‘Goldmine’ of Battlefield AI Data

    Hims & Hers lawsuit

    FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices

    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
No Result
View All Result
The Cyber Express
No Result
View All Result

Poste Italiane, Postepay Fined €12.5M for Unlawful User Data Processing

Samiksha Jain by Samiksha Jain
April 21, 2026
in Cyber News, Firewall Daily
0
Italian Data Protection Authority fine
585
SHARES
3.2k
VIEWS
Share on LinkedInShare on Twitter

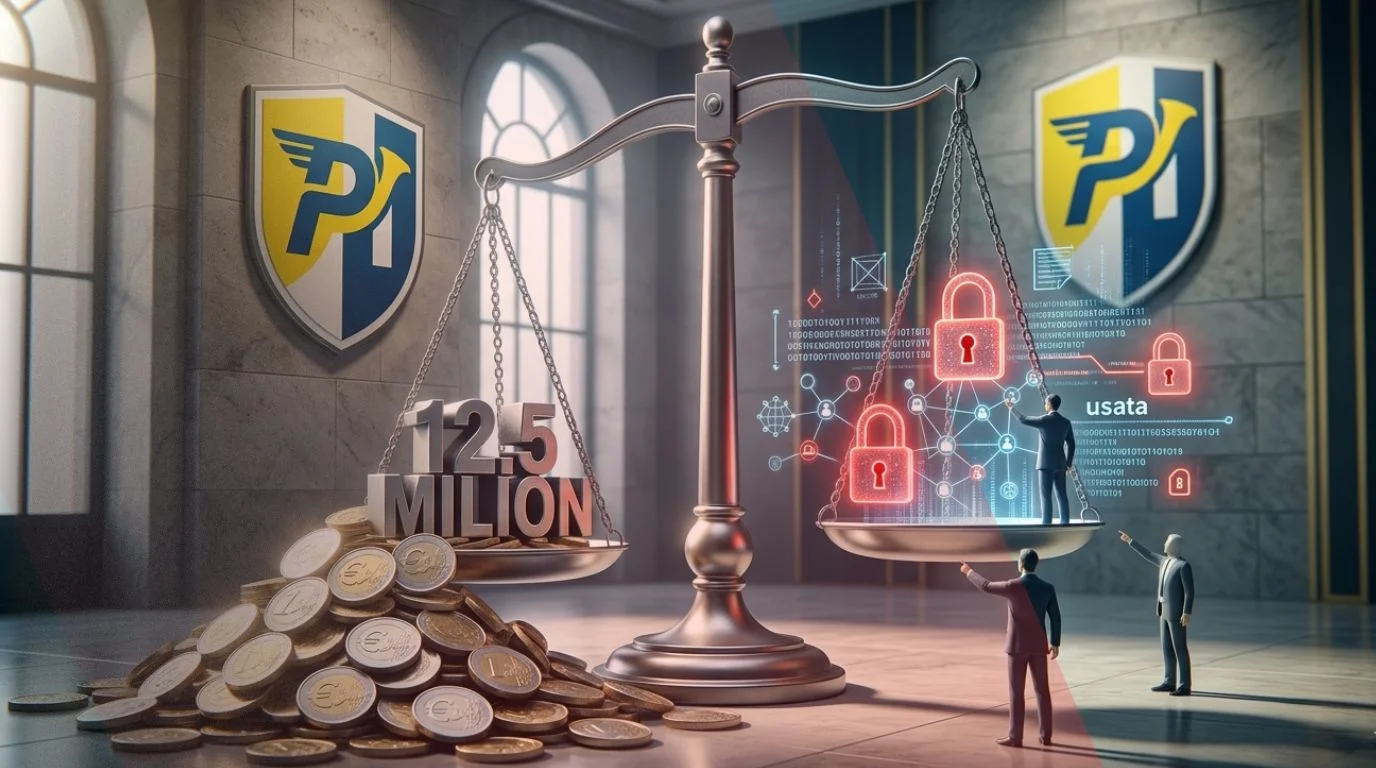
The Italian Data Protection Authority fine against Poste Italiane and Postepay has reached over €12.5 million, after regulators found unlawful processing of personal data affecting millions of users.

Italy’s Italian Data Protection Authority imposed a €6.6 million penalty on Poste Italiane and €5.8 million on Postepay. The action follows an investigation launched in April 2024 after multiple complaints from users regarding how their data was being handled through mobile applications.

Italian Data Protection Authority Fine Linked to Intrusive App Monitoring

The Italian Data Protection Authority fine centers on how BancoPosta and Postepay apps collected user data. Customers were required to allow monitoring of information stored on their devices, including details about installed and active applications.

According to the companies, this access was necessary to detect malware and prevent fraud in line with payment security requirements. However, the regulator found that the scope of monitoring went too far.

Authorities stated that the data collection methods were not proportionate and resulted in excessive intrusion into users’ private lives. The ruling emphasized that fraud prevention cannot justify blanket access to personal device data.

Multiple Compliance Failures Identified

The investigation behind the Italian Data Protection Authority fine also revealed broader compliance failures. Regulators flagged insufficient transparency in how users were informed about data collection practices.

The companies were also found to have not conducted an adequate Data Protection Impact Assessment. Such assessments are required when processing activities pose high risks to individual privacy.

Further issues included weak security measures, unclear policies on how long data was stored, and irregularities in defining data controller responsibilities. These gaps raised concerns about how user data was governed internally.

As part of the enforcement action, both companies have been ordered to stop the disputed data processing practices if still ongoing. They must also align their data retention policies with regulatory requirements and report compliance to the Authority.

Italian Regulator Steps Up Enforcement

The action reinforces a broader trend of stricter enforcement by the Italian Data Protection Authority across the financial sector. The Italian Data Protection Authority fines Poste Italiane and Postepay case follows another high-profile enforcement action earlier this year involving Intesa Sanpaolo.

In March 2026, the regulator imposed a €31.8 million penalty on the bank after uncovering serious lapses in how customer data was protected. The case involved unauthorized access to sensitive information of more than 3,500 customers over a period of more than two years.

Investigators found that a single employee had accessed customer records more than 6,600 times without any legitimate business reason. The breach went undetected for months, exposing weaknesses in the bank’s internal monitoring systems.

Insider Risks and Monitoring Gaps under Focus

The Intesa Sanpaolo case highlighted a different but equally critical issue. While Poste Italiane and Postepay were penalized for excessive data collection, the bank was fined for failing to detect misuse of legitimate access.

According to the Authority, the bank’s monitoring systems were not designed to identify slow, repeated misuse of access over time. This allowed the unauthorized activity to continue without triggering alerts, even when it involved high-risk individuals such as public figures.

Regulators concluded that the controls in place were not aligned with the risks associated with broad internal access to sensitive financial data. The case has since raised concerns about insider threats and the effectiveness of existing detection mechanisms within financial institutions.

Growing Pressure on Financial Services

Together, these cases reflect a tightening regulatory environment in Italy, where financial institutions are being held accountable for both overreach and underperformance in data protection.

The Italian Data Protection Authority fines Poste Italiane and Postepay decision highlights the importance of balancing fraud prevention measures with user privacy. Security controls must be proportionate, transparent, and supported by proper risk assessments.

At the same time, the Intesa Sanpaolo breach demonstrates that insufficient monitoring can be just as damaging, particularly when insider threats go unnoticed for extended periods.

With enforcement actions increasing in scale and frequency, organizations operating in the financial sector are facing mounting pressure to reassess their data governance frameworks. The regulator’s recent decisions make it clear that both excessive data collection and weak oversight can lead to significant financial and reputational consequences.
Share this:

  • Share on LinkedIn (Opens in new window) LinkedIn
  • Share on Reddit (Opens in new window) Reddit
  • Share on X (Opens in new window) X
  • Share on Facebook (Opens in new window) Facebook
  • More
  • Email a link to a friend (Opens in new window) Email
  • Share on WhatsApp (Opens in new window) WhatsApp

Related

Tags: App MonitoringData Protection Impact AssessmentItalian Data Protection AuthorityItalian Data Protection Authority finePostepay appsThe Cyber ExpressThe Cyber Express News
Previous Post

Indian Agency Arrests Key SIM Card Supplier of a Broader Cyber Fraud Network

Next Post

Bluesky, Fast-Growing X Alternative, Hit by Sophisticated DDoS Attack

Next Post
Bluesky cyberattack

Bluesky, Fast-Growing X Alternative, Hit by Sophisticated DDoS Attack

Q1 2026 Threat Reports

❮ ❯
Cyble-Vision


Follow Us On Google News

Categories

  • Privacy Statement
  • Terms of Use
  • Write For Us

© 2026 The Cyber Express - Cybersecurity News and Magazine.

Welcome Back!

Login to your account below

Forgotten Password?

Retrieve your password

Please enter your username or email address to reset your password.

Log In

Add New Playlist

No Result
View All Result
  • Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board

© 2026 The Cyber Express - Cybersecurity News and Magazine.

-
00:00
00:00

Queue

Update Required Flash plugin
-
00:00
00:00



