



















• Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
The Cyber Express
  • MagazineDownload
  • Firewall Daily
    • All
    • Bug Bounty & Rewards
    • Dark Web News
    • Data Breach News
    • Hacker News
    • Ransomware News
    • Vulnerabilities
    WorkOS, AI Agent, Prompt Injection, Grok, Grok AI, Gemini, Fraud, Agentic AI, AI-assisted Cyberattacks

    WorkOS Says a Researcher’s Runaway AI Pentest Agent Copied Customer Sales Records

    Nvidia board investigation

    Why Is Nvidia Investigating Its Own CEO, and Can the Board Remove Him?

    weekly roundup

    The Cyber Express Weekly Roundup: FBI Blames North Korea for $6B Binance Hack, Hackers Turn Up the Heat on Europe’s Fridges and More

    Stockal cyberattack

    Stockal Confirms Unauthorized Trades in 13 Customer Accounts

    Alpine Linux servers

    Alpine Linux SSH Flaw Lets Attackers Log In Without a Password

    Queens Public Library ransomware attack

    Ransomware Just Took New York’s Queens Library Offline, and It’s Not the First

    Amadeus cybersecurity incident

    Airline Data Breach Widens as Singapore Airlines Reports 46,000 Affected Records

    refrigeration cyberattacks

    After Supermarket Freezers, Hackers Turn Up the Heat on France’s Blood Supply

    university supercomputer hacking

    Two Canadians Accused of Turning US University Supercomputers Into Crypto Miners

    Trending Tags

    • blackbyte ransomware
    • Ransomware
    • lapsus$ ransomware
    • Apple
    • Apple vulnerability
  • Essentials
    • All
    • Compliance
    • Governance
    • Policy Updates
    • Regulations
    SEC, Misleading Cyber Disclosures, Financial data, financial data protection, SEC

    SEC Enforcement Fell 24% in Fiscal 2026

    ASD Essentials

    The Essential Eight Is Being Replaced: What Australian Organisations Need to Know

    SICW 2026

    AI Is Now Fighting on Both Sides of the Cyber War, Singapore Warns

    Morocco cybersecurity strategy

    Morocco Flags AI Threats, Prioritizes Critical Infrastructure Defense

    European Police Chiefs Convention 2026

    Europe’s Police Chiefs Face Growing Threat of AI-Driven Crime

    AI service security

    Hackers Are Stealing AI Keys. The Cost Can Reach $600,000

    AI security risks

    Sam Altman at UN Security Council: 6 AI Security Risks the World Cannot Ignore

    AI-enabled cyber attacks

    AI Gives Hackers an Edge Defenders Still Can’t Match, NCSC Warns

    Fraudulent SIM cards

    India’s DoT Warns Citizens Over SIM Fraud and IMEI Tampering

    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
    • All
    • How to
    • What is
    Infostealer Intelligence

    The 2026 Infostealer Intelligence Shortlist: Top 10 Vendors Security Teams Should Know

    Google Chrome

    How to Remove Saved Passwords From Google Chrome (And Why You Should)

    DPDP Rules, Cyble, DPDP Act, Cyble Vantage

    How Cyble’s Front-Row Vantage Can Help You in Complying to India’s DPDP Act

    Cybersecurity Countries

    The Top 8 Countries Leading the Cyber Defense Race in 2025

    link building

    The Link Building Secrets Your Competitors Don’t Want You to Know

    Supply Chain Attack

    Supply Chain Resilience and Physical Security: Lessons for 2025

    Healthcare cybersecurity trends of 2024

    Healthcare Cybersecurity: 2024 Was Tough, 2025 May Be Better

    CEO's Guide to Take-Down Services

    Shield Your Organization: CEO’s Perspective on Take-Down Services

    Azure sign-in Microsoft

    Microsoft Announces Mandatory MFA for Azure Sign-ins to Bolster Cloud Defenses

  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • All
    • Appointments
    • Budgets
    • Mergers & Aquisitions
    • Partnerships
    • Press Release
    • Startups
    Kerala Police Signs MoU With Cyble

    Kerala Police Signs MoU With Cyble to Use Threat Intelligence in Cybercrime Probes

    Gemini 4 Argon

    Gemini 4 Argon Restricted Over Cybersecurity Misuse Risks

    weekly roundup September 18 2026

    The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

    threat intelligence

    Cyble, UAE Cyber Security Council Unite Against Rising Cyber Threats

    Ukraine cybersecurity

    Zelensky Appoints Ihor Klymenko to Lead Ukraine’s Cybersecurity Center

    UK cyberattack rate

    UK Small Firms Bear Brunt of Rising Cyberattacks, Hiscox Finds

    Cyber Yodha Campaign

    Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

    UK Ukraine AI partnership

    Britain Gains Access to Ukraine’s ‘Goldmine’ of Battlefield AI Data

    Hims & Hers lawsuit

    FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices

    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
No Result
View All Result
  • MagazineDownload
  • Firewall Daily
    • All
    • Bug Bounty & Rewards
    • Dark Web News
    • Data Breach News
    • Hacker News
    • Ransomware News
    • Vulnerabilities
    WorkOS, AI Agent, Prompt Injection, Grok, Grok AI, Gemini, Fraud, Agentic AI, AI-assisted Cyberattacks

    WorkOS Says a Researcher’s Runaway AI Pentest Agent Copied Customer Sales Records

    Nvidia board investigation

    Why Is Nvidia Investigating Its Own CEO, and Can the Board Remove Him?

    weekly roundup

    The Cyber Express Weekly Roundup: FBI Blames North Korea for $6B Binance Hack, Hackers Turn Up the Heat on Europe’s Fridges and More

    Stockal cyberattack

    Stockal Confirms Unauthorized Trades in 13 Customer Accounts

    Alpine Linux servers

    Alpine Linux SSH Flaw Lets Attackers Log In Without a Password

    Queens Public Library ransomware attack

    Ransomware Just Took New York’s Queens Library Offline, and It’s Not the First

    Amadeus cybersecurity incident

    Airline Data Breach Widens as Singapore Airlines Reports 46,000 Affected Records

    refrigeration cyberattacks

    After Supermarket Freezers, Hackers Turn Up the Heat on France’s Blood Supply

    university supercomputer hacking

    Two Canadians Accused of Turning US University Supercomputers Into Crypto Miners

    Trending Tags

    • blackbyte ransomware
    • Ransomware
    • lapsus$ ransomware
    • Apple
    • Apple vulnerability
  • Essentials
    • All
    • Compliance
    • Governance
    • Policy Updates
    • Regulations
    SEC, Misleading Cyber Disclosures, Financial data, financial data protection, SEC

    SEC Enforcement Fell 24% in Fiscal 2026

    ASD Essentials

    The Essential Eight Is Being Replaced: What Australian Organisations Need to Know

    SICW 2026

    AI Is Now Fighting on Both Sides of the Cyber War, Singapore Warns

    Morocco cybersecurity strategy

    Morocco Flags AI Threats, Prioritizes Critical Infrastructure Defense

    European Police Chiefs Convention 2026

    Europe’s Police Chiefs Face Growing Threat of AI-Driven Crime

    AI service security

    Hackers Are Stealing AI Keys. The Cost Can Reach $600,000

    AI security risks

    Sam Altman at UN Security Council: 6 AI Security Risks the World Cannot Ignore

    AI-enabled cyber attacks

    AI Gives Hackers an Edge Defenders Still Can’t Match, NCSC Warns

    Fraudulent SIM cards

    India’s DoT Warns Citizens Over SIM Fraud and IMEI Tampering

    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
    • All
    • How to
    • What is
    Infostealer Intelligence

    The 2026 Infostealer Intelligence Shortlist: Top 10 Vendors Security Teams Should Know

    Google Chrome

    How to Remove Saved Passwords From Google Chrome (And Why You Should)

    DPDP Rules, Cyble, DPDP Act, Cyble Vantage

    How Cyble’s Front-Row Vantage Can Help You in Complying to India’s DPDP Act

    Cybersecurity Countries

    The Top 8 Countries Leading the Cyber Defense Race in 2025

    link building

    The Link Building Secrets Your Competitors Don’t Want You to Know

    Supply Chain Attack

    Supply Chain Resilience and Physical Security: Lessons for 2025

    Healthcare cybersecurity trends of 2024

    Healthcare Cybersecurity: 2024 Was Tough, 2025 May Be Better

    CEO's Guide to Take-Down Services

    Shield Your Organization: CEO’s Perspective on Take-Down Services

    Azure sign-in Microsoft

    Microsoft Announces Mandatory MFA for Azure Sign-ins to Bolster Cloud Defenses

  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • All
    • Appointments
    • Budgets
    • Mergers & Aquisitions
    • Partnerships
    • Press Release
    • Startups
    Kerala Police Signs MoU With Cyble

    Kerala Police Signs MoU With Cyble to Use Threat Intelligence in Cybercrime Probes

    Gemini 4 Argon

    Gemini 4 Argon Restricted Over Cybersecurity Misuse Risks

    weekly roundup September 18 2026

    The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

    threat intelligence

    Cyble, UAE Cyber Security Council Unite Against Rising Cyber Threats

    Ukraine cybersecurity

    Zelensky Appoints Ihor Klymenko to Lead Ukraine’s Cybersecurity Center

    UK cyberattack rate

    UK Small Firms Bear Brunt of Rising Cyberattacks, Hiscox Finds

    Cyber Yodha Campaign

    Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

    UK Ukraine AI partnership

    Britain Gains Access to Ukraine’s ‘Goldmine’ of Battlefield AI Data

    Hims & Hers lawsuit

    FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices

    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
No Result
View All Result
The Cyber Express
No Result
View All Result

Cyble Research Discovers ShadowHS, an In-Memory Linux Framework for Long-Term Access

Ashish Khaitan by Ashish Khaitan
January 30, 2026
in Firewall Daily, Cyber News, Dark Web News, Vulnerabilities
0
ShadowHS
585
SHARES
3.2k
VIEWS
Share on LinkedInShare on Twitter

Cyble Research & Intelligence Labs (CRIL) has uncovered a post-exploitation Linux framework called ShadowHS, designed for stealthy, in-memory operations. Unlike traditional malware, ShadowHS leverages a fileless architecture and a weaponized version of hackshell, enabling attackers to maintain long-term, operator-controlled access to compromised Linux systems. 

Fileless Execution and Weaponized Hackshell 

The ShadowHS Linux framework operates entirely in memory, leaving no persistent binaries on disk. CRIL’s analysis revealed that the framework uses an encrypted shell loader to deploy a heavily modified version of hackshell, enabling an interactive post-exploitation environment.

The loader decrypts and reconstructs the payload in memory using AES‑256‑CBC encryption, Perl byte skipping, and gzip decompression. The payload is executed via /proc/<pid>/fd/<fd> with a spoofed argv[0], ensuring that no filesystem artifacts remain.
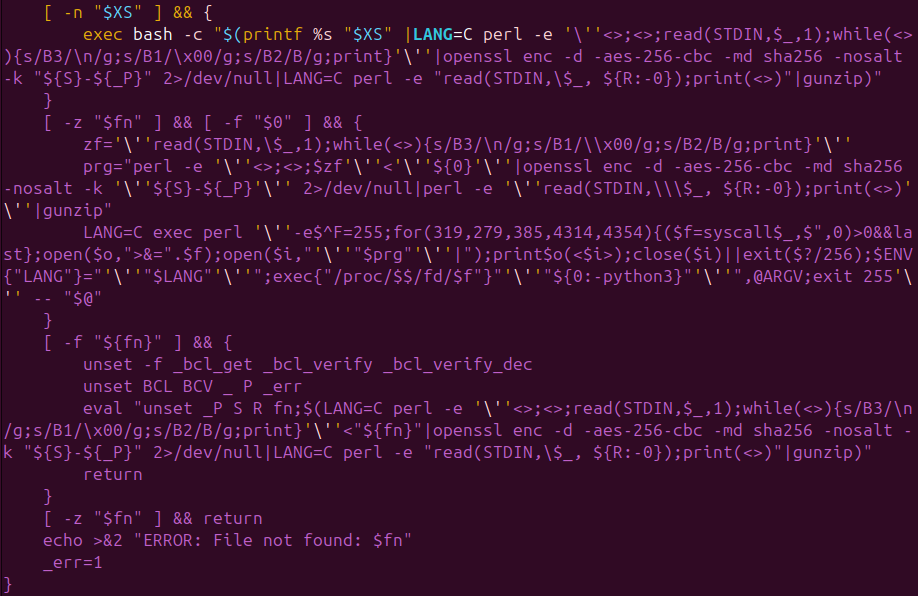
Payload Reconstruction & Fileless Execution
Payload Reconstruction & Fileless Execution (Source: CRIL)

Once active, ShadowHS prioritizes reconnaissance, fingerprinting host security measures, evaluating prior compromises, and providing an operator-controlled interface. Its runtime behavior is deliberately restrained, allowing attackers to selectively invoke capabilities such as credential access, lateral movement, privilege escalation, cryptomining, and covert data exfiltration. 

CRIL Observations on Operator-Centric Design 

According to CRIL, ShadowHS reflects mature operator tradecraft rather than the patterns of opportunistic Linux malware. Its in-memory design allows operators to assess system security posture while avoiding traditional detection mechanisms.

The payload performs aggressive EDR and AV fingerprinting, checking for commercial endpoint tools such as CrowdStrike, Tanium, Sophos, and Microsoft Defender, as well as cloud and OT/ICS telemetry agents. 

Runtime Dependency Validation
Runtime Dependency Validation (Source: CRIL)

“ShadowHS demonstrates a clear separation between restrained runtime activity and extensive dormant capabilities,” CRIL notes. “This is indicative of a deliberate operator-driven post-exploitation platform rather than automated malware.” 

Covert Data Exfiltration 

One of ShadowHS’s most notable features is its ability to exfiltrate data without using standard network channels. The Linux framework implements user-space tunneling over GSocket, replacing rsync’s default transport.

This allows files to be transferred stealthily across firewalls and restrictive network environments. CRIL observed two variants: one using DBus-based tunneling and another employing netcat-style GSocket tunnels, both preserving timestamps, permissions, and partial transfer state. 

Dormant Capabilities and Lateral Movement 

ShadowHS also contains dormant modules that operators can activate on demand. These include: 

  • Memory dumping for credential theft 
  • SSH-based lateral movement and brute-force scanning 
  • Privilege escalation using kernel exploits 
  • Cryptocurrency mining via XMRig, GMiner, and lolMiner 

The framework incorporates anti-competition logic to detect and terminate rival malware, including miners like Rondo and Kinsing, as well as credential-stealing backdoors such as Ebury. It also evaluates kernel integrity and loaded modules, helping the operator determine if the host is already compromised or actively monitored. 

Implications for Threat Defense 

The discovery of ShadowHS stresses the challenges organizations face in defending Linux environments against fileless, in-memory threats. CRIL notes that traditional signature-based antivirus solutions and file-based detection mechanisms are insufficient to detect frameworks like ShadowHS. Effective defense requires monitoring process behavior, kernel-level telemetry, and memory-resident activity. 

“ShadowHS represents a fully operator-controlled, adaptive Linux framework designed for stealth and long-term access,” CRIL stated. “Its use of a weaponized hackshell, fileless execution, and exfiltration methods highlights the growing need for proactive threat intelligence and advanced monitoring strategies.” 

See ShadowHS and new cyber threats in action, schedule your Cyble demo today, and gain real-time visibility into cyber risks before they impact your organization. 
Share this:

  • Share on LinkedIn (Opens in new window) LinkedIn
  • Share on Reddit (Opens in new window) Reddit
  • Share on X (Opens in new window) X
  • Share on Facebook (Opens in new window) Facebook
  • More
  • Email a link to a friend (Opens in new window) Email
  • Share on WhatsApp (Opens in new window) WhatsApp

Related

Tags: CRILhackshellLinux frameworkShadowHSThe Cyber ExpressThe Cyber Express News
Previous Post

Cybersecurity Experts Arrested During Courthouse Pen Test Reach $600K Settlement

Next Post

CNIL Fine on France Travail After Hack Exposes 20 Years of Job Seekers’ Personal Data

Next Post
CNIL fine on France Travail

CNIL Fine on France Travail After Hack Exposes 20 Years of Job Seekers’ Personal Data

Q1 2026 Threat Reports

❮ ❯
Cyble-Vision


Follow Us On Google News

Categories

  • Privacy Statement
  • Terms of Use
  • Write For Us

© 2026 The Cyber Express - Cybersecurity News and Magazine.

Welcome Back!

Login to your account below

Forgotten Password?

Retrieve your password

Please enter your username or email address to reset your password.

Log In

Add New Playlist

No Result
View All Result
  • Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board

© 2026 The Cyber Express - Cybersecurity News and Magazine.

-
00:00
00:00

Queue

Update Required Flash plugin
-
00:00
00:00




