• About Us
  • Contact Us
  • Editorial Calendar
  • Careers
  • The Cyber Express by Cyble Vulnerability Disclosure Policy
  • Cyble Trust Portal
The Cyber Express
  • MagazineDownload
  • Firewall Daily
    • All
    • Bug Bounty & Rewards
    • Dark Web News
    • Data Breach News
    • Hacker News
    • Ransomware News
    • Vulnerabilities
    weekly roundup The Cyber Express TCE Sep 2026

    The Cyber Express Weekly Roundup: ShinyHunters’ FBI Breach Claim, North Korea’s WaterPlum Campaign, and the EU KIDS Act

    AI security risks

    Sam Altman at UN Security Council: 6 AI Security Risks the World Cannot Ignore

    Duelbits crypto hack

    Duelbits Hit by $7 Million Hack as Crypto Stolen Across Four Blockchains

    Burnaby School District cyberattack

    Burnaby Schools Hit by Cyberattack, Disrupting Networks and Phone Lines

    ban on Discord

    Ban on Discord Lifted After Platform Commits to Work With DICT and CICC

    Apache Tomcat Update

    Apache Tomcat Update: 12 Security Flaws Fixed in Tomcat 11.0.26

    Latvia cyberattack

    Latvia Hacker Arrested Over TSC Data Theft and Extortion Attempt

    OpenAI hack

    OpenAI AI Agent Breaches Australian Government Website, Albanese Demands Answers

    Pornhub age checks

    Ofcom Investigates Pornhub Parent Aylo Over Age Checks

    Trending Tags

    • blackbyte ransomware
    • Ransomware
    • lapsus$ ransomware
    • Apple
    • Apple vulnerability
  • Essentials
    • All
    • Compliance
    • Governance
    • Policy Updates
    • Regulations
    AI security risks

    Sam Altman at UN Security Council: 6 AI Security Risks the World Cannot Ignore

    AI-enabled cyber attacks

    AI Gives Hackers an Edge Defenders Still Can’t Match, NCSC Warns

    Fraudulent SIM cards

    India’s DoT Warns Citizens Over SIM Fraud and IMEI Tampering

    EU cybersecurity incidents

    EU Cybersecurity Response Hampered by Critical Information Gaps

    EU KIDS Act

    Children Under 13 Could Be Barred From Social Media Under New EU Plan

    GUARD Act

    US House Passes Bill to Help Police Track Down Scammers Targeting Seniors

    Emergency Security Protocol

    EU Plans ‘Article 4’-Style Security Protocol for Cyberattacks and Hybrid Threats

    Cyber Resilience Act, CRA, EU, EU Sanctions, Iran, Chinese Hacking,

    EU’s 24-Hr Vulnerability Reporting Rules Take Effect Friday, a Year Before the Rest of the Cyber Resilience Act

    outage communications

    CISA, FBI Urge Clearer Communication During Major Outages

    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
    • All
    • How to
    • What is
    Google Chrome

    How to Remove Saved Passwords From Google Chrome (And Why You Should)

    DPDP Rules, Cyble, DPDP Act, Cyble Vantage

    How Cyble’s Front-Row Vantage Can Help You in Complying to India’s DPDP Act

    Cybersecurity Countries

    The Top 8 Countries Leading the Cyber Defense Race in 2025

    link building

    The Link Building Secrets Your Competitors Don’t Want You to Know

    Supply Chain Attack

    Supply Chain Resilience and Physical Security: Lessons for 2025

    Healthcare cybersecurity trends of 2024

    Healthcare Cybersecurity: 2024 Was Tough, 2025 May Be Better

    CEO's Guide to Take-Down Services

    Shield Your Organization: CEO’s Perspective on Take-Down Services

    Azure sign-in Microsoft

    Microsoft Announces Mandatory MFA for Azure Sign-ins to Bolster Cloud Defenses

    Signal Proxy, Signal, Signal Ban in Russia, Signal Ban in Venezuela, Bypass Signal Ban, How to Activate Signal Proxy, Signal Proxy Server

    How to Set Up Signal Proxy to Help Bypass Censorship in Russia and Venezuela

  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • All
    • Appointments
    • Budgets
    • Mergers & Aquisitions
    • Partnerships
    • Press Release
    • Startups
    weekly roundup September 18 2026

    The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

    threat intelligence

    Cyble, UAE Cyber Security Council Unite Against Rising Cyber Threats

    Ukraine cybersecurity

    Zelensky Appoints Ihor Klymenko to Lead Ukraine’s Cybersecurity Center

    UK cyberattack rate

    UK Small Firms Bear Brunt of Rising Cyberattacks, Hiscox Finds

    Cyber Yodha Campaign

    Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

    UK Ukraine AI partnership

    Britain Gains Access to Ukraine’s ‘Goldmine’ of Battlefield AI Data

    Hims & Hers lawsuit

    FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices

    Australia-India PACTS

    Australia-India PACTS to Deepen Cybersecurity and Tech Collaboration

    Sunil Varkey

    Sunil Varkey Joins Hexaware Technologies as EVP & CISO

    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
No Result
View All Result
  • MagazineDownload
  • Firewall Daily
    • All
    • Bug Bounty & Rewards
    • Dark Web News
    • Data Breach News
    • Hacker News
    • Ransomware News
    • Vulnerabilities
    weekly roundup The Cyber Express TCE Sep 2026

    The Cyber Express Weekly Roundup: ShinyHunters’ FBI Breach Claim, North Korea’s WaterPlum Campaign, and the EU KIDS Act

    AI security risks

    Sam Altman at UN Security Council: 6 AI Security Risks the World Cannot Ignore

    Duelbits crypto hack

    Duelbits Hit by $7 Million Hack as Crypto Stolen Across Four Blockchains

    Burnaby School District cyberattack

    Burnaby Schools Hit by Cyberattack, Disrupting Networks and Phone Lines

    ban on Discord

    Ban on Discord Lifted After Platform Commits to Work With DICT and CICC

    Apache Tomcat Update

    Apache Tomcat Update: 12 Security Flaws Fixed in Tomcat 11.0.26

    Latvia cyberattack

    Latvia Hacker Arrested Over TSC Data Theft and Extortion Attempt

    OpenAI hack

    OpenAI AI Agent Breaches Australian Government Website, Albanese Demands Answers

    Pornhub age checks

    Ofcom Investigates Pornhub Parent Aylo Over Age Checks

    Trending Tags

    • blackbyte ransomware
    • Ransomware
    • lapsus$ ransomware
    • Apple
    • Apple vulnerability
  • Essentials
    • All
    • Compliance
    • Governance
    • Policy Updates
    • Regulations
    AI security risks

    Sam Altman at UN Security Council: 6 AI Security Risks the World Cannot Ignore

    AI-enabled cyber attacks

    AI Gives Hackers an Edge Defenders Still Can’t Match, NCSC Warns

    Fraudulent SIM cards

    India’s DoT Warns Citizens Over SIM Fraud and IMEI Tampering

    EU cybersecurity incidents

    EU Cybersecurity Response Hampered by Critical Information Gaps

    EU KIDS Act

    Children Under 13 Could Be Barred From Social Media Under New EU Plan

    GUARD Act

    US House Passes Bill to Help Police Track Down Scammers Targeting Seniors

    Emergency Security Protocol

    EU Plans ‘Article 4’-Style Security Protocol for Cyberattacks and Hybrid Threats

    Cyber Resilience Act, CRA, EU, EU Sanctions, Iran, Chinese Hacking,

    EU’s 24-Hr Vulnerability Reporting Rules Take Effect Friday, a Year Before the Rest of the Cyber Resilience Act

    outage communications

    CISA, FBI Urge Clearer Communication During Major Outages

    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
    • All
    • How to
    • What is
    Google Chrome

    How to Remove Saved Passwords From Google Chrome (And Why You Should)

    DPDP Rules, Cyble, DPDP Act, Cyble Vantage

    How Cyble’s Front-Row Vantage Can Help You in Complying to India’s DPDP Act

    Cybersecurity Countries

    The Top 8 Countries Leading the Cyber Defense Race in 2025

    link building

    The Link Building Secrets Your Competitors Don’t Want You to Know

    Supply Chain Attack

    Supply Chain Resilience and Physical Security: Lessons for 2025

    Healthcare cybersecurity trends of 2024

    Healthcare Cybersecurity: 2024 Was Tough, 2025 May Be Better

    CEO's Guide to Take-Down Services

    Shield Your Organization: CEO’s Perspective on Take-Down Services

    Azure sign-in Microsoft

    Microsoft Announces Mandatory MFA for Azure Sign-ins to Bolster Cloud Defenses

    Signal Proxy, Signal, Signal Ban in Russia, Signal Ban in Venezuela, Bypass Signal Ban, How to Activate Signal Proxy, Signal Proxy Server

    How to Set Up Signal Proxy to Help Bypass Censorship in Russia and Venezuela

  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • All
    • Appointments
    • Budgets
    • Mergers & Aquisitions
    • Partnerships
    • Press Release
    • Startups
    weekly roundup September 18 2026

    The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

    threat intelligence

    Cyble, UAE Cyber Security Council Unite Against Rising Cyber Threats

    Ukraine cybersecurity

    Zelensky Appoints Ihor Klymenko to Lead Ukraine’s Cybersecurity Center

    UK cyberattack rate

    UK Small Firms Bear Brunt of Rising Cyberattacks, Hiscox Finds

    Cyber Yodha Campaign

    Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

    UK Ukraine AI partnership

    Britain Gains Access to Ukraine’s ‘Goldmine’ of Battlefield AI Data

    Hims & Hers lawsuit

    FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices

    Australia-India PACTS

    Australia-India PACTS to Deepen Cybersecurity and Tech Collaboration

    Sunil Varkey

    Sunil Varkey Joins Hexaware Technologies as EVP & CISO

    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
No Result
View All Result
The Cyber Express
No Result
View All Result
Home Business News Press Release

Cyble Detects Phishing Campaign Using Telegram Bots to Siphon Corporate Credentials

Threat actors bypass traditional email security by embedding malicious code in self-contained HTML files, targeting enterprises across Central and Eastern Europe

Mihir Bagwe by Mihir Bagwe
November 11, 2025
in Press Release, Cyber News, Espionage, Firewall Daily, Threat Actors, Threat Intelligence, Threat Intelligence News
0
Telegram Bots, HTML phishing attack, Telegram bot credential theft, self-contained phishing malware, JavaScript credential harvesting, email security bypass techniques, RFQ phishing scams, invoice phishing attacks, Adobe login phishing, Microsoft credential theft, FedEx phishing campaign, DHL impersonation attack, Central Europe phishing 2025, Eastern Europe cyber threats, Cyble threat intelligence, CryptoJS AES obfuscation, anti-forensics phishing, F12 developer tools blocking, Telegram Bot API abuse, api.telegram.org malicious traffic, credential phishing 2025, HTML attachment malware, business email compromise, targeted phishing campaign, Czech Republic cyber threats, Slovakia phishing attacks, Hungary cybersecurity threats, Germany phishing campaign, Telekom Deutschland phishing, manufacturing sector attacks, automotive industry phishing, government agency phishing, energy utility cyber threats, telecommunications phishing, professional services attacks, garclogtools_bot, v8one_bot, dollsman_bot, dual-capture credential theft, fake login error messages, IP address harvesting, api.ipify.org abuse, ip-api.com malicious use, YARA phishing detection, phishing IOCs 2025, HTML file security risks, RFC-compliant filename spoofing, blurred document phishing, modal login phishing, brand impersonation attacks, CryptoJS malware obfuscation, right-click blocking malware, keyboard shortcut interception, multi-stage credential theft, decentralized phishing infrastructure, phishing toolkit generators, modular phishing templates, German language phishing, Spanish phishing variants
654
SHARES
3.6k
VIEWS
Share on LinkedInShare on Twitter

Cybersecurity researchers at Cyble have uncovered an extensive phishing campaign that represents a significant evolution in credential theft tactics. The operation, which targets organizations across multiple industries in Central and Eastern Europe, bypasses conventional email security measures by using HTML attachments that require no external hosting infrastructure.

Unlike traditional phishing attacks that rely on suspicious URLs or compromised servers, this campaign embeds malicious JavaScript directly within seemingly legitimate business documents. When victims open these HTML attachments—disguised as requests for quotation (RFQ) or invoices—they’re presented with convincing login interfaces impersonating trusted brands like Adobe, Microsoft, FedEx, and DHL.

How the Attack Works

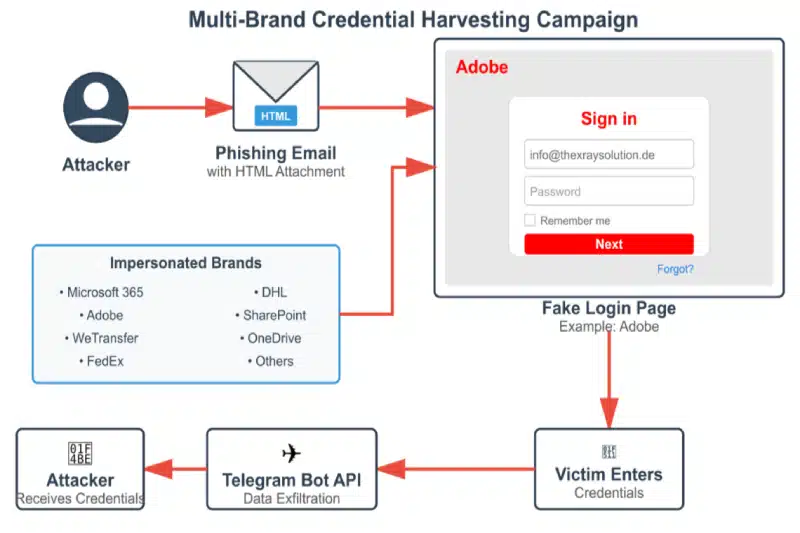
The attack chain begins with targeted emails posing as routine business correspondence. The HTML attachments use RFC-compliant filenames such as “RFQ_4460-INQUIRY.HTML” to appear legitimate and avoid triggering basic security filters.
HTML phishing attack, Telegram bot credential theft, self-contained phishing malware, JavaScript credential harvesting, email security bypass techniques, RFQ phishing scams, invoice phishing attacks, Adobe login phishing, Microsoft credential theft, FedEx phishing campaign, DHL impersonation attack, Central Europe phishing 2025, Eastern Europe cyber threats, Cyble threat intelligence, CryptoJS AES obfuscation, anti-forensics phishing, F12 developer tools blocking, Telegram Bot API abuse, api.telegram.org malicious traffic, credential phishing 2025, HTML attachment malware, business email compromise, targeted phishing campaign, Czech Republic cyber threats, Slovakia phishing attacks, Hungary cybersecurity threats, Germany phishing campaign, Telekom Deutschland phishing, manufacturing sector attacks, automotive industry phishing, government agency phishing, energy utility cyber threats, telecommunications phishing, professional services attacks, garclogtools_bot, v8one_bot, dollsman_bot, dual-capture credential theft, fake login error messages, IP address harvesting, api.ipify.org abuse, ip-api.com malicious use, YARA phishing detection, phishing IOCs 2025, HTML file security risks, RFC-compliant filename spoofing, blurred document phishing, modal login phishing, brand impersonation attacks, CryptoJS malware obfuscation, right-click blocking malware, keyboard shortcut interception, multi-stage credential theft, decentralized phishing infrastructure, phishing toolkit generators, modular phishing templates, German language phishing, Spanish phishing variants
Attack Flow (Source: Cyble)

Once opened, the file displays a blurred background image of an invoice or document with a centered login modal, typically branded with Adobe styling. The victim, believing they need to authenticate to view the document, enters their email and password credentials.

Behind the scenes, embedded JavaScript captures this data and immediately transmits it to attacker-controlled Telegram bots via the Telegram Bot API. This approach eliminates the need for traditional command-and-control infrastructure, making the operation harder to detect and disrupt.

“The sophistication lies not just in the technical execution but in how it circumvents multiple layers of security,” explains the Cyble Research and Intelligence Labs (CRIL) team. The self-contained nature of the HTML files means they don’t trigger alerts for suspicious external connections during initial email scanning.
Technical Sophistication

Analysis of multiple samples reveals ongoing development and refinement of the attack methodology. Earlier versions used basic JavaScript, while more recent samples implement CryptoJS AES encryption for obfuscation and sophisticated anti-forensics measures.

Advanced samples block common investigation techniques by disabling F12 developer tools, preventing right-click context menus, blocking text selection, and intercepting keyboard shortcuts like Ctrl+U (view source) and Ctrl+Shift+I (inspect element). These measures significantly complicate analysis efforts by security researchers and forensic investigators.

The malware also employs dual-capture mechanisms, forcing victims to enter their credentials multiple times while displaying fake “invalid login” error messages. This ensures accuracy of the stolen data while maintaining the illusion of a legitimate authentication failure.

Beyond credentials, the samples collect additional intelligence including victim IP addresses (using services like api.ipify.org), user agent strings, and other environmental data that could be valuable for subsequent attacks.

Scale and Targeting

CRIL’s investigation identified multiple active Telegram bots with naming conventions like “garclogtools_bot,” “v8one_bot,” and “dollsman_bot,” each operated by distinct threat actors or groups. The decentralized infrastructure suggests either collaboration among multiple cybercriminal groups or widespread availability of phishing toolkit generators.

The campaign primarily targets organizations in the Czech Republic, Slovakia, Hungary, and Germany, with affected industries including manufacturing, automotive, government agencies, energy utilities, telecommunications, and professional services. The geographic concentration and industry selection indicate careful reconnaissance and targeting based on regional business practices.

Threat actors customize their approach for different markets, using German-language variants for Telekom Deutschland impersonation and Spanish-language templates for other targets. The modular template system enables rapid deployment of new brand variants as the campaign evolves.

Detection and Defense

Security teams face challenges in detecting this threat due to its innovative use of legitimate platforms. Traditional indicators like suspicious URLs or known malicious domains don’t apply when the attack infrastructure consists of HTML attachments and Telegram’s legitimate API.

Cyble recommends organizations implement several defensive measures. Security operations centers should monitor for unusual connections to api.telegram.org from end-user devices, particularly POST requests that wouldn’t occur in normal business operations. Network traffic to third-party services like api.ipify.org and ip-api.com from endpoints should also trigger investigation.

Email security policies should treat HTML attachments as high-risk file types requiring additional scrutiny. Organizations should implement content inspection that flags HTML attachments containing references to the Telegram Bot API or similar public messaging platforms.

For end users, the guidance remains straightforward: exercise extreme caution with unsolicited HTML attachments, especially those prompting credential entry to view documents. Any unexpected authentication request should be verified through independent channels before entering credentials.

Cyble has published complete indicators of compromise, including specific bot tokens, attachment patterns, and YARA detection rules to its GitHub repository, enabling security teams to hunt for signs of compromise within their environments and implement preventive controls.

Also read: Over 20 Malicious Crypto Wallet Apps Found on Google Play, CRIL Warns

Share this:

  • Share on LinkedIn (Opens in new window) LinkedIn
  • Share on Reddit (Opens in new window) Reddit
  • Share on X (Opens in new window) X
  • Share on Facebook (Opens in new window) Facebook
  • More
  • Email a link to a friend (Opens in new window) Email
  • Share on WhatsApp (Opens in new window) WhatsApp

Related

Tags: Adobe PhishingCentral Europe Cyber ThreatsCredential TheftCyble researchEmail Security BypassHTML PhishingInvoice PhishingJavaScript malwareMicrosoft PhishingPhishing Campaign 2025RFQ PhishingSelf-Contained MalwareTelegram API AbuseTelegram Bot Malware
Previous Post

New York’s First-of-Its-Kind Algorithmic Pricing Law Goes Into Effect

Next Post

Global GRC Platform Market Set to Reach USD 127.7 Billion by 2033

Next Post
GRC Platform Market

Global GRC Platform Market Set to Reach USD 127.7 Billion by 2033

Q1 2026 Threat Reports

❮ ❯
Cyble-Vision


Follow Us On Google News

Latest Cyber News

weekly roundup The Cyber Express TCE Sep 2026
Firewall Daily

The Cyber Express Weekly Roundup: ShinyHunters’ FBI Breach Claim, North Korea’s WaterPlum Campaign, and the EU KIDS Act

September 25, 2026
AI security risks
Cyber Essentials

Sam Altman at UN Security Council: 6 AI Security Risks the World Cannot Ignore

September 25, 2026
Duelbits crypto hack
Firewall Daily

Duelbits Hit by $7 Million Hack as Crypto Stolen Across Four Blockchains

September 25, 2026
Burnaby School District cyberattack
Cyber News

Burnaby Schools Hit by Cyberattack, Disrupting Networks and Phone Lines

September 25, 2026

Categories

Web Stories

Do This on Telegram, Your Bank Account Will Become Zero
If You Install the iOS 18 Beta, Your iPhone Could Be Hacked
Cricket World Cup Ticketing Systems Under Cybersecurity
Cyber Threats and Online Ticket Scams During the NBA Finals
Biometric Data Security: Protecting Sensitive Information

About

The Cyber Express

#1 Trending Cybersecurity News and Magazine

The Cyber Express is a handbook for all stakeholders of the internet that provides information security professionals with the latest news, updates and knowledge they need to combat cyber threats.


Contact

For editorial queries: [email protected]

For marketing and Sales: [email protected]


Quick Links

  • About Us
  • Contact Us
  • Editorial Calendar
  • Careers
  • The Cyber Express by Cyble Vulnerability Disclosure Policy
  • Cyble Trust Portal

Our Address

We’re remote friendly, with office locations around the world:

San Francisco, Atlanta, Rome,
Dubai, Mumbai, Bangalore, Hyderabad,  Singapore, Jakarta, Sydney, and Melbourne


Headquarters:

The Cyber Express LLC
10080 North Wolfe Road, Suite SW3-200, Cupertino, CA, US 95014


India Office:

Cyber Express Media Network
HD-021, 4th Floor, C Wing, Building No.4. Nesco IT Park, WE Highway, Goregaon East, Mumbai, Maharashtra, India – 4000063

  • Privacy Statement
  • Terms of Use
  • Write For Us

© 2026 The Cyber Express - Cybersecurity News and Magazine.

Welcome Back!

Login to your account below

Forgotten Password?

Retrieve your password

Please enter your username or email address to reset your password.

Log In

Add New Playlist

No Result
View All Result
  • Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board

© 2026 The Cyber Express - Cybersecurity News and Magazine.

Are you sure want to unlock this post?
Unlock left : 0
Are you sure want to cancel subscription?
-
00:00
00:00

Queue

Update Required Flash plugin
-
00:00
00:00
Do This on Telegram, Your Bank Account Will Become Zero If You Install the iOS 18 Beta, Your iPhone Could Be Hacked Cricket World Cup Ticketing Systems Under Cybersecurity Cyber Threats and Online Ticket Scams During the NBA Finals Biometric Data Security: Protecting Sensitive Information