




















• Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
The Cyber Express
  • MagazineDownload
  • Firewall Daily
    • All
    • Bug Bounty & Rewards
    • Dark Web News
    • Data Breach News
    • Hacker News
    • Ransomware News
    • Vulnerabilities
    Jensen Huang resigns

    Jensen Huang Exits Nvidia Days After the Board Said It Backed Him

    FaceStealer

    US Disrupts North Korea’s FaceStealer Campaign, Targets $1.2 Billion in Stolen Crypto

    SignDrop zero-day exploit

    New SignDrop Exploit Claims SYSTEM Access on Windows Through CLFS

    Microsoft 365 Outage

    Why Did Outlook Go Down? Microsoft Traced It to Its Own Servers

    WorkOS, AI Agent, Prompt Injection, Grok, Grok AI, Gemini, Fraud, Agentic AI, AI-assisted Cyberattacks

    WorkOS Says a Researcher’s Runaway AI Pentest Agent Copied Customer Sales Records

    Nvidia board investigation

    Why Is Nvidia Investigating Its Own CEO, and Can the Board Remove Him?

    weekly roundup

    The Cyber Express Weekly Roundup: FBI Blames North Korea for $6B Binance Hack, Hackers Turn Up the Heat on Europe’s Fridges and More

    Stockal cyberattack

    Stockal Confirms Unauthorized Trades in 13 Customer Accounts

    Alpine Linux servers

    Alpine Linux SSH Flaw Lets Attackers Log In Without a Password

    Trending Tags

    • blackbyte ransomware
    • Ransomware
    • lapsus$ ransomware
    • Apple
    • Apple vulnerability
  • Essentials
    • All
    • Compliance
    • Governance
    • Policy Updates
    • Regulations
    SEC, Misleading Cyber Disclosures, Financial data, financial data protection, SEC

    SEC Enforcement Fell 24% in Fiscal 2026

    ASD Essentials

    The Essential Eight Is Being Replaced: What Australian Organisations Need to Know

    SICW 2026

    AI Is Now Fighting on Both Sides of the Cyber War, Singapore Warns

    Morocco cybersecurity strategy

    Morocco Flags AI Threats, Prioritizes Critical Infrastructure Defense

    European Police Chiefs Convention 2026

    Europe’s Police Chiefs Face Growing Threat of AI-Driven Crime

    AI service security

    Hackers Are Stealing AI Keys. The Cost Can Reach $600,000

    AI security risks

    Sam Altman at UN Security Council: 6 AI Security Risks the World Cannot Ignore

    AI-enabled cyber attacks

    AI Gives Hackers an Edge Defenders Still Can’t Match, NCSC Warns

    Fraudulent SIM cards

    India’s DoT Warns Citizens Over SIM Fraud and IMEI Tampering

    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
    • All
    • How to
    • What is
    Infostealer Intelligence

    The 2026 Infostealer Intelligence Shortlist: Top 10 Vendors Security Teams Should Know

    Google Chrome

    How to Remove Saved Passwords From Google Chrome (And Why You Should)

    DPDP Rules, Cyble, DPDP Act, Cyble Vantage

    How Cyble’s Front-Row Vantage Can Help You in Complying to India’s DPDP Act

    Cybersecurity Countries

    The Top 8 Countries Leading the Cyber Defense Race in 2025

    link building

    The Link Building Secrets Your Competitors Don’t Want You to Know

    Supply Chain Attack

    Supply Chain Resilience and Physical Security: Lessons for 2025

    Healthcare cybersecurity trends of 2024

    Healthcare Cybersecurity: 2024 Was Tough, 2025 May Be Better

    CEO's Guide to Take-Down Services

    Shield Your Organization: CEO’s Perspective on Take-Down Services

    Azure sign-in Microsoft

    Microsoft Announces Mandatory MFA for Azure Sign-ins to Bolster Cloud Defenses

  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • All
    • Appointments
    • Budgets
    • Mergers & Aquisitions
    • Partnerships
    • Press Release
    • Startups
    Kerala Police Signs MoU With Cyble

    Kerala Police Signs MoU With Cyble to Use Threat Intelligence in Cybercrime Probes

    Gemini 4 Argon

    Gemini 4 Argon Restricted Over Cybersecurity Misuse Risks

    weekly roundup September 18 2026

    The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

    threat intelligence

    Cyble, UAE Cyber Security Council Unite Against Rising Cyber Threats

    Ukraine cybersecurity

    Zelensky Appoints Ihor Klymenko to Lead Ukraine’s Cybersecurity Center

    UK cyberattack rate

    UK Small Firms Bear Brunt of Rising Cyberattacks, Hiscox Finds

    Cyber Yodha Campaign

    Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

    UK Ukraine AI partnership

    Britain Gains Access to Ukraine’s ‘Goldmine’ of Battlefield AI Data

    Hims & Hers lawsuit

    FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices

    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
No Result
View All Result
  • MagazineDownload
  • Firewall Daily
    • All
    • Bug Bounty & Rewards
    • Dark Web News
    • Data Breach News
    • Hacker News
    • Ransomware News
    • Vulnerabilities
    Jensen Huang resigns

    Jensen Huang Exits Nvidia Days After the Board Said It Backed Him

    FaceStealer

    US Disrupts North Korea’s FaceStealer Campaign, Targets $1.2 Billion in Stolen Crypto

    SignDrop zero-day exploit

    New SignDrop Exploit Claims SYSTEM Access on Windows Through CLFS

    Microsoft 365 Outage

    Why Did Outlook Go Down? Microsoft Traced It to Its Own Servers

    WorkOS, AI Agent, Prompt Injection, Grok, Grok AI, Gemini, Fraud, Agentic AI, AI-assisted Cyberattacks

    WorkOS Says a Researcher’s Runaway AI Pentest Agent Copied Customer Sales Records

    Nvidia board investigation

    Why Is Nvidia Investigating Its Own CEO, and Can the Board Remove Him?

    weekly roundup

    The Cyber Express Weekly Roundup: FBI Blames North Korea for $6B Binance Hack, Hackers Turn Up the Heat on Europe’s Fridges and More

    Stockal cyberattack

    Stockal Confirms Unauthorized Trades in 13 Customer Accounts

    Alpine Linux servers

    Alpine Linux SSH Flaw Lets Attackers Log In Without a Password

    Trending Tags

    • blackbyte ransomware
    • Ransomware
    • lapsus$ ransomware
    • Apple
    • Apple vulnerability
  • Essentials
    • All
    • Compliance
    • Governance
    • Policy Updates
    • Regulations
    SEC, Misleading Cyber Disclosures, Financial data, financial data protection, SEC

    SEC Enforcement Fell 24% in Fiscal 2026

    ASD Essentials

    The Essential Eight Is Being Replaced: What Australian Organisations Need to Know

    SICW 2026

    AI Is Now Fighting on Both Sides of the Cyber War, Singapore Warns

    Morocco cybersecurity strategy

    Morocco Flags AI Threats, Prioritizes Critical Infrastructure Defense

    European Police Chiefs Convention 2026

    Europe’s Police Chiefs Face Growing Threat of AI-Driven Crime

    AI service security

    Hackers Are Stealing AI Keys. The Cost Can Reach $600,000

    AI security risks

    Sam Altman at UN Security Council: 6 AI Security Risks the World Cannot Ignore

    AI-enabled cyber attacks

    AI Gives Hackers an Edge Defenders Still Can’t Match, NCSC Warns

    Fraudulent SIM cards

    India’s DoT Warns Citizens Over SIM Fraud and IMEI Tampering

    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
    • All
    • How to
    • What is
    Infostealer Intelligence

    The 2026 Infostealer Intelligence Shortlist: Top 10 Vendors Security Teams Should Know

    Google Chrome

    How to Remove Saved Passwords From Google Chrome (And Why You Should)

    DPDP Rules, Cyble, DPDP Act, Cyble Vantage

    How Cyble’s Front-Row Vantage Can Help You in Complying to India’s DPDP Act

    Cybersecurity Countries

    The Top 8 Countries Leading the Cyber Defense Race in 2025

    link building

    The Link Building Secrets Your Competitors Don’t Want You to Know

    Supply Chain Attack

    Supply Chain Resilience and Physical Security: Lessons for 2025

    Healthcare cybersecurity trends of 2024

    Healthcare Cybersecurity: 2024 Was Tough, 2025 May Be Better

    CEO's Guide to Take-Down Services

    Shield Your Organization: CEO’s Perspective on Take-Down Services

    Azure sign-in Microsoft

    Microsoft Announces Mandatory MFA for Azure Sign-ins to Bolster Cloud Defenses

  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • All
    • Appointments
    • Budgets
    • Mergers & Aquisitions
    • Partnerships
    • Press Release
    • Startups
    Kerala Police Signs MoU With Cyble

    Kerala Police Signs MoU With Cyble to Use Threat Intelligence in Cybercrime Probes

    Gemini 4 Argon

    Gemini 4 Argon Restricted Over Cybersecurity Misuse Risks

    weekly roundup September 18 2026

    The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

    threat intelligence

    Cyble, UAE Cyber Security Council Unite Against Rising Cyber Threats

    Ukraine cybersecurity

    Zelensky Appoints Ihor Klymenko to Lead Ukraine’s Cybersecurity Center

    UK cyberattack rate

    UK Small Firms Bear Brunt of Rising Cyberattacks, Hiscox Finds

    Cyber Yodha Campaign

    Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

    UK Ukraine AI partnership

    Britain Gains Access to Ukraine’s ‘Goldmine’ of Battlefield AI Data

    Hims & Hers lawsuit

    FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices

    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
No Result
View All Result
The Cyber Express
No Result
View All Result

Norton Healthcare Cyber Attack: ALPHV/BlackCat Posts Ransom Note

Weeks after Norton Healthcare announced that it got a suspicious message about its network on May 9, the ALPHV/BlackCat ransomware group claimed that it attacked the healthcare

Editorial by Editorial
July 7, 2023
in Data Breach News, Firewall Daily
0
Norton healthcare cyber attack 1
585
SHARES
3.2k
VIEWS
Share on LinkedInShare on Twitter

Weeks after the first update on the Norton Healthcare cyber attack came, the ALPHV/BlackCat ransomware group disclosed that it was a ransomware attack.

Norton Healthcare earlier announced a “cyber-incident” after it got a suspicious message on May 9. Threat intelligence researcher Brett Callow posted the following blurred screenshot of the leaked data from the Norton Healthcare cyber attack.

Norton Healthcare cyber attack
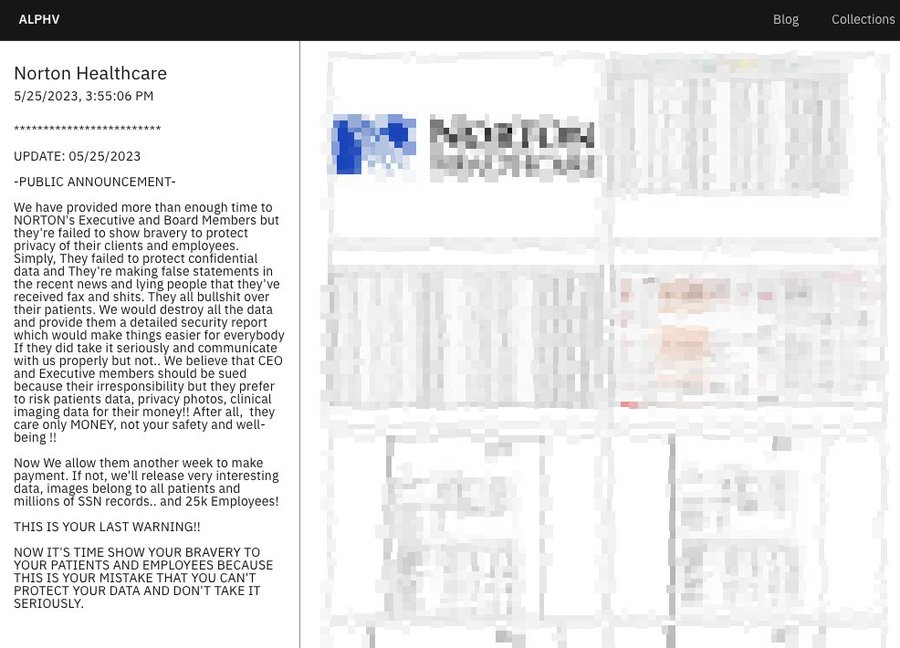
Norton Healthcare Cyber Attack
Screenshot from ALPHV leak site (Photo: Brett Callow/ Twitter)

ALPHV wrote on its leak site that the time given to Norton executives and board members was exhausted wherein they did not try to protect the privacy of their clients and employees. “They’re making false statements in the recent news and lying people that they’ve received fax….”

The ransomware group said that they would destroy all the exfiltrated data and give them a detailed security report, from the Norton Healthcare cyber attack.

The ransomware group made a rant about the officials of Norton Healthcare getting sued for their irresponsibility in risking patient data, that they stole in the Norton ransomware attack.

The group exfiltrated photos, millions of SSN records, 25,0000 employee data, clinical imaging data, etc. The ALPHV post extended the ransom payment deadline another week following which if their demands were not met, they will leak the data.

This was the group’s last warning for Norton Healthcare.

History of the Norton Healthcare cyber attack

The Norton Healthcare cyber attack came to light on May 10, when the company announced on Facebook about an IT disruption that affected its services.

Norton healthcare cyber attack

Disrupted services from the Norton Healthcare cyber attack were Norton eCare and Norton My Chart, the healthcare service’s electronic medical records software.

Two days later, Norton Healthcare disclosed on Facebook that it was indeed a cyber attack.

Norton healthcare cyber attack

“Although- our review is ongoing, an initial analysis confirms Norton Health care was the victim of a cyber-event.” They confirmed that medical practices and other facilities were open while caregivers maintained the required protocols in the absence of accessible systems.

Further updates on the Norton Healthcare cyber attack came with a May 16 notification on Facebook, which disclosed that the cyber attack happened on May 9, following which their IT systems had to be taken offline.

“Why is no one talking about all of the non-elective, time-sensitive surgeries that are being canceled or not scheduled? No images being read, no imaging available for before, after or during surgeries,” a Facebook user responded.

Other details about the Norton Healthcare cyberattack

Several patients spoke up about delayed healthcare services for reports and results due to the Norton Healthcare cyber attack.

The last alert made by the healthcare today assured that they were closer to resuming all operations and bringing the systems back online.

According to the healthcare’s news release updated on May 24, the following services were impacted by the Norton Healthcare cyber attack:

  • Same-day appointment for illnesses or minor injury
  • Emergency care
  • Some procedures including exams and appointments were required to be rescheduled.
  • Sharing test results and images
  • Prescription refill
  • Online payments for Norton MyChart

“We want to let the community know that we know that our processes are a little bit different now. They’re a bit different so that care can continue,” a WDRB report on May 24 cited Renee Murphy, Norton Healthcare’s chief marketing and communications officer.

“What happened to us in the cyber event, again, was something that happened to us and we’ve responded accordingly in a way that care can continue,” he said.

It is not clear how much data was exfiltrated and the sum ALPHV ransomware group has demanded for data stolen from the Norton Healthcare cyber attack. The Cyber Express reached out to the healthcare and we will update this report as we receive a response from them.

Norton Healthcare serves nearly 600,000 patients across Louisville, a year. It has $4.7 billion worth of assets with five hospitals, eight outpatient centers, 18 urgent care clinics, and 289 doctor’s offices.

BlackCat ransomware and US healthcare

ALPHV/BlackCat ransomware group is among the top three ransomware gangs by the number of victims till date. Healthcare sector continues to be one of its preferred targets.

The Health Sector Cybersecurity Coordination Center of the US Department of Health and Human Services in January alerted about the BlackCat ransomware group’s operations in the healthcare sector, particularly its triple extortion tactic.

This means that in addition to encrypting data and demanding a ransom, the group also threatens to leak the data and launch distributed denial-of-service attacks if the ransom is not paid.

BlackCat is believed to have emerged from Darkside and BlackMatter, and is connected to former members of the REvil group.

BlackCat has demanded ransom payments as high as $1.5 million, with affiliates retaining 80% to 90% of the extortion payments. The group frequently updates its tooling and arsenal as they undergo testing and usage cycles, making it a dynamic and evolving threat.

Security researchers have identified instances where BlackCat attackers have utilized a PowerShell command to download Cobalt Strike beacons on affected systems, as well as a penetration testing tool called Brute Ratel, which exhibits remote access features similar to Cobalt Strike.

The encryption methods employed by BlackCat include ChaCha20 and AES, along with six encryption modes: Full, HeadOnly, DotPattern, SmartPattern, AdvancedSmartPattern, and Auto.

BlackCat’s latest ransomware variant, developed in the memory-safe and cross-platform programming language Rust, provides the group with enhanced flexibility and capabilities.

Share this:

  • Share on LinkedIn (Opens in new window) LinkedIn
  • Share on Reddit (Opens in new window) Reddit
  • Share on X (Opens in new window) X
  • Share on Facebook (Opens in new window) Facebook
  • More
  • Email a link to a friend (Opens in new window) Email
  • Share on WhatsApp (Opens in new window) WhatsApp

Related

Tags: ALPHV Ransomware Grouphealthcare cyberattackNorton Healthcare ransomware attackThe Cyber ExpressThe Cyber Express News
Previous Post

All You Need to Know About The Nokoyawa Ransomware Group

Next Post

Linux Devices Attacked Via a Mirai Botnet Variant ‘IZ1H9’

Next Post
Mirai botnet cyber attack

Linux Devices Attacked Via a Mirai Botnet Variant 'IZ1H9'

Q1 2026 Threat Reports

❮ ❯
Cyble-Vision


Follow Us On Google News

Categories

  • Privacy Statement
  • Terms of Use
  • Write For Us

© 2026 The Cyber Express - Cybersecurity News and Magazine.

Welcome Back!

Login to your account below

Forgotten Password?

Retrieve your password

Please enter your username or email address to reset your password.

Log In

Add New Playlist

No Result
View All Result
  • Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board

© 2026 The Cyber Express - Cybersecurity News and Magazine.

-
00:00
00:00

Queue

Update Required Flash plugin
-
00:00
00:00



