




















• Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
The Cyber Express
  • MagazineDownload
  • Firewall Daily
    • All
    • Bug Bounty & Rewards
    • Dark Web News
    • Data Breach News
    • Hacker News
    • Ransomware News
    • Vulnerabilities
    Jensen Huang resigns

    Jensen Huang Exits Nvidia Days After the Board Said It Backed Him

    FaceStealer

    US Disrupts North Korea’s FaceStealer Campaign, Targets $1.2 Billion in Stolen Crypto

    SignDrop zero-day exploit

    New SignDrop Exploit Claims SYSTEM Access on Windows Through CLFS

    Microsoft 365 Outage

    Why Did Outlook Go Down? Microsoft Traced It to Its Own Servers

    WorkOS, AI Agent, Prompt Injection, Grok, Grok AI, Gemini, Fraud, Agentic AI, AI-assisted Cyberattacks

    WorkOS Says a Researcher’s Runaway AI Pentest Agent Copied Customer Sales Records

    Nvidia board investigation

    Why Is Nvidia Investigating Its Own CEO, and Can the Board Remove Him?

    weekly roundup

    The Cyber Express Weekly Roundup: FBI Blames North Korea for $6B Binance Hack, Hackers Turn Up the Heat on Europe’s Fridges and More

    Stockal cyberattack

    Stockal Confirms Unauthorized Trades in 13 Customer Accounts

    Alpine Linux servers

    Alpine Linux SSH Flaw Lets Attackers Log In Without a Password

    Trending Tags

    • blackbyte ransomware
    • Ransomware
    • lapsus$ ransomware
    • Apple
    • Apple vulnerability
  • Essentials
    • All
    • Compliance
    • Governance
    • Policy Updates
    • Regulations
    SEC, Misleading Cyber Disclosures, Financial data, financial data protection, SEC

    SEC Enforcement Fell 24% in Fiscal 2026

    ASD Essentials

    The Essential Eight Is Being Replaced: What Australian Organisations Need to Know

    SICW 2026

    AI Is Now Fighting on Both Sides of the Cyber War, Singapore Warns

    Morocco cybersecurity strategy

    Morocco Flags AI Threats, Prioritizes Critical Infrastructure Defense

    European Police Chiefs Convention 2026

    Europe’s Police Chiefs Face Growing Threat of AI-Driven Crime

    AI service security

    Hackers Are Stealing AI Keys. The Cost Can Reach $600,000

    AI security risks

    Sam Altman at UN Security Council: 6 AI Security Risks the World Cannot Ignore

    AI-enabled cyber attacks

    AI Gives Hackers an Edge Defenders Still Can’t Match, NCSC Warns

    Fraudulent SIM cards

    India’s DoT Warns Citizens Over SIM Fraud and IMEI Tampering

    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
    • All
    • How to
    • What is
    Infostealer Intelligence

    The 2026 Infostealer Intelligence Shortlist: Top 10 Vendors Security Teams Should Know

    Google Chrome

    How to Remove Saved Passwords From Google Chrome (And Why You Should)

    DPDP Rules, Cyble, DPDP Act, Cyble Vantage

    How Cyble’s Front-Row Vantage Can Help You in Complying to India’s DPDP Act

    Cybersecurity Countries

    The Top 8 Countries Leading the Cyber Defense Race in 2025

    link building

    The Link Building Secrets Your Competitors Don’t Want You to Know

    Supply Chain Attack

    Supply Chain Resilience and Physical Security: Lessons for 2025

    Healthcare cybersecurity trends of 2024

    Healthcare Cybersecurity: 2024 Was Tough, 2025 May Be Better

    CEO's Guide to Take-Down Services

    Shield Your Organization: CEO’s Perspective on Take-Down Services

    Azure sign-in Microsoft

    Microsoft Announces Mandatory MFA for Azure Sign-ins to Bolster Cloud Defenses

  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • All
    • Appointments
    • Budgets
    • Mergers & Aquisitions
    • Partnerships
    • Press Release
    • Startups
    Kerala Police Signs MoU With Cyble

    Kerala Police Signs MoU With Cyble to Use Threat Intelligence in Cybercrime Probes

    Gemini 4 Argon

    Gemini 4 Argon Restricted Over Cybersecurity Misuse Risks

    weekly roundup September 18 2026

    The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

    threat intelligence

    Cyble, UAE Cyber Security Council Unite Against Rising Cyber Threats

    Ukraine cybersecurity

    Zelensky Appoints Ihor Klymenko to Lead Ukraine’s Cybersecurity Center

    UK cyberattack rate

    UK Small Firms Bear Brunt of Rising Cyberattacks, Hiscox Finds

    Cyber Yodha Campaign

    Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

    UK Ukraine AI partnership

    Britain Gains Access to Ukraine’s ‘Goldmine’ of Battlefield AI Data

    Hims & Hers lawsuit

    FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices

    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
No Result
View All Result
  • MagazineDownload
  • Firewall Daily
    • All
    • Bug Bounty & Rewards
    • Dark Web News
    • Data Breach News
    • Hacker News
    • Ransomware News
    • Vulnerabilities
    Jensen Huang resigns

    Jensen Huang Exits Nvidia Days After the Board Said It Backed Him

    FaceStealer

    US Disrupts North Korea’s FaceStealer Campaign, Targets $1.2 Billion in Stolen Crypto

    SignDrop zero-day exploit

    New SignDrop Exploit Claims SYSTEM Access on Windows Through CLFS

    Microsoft 365 Outage

    Why Did Outlook Go Down? Microsoft Traced It to Its Own Servers

    WorkOS, AI Agent, Prompt Injection, Grok, Grok AI, Gemini, Fraud, Agentic AI, AI-assisted Cyberattacks

    WorkOS Says a Researcher’s Runaway AI Pentest Agent Copied Customer Sales Records

    Nvidia board investigation

    Why Is Nvidia Investigating Its Own CEO, and Can the Board Remove Him?

    weekly roundup

    The Cyber Express Weekly Roundup: FBI Blames North Korea for $6B Binance Hack, Hackers Turn Up the Heat on Europe’s Fridges and More

    Stockal cyberattack

    Stockal Confirms Unauthorized Trades in 13 Customer Accounts

    Alpine Linux servers

    Alpine Linux SSH Flaw Lets Attackers Log In Without a Password

    Trending Tags

    • blackbyte ransomware
    • Ransomware
    • lapsus$ ransomware
    • Apple
    • Apple vulnerability
  • Essentials
    • All
    • Compliance
    • Governance
    • Policy Updates
    • Regulations
    SEC, Misleading Cyber Disclosures, Financial data, financial data protection, SEC

    SEC Enforcement Fell 24% in Fiscal 2026

    ASD Essentials

    The Essential Eight Is Being Replaced: What Australian Organisations Need to Know

    SICW 2026

    AI Is Now Fighting on Both Sides of the Cyber War, Singapore Warns

    Morocco cybersecurity strategy

    Morocco Flags AI Threats, Prioritizes Critical Infrastructure Defense

    European Police Chiefs Convention 2026

    Europe’s Police Chiefs Face Growing Threat of AI-Driven Crime

    AI service security

    Hackers Are Stealing AI Keys. The Cost Can Reach $600,000

    AI security risks

    Sam Altman at UN Security Council: 6 AI Security Risks the World Cannot Ignore

    AI-enabled cyber attacks

    AI Gives Hackers an Edge Defenders Still Can’t Match, NCSC Warns

    Fraudulent SIM cards

    India’s DoT Warns Citizens Over SIM Fraud and IMEI Tampering

    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
    • All
    • How to
    • What is
    Infostealer Intelligence

    The 2026 Infostealer Intelligence Shortlist: Top 10 Vendors Security Teams Should Know

    Google Chrome

    How to Remove Saved Passwords From Google Chrome (And Why You Should)

    DPDP Rules, Cyble, DPDP Act, Cyble Vantage

    How Cyble’s Front-Row Vantage Can Help You in Complying to India’s DPDP Act

    Cybersecurity Countries

    The Top 8 Countries Leading the Cyber Defense Race in 2025

    link building

    The Link Building Secrets Your Competitors Don’t Want You to Know

    Supply Chain Attack

    Supply Chain Resilience and Physical Security: Lessons for 2025

    Healthcare cybersecurity trends of 2024

    Healthcare Cybersecurity: 2024 Was Tough, 2025 May Be Better

    CEO's Guide to Take-Down Services

    Shield Your Organization: CEO’s Perspective on Take-Down Services

    Azure sign-in Microsoft

    Microsoft Announces Mandatory MFA for Azure Sign-ins to Bolster Cloud Defenses

  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • All
    • Appointments
    • Budgets
    • Mergers & Aquisitions
    • Partnerships
    • Press Release
    • Startups
    Kerala Police Signs MoU With Cyble

    Kerala Police Signs MoU With Cyble to Use Threat Intelligence in Cybercrime Probes

    Gemini 4 Argon

    Gemini 4 Argon Restricted Over Cybersecurity Misuse Risks

    weekly roundup September 18 2026

    The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

    threat intelligence

    Cyble, UAE Cyber Security Council Unite Against Rising Cyber Threats

    Ukraine cybersecurity

    Zelensky Appoints Ihor Klymenko to Lead Ukraine’s Cybersecurity Center

    UK cyberattack rate

    UK Small Firms Bear Brunt of Rising Cyberattacks, Hiscox Finds

    Cyber Yodha Campaign

    Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

    UK Ukraine AI partnership

    Britain Gains Access to Ukraine’s ‘Goldmine’ of Battlefield AI Data

    Hims & Hers lawsuit

    FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices

    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
No Result
View All Result
The Cyber Express
No Result
View All Result

MGM Resorts Cyber Attack: The Assault, Intrusion, and the ‘Unknown User’ Through the Hacker’s Lens

ALPHV noted the appearance of a user on the 'MGM victim chat' just a few hours after deploying the ransomware, as stated in their dark web post.

Editorial by Editorial
September 15, 2023
in Firewall Daily, Ransomware News
0
MGM Resorts Cyber Attack
585
SHARES
3.2k
VIEWS
Share on LinkedInShare on Twitter

The ALPHV ransomware group, suspected to be behind the MGM Resorts cyber attack, has finally spoken out regarding the security incident.

Contrary to initial assumptions, the renowned global powerhouse in the casino and resort industry, MGM Resorts, initially did not fall prey to ransomware during the cyber attack. However, they later did.

ALPHV has provided clarification on its dark web platform, stating that ransomware was not deployed until a specific period had passed, during which the hackers attempted to establish communication with the MGM group.

The MGM Resorts Cyber Attack: ALPHV Ransomware Group’s Account

The much talked about MGM Resorts cyberattack has been officially confirmed as an incident involving unauthorized access and the acquisition of administrator privileges for their Okta Sync servers, by the ransomware group.

Okta, a California-based IT service management company, plays a central role in this breach. The company provides cloud-based software for ensuring secure user access, authentication, and the management of applications and websites.
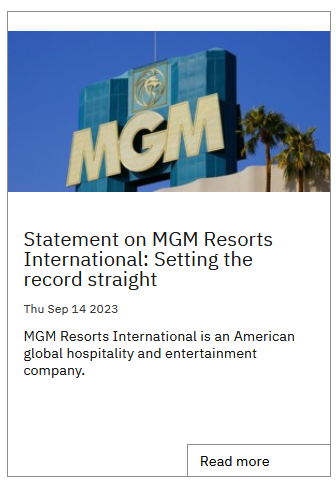
MGM Resorts cyber attack
ALPHV’s leak site post (Photo: Falcon Feeds/ Twitter)

ALPHV, also known as the BlackCat ransomware group, stated, “We have made multiple attempts to reach out to MGM Resorts International.

However, their efforts to engage with MGM Resorts officials were not reciprocated. Instead, the company opted to safeguard its networks by shutting down their systems.

ALPHV also revealed that they observed MGM Resorts taking swift action to shut down all their Okta Sync servers. It became evident to ALPHV that MGM Resorts’ IT team had detected external entities present on their Okta Agents servers.
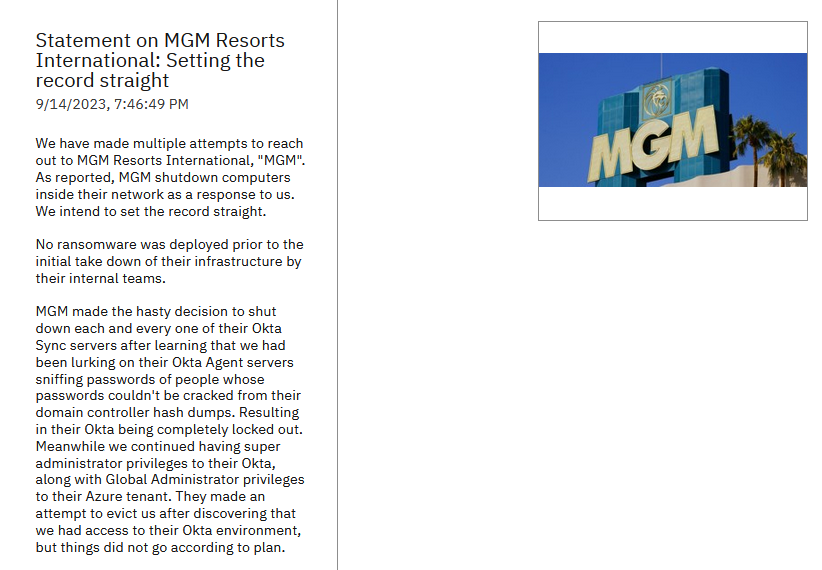
MGM Resorts cyber attack
ALPHV’s narration of the MGM Resorts data breach (Photo: Falcon Feeds/ Twitter)

ALPHV was looking for passwords to gain access and remain unnoticed for logging in through an employee’s account credentials as part of the MGM Resorts ransomware attack.

In their post, ALPHV acknowledged encountering challenges when attempting to crack passwords from the domain controller hash dumps. This eventually resulted in the complete lockdown of Okta.

During this process, ALPHV emphasized that they successfully obtained full access to super administrator privileges within the Okta system, ultimately paving the way for the MGM Resorts cyber attack.

The hackers boasted of gaining Global Administrator privileges to their Azure tenant as well, which helped continue with the MGM ransomware attack.

MGM IT Team’s Struggle to Remove ALPHV Ransomware Group

ALPHV also elaborated on the situation where the MGM Resorts cybersecurity team attempted to evict them. “They made an attempt to evict us after discovering that we had access to their Okta environment, but things did not go according to plan.”

“On Sunday night (September 10, 2023) MGM implemented conditional restrictions that bared all access to their Okta (MGMResorts.okta.com) environment due to inadequate administrative capabilities and weak incident response playbooks,” ALPHV wrote.

At each step of the MGM Resorts cyber attack, ALPHV met with hurdles, however, they managed to gain access to the systems and noted in the dark web post where the global casino giant lagged in implementing security protocols.
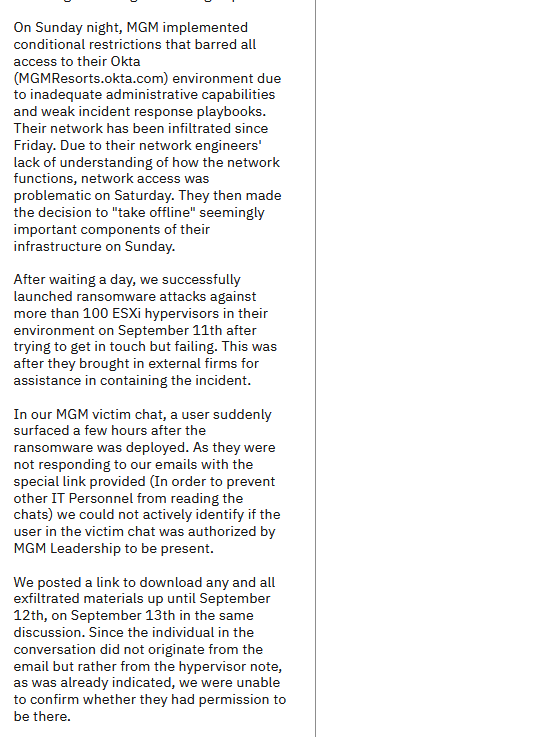
MGM Resorts cyber attack
ALPHV talks about an unknown user on MGM network (Photo: Falcon Feeds/ Twitter)

ALPHV claimed that the MGM Resorts networks were infiltrated not from Sunday but from Friday, 8 September, 2023 making it the seventh day of the MGM Resorts hacking.
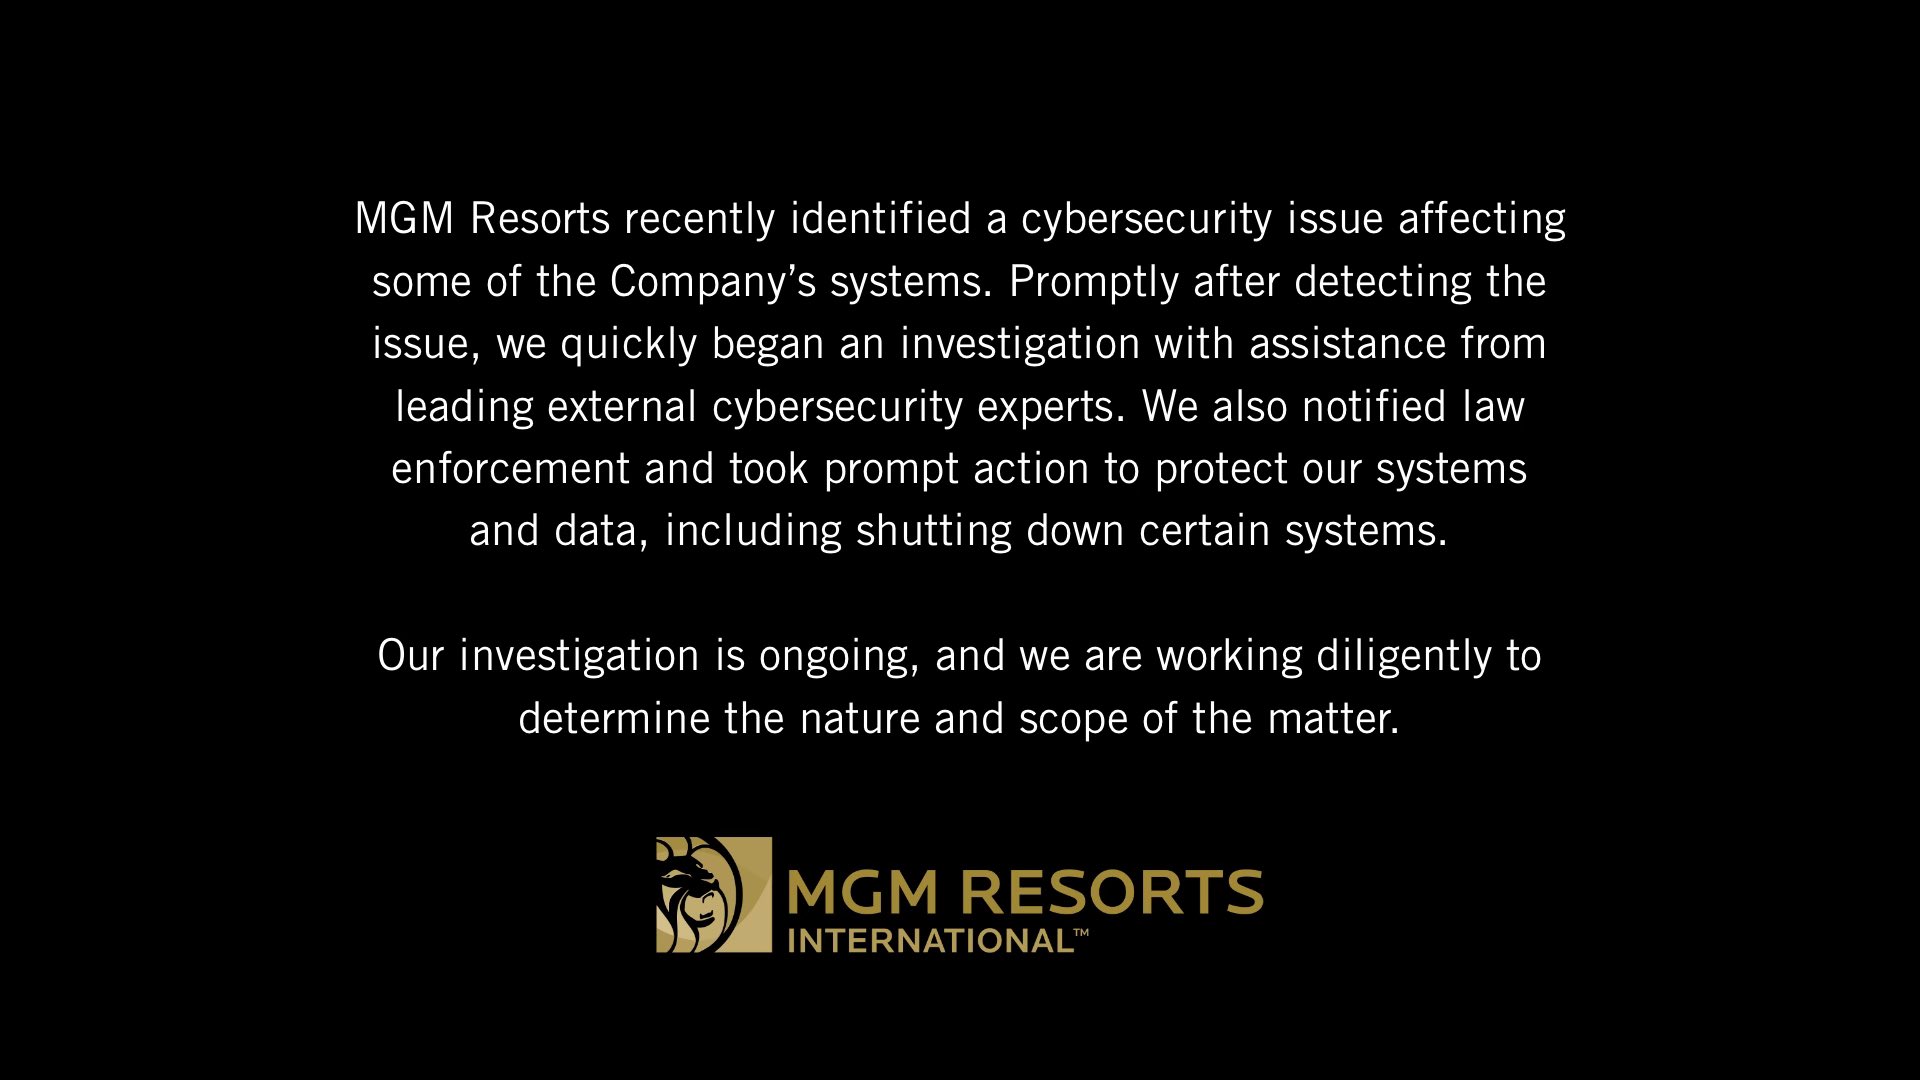
MGM Resorts cyber attack
MGM Resorts’ alert on Twitter

On September 11, 2023, MGM Resorts posted the above alert on its Twitter/X account, notifying the public that they had recently detected a cybersecurity issue.

MGM Resorts Could Have Handled it Better, Says ALPHV

The ransomware group stated that MGM Resorts’ network engineers could have managed the cyberattack more effectively on Saturday.

On Sunday, one day after the initial incident, ALPHV executed a ransomware attack on MGM Resorts.

They targeted over 100 ESXi hypervisors in their environment on September 11. Meanwhile, they made several unsuccessful attempts to communicate with the MGM authorities who stirred clear and remained mum.

Unknown User on MGM Resorts Network

ALPHV noted the appearance of a user on the ‘MGM victim chat’ just a few hours after deploying the ransomware, as stated in their post on their leak site concerning the MGM Resorts hack.

This user, however, remained unresponsive to ALPHV and refrained from clicking on any links sent by the cybercriminal group.

The hackers sent emails with special links to the user. At this point, ALPHV was left unsure if the user was from the company or was someone with unauthorized access.

ALPHV wanted to prevent other IT Personnel from MGM Resorts from reading the chats.

This shows that someone who was accessing or monitoring the systems of MGM Resorts learned about negotiations but did not click on any links to maintain caution and not increase the attack.

The link to download all the exfiltrated data from the MGM Resorts systems was left accessible on the same chat, to the company for perusal for two days on September 12 and 13.

Speculating about the background and identity of the unknown user, ALPHV concluded, “Since the individual in the conversation did not originate from the email but rather from the hypervisor note, as was already indicated, we were unable to confirm whether they had permission to be there.”

The uncertainty surrounding this situation explains the time taken by ALPHV to claim the MGM Resorts cyber attack if they started with their heist a week ago.

Media Disclaimer: This report is based on internal and external research obtained through various means. The information provided is for reference purposes only, and users bear full responsibility for their reliance on it. The Cyber Express assumes no liability for the accuracy or consequences of using this information.

Share this:

  • Share on LinkedIn (Opens in new window) LinkedIn
  • Share on Reddit (Opens in new window) Reddit
  • Share on X (Opens in new window) X
  • Share on Facebook (Opens in new window) Facebook
  • More
  • Email a link to a friend (Opens in new window) Email
  • Share on WhatsApp (Opens in new window) WhatsApp

Related

Tags: ALPHV MGM attackBlackCat MGM ransomware attackCasino ransomware attackHospitality sector ransomwareMGM Resorts cyber attackMGM Resorts Ransomware attackThe Cyber ExpressThe Cyber Express News
Previous Post

Indian Banks Under Attack: Hackers Target Dakshin Bihar Gramin Bank, City Union Bank

Next Post

Gerchik Trading Ecosystem Faces Data Breach Risk: What You Need to Know

Next Post
Gerchik Trading Ecosystem data breach

Gerchik Trading Ecosystem Faces Data Breach Risk: What You Need to Know

Q1 2026 Threat Reports

❮ ❯
Cyble-Vision


Follow Us On Google News

Categories

  • Privacy Statement
  • Terms of Use
  • Write For Us

© 2026 The Cyber Express - Cybersecurity News and Magazine.

Welcome Back!

Login to your account below

Forgotten Password?

Retrieve your password

Please enter your username or email address to reset your password.

Log In

Add New Playlist

No Result
View All Result
  • Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board

© 2026 The Cyber Express - Cybersecurity News and Magazine.

-
00:00
00:00

Queue

Update Required Flash plugin
-
00:00
00:00



