• About Us
  • Contact Us
  • Editorial Calendar
  • Careers
  • The Cyber Express by Cyble Vulnerability Disclosure Policy
  • Cyble Trust Portal
The Cyber Express
  • MagazineDownload
  • Firewall Daily
    • All
    • Bug Bounty & Rewards
    • Dark Web News
    • Data Breach News
    • Hacker News
    • Ransomware News
    • Vulnerabilities
    Operation Serengeti III

    INTERPOL’s Operation Serengeti III Disrupts 10,909 Malicious Networks

    AI cyberattack simulations

    Japan AI Cyberattack Simulations Planned as PHP Flaws Disrupt Services

    Yonsei University cyberattack

    Yonsei University Cyberattack Hits 10,000 Students, Months After Sogang Breach

    CVE-2026-109618

    PHP2Shell Patch Rush Takes Wikipedia, Govt Sites Offline

    SafePay ransomware

    FBI, CISA Warn SafePay Ransomware Has Hit 600+ Victims

    BAE Systems cyberattack

    BAE Systems Cyberattack Halts Bankruptcy Notices at Every U.S. Federal Court

    fake driving licence

    No Lessons, No Test, No Travel: Dubai Police Bust AED 10,000 Licence Scheme

    generative AI in research

    AI Can’t Judge Your Paper: EU Updates Guidelines on Peer Review and AI Agents

    ASD Essentials

    The Essential Eight Is Being Replaced: What Australian Organisations Need to Know

    Trending Tags

    • blackbyte ransomware
    • Ransomware
    • lapsus$ ransomware
    • Apple
    • Apple vulnerability
  • Essentials
    • All
    • Compliance
    • Governance
    • Policy Updates
    • Regulations
    ASD Essentials

    The Essential Eight Is Being Replaced: What Australian Organisations Need to Know

    SICW 2026

    AI Is Now Fighting on Both Sides of the Cyber War, Singapore Warns

    Morocco cybersecurity strategy

    Morocco Flags AI Threats, Prioritizes Critical Infrastructure Defense

    European Police Chiefs Convention 2026

    Europe’s Police Chiefs Face Growing Threat of AI-Driven Crime

    AI service security

    Hackers Are Stealing AI Keys. The Cost Can Reach $600,000

    AI security risks

    Sam Altman at UN Security Council: 6 AI Security Risks the World Cannot Ignore

    AI-enabled cyber attacks

    AI Gives Hackers an Edge Defenders Still Can’t Match, NCSC Warns

    Fraudulent SIM cards

    India’s DoT Warns Citizens Over SIM Fraud and IMEI Tampering

    EU cybersecurity incidents

    EU Cybersecurity Response Hampered by Critical Information Gaps

    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
    • All
    • How to
    • What is
    Infostealer Intelligence

    The 2026 Infostealer Intelligence Shortlist: Top 10 Vendors Security Teams Should Know

    Google Chrome

    How to Remove Saved Passwords From Google Chrome (And Why You Should)

    DPDP Rules, Cyble, DPDP Act, Cyble Vantage

    How Cyble’s Front-Row Vantage Can Help You in Complying to India’s DPDP Act

    Cybersecurity Countries

    The Top 8 Countries Leading the Cyber Defense Race in 2025

    link building

    The Link Building Secrets Your Competitors Don’t Want You to Know

    Supply Chain Attack

    Supply Chain Resilience and Physical Security: Lessons for 2025

    Healthcare cybersecurity trends of 2024

    Healthcare Cybersecurity: 2024 Was Tough, 2025 May Be Better

    CEO's Guide to Take-Down Services

    Shield Your Organization: CEO’s Perspective on Take-Down Services

    Azure sign-in Microsoft

    Microsoft Announces Mandatory MFA for Azure Sign-ins to Bolster Cloud Defenses

  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • All
    • Appointments
    • Budgets
    • Mergers & Aquisitions
    • Partnerships
    • Press Release
    • Startups
    Kerala Police Signs MoU With Cyble

    Kerala Police Signs MoU With Cyble to Use Threat Intelligence in Cybercrime Probes

    Gemini 4 Argon

    Gemini 4 Argon Restricted Over Cybersecurity Misuse Risks

    weekly roundup September 18 2026

    The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

    threat intelligence

    Cyble, UAE Cyber Security Council Unite Against Rising Cyber Threats

    Ukraine cybersecurity

    Zelensky Appoints Ihor Klymenko to Lead Ukraine’s Cybersecurity Center

    UK cyberattack rate

    UK Small Firms Bear Brunt of Rising Cyberattacks, Hiscox Finds

    Cyber Yodha Campaign

    Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

    UK Ukraine AI partnership

    Britain Gains Access to Ukraine’s ‘Goldmine’ of Battlefield AI Data

    Hims & Hers lawsuit

    FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices

    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
No Result
View All Result
The Cyber Express
No Result
View All Result
Home Cyber News

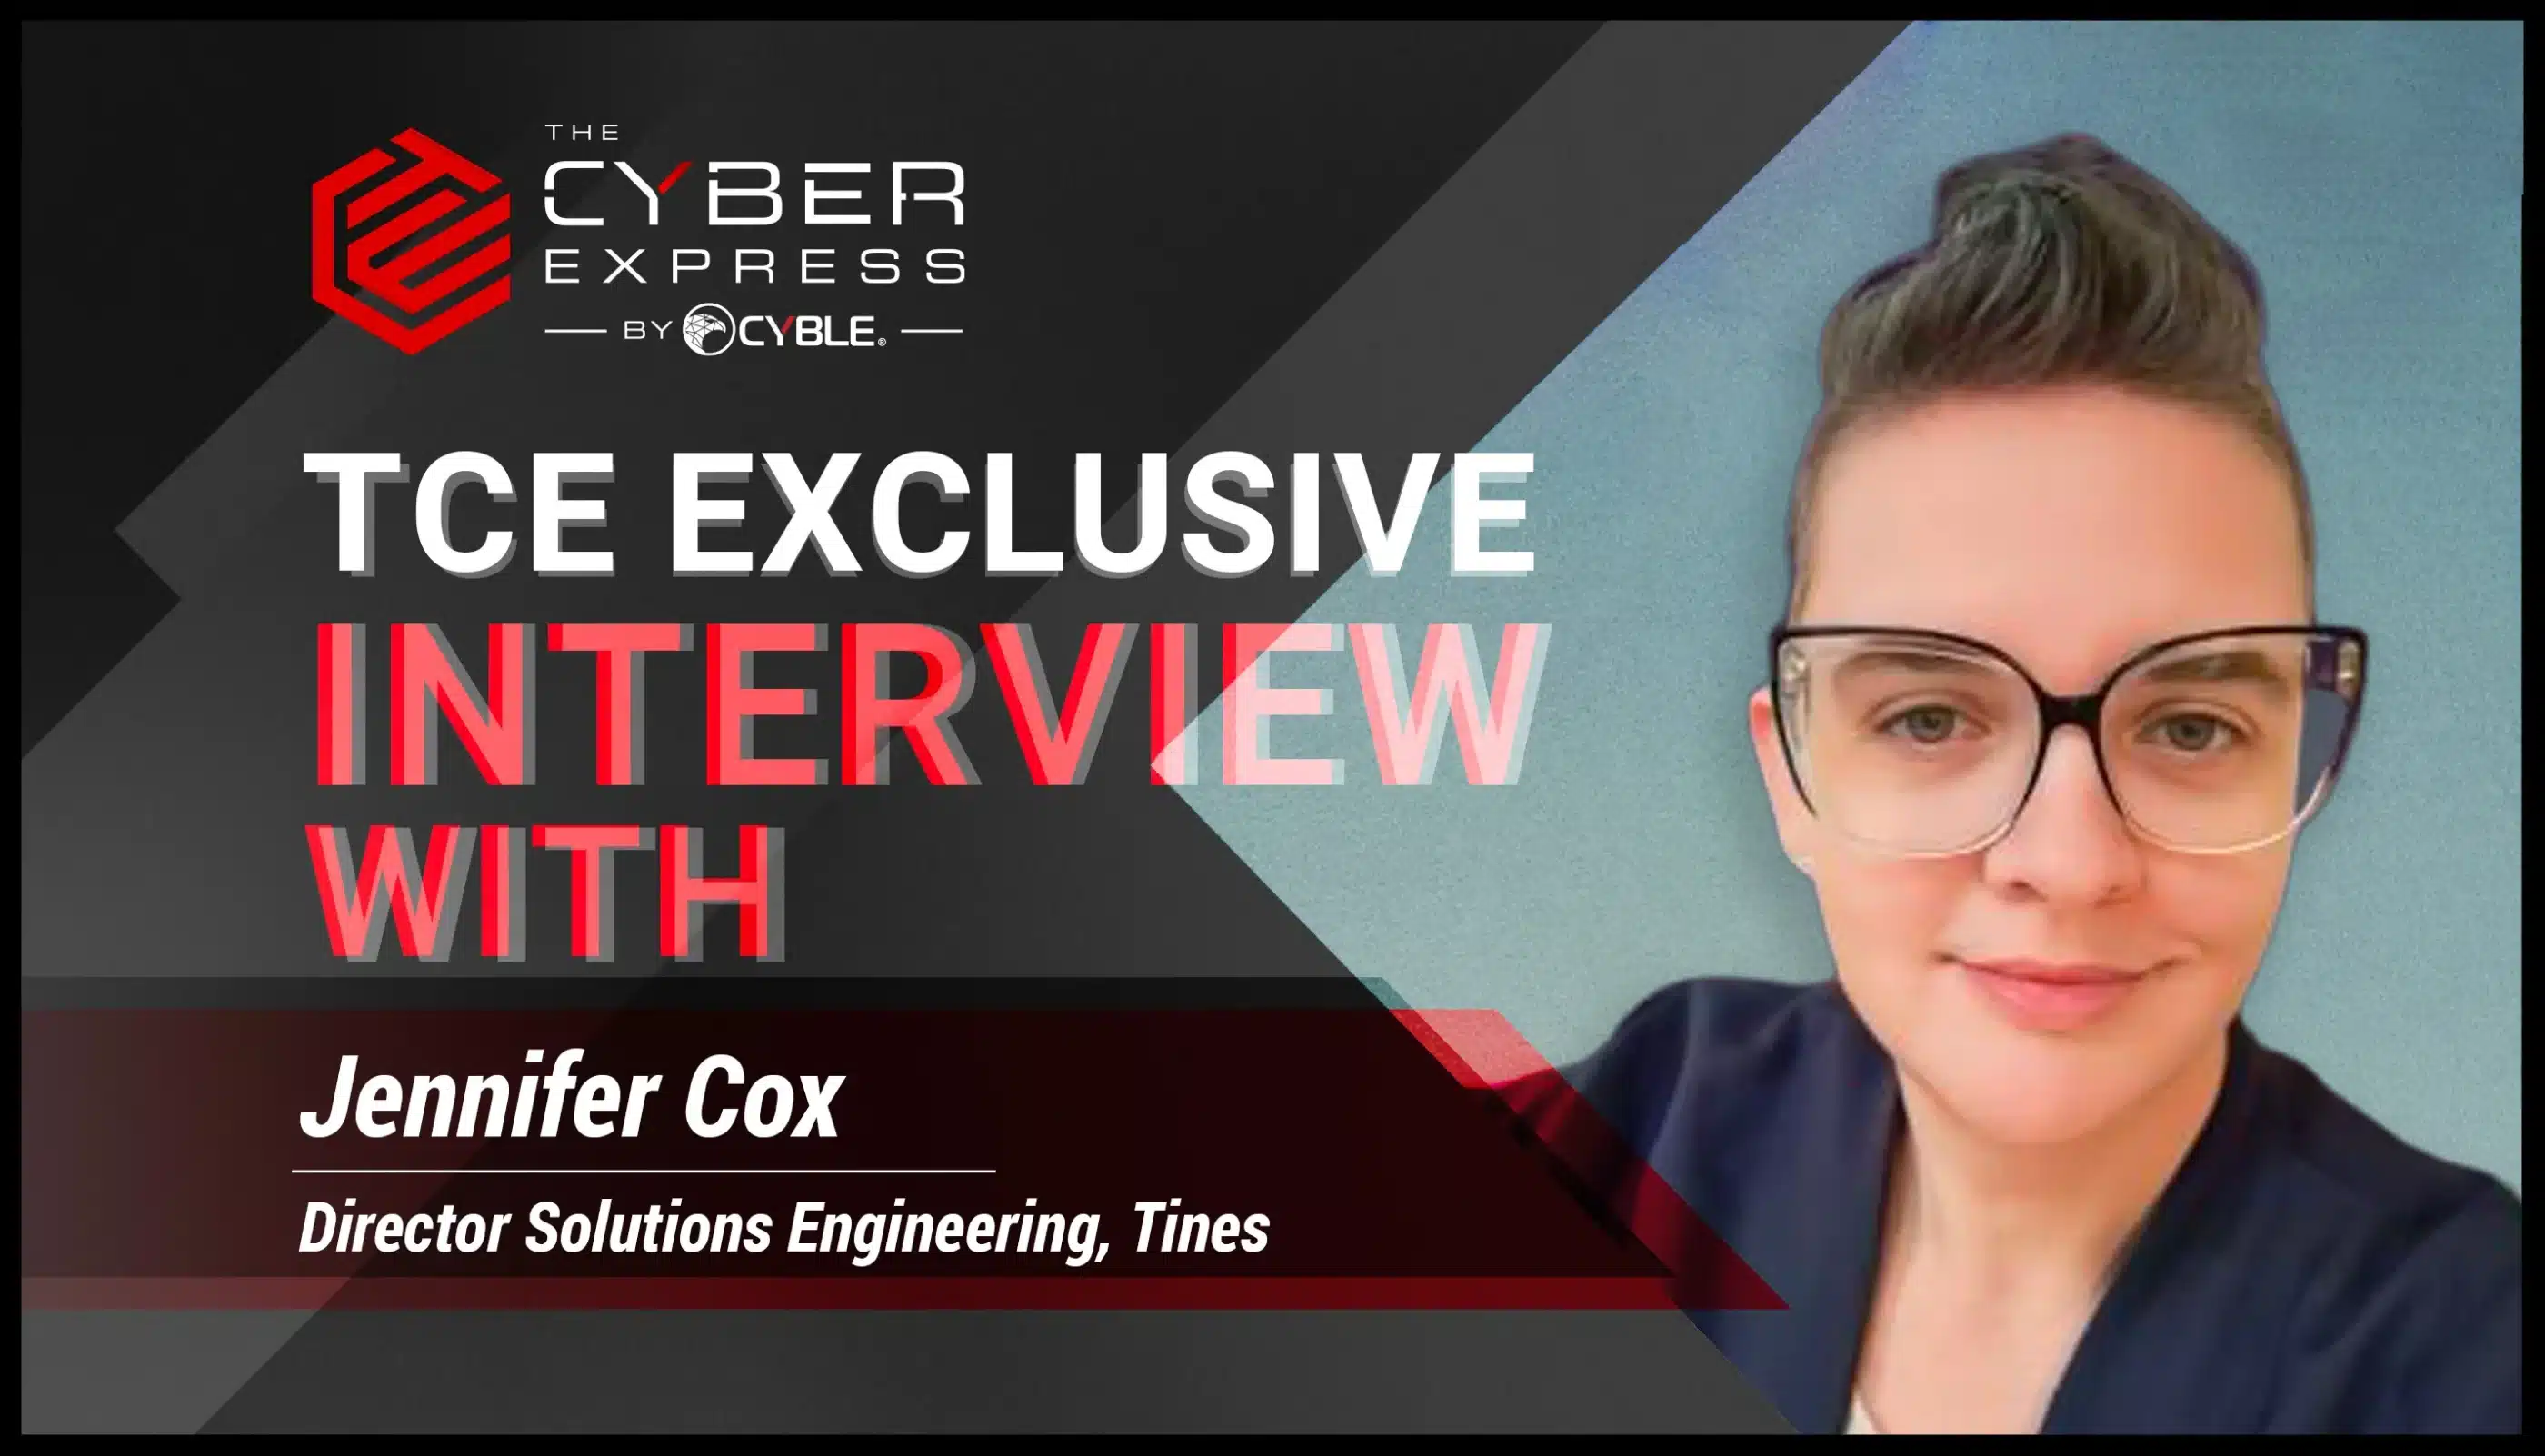
Jennifer Cox on Why Most Security Teams Never See the Real Benefits of Automation

Samiksha Jain by Samiksha Jain
March 31, 2026
in Cyber News
0
Jennifer Cox Interview
598
SHARES
3.3k
VIEWS
Share on LinkedInShare on Twitter

Nineteen years is a long time to watch an industry transform — and Jennifer Cox has had a front-row seat to all of it.

Two decades ago, cybersecurity barely made it onto the agenda. Today it sits at the top of it. Cox has worked through every stage of that change — across communication strategy, cloud security, global program delivery, and now security automation.

As Director of Solutions Engineering at Tines, she works at a practical intersection: helping organizations cut through the noise of over-engineered tools and actually automate security workflows in ways that stick. It’s less about the technology and more about getting the people, processes, and priorities aligned — something Cox has spent the better part of her career figuring out.

A Bronze Stevie Award winner and recognised across multiple industry honours, she measures success not in tools deployed but in whether security teams are operating with less chaos and whether boards finally understand what they’re being asked to fund.

In this interview, Cox talks about the real barriers to security automation, how teams can stop drowning in alerts, what it takes to speak the board’s language, and why women in cybersecurity should stop waiting to feel ready.

Read Full Interview
Jennifer Cox Interview: The Human Side of Automation

TCE: You have nearly two decades of experience across cybersecurity, communication strategy, and global program delivery. What key changes in the cybersecurity landscape have most influenced how organizations approach security today?

Jennifer Cox: Over nearly two decades, the biggest shift I’ve seen is that cybersecurity has moved from “IT problem” to business risk that boards and regulators actively care about.  The rise of ransomware, supply chain attacks, and SaaS sprawl means security is now tightly linked to revenue continuity, brand, and trust.

At the same time, the attack surface has exploded: cloud, remote work, APIs, identities, and third parties have made traditional perimeter thinking obsolete.  That’s forced organisations to move from reactive, tool‑centric security to more proactive, automated, and outcomes‑driven programs that tie controls to real business processes.

TCE: In your role at Tines, you work closely with organizations implementing security automation. What are the biggest operational challenges security teams face when trying to automate their workflows?

Jennifer Cox: When I work with teams on automation, the tech is rarely the hardest part; it’s people and process.  Many SOCs are stuck in “semi‑automation” mode, where analysts still babysit workflows and manually approve every decision, so they never see the real benefits.
The other big challenge is skills and ownership: you need people who understand both the security problem and how to design reliable automated workflows.  Without that, you end up with brittle playbooks, over‑engineered logic, and fear of “breaking production,” which slows everything down.

TCE: Security automation is often positioned as a way to reduce alert fatigue and improve response times. From what you’ve seen, where are organizations gaining the most measurable benefits from automation today?

Jennifer Cox: The most measurable wins I see today are in three areas: alert handling, investigations, and compliance.  Automating enrichment, correlation, and deduplication can cut the number of alerts reaching humans by the majority, which directly reduces fatigue and backlog.

On the investigation side, well‑designed workflows shrink time‑to‑conclusion from hours to minutes by gathering evidence, checking context, and making initial determinations automatically.  And in governance and compliance, automating evidence collection, control checks, and risk workflows saves huge amounts of manual effort and audit pain.

TCE: Many organizations invest heavily in security tools but still struggle with complexity and integration. What should security leaders look for when evaluating automation platforms to ensure they deliver real operational value?

Jennifer Cox: Security leaders should stop buying “feature lists” and start buying outcomes. I’d look for platforms that are easy enough for your analysts to own day‑to‑day, integrate cleanly with your existing tools, and make it simple to iterate on workflows as your environment changes.

You also want strong guardrails: testing, version control, approval paths, and observability so you can trust automation in production.  Finally, pay close attention to how the platform handles failure modes and exceptions; resilient error handling is the difference between “nice demo” and genuine operational value.

TCE: You specialize in bridging complex technical solutions with business outcomes. How can security teams better communicate the value of cybersecurity investments to executive leadership and boards?

Jennifer Cox: Security teams need to translate technical noise into business‑relevant stories. That means moving away from raw counts of alerts or vulnerabilities and focusing on metrics like reduction in high‑risk exposure, time to contain business‑critical incidents, or improved uptime for key services.

I encourage teams to tie every major initiative to a clear narrative: what business process it protects, which risk or regulatory obligation it addresses, and what would happen if we didn’t do it.  Executives don’t need every detail of the exploit chain; they need to understand impact, options, and confidence levels so they can make informed decisions.

Jennifer Cox Interview

TCE: As cloud adoption continues to grow, how has the role of solutions engineering evolved in helping organizations maintain strong security and compliance frameworks?

Jennifer Cox: As cloud adoption has grown, solutions engineering has shifted from “here’s how the product works” to “here’s how this fits into your entire security and compliance ecosystem.”  You’re no longer just doing feature demos; you’re co‑designing architectures that span multiple clouds, SaaS platforms, and regulatory regimes.

It also means being comfortable speaking both Kubernetes and boardroom. You’re often the translator between engineering, security, legal, and the business, making sure that what’s being built is secure, automatable, and actually usable by the teams who’ll live with it every day.

TCE: Security teams today operate under constant pressure from growing threat volumes and limited resources. What strategies can help organizations build more resilient and efficient security operations?

Jennifer Cox: Resilient security operations start with being ruthless about focus. Not every alert or control is created equal, so prioritisation and risk‑based workflows matter more than ever.  Automation should handle repetitive, low‑risk work so humans can focus on complex investigations, threat hunting, and continuous improvement.

I also push teams to build in recovery as a feature: runbooks, tabletop exercises, and post‑incident reviews that feed back into updated playbooks and automations.  Over time, this closes the loop; every incident makes your people, your processes, and your automation a little sharper.

TCE: Having led global programs and cross-functional teams, what leadership approaches have helped you align technical teams with broader business objectives?

Jennifer Cox: Leading global and cross‑functional teams, I’ve found that clarity plus autonomy beats command‑and‑control every time.  If people understand the “why” behind an objective and how it ties to the business, they’ll usually find better ways to get there than anything you could script.

I focus on three things: listening hard first, co‑creating goals with the team, and being transparent about trade‑offs.  That creates psychological safety, which is essential in security, because you want people to surface bad news early, challenge assumptions, and admit when something isn’t working.

TCE: As we mark International Women’s Day, what meaningful progress have you seen in the representation and leadership of women in cybersecurity over the years?

Jennifer Cox: We’ve seen meaningful progress, but it’s been a grind, not a fairy tale. Women now hold a growing share of managerial and CISO roles globally, and more are in hiring and budget‑owning positions than even a few years ago.  We’re also seeing increased funding and visibility for women‑led cybersecurity companies, communities, and initiatives.

At the same time, representation at the very top; C‑suite and board level; is still far too low, and retention remains a challenge.  So I’d describe the moment as “real momentum with plenty of unfinished work,” which is why I stay so active in communities like WiCyS and mentoring

TCE: For women looking to build long-term careers in cybersecurity and technical leadership, what advice would you share based on your own journey in the industry?

Jennifer Cox: First, you absolutely belong here; even if you don’t look like the stereotype of a security professional.  Don’t wait to feel “ready” before you go for the role, the talk, or the promotion; my own career is full of moments where I said yes, panicked a little, and then grew into it. Second, build your support system as intentionally as you build your skills: mentors, sponsors, peers, and communities that will advocate for you when you’re not in the room.  And finally, protect your energy; burnout and bias are real, but so is your right to step away from unhealthy environments and choose spaces where you can actually thrive.
Share this:

  • Share on LinkedIn (Opens in new window) LinkedIn
  • Share on Reddit (Opens in new window) Reddit
  • Share on X (Opens in new window) X
  • Share on Facebook (Opens in new window) Facebook
  • More
  • Email a link to a friend (Opens in new window) Email
  • Share on WhatsApp (Opens in new window) WhatsApp

Related

Tags: cloud securityJennifer CoxJennifer Cox Interviewsecurity automationThe Cyber ExpressThe Cyber Express Interview
Previous Post

Axios Supply Chain Attack Exposes Developers to Hidden Malware

Next Post

Hacked, Leaked, Public—What the Kash Patel Email Hack Is Really About

Next Post
Kash Patel email hack

Hacked, Leaked, Public—What the Kash Patel Email Hack Is Really About

Q1 2026 Threat Reports

❮ ❯
Cyble-Vision


Follow Us On Google News

Latest Cyber News

Operation Serengeti III
Firewall Daily

INTERPOL’s Operation Serengeti III Disrupts 10,909 Malicious Networks

October 23, 2026
AI cyberattack simulations
Firewall Daily

Japan AI Cyberattack Simulations Planned as PHP Flaws Disrupt Services

October 23, 2026
software supply chain security
Cyber News

Why Fintechs Must Treat Software Supply Chain Security as an Enterprise Risk

October 23, 2026
AI-built websites
Cyber News

Live API Keys Found in Public Code of AI-Built Websites, Cyble Research Shows

October 22, 2026

Categories

Web Stories

Do This on Telegram, Your Bank Account Will Become Zero
If You Install the iOS 18 Beta, Your iPhone Could Be Hacked
Cricket World Cup Ticketing Systems Under Cybersecurity
Cyber Threats and Online Ticket Scams During the NBA Finals
Biometric Data Security: Protecting Sensitive Information

About

The Cyber Express

#1 Trending Cybersecurity News and Magazine

The Cyber Express is a handbook for all stakeholders of the internet that provides information security professionals with the latest news, updates and knowledge they need to combat cyber threats.


Contact

For editorial queries: [email protected]

For marketing and Sales: [email protected]


Quick Links

  • About Us
  • Contact Us
  • Editorial Calendar
  • Careers
  • The Cyber Express by Cyble Vulnerability Disclosure Policy
  • Cyble Trust Portal

Our Address

We’re remote friendly, with office locations around the world:

San Francisco, Atlanta, Rome,
Dubai, Mumbai, Bangalore, Hyderabad,  Singapore, Jakarta, Sydney, and Melbourne


Headquarters:

The Cyber Express LLC
10080 North Wolfe Road, Suite SW3-200, Cupertino, CA, US 95014


India Office:

Cyber Express Media Network
HD-021, 4th Floor, C Wing, Building No.4. Nesco IT Park, WE Highway, Goregaon East, Mumbai, Maharashtra, India – 4000063

  • Privacy Statement
  • Terms of Use
  • Write For Us

© 2026 The Cyber Express - Cybersecurity News and Magazine.

Welcome Back!

Login to your account below

Forgotten Password?

Retrieve your password

Please enter your username or email address to reset your password.

Log In

Add New Playlist

No Result
View All Result
  • Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board

© 2026 The Cyber Express - Cybersecurity News and Magazine.

Are you sure want to unlock this post?
Unlock left : 0
Are you sure want to cancel subscription?
-
00:00
00:00

Queue

Update Required Flash plugin
-
00:00
00:00
Do This on Telegram, Your Bank Account Will Become Zero If You Install the iOS 18 Beta, Your iPhone Could Be Hacked Cricket World Cup Ticketing Systems Under Cybersecurity Cyber Threats and Online Ticket Scams During the NBA Finals Biometric Data Security: Protecting Sensitive Information