



















• Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
The Cyber Express
  • MagazineDownload
  • Firewall Daily
    • All
    • Bug Bounty & Rewards
    • Dark Web News
    • Data Breach News
    • Hacker News
    • Ransomware News
    • Vulnerabilities
    WorkOS, AI Agent, Prompt Injection, Grok, Grok AI, Gemini, Fraud, Agentic AI, AI-assisted Cyberattacks

    WorkOS Says a Researcher’s Runaway AI Pentest Agent Copied Customer Sales Records

    Nvidia board investigation

    Why Is Nvidia Investigating Its Own CEO, and Can the Board Remove Him?

    weekly roundup

    The Cyber Express Weekly Roundup: FBI Blames North Korea for $6B Binance Hack, Hackers Turn Up the Heat on Europe’s Fridges and More

    Stockal cyberattack

    Stockal Confirms Unauthorized Trades in 13 Customer Accounts

    Alpine Linux servers

    Alpine Linux SSH Flaw Lets Attackers Log In Without a Password

    Queens Public Library ransomware attack

    Ransomware Just Took New York’s Queens Library Offline, and It’s Not the First

    Amadeus cybersecurity incident

    Airline Data Breach Widens as Singapore Airlines Reports 46,000 Affected Records

    refrigeration cyberattacks

    After Supermarket Freezers, Hackers Turn Up the Heat on France’s Blood Supply

    university supercomputer hacking

    Two Canadians Accused of Turning US University Supercomputers Into Crypto Miners

    Trending Tags

    • blackbyte ransomware
    • Ransomware
    • lapsus$ ransomware
    • Apple
    • Apple vulnerability
  • Essentials
    • All
    • Compliance
    • Governance
    • Policy Updates
    • Regulations
    ASD Essentials

    The Essential Eight Is Being Replaced: What Australian Organisations Need to Know

    SICW 2026

    AI Is Now Fighting on Both Sides of the Cyber War, Singapore Warns

    Morocco cybersecurity strategy

    Morocco Flags AI Threats, Prioritizes Critical Infrastructure Defense

    European Police Chiefs Convention 2026

    Europe’s Police Chiefs Face Growing Threat of AI-Driven Crime

    AI service security

    Hackers Are Stealing AI Keys. The Cost Can Reach $600,000

    AI security risks

    Sam Altman at UN Security Council: 6 AI Security Risks the World Cannot Ignore

    AI-enabled cyber attacks

    AI Gives Hackers an Edge Defenders Still Can’t Match, NCSC Warns

    Fraudulent SIM cards

    India’s DoT Warns Citizens Over SIM Fraud and IMEI Tampering

    EU cybersecurity incidents

    EU Cybersecurity Response Hampered by Critical Information Gaps

    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
    • All
    • How to
    • What is
    Infostealer Intelligence

    The 2026 Infostealer Intelligence Shortlist: Top 10 Vendors Security Teams Should Know

    Google Chrome

    How to Remove Saved Passwords From Google Chrome (And Why You Should)

    DPDP Rules, Cyble, DPDP Act, Cyble Vantage

    How Cyble’s Front-Row Vantage Can Help You in Complying to India’s DPDP Act

    Cybersecurity Countries

    The Top 8 Countries Leading the Cyber Defense Race in 2025

    link building

    The Link Building Secrets Your Competitors Don’t Want You to Know

    Supply Chain Attack

    Supply Chain Resilience and Physical Security: Lessons for 2025

    Healthcare cybersecurity trends of 2024

    Healthcare Cybersecurity: 2024 Was Tough, 2025 May Be Better

    CEO's Guide to Take-Down Services

    Shield Your Organization: CEO’s Perspective on Take-Down Services

    Azure sign-in Microsoft

    Microsoft Announces Mandatory MFA for Azure Sign-ins to Bolster Cloud Defenses

  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • All
    • Appointments
    • Budgets
    • Mergers & Aquisitions
    • Partnerships
    • Press Release
    • Startups
    Kerala Police Signs MoU With Cyble

    Kerala Police Signs MoU With Cyble to Use Threat Intelligence in Cybercrime Probes

    Gemini 4 Argon

    Gemini 4 Argon Restricted Over Cybersecurity Misuse Risks

    weekly roundup September 18 2026

    The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

    threat intelligence

    Cyble, UAE Cyber Security Council Unite Against Rising Cyber Threats

    Ukraine cybersecurity

    Zelensky Appoints Ihor Klymenko to Lead Ukraine’s Cybersecurity Center

    UK cyberattack rate

    UK Small Firms Bear Brunt of Rising Cyberattacks, Hiscox Finds

    Cyber Yodha Campaign

    Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

    UK Ukraine AI partnership

    Britain Gains Access to Ukraine’s ‘Goldmine’ of Battlefield AI Data

    Hims & Hers lawsuit

    FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices

    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
No Result
View All Result
  • MagazineDownload
  • Firewall Daily
    • All
    • Bug Bounty & Rewards
    • Dark Web News
    • Data Breach News
    • Hacker News
    • Ransomware News
    • Vulnerabilities
    WorkOS, AI Agent, Prompt Injection, Grok, Grok AI, Gemini, Fraud, Agentic AI, AI-assisted Cyberattacks

    WorkOS Says a Researcher’s Runaway AI Pentest Agent Copied Customer Sales Records

    Nvidia board investigation

    Why Is Nvidia Investigating Its Own CEO, and Can the Board Remove Him?

    weekly roundup

    The Cyber Express Weekly Roundup: FBI Blames North Korea for $6B Binance Hack, Hackers Turn Up the Heat on Europe’s Fridges and More

    Stockal cyberattack

    Stockal Confirms Unauthorized Trades in 13 Customer Accounts

    Alpine Linux servers

    Alpine Linux SSH Flaw Lets Attackers Log In Without a Password

    Queens Public Library ransomware attack

    Ransomware Just Took New York’s Queens Library Offline, and It’s Not the First

    Amadeus cybersecurity incident

    Airline Data Breach Widens as Singapore Airlines Reports 46,000 Affected Records

    refrigeration cyberattacks

    After Supermarket Freezers, Hackers Turn Up the Heat on France’s Blood Supply

    university supercomputer hacking

    Two Canadians Accused of Turning US University Supercomputers Into Crypto Miners

    Trending Tags

    • blackbyte ransomware
    • Ransomware
    • lapsus$ ransomware
    • Apple
    • Apple vulnerability
  • Essentials
    • All
    • Compliance
    • Governance
    • Policy Updates
    • Regulations
    ASD Essentials

    The Essential Eight Is Being Replaced: What Australian Organisations Need to Know

    SICW 2026

    AI Is Now Fighting on Both Sides of the Cyber War, Singapore Warns

    Morocco cybersecurity strategy

    Morocco Flags AI Threats, Prioritizes Critical Infrastructure Defense

    European Police Chiefs Convention 2026

    Europe’s Police Chiefs Face Growing Threat of AI-Driven Crime

    AI service security

    Hackers Are Stealing AI Keys. The Cost Can Reach $600,000

    AI security risks

    Sam Altman at UN Security Council: 6 AI Security Risks the World Cannot Ignore

    AI-enabled cyber attacks

    AI Gives Hackers an Edge Defenders Still Can’t Match, NCSC Warns

    Fraudulent SIM cards

    India’s DoT Warns Citizens Over SIM Fraud and IMEI Tampering

    EU cybersecurity incidents

    EU Cybersecurity Response Hampered by Critical Information Gaps

    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
    • All
    • How to
    • What is
    Infostealer Intelligence

    The 2026 Infostealer Intelligence Shortlist: Top 10 Vendors Security Teams Should Know

    Google Chrome

    How to Remove Saved Passwords From Google Chrome (And Why You Should)

    DPDP Rules, Cyble, DPDP Act, Cyble Vantage

    How Cyble’s Front-Row Vantage Can Help You in Complying to India’s DPDP Act

    Cybersecurity Countries

    The Top 8 Countries Leading the Cyber Defense Race in 2025

    link building

    The Link Building Secrets Your Competitors Don’t Want You to Know

    Supply Chain Attack

    Supply Chain Resilience and Physical Security: Lessons for 2025

    Healthcare cybersecurity trends of 2024

    Healthcare Cybersecurity: 2024 Was Tough, 2025 May Be Better

    CEO's Guide to Take-Down Services

    Shield Your Organization: CEO’s Perspective on Take-Down Services

    Azure sign-in Microsoft

    Microsoft Announces Mandatory MFA for Azure Sign-ins to Bolster Cloud Defenses

  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • All
    • Appointments
    • Budgets
    • Mergers & Aquisitions
    • Partnerships
    • Press Release
    • Startups
    Kerala Police Signs MoU With Cyble

    Kerala Police Signs MoU With Cyble to Use Threat Intelligence in Cybercrime Probes

    Gemini 4 Argon

    Gemini 4 Argon Restricted Over Cybersecurity Misuse Risks

    weekly roundup September 18 2026

    The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

    threat intelligence

    Cyble, UAE Cyber Security Council Unite Against Rising Cyber Threats

    Ukraine cybersecurity

    Zelensky Appoints Ihor Klymenko to Lead Ukraine’s Cybersecurity Center

    UK cyberattack rate

    UK Small Firms Bear Brunt of Rising Cyberattacks, Hiscox Finds

    Cyber Yodha Campaign

    Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

    UK Ukraine AI partnership

    Britain Gains Access to Ukraine’s ‘Goldmine’ of Battlefield AI Data

    Hims & Hers lawsuit

    FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices

    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
No Result
View All Result
The Cyber Express
No Result
View All Result

Attackers Deploy Dormant Backdoors in Ivanti EPMM to Bypass Patching of Latest 0-Days

Mihir Bagwe by Mihir Bagwe
February 18, 2026
in Vulnerability News, Cyber News, Vulnerabilities
0
Ivanti EPMM, Reconnaissance
585
SHARES
3.2k
VIEWS
Share on LinkedInShare on Twitter

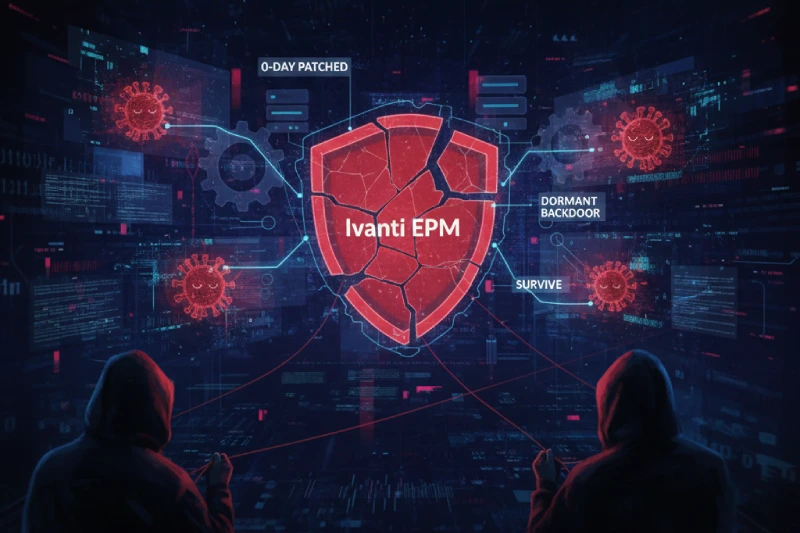
Threat actors weaponized two Ivanti zero-days so quickly that security teams discovered web shells already installed on servers—using arithmetic expansion in bash scripts to slip past authentication entirely.

Researchers at Palo Alto Network’s Unit 42 documented widespread exploitation of two Ivanti EPMM vulnerabilities, tracked as CVE-2026-1281 and CVE-2026-1340, which revealed attackers moving from initial reconnaissance to deploying persistent backdoors designed to survive patching cycles.

The critical vulnerabilities affecting Ivanti Endpoint Manager Mobile allow unauthenticated remote code execution through a deceptively simple bash arithmetic expansion trick that transforms mobile device management infrastructure into attacker-controlled command posts.

Palo Alto Networks’ Cortex Xpanse identified over 4,400 EPMM instances exposed on the public internet, representing massive attack surface across state and local government, healthcare, manufacturing, professional services and high-technology sectors in the United States, Germany, Australia and Canada. CISA added CVE-2026-1281 to its Known Exploited Vulnerabilities catalog, signaling the threat’s severity and requiring federal agencies to patch by February 1.

Also read: Ivanti Patches Two Zero-Days in Mobile Manager After Attackers Exploit Vulnerable Systems

Exploitation Chain and Attack Patterns of Ivanti EPMM Bugs

The exploitation leverages legacy bash scripts Apache uses for URL rewriting in EPMM’s In-House Application Distribution and Android File Transfer features. Both vulnerabilities score 9.8 on the CVSS scale, meaning attackers need no credentials, no user interaction and no complex preconditions—just a malicious HTTP GET request to gain complete server control.

The technical mechanics reveal sophisticated abuse of bash’s arithmetic expansion feature. Attackers send HTTP requests to vulnerable endpoints like /mifs/c/appstore/fob/ with specially crafted parameters. The attack manipulates how bash resolves variables during arithmetic operations by setting one parameter to point to another variable name, then embedding malicious commands inside that second variable as an array index.

When the vulnerable script attempts arithmetic comparison using the first variable, bash automatically resolves it by looking up the second variable. Inside that variable, attackers nest their payload within array index notation. Bash executes the command while resolving the array, achieving code execution through what appears to be simple variable comparison.

Unit 42 observed multiple attack patterns demonstrating both automated scanning and targeted operations. Reconnaissance attempts used simple sleep commands to verify vulnerability—if servers paused exactly five seconds before returning errors, attackers confirmed they achieved remote code execution and immediately followed up with malicious payloads.

Reverse shell attempts established outbound connections to attacker-controlled servers, with captured traffic showing commands like ncat connecting to IP addresses on ports 443 and 8443. These connections give attackers interactive terminal access to compromised systems, enabling manual exploration and privilege escalation.

Web shell installations proved particularly concerning. Attackers deployed lightweight JSP web shells with innocuous names like 401.jsp, 403.jsp and 1.jsp at the filepath /mi/tomcat/webapps/mifs/. If web servers run as root or Administrator—common in EPMM deployments—attackers gain full administrative control. The web shells enable persistent access that survives reboots and provides backup entry points if other access methods get discovered.

Malware download campaigns demonstrated coordination with broader criminal infrastructure. Some attacks attempted to bypass authentication and immediately download second-stage payloads. One campaign involved installing the Nezha monitoring agent, an open-source server monitoring tool, with special parameters that fetched from Gitee if victims were located in China—maximizing victim reach across geographic boundaries.

Botnet activity emerged as attackers integrated compromised EPMM servers into larger criminal networks. The combination of web shells, reverse shells and monitoring agents suggests attackers aim to transform enterprise mobile management platforms into nodes within distributed attack infrastructure rather than pursuing single-target objectives.

The exploitation timeline reveals threat actors’ acceleration capabilities. Organizations that hadn’t patched within days of disclosure found their systems already compromised with dormant backdoors installed. These backdoors remain hidden until attackers need them, potentially surviving patch deployment if organizations fail to hunt for indicators of compromise before remediation.

Fixes Available

Ivanti released RPM scripts providing temporary mitigation for affected versions. Organizations running versions 12.5.0.x, 12.6.0.x and 12.7.0.x should deploy RPM 12.x.0.x, while those on 12.5.1.0 and 12.6.1.0 require RPM 12.x.1.x. Applying patches requires no downtime and causes no functional impact. However, Ivanti warns that upgrading to new versions requires reinstalling the RPM since patches don’t persist across version changes.

The permanent fix arrives with version 12.8.0.0, scheduled for release later in Q1 2026. Organizations suspecting compromise should not attempt cleaning affected systems. Ivanti recommends either restoring EPMM from known-good backups taken before exploitation or rebuilding appliances and migrating data to replacement systems.

Post-restoration, administrators must reset passwords for local EPMM accounts, LDAP and KDC service accounts, revoke and replace public certificates, and reset passwords for all internal and external service accounts configured with EPMM. The comprehensive password reset reflects how deeply attackers can infiltrate once they achieve initial code execution.

Unit 42 provided XQL queries enabling Cortex XDR customers to hunt for exploitation signs. One query parses EPMM logs for HTTP requests matching exploitation URI parameters, extracting version numbers to help security teams identify vulnerable software. A second query analyzes firewall logs for traffic patterns consistent with exploitation attempts.

Organizations with internet-facing management interfaces must adopt assumed breach mentality, treating these vulnerability disclosures as potential compromise requiring immediate forensic investigation alongside patching efforts.
Share this:

  • Share on LinkedIn (Opens in new window) LinkedIn
  • Share on Reddit (Opens in new window) Reddit
  • Share on X (Opens in new window) X
  • Share on Facebook (Opens in new window) Facebook
  • More
  • Email a link to a friend (Opens in new window) Email
  • Share on WhatsApp (Opens in new window) WhatsApp

Related

Tags: Ivanti EPMMReconnaissance
Previous Post

Zero-Day in Dell RecoverPoint Exploited by Chinese Hacker Group

Next Post

OpenAI’s New Enterprise Security Mode Locks Down ChatGPT Against Prompt Injection

Next Post
Lockdown Mode, ChatGPT

OpenAI's New Enterprise Security Mode Locks Down ChatGPT Against Prompt Injection

Q1 2026 Threat Reports

❮ ❯
Cyble-Vision


Follow Us On Google News

Categories

  • Privacy Statement
  • Terms of Use
  • Write For Us

© 2026 The Cyber Express - Cybersecurity News and Magazine.

Welcome Back!

Login to your account below

Forgotten Password?

Retrieve your password

Please enter your username or email address to reset your password.

Log In

Add New Playlist

No Result
View All Result
  • Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board

© 2026 The Cyber Express - Cybersecurity News and Magazine.

-
00:00
00:00

Queue

Update Required Flash plugin
-
00:00
00:00



