
































The wave of attacks that spoiled supermarket food across Europe and reached France’s blood service now has an official explanation from the United States. The FBI says cold chain cyberattacks are succeeding for a simple reason: many temperature controllers are unpatched, reachable from the internet, or still using the default passwords printed in the manufacturer’s manual.
US agencies have released a joint advisory urging organisations to lock down industrial refrigeration and cold chain monitoring systems before the same activity causes damage at home.
What the FBI Says About Cold Chain Cyberattacks
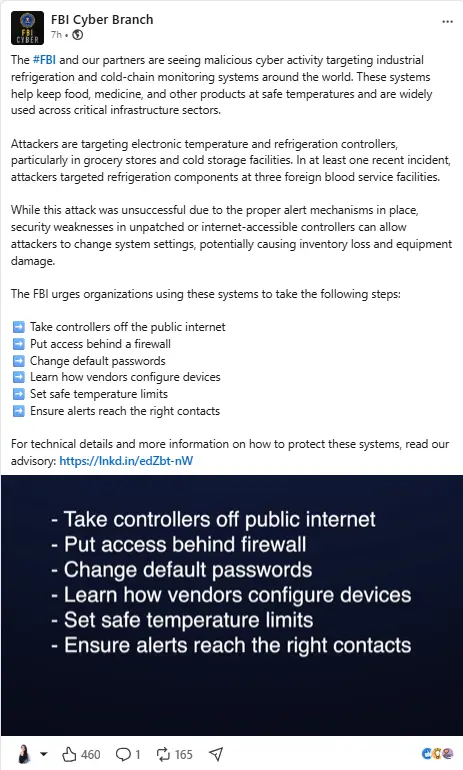
In a video message, Brett Leatherman, Head of FBI Cyber, said the FBI and its partners are seeing malicious cyber activity targeting industrial refrigeration and cold chain systems around the world.
“The FBI and our partners are seeing malicious cyber activity targeting industrial refrigeration and cold chain systems around the world. Earlier, this month in France, attackers went after the refrigeration at three national blood service sites. These systems, though, protect food and medicine across healthcare, food and agriculture, and other critical sectors here in the United States as well,” said Leatherman.
He pointed to France, where attackers went after refrigeration at three national blood service sites earlier this month. “The alarms went to the right people, the staff responded, and in this case no blood was lost,” he said.
Leatherman warned that the same kind of systems protect food and medicine across healthcare, food and agriculture and other critical sectors in the United States.

Attackers are getting in through controllers that are unpatched, reachable from the internet, or still using the default passwords lists in the manufacturer’s manual. The FBI and our partners released an advisory and steps you can take right now,” he informed.
Who Issued the Advisory
The advisory comes from the Cybersecurity and Infrastructure Security Agency (CISA), the FBI, the Department of Health and Human Services, the Department of Agriculture and the Department of Transportation.
The agencies say these systems are widely used across the Healthcare and Public Health, Chemical, Food and Agriculture, and Transportation Systems sectors, including in refrigerated transport. They handle automated and remote temperature monitoring, continuous temperature logging, defrost cycle management and energy optimisation.
How the Attacks Work
According to the advisory, attackers are targeting electronic temperature controllers and commercial refrigeration controllers in retail grocery and cold storage facilities.
They may exploit unpatched or internet-exposed systems to change settings remotely and force units into continuous heating and defrost cycles. The agencies list three main routes in: authentication bypass, arbitrary code injection and weak configurations.
Once inside, attackers can change temperatures. The advisory says this can shorten equipment life, create a fire hazard, cause inventory loss, or indirectly harm consumers if products are eaten after unsafe storage. Attackers can also cause a denial-of-view condition, where operators lose sight of current temperatures.
What Organisations Are Being Told to Do
The agencies urge owners and operators to act immediately. Their recommendations include:
- Remove internet exposure. Do not connect controller panels to the public internet. If remote access is necessary, protect it with an up-to-date firewall or edge device.
- Separate the systems. Place operational technology devices on a dedicated network segment, apart from business networks.
- Fix credentials. Change default passwords, use strong passwords and password policies, and use phishing-resistant multifactor authentication where possible.
- Patch and replace. Keep firmware updated, and retire devices that have reached end of life and no longer get manufacturer support.
- Limit who can make changes. Use allowlists so only approved devices and IP addresses can change settings.
- Keep backups. Store current backups offsite and offline, and test them.
- Watch the logs. Turn on logging and review it for unexpected activity. Where devices don’t produce usable logs, monitor their network traffic instead.
- Set safe limits. Define reasonable temperature setpoint ranges and set alerts for any changes outside them.
The agencies say these steps align with the Cross-Sector Cybersecurity Performance Goals developed by CISA and the National Institute of Standards and Technology.
The blood service incident is the example the FBI chose to highlight, and it shows what made the difference. The attack was not stopped at the controller. It was caught because alarms reached the right people and staff acted quickly. The advisory’s final recommendation, alerting on unsafe temperature changes, reflects that same lesson.





