• About Us
  • Contact Us
  • Editorial Calendar
  • Careers
  • The Cyber Express by Cyble Vulnerability Disclosure Policy
  • Cyble Trust Portal
The Cyber Express
  • MagazineDownload
  • Firewall Daily
    • All
    • Bug Bounty & Rewards
    • Dark Web News
    • Data Breach News
    • Hacker News
    • Ransomware News
    • Vulnerabilities
    ASD Essentials

    The Essential Eight Is Being Replaced: What Australian Organisations Need to Know

    weekly cybersecurity roundup

    The Cyber Express Weekly Roundup: Hackers Turn Supermarket Freezers Into Ovens, UPI PIN Theft and More

    Infostealer Intelligence

    The 2026 Infostealer Intelligence Shortlist: Top 10 Vendors Security Teams Should Know

    GhostBat RAT

    Fake Traffic Challan Texts Are Stealing UPI PINs From Android Users in India

    Microsoft cybercrime crackdown

    Inside the Phishing Marketplace Microsoft Just Took Down: 2,300 Fake Templates Exposed

    Fake X Accounts

    X Removes 13,000 Fake Accounts Ahead of US Midterm Elections

    OLVX marketplace

    OLVX Marketplace Dismantled After Joint FBI-North Macedonia Probe

    French supermarket cyberattack

    Hackers Turned French Supermarket Freezers Into Ovens Overnight

    CVE-2026-89111

    SAP Patches Critical CVSS 10.0 Flaw in Cloud SDK for Python

    Trending Tags

    • blackbyte ransomware
    • Ransomware
    • lapsus$ ransomware
    • Apple
    • Apple vulnerability
  • Essentials
    • All
    • Compliance
    • Governance
    • Policy Updates
    • Regulations
    ASD Essentials

    The Essential Eight Is Being Replaced: What Australian Organisations Need to Know

    SICW 2026

    AI Is Now Fighting on Both Sides of the Cyber War, Singapore Warns

    Morocco cybersecurity strategy

    Morocco Flags AI Threats, Prioritizes Critical Infrastructure Defense

    European Police Chiefs Convention 2026

    Europe’s Police Chiefs Face Growing Threat of AI-Driven Crime

    AI service security

    Hackers Are Stealing AI Keys. The Cost Can Reach $600,000

    AI security risks

    Sam Altman at UN Security Council: 6 AI Security Risks the World Cannot Ignore

    AI-enabled cyber attacks

    AI Gives Hackers an Edge Defenders Still Can’t Match, NCSC Warns

    Fraudulent SIM cards

    India’s DoT Warns Citizens Over SIM Fraud and IMEI Tampering

    EU cybersecurity incidents

    EU Cybersecurity Response Hampered by Critical Information Gaps

    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
    • All
    • How to
    • What is
    Infostealer Intelligence

    The 2026 Infostealer Intelligence Shortlist: Top 10 Vendors Security Teams Should Know

    Google Chrome

    How to Remove Saved Passwords From Google Chrome (And Why You Should)

    DPDP Rules, Cyble, DPDP Act, Cyble Vantage

    How Cyble’s Front-Row Vantage Can Help You in Complying to India’s DPDP Act

    Cybersecurity Countries

    The Top 8 Countries Leading the Cyber Defense Race in 2025

    link building

    The Link Building Secrets Your Competitors Don’t Want You to Know

    Supply Chain Attack

    Supply Chain Resilience and Physical Security: Lessons for 2025

    Healthcare cybersecurity trends of 2024

    Healthcare Cybersecurity: 2024 Was Tough, 2025 May Be Better

    CEO's Guide to Take-Down Services

    Shield Your Organization: CEO’s Perspective on Take-Down Services

    Azure sign-in Microsoft

    Microsoft Announces Mandatory MFA for Azure Sign-ins to Bolster Cloud Defenses

  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • All
    • Appointments
    • Budgets
    • Mergers & Aquisitions
    • Partnerships
    • Press Release
    • Startups
    Kerala Police Signs MoU With Cyble

    Kerala Police Signs MoU With Cyble to Use Threat Intelligence in Cybercrime Probes

    Gemini 4 Argon

    Gemini 4 Argon Restricted Over Cybersecurity Misuse Risks

    weekly roundup September 18 2026

    The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

    threat intelligence

    Cyble, UAE Cyber Security Council Unite Against Rising Cyber Threats

    Ukraine cybersecurity

    Zelensky Appoints Ihor Klymenko to Lead Ukraine’s Cybersecurity Center

    UK cyberattack rate

    UK Small Firms Bear Brunt of Rising Cyberattacks, Hiscox Finds

    Cyber Yodha Campaign

    Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

    UK Ukraine AI partnership

    Britain Gains Access to Ukraine’s ‘Goldmine’ of Battlefield AI Data

    Hims & Hers lawsuit

    FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices

    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
No Result
View All Result
The Cyber Express
No Result
View All Result
Home Features Espionage

Chinese Espionage Operation ‘Volt Typhoon’ Targets US Critical Infrastructure

The group, which has been active since mid-2021, has conducted several cyber attacks targeting critical infrastructure organizations in Guam and networks across the United States

Editorial by Editorial
May 25, 2023
in Espionage, Firewall Daily
0
Volt Typhoon
749
SHARES
4.2k
VIEWS
Share on LinkedInShare on Twitter

Volt Typhoon, a state-sponsored Chinese espionage actor, has managed to infiltrate US infrastructure networks., warned a joint Cybersecurity Advisory (CSA) issued by the United States and its allies. However, China has rejected the claim calling the advisory a “collective disinformation campaign”.

The Chinese espionage group, which has been active since mid-2021, has conducted several cyber attacks targeting critical infrastructure organizations in Guam and networks across the United States, noted a Microsoft security report.

The Volt Typhoon campaign, which is mainly working towards gathering information and espionage, is refining itself to develop capabilities that could gravely impact the communications infrastructure between Asia and the United States.

The joint advisory aims to alert organizations of the activities and techniques used by the state-sponsored Chinese hackers and how the same can be applied worldwide.

The authoring agencies of the joint advisory include the United States NSA, CISA, FBI, Australia’s ACSC, Canada’s CCCS, New Zealand’s NCSC-NZ, and the United Kingdom’s NCSC-UK.

Chinese cyber espionage detected by security researchers

Volt Typhoon, which has been referred as ‘BRONZE SILHOUETTE‘ by Secureworks Counter Threat Unit (CTU) researchers, has been carefully running its operations to blend in with legitimate network activity and stay undetected, noted a report published by the cybersecurity company.
“Think of a spy going undercover, their goal is to blend in and go unnoticed. This is exactly what Bronze Silhouette does by mimicking usual network activity,” said Marc Burnard, Senor Consultant Information Security Research and China thematic lead, Secureworks.

“This suggests a level of operational maturity and adherence to a modus operandi that is engineered to reduce the likelihood of the detection and attribution of the group’s intrusion activity.”

Stating that China is known to be “highly skilled in cyber espionage”, Burnard added.

A series of high-profile U.S Department of Justice indictments of Chinese nationals allegedly involved in cyberespionage activity and the public exposures of this type of activity by security vendors recently were attributed to the Chinese government.

According to Burnard, this might have resulted in increased pressure from leadership within the People’s Republic of China to avoid public scrutiny of its cyberespionage activity.

Activities of Volt Typhoon by the PRC: The LotL way

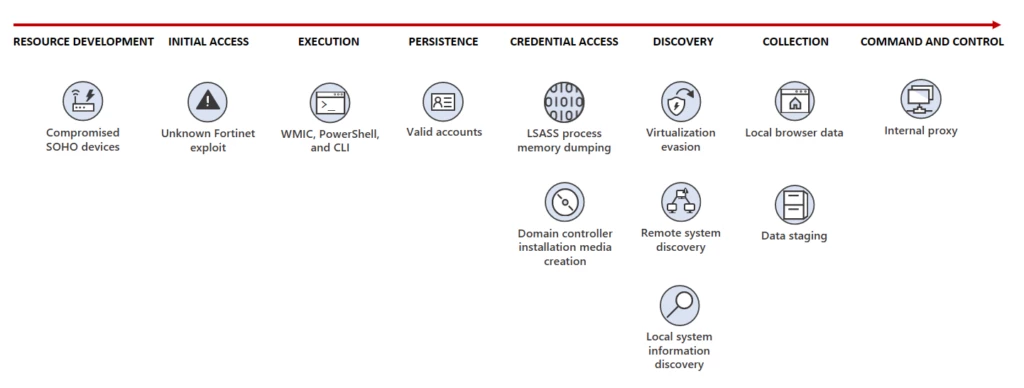
Employing fileless malware or LOLbins, the Volt Typhoon by the PRC followed the living off the land (LotL) technique and procedure to utilize legitimate software from the system to cause cyber attacks.

This allowed Volt Typhoon to effectively evade detection and blend in among users as legitimate for the most part of the attack.
Volt Typhoon
Attack mechanism of Volt Typhoon (Photo: Microsoft)

“The actor has leveraged compromised small office/home office (SOHO) network devices as intermediate infrastructure to obscure their activity by having much of the command and control (C2) traffic emanate from local ISPs in the geographic area of the victim,” the advisory noted.

Tools used by Volt Typhoon

Addressing the technique used by Volt Typhoon, the advisory said, “The actor has used Earthworm and a custom Fast Reverse Proxy (FRP) client with hardcoded C2 callbacks [T1090] to ports 8080, 8443, 8043, 8000, and 10443.” The group used various files names including isco_up.exe, cl64.exe, vm3dservice.exe, watchdogd.exe, Win.exe, WmiPreSV.exe, and WmiPrvSE.exe.

The commands used for malicious activities did not rely on administrative login credentials to find results.

They used a Windows Management Instrumentation Command Line query and gathered storage data on the local host, drive letter, file system, and more.

The command used by the threat actors — c md.exe /C “wmic path win32_logicaldisk get caption,filesystem,freespace,size,volumename”

Zero-Trust model advised

To maintain caution, the advisory about the Volt Typhoon group by the PRC mentioned that small and home office users must pay attention that the network management interfaces being exposed to the internet.

This is to prevent unauthorized access to avoid them being re-purposed as redirectories. Going for the zero-trust principle was also suggested for access management.

Elaborating on the state of compromise of the domain, the advisory wrote, “If an actor can exfiltrate the ntds.dit and SYSTEM registry hive, the entire domain should be considered compromised, as the actor will generally be able to crack the password hashes for domain user accounts, create their own accounts, and/or join unauthorized systems to the domain.”

Users were urged to limit port proxy usage with a time limit so Volt Typhoon and similar groups cannot create backdoors, and bypass the firewall policies.

Volt Typhoon’s whereabouts

Active since mid 2021, Volt Typhoon is based in China and conducts espionage against the targets. “Microsoft assesses with moderate confidence that this Volt Typhoon campaign is pursuing development of capabilities that could disrupt critical communications infrastructure between the United States and Asia region during future crises,” a Microsoft report read.

The targets of the group include however are not limited to critical infrastructure in Guam and other US nations. They have also attacked sectors including government, communications, utility, manufacturing, construction, maritime, and education among others.

Summing up the attack vector of the Volt Typhoon, the Microsoft report stated that the group gains initial access to organizations via internet-facing Fortinet FortiGuard devices. They extract credentials to misuse them further and rarely use malware in their post-compromise activities.

They were often found using the command-line tool Ntdsutil.exe to create installation media from domain controllers to create new domain controllers.

China Denies Involvement, Rejects Spying Accusations

Reacting to the cybersecurity advisory issued by the US and its allies, the Chinese government has rejected the spying accusations, stating that the warning was a “collective disinformation campaign” against the country, The Reuters reported.

Refuting the claims, Mao Ning, the Chinese foreign ministry spokesperson said that the United States was the “empire of hacking” and the intention of the report was to promote the ‘the Five Eyes’ — a global surveillance arrangement between the United States, the United Kingdom, Canada, Australia and New Zealand, the report added.

Response from the team of United States Cyber Defense Agencies

Addressing Chinese threat actors targeting the United States, Jen Easterly, Director of CISA said, “For years, China has conducted aggressive cyber operations to steal intellectual property and sensitive data from organizations around the globe.. Today’s advisory highlights China’s continued use of sophisticated means to target our nation’s critical infrastructure, and it gives network defenders important insights into how to detect and mitigate this malicious activity.”

“We encourage all organizations to review the advisory, take action to mitigate risk, and report any evidence of anomalous activity. We must work together to ensure the security and resilience of our critical infrastructure,” Jen concluded.

Volt Typhoon
Image courtesy: CISA

Another CISA advisory about Chinese infiltration and attacks aimed at the United States and other nations stated that China currently is the most active cyber espionage threat. “China almost certainly is capable of launching cyber attacks that could disrupt critical infrastructure services within the United States, including against oil and gas pipelines, and rail systems,” the advisory read.

Mitigation help offered by Microsoft

Microsoft urged users to immediately change their password and other login credentials to prevent further misuse of their accounts and access. Opting for multi-factor authentication is recommended to defend against Volt Typhoon attacks.

Turning on cloud-delivered protection in Microsoft Defender Antivirus can immensely improve security. Also, running endpoint detection and response (EDR) in block mode was also encouraged so Microsoft Defender can block malicious artifacts even in the inactivity of other anti-virus tools in the system.

Share this:

  • Share on LinkedIn (Opens in new window) LinkedIn
  • Share on Reddit (Opens in new window) Reddit
  • Share on X (Opens in new window) X
  • Share on Facebook (Opens in new window) Facebook
  • More
  • Email a link to a friend (Opens in new window) Email
  • Share on WhatsApp (Opens in new window) WhatsApp

Related

Tags: Chinese espionagemalware free espionagePRC cybercriminalsThe Cyber ExpressThe Cyber Express NewsVolt Typhoon
Previous Post

Cyber Attack on UAE Banking Sector: Mysterious Team Bangladesh Claims to Hit First Abu Dhabi Bank

Next Post

Iranian Cybercriminals Targeting UAE Government Websites Traced with Backdoor Data

Next Post
Iranian Cybercriminals Targeting UAE Government

Iranian Cybercriminals Targeting UAE Government Websites Traced with Backdoor Data

Q1 2026 Threat Reports

❮ ❯
Cyble-Vision


Follow Us On Google News

Latest Cyber News

ASD Essentials
Cyber Essentials

The Essential Eight Is Being Replaced: What Australian Organisations Need to Know

October 16, 2026
weekly cybersecurity roundup
Cyber News

The Cyber Express Weekly Roundup: Hackers Turn Supermarket Freezers Into Ovens, UPI PIN Theft and More

October 16, 2026
Infostealer Intelligence
Firewall Daily

The 2026 Infostealer Intelligence Shortlist: Top 10 Vendors Security Teams Should Know

October 15, 2026
GhostBat RAT
Cyber News

Fake Traffic Challan Texts Are Stealing UPI PINs From Android Users in India

October 15, 2026

Categories

Web Stories

Do This on Telegram, Your Bank Account Will Become Zero
If You Install the iOS 18 Beta, Your iPhone Could Be Hacked
Cricket World Cup Ticketing Systems Under Cybersecurity
Cyber Threats and Online Ticket Scams During the NBA Finals
Biometric Data Security: Protecting Sensitive Information

About

The Cyber Express

#1 Trending Cybersecurity News and Magazine

The Cyber Express is a handbook for all stakeholders of the internet that provides information security professionals with the latest news, updates and knowledge they need to combat cyber threats.


Contact

For editorial queries: [email protected]

For marketing and Sales: [email protected]


Quick Links

  • About Us
  • Contact Us
  • Editorial Calendar
  • Careers
  • The Cyber Express by Cyble Vulnerability Disclosure Policy
  • Cyble Trust Portal

Our Address

We’re remote friendly, with office locations around the world:

San Francisco, Atlanta, Rome,
Dubai, Mumbai, Bangalore, Hyderabad,  Singapore, Jakarta, Sydney, and Melbourne


Headquarters:

The Cyber Express LLC
10080 North Wolfe Road, Suite SW3-200, Cupertino, CA, US 95014


India Office:

Cyber Express Media Network
HD-021, 4th Floor, C Wing, Building No.4. Nesco IT Park, WE Highway, Goregaon East, Mumbai, Maharashtra, India – 4000063

  • Privacy Statement
  • Terms of Use
  • Write For Us

© 2026 The Cyber Express - Cybersecurity News and Magazine.

Welcome Back!

Login to your account below

Forgotten Password?

Retrieve your password

Please enter your username or email address to reset your password.

Log In

Add New Playlist

No Result
View All Result
  • Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board

© 2026 The Cyber Express - Cybersecurity News and Magazine.

Are you sure want to unlock this post?
Unlock left : 0
Are you sure want to cancel subscription?
-
00:00
00:00

Queue

Update Required Flash plugin
-
00:00
00:00
Do This on Telegram, Your Bank Account Will Become Zero If You Install the iOS 18 Beta, Your iPhone Could Be Hacked Cricket World Cup Ticketing Systems Under Cybersecurity Cyber Threats and Online Ticket Scams During the NBA Finals Biometric Data Security: Protecting Sensitive Information