
















• Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
The Cyber Express
  • MagazineDownload
  • Firewall Daily
    • All
    • Bug Bounty & Rewards
    • Dark Web News
    • Data Breach News
    • Hacker News
    • Ransomware News
    • Vulnerabilities
    weekly roundup October 30

    The Cyber Express Weekly Roundup: Binance Hit by $6.3 Billion Security Incident, South Korea Busts AI-Powered Hacking Ring and More

    Binance Data Breach

    Binance Security Incident Affects $6.3 Billion in Crypto Assets, $3 Billion Frozen

    Cyberattacks on Japan

    Three Cyberattack Campaigns Target Japan, Exposing AI’s Growing Role

    Ukrainian ransomware affiliate

    Ransomware Attacks on Hospitals and Businesses Lead to 70-Month Sentence

    FBI seizes Virtualine

    FBI Seizes Bulletproof Hosting Domain Linked to Cybercrime

    ASD Cyber Threat Report

    Australian Data Breach Incidents Up 66% as AI Sharpens Scams

    INJ3CTOR3

    INJ3CTOR3 Malware Steals FreePBX Credentials, Enabling Toll Fraud After Cleanup

    Discoverable Servers

    Discord to Let Google Index Public Server Messages, Raising Privacy Concerns

    Columbia University cyberattack

    Columbia University Settles $16.1M Data Breach Lawsuit After 2025 Cyberattack

    Trending Tags

    • blackbyte ransomware
    • Ransomware
    • lapsus$ ransomware
    • Apple
    • Apple vulnerability
  • Essentials
    • All
    • Compliance
    • Governance
    • Policy Updates
    • Regulations
    ASD Essentials

    The Essential Eight Is Being Replaced: What Australian Organisations Need to Know

    SICW 2026

    AI Is Now Fighting on Both Sides of the Cyber War, Singapore Warns

    Morocco cybersecurity strategy

    Morocco Flags AI Threats, Prioritizes Critical Infrastructure Defense

    European Police Chiefs Convention 2026

    Europe’s Police Chiefs Face Growing Threat of AI-Driven Crime

    AI service security

    Hackers Are Stealing AI Keys. The Cost Can Reach $600,000

    AI security risks

    Sam Altman at UN Security Council: 6 AI Security Risks the World Cannot Ignore

    AI-enabled cyber attacks

    AI Gives Hackers an Edge Defenders Still Can’t Match, NCSC Warns

    Fraudulent SIM cards

    India’s DoT Warns Citizens Over SIM Fraud and IMEI Tampering

    EU cybersecurity incidents

    EU Cybersecurity Response Hampered by Critical Information Gaps

    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
    • All
    • How to
    • What is
    Infostealer Intelligence

    The 2026 Infostealer Intelligence Shortlist: Top 10 Vendors Security Teams Should Know

    Google Chrome

    How to Remove Saved Passwords From Google Chrome (And Why You Should)

    DPDP Rules, Cyble, DPDP Act, Cyble Vantage

    How Cyble’s Front-Row Vantage Can Help You in Complying to India’s DPDP Act

    Cybersecurity Countries

    The Top 8 Countries Leading the Cyber Defense Race in 2025

    link building

    The Link Building Secrets Your Competitors Don’t Want You to Know

    Supply Chain Attack

    Supply Chain Resilience and Physical Security: Lessons for 2025

    Healthcare cybersecurity trends of 2024

    Healthcare Cybersecurity: 2024 Was Tough, 2025 May Be Better

    CEO's Guide to Take-Down Services

    Shield Your Organization: CEO’s Perspective on Take-Down Services

    Azure sign-in Microsoft

    Microsoft Announces Mandatory MFA for Azure Sign-ins to Bolster Cloud Defenses

  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • All
    • Appointments
    • Budgets
    • Mergers & Aquisitions
    • Partnerships
    • Press Release
    • Startups
    Kerala Police Signs MoU With Cyble

    Kerala Police Signs MoU With Cyble to Use Threat Intelligence in Cybercrime Probes

    Gemini 4 Argon

    Gemini 4 Argon Restricted Over Cybersecurity Misuse Risks

    weekly roundup September 18 2026

    The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

    threat intelligence

    Cyble, UAE Cyber Security Council Unite Against Rising Cyber Threats

    Ukraine cybersecurity

    Zelensky Appoints Ihor Klymenko to Lead Ukraine’s Cybersecurity Center

    UK cyberattack rate

    UK Small Firms Bear Brunt of Rising Cyberattacks, Hiscox Finds

    Cyber Yodha Campaign

    Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

    UK Ukraine AI partnership

    Britain Gains Access to Ukraine’s ‘Goldmine’ of Battlefield AI Data

    Hims & Hers lawsuit

    FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices

    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
No Result
View All Result
The Cyber Express
No Result
View All Result

Fake App Mimicking Shagle Targets Android Users

The open-source Telegram app is used to create the fake app mimicking Shagle which has the StrongPity backdoor code.

thecyberexpress by thecyberexpress
January 12, 2023
in Data Breach News, Firewall Daily
0
Shagle
585
SHARES
3.2k
VIEWS
Share on LinkedInShare on Twitter

ESET researchers have found an espionage campaign that targets Android users looking for an app for Shagle, a video chat platform. The trojanized fake app mimicking shagle is made using the Android version of the Telegram app.

While the original Shagle website does not offer an app for video chats, the fake website for Shagle made by the StrongPity espionage gang offers one that is available for Android-run devices. However, the app is not distributed on Google Play Store.

The StrongPity espionage campaign distributing the fake app mimicking Shagle

The open-source Telegram app is used to create the fake app mimicking Shagle which has the StrongPity backdoor code.

Researchers also found that the version of malware on the Shagle application was not active at a certain time however, it can be updated should StrongPity change its plans to relaunch the campaign.

The research read that the app could not be installed at the time of research, nor could its backdoor functionality be triggered.

They did not find any victims of this app either leading to speculations of it being a highly targeted campaign for specific individuals or entities. It was last available around February 25, 2022.

The following are the capabilities of the fake app mimicking Shagle. It can:

  • Record calls
  • Collect SMSes
  • Access call logs
  • Copy contact lists
  • Request to activate accessibility services
  • Granting permissions silently if the device is rooted

It would silently grant permissions to WRITE_SETTINGS, MODIFY_PHONE_STATE, and READ_PRIVILEGED_PHONE_STATE among others if the device is rooted.

If extended permissions are granted to the fake app mimicking Shagle it can also access notifications and exfiltrate messages from 17 other apps on the device. They are:

  1. Messenger
  2. Gmail
  3. Twitter
  4. Tinder
  5. Viber
  6. Skype
  7. Messenger Lite
  8. LINE: Calls & Messages
  9. Kik – Messaging & Chat App
  10. tango-live steam & video chat
  11. Hangouts
  12. Telegram
  13. WeChat
  14. Snapchat
  15. Hike News & Content
  16. imo-International Calls & Chat
  17. Instagram

Technical details of the fake app mimicking Shagle

Malicious activities first trigged upon the execution of defined actions including BOOT_COMPLETED, BATTERY_LOW, or USER_PRESENT.

It used interprocess communication (IPC) for interacting between its own components and launching its commands. It would then send system data to the C&C server using HTTPS.

The received AES-encrypted file with 11 binary modules would get saved in the app’s internal storage at /data/user/0/org.telegram.messenger/files/.li/.

The modules would get saved in the sharedconfig.xml file which would get dynamically triggered by the parent app.

The module libarm.jar (cm module) was responsible for recording phone calls while services.jar (lo module) was used for fetching the device location.

The copied device data would get stored in the /data/user/0/org.telegram.messenger/databases/outdata database and then would be encrypted and sent to the C&C server as shown in the figure below:
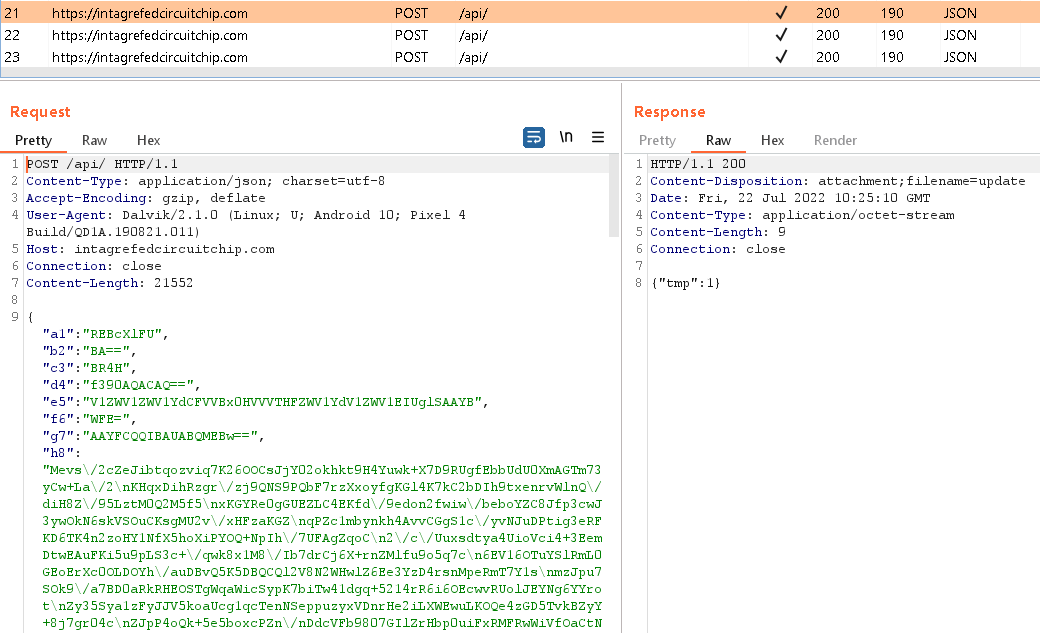
https://www.welivesecurity.com/wp-content/uploads/2023/01/Figure-13.-Encrypted-user-data-exfiltrated-to-the-CC-server.png

(Source: welivesecurity)

The domain name used by this campaign had the word ‘dutch’. The HTML code found on the fake Shagle website was copied from the original shagle.com website on November 1, 2021.

The domain was also registered on the same day. The code was taken using the automated tool HTTrack.

Telegram app’s AndroidManifest.xml was used for the components and permissions needed by the Shagle apps backdoor code.

Moreover, org.telegram.messenger package was used to insert malicious classes to make the fake Shagle app appear legitimate.

Figure 2. Logs generated by the HTTrack tool recorded in the fake website%E2%80%99s HTML code 2
HTML code for the fake Shagle website (Source: welivesecurity)


The fake app mimicking Shagle uses Telegram version 7.5.0 (22467). And while package names for Android apps must be unique IDs, this trojanized android app used the same as the official Telegram app.

This also gives away that those users using the original Telegram app cannot install the malicious Shagle app.

Researchers argue that this may be a maneuver to narrow down targets based on those using the Telegram app. They may even coax users to uninstall Telegram or StrongPity was focused on launching this malicious campaign in countries with fewer Telegram users.

Telegram’s error documentation clarified that StrongPity developers did not get their own API ID for initial testing and copied the sample API ID from Telegram’s open-source code.

Since Telegram does not allow the use of a sample API Id outside a limit, researchers got an error message during signing up using a phone number.

No new working version of the fake Shagle app was also found during research. This suggests that the campaign may have become defunct. It also suggests that their designated target may have been victimized at an early stage.

Similarity between this campaign to the previous Android campaign

Researchers found that this app uses a certificate signature that matches the one used in a previous campaign by the group.

The previous campaign discovered in 2021 was the only other malicious Android campaign attributed to the StrongPity espionage group. It was about a malicious Syrian e-gov app.

Figure 3. This certificate signed the fake Shagle app and the trojanized Syrian e gov app
The similar certificate signature for Shagle and the Syrian app (Source: welivesecurity)

Upon comparing the backdoor code between both campaigns using SHA-1: 5A5910C2C9180382FCF7A939E9909044F0E8918B, it was found that the new campaign offers some added functionalities with the same code and similar functions as offered in the prior app.


Share this:

  • Share on LinkedIn (Opens in new window) LinkedIn
  • Share on Reddit (Opens in new window) Reddit
  • Share on X (Opens in new window) X
  • Share on Facebook (Opens in new window) Facebook
  • More
  • Email a link to a friend (Opens in new window) Email
  • Share on WhatsApp (Opens in new window) WhatsApp

Related

Tags: cyber express newsfake app mimicking shagleshagle spying appStrongPity espionage campaignstrongpity targets androidThe Cyber Express
Previous Post

Flights in US Grounded For Hours After Computer Outage

Next Post

‘Attack for Freedom’: Brazil Government Website Data Leaked on Hacker Forum

Next Post
Brazil Government Website Data Leak

'Attack for Freedom': Brazil Government Website Data Leaked on Hacker Forum

Cyble-Vision


Follow Us On Google News

Categories

Q1 2026 Threat Reports

❮ ❯
  • Privacy Statement
  • Terms of Use
  • Write For Us

© 2026 The Cyber Express - Cybersecurity News and Magazine.

Welcome Back!

Login to your account below

Forgotten Password?

Retrieve your password

Please enter your username or email address to reset your password.

Log In

Add New Playlist

No Result
View All Result
  • Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board

© 2026 The Cyber Express - Cybersecurity News and Magazine.

-
00:00
00:00

Queue

Update Required Flash plugin
-
00:00
00:00


