
















• Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
The Cyber Express
  • MagazineDownload
  • Firewall Daily
    • All
    • Bug Bounty & Rewards
    • Dark Web News
    • Data Breach News
    • Hacker News
    • Ransomware News
    • Vulnerabilities
    weekly roundup October 30

    The Cyber Express Weekly Roundup: Binance Hit by $6.3 Billion Security Incident, South Korea Busts AI-Powered Hacking Ring and More

    Binance Data Breach

    Binance Security Incident Affects $6.3 Billion in Crypto Assets, $3 Billion Frozen

    Cyberattacks on Japan

    Three Cyberattack Campaigns Target Japan, Exposing AI’s Growing Role

    Ukrainian ransomware affiliate

    Ransomware Attacks on Hospitals and Businesses Lead to 70-Month Sentence

    FBI seizes Virtualine

    FBI Seizes Bulletproof Hosting Domain Linked to Cybercrime

    ASD Cyber Threat Report

    Australian Data Breach Incidents Up 66% as AI Sharpens Scams

    INJ3CTOR3

    INJ3CTOR3 Malware Steals FreePBX Credentials, Enabling Toll Fraud After Cleanup

    Discoverable Servers

    Discord to Let Google Index Public Server Messages, Raising Privacy Concerns

    Columbia University cyberattack

    Columbia University Settles $16.1M Data Breach Lawsuit After 2025 Cyberattack

    Trending Tags

    • blackbyte ransomware
    • Ransomware
    • lapsus$ ransomware
    • Apple
    • Apple vulnerability
  • Essentials
    • All
    • Compliance
    • Governance
    • Policy Updates
    • Regulations
    ASD Essentials

    The Essential Eight Is Being Replaced: What Australian Organisations Need to Know

    SICW 2026

    AI Is Now Fighting on Both Sides of the Cyber War, Singapore Warns

    Morocco cybersecurity strategy

    Morocco Flags AI Threats, Prioritizes Critical Infrastructure Defense

    European Police Chiefs Convention 2026

    Europe’s Police Chiefs Face Growing Threat of AI-Driven Crime

    AI service security

    Hackers Are Stealing AI Keys. The Cost Can Reach $600,000

    AI security risks

    Sam Altman at UN Security Council: 6 AI Security Risks the World Cannot Ignore

    AI-enabled cyber attacks

    AI Gives Hackers an Edge Defenders Still Can’t Match, NCSC Warns

    Fraudulent SIM cards

    India’s DoT Warns Citizens Over SIM Fraud and IMEI Tampering

    EU cybersecurity incidents

    EU Cybersecurity Response Hampered by Critical Information Gaps

    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
    • All
    • How to
    • What is
    Infostealer Intelligence

    The 2026 Infostealer Intelligence Shortlist: Top 10 Vendors Security Teams Should Know

    Google Chrome

    How to Remove Saved Passwords From Google Chrome (And Why You Should)

    DPDP Rules, Cyble, DPDP Act, Cyble Vantage

    How Cyble’s Front-Row Vantage Can Help You in Complying to India’s DPDP Act

    Cybersecurity Countries

    The Top 8 Countries Leading the Cyber Defense Race in 2025

    link building

    The Link Building Secrets Your Competitors Don’t Want You to Know

    Supply Chain Attack

    Supply Chain Resilience and Physical Security: Lessons for 2025

    Healthcare cybersecurity trends of 2024

    Healthcare Cybersecurity: 2024 Was Tough, 2025 May Be Better

    CEO's Guide to Take-Down Services

    Shield Your Organization: CEO’s Perspective on Take-Down Services

    Azure sign-in Microsoft

    Microsoft Announces Mandatory MFA for Azure Sign-ins to Bolster Cloud Defenses

  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • All
    • Appointments
    • Budgets
    • Mergers & Aquisitions
    • Partnerships
    • Press Release
    • Startups
    Kerala Police Signs MoU With Cyble

    Kerala Police Signs MoU With Cyble to Use Threat Intelligence in Cybercrime Probes

    Gemini 4 Argon

    Gemini 4 Argon Restricted Over Cybersecurity Misuse Risks

    weekly roundup September 18 2026

    The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

    threat intelligence

    Cyble, UAE Cyber Security Council Unite Against Rising Cyber Threats

    Ukraine cybersecurity

    Zelensky Appoints Ihor Klymenko to Lead Ukraine’s Cybersecurity Center

    UK cyberattack rate

    UK Small Firms Bear Brunt of Rising Cyberattacks, Hiscox Finds

    Cyber Yodha Campaign

    Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

    UK Ukraine AI partnership

    Britain Gains Access to Ukraine’s ‘Goldmine’ of Battlefield AI Data

    Hims & Hers lawsuit

    FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices

    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
No Result
View All Result
The Cyber Express
No Result
View All Result

Wagner Group Attacks Russia with Ransomware; Researchers Divided on Origins

According to researchers, this variant of Chaos ransomware dropped a ransom note that urged the victims to join Russian mercenary group PMC Wagner

Ashish Khaitan by Ashish Khaitan
July 4, 2023
in Dark Web News, Firewall Daily
0
MicrosoftTeams image 92
585
SHARES
3.2k
VIEWS
Share on LinkedInShare on Twitter

In a strange twist of events, Wagner Group has claimed to attack Russia in a new ransomware campaign. Using what has been dubbed a new strain of ransomware, the Wagner Group has attacked Russia in what appears to be an attempt to recruit more people to the Russian mercenary group.

According to researchers, this variant of Chaos ransomware dropped a ransom note that urged the victims to join PMC Wagner, the Russian mercenary group currently at loggerheads with the country’s administration.

However, threat researcher Brett Callow suspects whether this “Wagner ransomware” has actually been deployed in Russia or anywhere else. 

Wagner Group, officially known as PMC Wagner, is a Russian state-sponsored group of mercenaries operating beyond Russia’s laws. 

Wagner Group attacks Russia: Insights provided by Cyble

During their investigation, researchers at Cyble discovered that the Wagner Group, a notorious paramilitary organization, has not claimed responsibility for the recent ransomware attacks in Russia.

This has led to speculation about the actual perpetrators and their motives for targeting Russian computers.

Cyble’s Research and Intelligence Labs (CRIL) stated in a blog post that the ransomware used in the attacks is a variant of Chaos ransomware.

This ransomware is a variant of Chaos ransomware. During our analysis, we found that the ransom note dropped by this ransomware, instead of demanding money, urges users to join the PMC Wagner,” said the blog post.

“The ransom note includes a call to wage war against Shoigu. Sergei Kuzhugetovich Shoigu is a prominent Russian politician and military officer, serving as the Minister of Defence of Russia since 2012.”

The content of the ransom note aligns with the information found in the bio section of the WAGNER GROUP Telegram channel, as shown below.
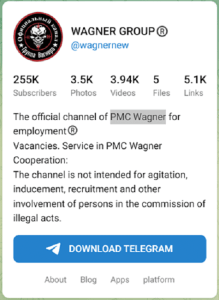
Wagner group

Furthermore, the ransomware sample analyzed by CRIL was submitted to VirusTotal from Russia, and the ransom note itself was written in Russian. These findings indicate that the primary targets of this ransomware campaign are Russian netizens.

CRIL has reported on this malware strain, which is based on a variant of Chaos ransomware. Their comprehensive report highlights the Wagner Group’s attack on Russia as a means to promote PMC Wagner.

Additionally, Cyble has uncovered that the ransom note includes a phone number for Wagner’s recruitment offices in Moscow, accompanied by the statement, “If you want to go against the officials!”

However, Brett Callow, Threat Intelligence Analyst at Emisoft, suspected that it’s a bogus campaign.

“AFAIK, there is no evidence that #Wagner #ransomware has actually been deployed in Russia or, for that matter, anywhere else. All we have is a sample that somebody – perhaps the same person who created it – uploaded to VT, possibly just for lulz,” he tweeted.

Wagner Group Attacks Russia: Unveiling the Malware Involved

The alleged attacks carried out by the Wagner Group in Russia through a new ransomware campaign have raised significant concerns regarding their implications and consequences.

Not only do these attacks compromise the security and integrity of computer systems in Russia, but they also serve as a disturbing recruitment tool for the controversial paramilitary organization.

The threat actor behind the attacks employs a new strain of ransomware that not only encrypts victims’ files but also coerces them into joining the Wagner Group, following the paramilitary group’s recent rebellion against the Kremlin.

According to research by PC Risk, the Wagner malware encrypts files and demands a ransom, appending a “.WAGNER” extension to each locked file. The ransom note emphasizes the Wagner Group’s rebellion against the Russian government.

Upon execution, the ransomware initiates various variables to control its behavior. One crucial task involves checking for existing instances of the ransomware by comparing the list of currently running processes and their names. If a match is found, the ransomware terminates to avoid simultaneous execution of multiple instances.

Next, the ransomware verifies the “checkSleep” variable. If set to true, the ransomware confirms whether it runs from a specific folder (%APPDATA%). If not, it enters a sleep mode for a specified period, determined by the attacker.

Subsequently, the ransomware attempts to achieve persistence and escalate privileges based on specific flag variables defined by the attacker. If the “checkAdminPrivilage” flag is true, the ransomware seeks persistence and elevated privileges by creating a copy of itself named “svchost.exe” in the system’s startup folder.

It then terminates the current instance and recursively executes the copied file with elevated privileges.

In cases where the value of “checkAdminPrivilage” is false, the ransomware checks the status of the “checkCopyRoaming” variable. If true, the ransomware solely adds its binary to the startup folder for persistence.

Furthermore, the ransomware incorporates an additional persistence mechanism depending on the value of the “checkStartupFolder” variable. When set to true, the ransomware creates a shortcut file in the startup folder, pointing to its location. As a result, the ransomware is automatically executed upon system startup

Media Disclaimer: This report is based on internal and external research obtained through various means. The information provided is for reference purposes only, and users bear full responsibility for their reliance on it. The Cyber Express assumes no liability for the accuracy or consequences of using this information.


Share this:

  • Share on LinkedIn (Opens in new window) LinkedIn
  • Share on Reddit (Opens in new window) Reddit
  • Share on X (Opens in new window) X
  • Share on Facebook (Opens in new window) Facebook
  • More
  • Email a link to a friend (Opens in new window) Email
  • Share on WhatsApp (Opens in new window) WhatsApp

Related

Tags: The Cyber ExpressThe Cyber Express NewsWagner Group Attacks Russia
Previous Post

Cyberwarfare Fears Rise as Pro-Russian ‘UserSec’ Gains Support From 8 Hacking Group

Next Post

Rebooting Everyday, And More: Seven Tips to Keep Your Smartphones Safe From Cyber Attacks

Next Post
Keep Your Smartphones Safe From Cyber Attacks

Rebooting Everyday, And More: Seven Tips to Keep Your Smartphones Safe From Cyber Attacks

Cyble-Vision


Follow Us On Google News

Categories

Q1 2026 Threat Reports

❮ ❯
  • Privacy Statement
  • Terms of Use
  • Write For Us

© 2026 The Cyber Express - Cybersecurity News and Magazine.

Welcome Back!

Login to your account below

Forgotten Password?

Retrieve your password

Please enter your username or email address to reset your password.

Log In

Add New Playlist

No Result
View All Result
  • Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board

© 2026 The Cyber Express - Cybersecurity News and Magazine.

-
00:00
00:00

Queue

Update Required Flash plugin
-
00:00
00:00


