
















• Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
The Cyber Express
  • MagazineDownload
  • Firewall Daily
    • All
    • Bug Bounty & Rewards
    • Dark Web News
    • Data Breach News
    • Hacker News
    • Ransomware News
    • Vulnerabilities
    weekly roundup October 30

    The Cyber Express Weekly Roundup: Binance Hit by $6.3 Billion Security Incident, South Korea Busts AI-Powered Hacking Ring and More

    Binance Data Breach

    Binance Security Incident Affects $6.3 Billion in Crypto Assets, $3 Billion Frozen

    Cyberattacks on Japan

    Three Cyberattack Campaigns Target Japan, Exposing AI’s Growing Role

    Ukrainian ransomware affiliate

    Ransomware Attacks on Hospitals and Businesses Lead to 70-Month Sentence

    FBI seizes Virtualine

    FBI Seizes Bulletproof Hosting Domain Linked to Cybercrime

    ASD Cyber Threat Report

    Australian Data Breach Incidents Up 66% as AI Sharpens Scams

    INJ3CTOR3

    INJ3CTOR3 Malware Steals FreePBX Credentials, Enabling Toll Fraud After Cleanup

    Discoverable Servers

    Discord to Let Google Index Public Server Messages, Raising Privacy Concerns

    Columbia University cyberattack

    Columbia University Settles $16.1M Data Breach Lawsuit After 2025 Cyberattack

    Trending Tags

    • blackbyte ransomware
    • Ransomware
    • lapsus$ ransomware
    • Apple
    • Apple vulnerability
  • Essentials
    • All
    • Compliance
    • Governance
    • Policy Updates
    • Regulations
    ASD Essentials

    The Essential Eight Is Being Replaced: What Australian Organisations Need to Know

    SICW 2026

    AI Is Now Fighting on Both Sides of the Cyber War, Singapore Warns

    Morocco cybersecurity strategy

    Morocco Flags AI Threats, Prioritizes Critical Infrastructure Defense

    European Police Chiefs Convention 2026

    Europe’s Police Chiefs Face Growing Threat of AI-Driven Crime

    AI service security

    Hackers Are Stealing AI Keys. The Cost Can Reach $600,000

    AI security risks

    Sam Altman at UN Security Council: 6 AI Security Risks the World Cannot Ignore

    AI-enabled cyber attacks

    AI Gives Hackers an Edge Defenders Still Can’t Match, NCSC Warns

    Fraudulent SIM cards

    India’s DoT Warns Citizens Over SIM Fraud and IMEI Tampering

    EU cybersecurity incidents

    EU Cybersecurity Response Hampered by Critical Information Gaps

    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
    • All
    • How to
    • What is
    Infostealer Intelligence

    The 2026 Infostealer Intelligence Shortlist: Top 10 Vendors Security Teams Should Know

    Google Chrome

    How to Remove Saved Passwords From Google Chrome (And Why You Should)

    DPDP Rules, Cyble, DPDP Act, Cyble Vantage

    How Cyble’s Front-Row Vantage Can Help You in Complying to India’s DPDP Act

    Cybersecurity Countries

    The Top 8 Countries Leading the Cyber Defense Race in 2025

    link building

    The Link Building Secrets Your Competitors Don’t Want You to Know

    Supply Chain Attack

    Supply Chain Resilience and Physical Security: Lessons for 2025

    Healthcare cybersecurity trends of 2024

    Healthcare Cybersecurity: 2024 Was Tough, 2025 May Be Better

    CEO's Guide to Take-Down Services

    Shield Your Organization: CEO’s Perspective on Take-Down Services

    Azure sign-in Microsoft

    Microsoft Announces Mandatory MFA for Azure Sign-ins to Bolster Cloud Defenses

  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • All
    • Appointments
    • Budgets
    • Mergers & Aquisitions
    • Partnerships
    • Press Release
    • Startups
    Kerala Police Signs MoU With Cyble

    Kerala Police Signs MoU With Cyble to Use Threat Intelligence in Cybercrime Probes

    Gemini 4 Argon

    Gemini 4 Argon Restricted Over Cybersecurity Misuse Risks

    weekly roundup September 18 2026

    The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

    threat intelligence

    Cyble, UAE Cyber Security Council Unite Against Rising Cyber Threats

    Ukraine cybersecurity

    Zelensky Appoints Ihor Klymenko to Lead Ukraine’s Cybersecurity Center

    UK cyberattack rate

    UK Small Firms Bear Brunt of Rising Cyberattacks, Hiscox Finds

    Cyber Yodha Campaign

    Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

    UK Ukraine AI partnership

    Britain Gains Access to Ukraine’s ‘Goldmine’ of Battlefield AI Data

    Hims & Hers lawsuit

    FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices

    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
No Result
View All Result
The Cyber Express
No Result
View All Result

SharpPanda APT Targets High-Level Government Officials From G20 Nations

The G20, established in 1999, is a prominent international forum comprising 19 countries and the European Union

Editorial by Editorial
June 2, 2023
in Firewall Daily
0
G20 Nations e1685709447488
585
SHARES
3.2k
VIEWS
Share on LinkedInShare on Twitter

Cybersecurity researchers at Cyble Research and Intelligence Labs (CRIL) have recently uncovered an ongoing campaign by the sophisticated hacking group known as SharpPanda APT.

This group, previously observed targeting government officials in Southeast Asian countries, has now shifted its focus to high-level government officials from G20 nations.

“Previously, this APT group has been observed targeting government officials, particularly in Southeast Asian countries,” said the CRIL report.

“This latest campaign specifically targets high-level government officials from G20 nations.”

The G20, established in 1999, is a prominent international forum comprising 19 countries and the European Union.

This shift in focus raises concerns about the group’s evolving tactics and the potential implications for global security and economic cooperation.

The origins of SharpPanda APT

SharpPanda APT has established a reputation for executing extended and sophisticated cyber attacks against specific geopolitical targets.

It employs strategies such as spear-phishing, social engineering manipulation, and exploiting zero-day vulnerabilities. Governments, organizations, and industries have all fallen victim to their intrusive activities.

The G20, comprised of 19 countries and the European Union, was established in 1999 as an international forum to foster global economic cooperation and address key challenges impacting the worldwide economy.

With member countries representing a diverse range of economies and collectively accounting for a significant share of global GDP and population, the G20 holds annual summits where leaders convene to discuss and coordinate security, economic, and financial policies.

SharpPanda APT campaign and G20 officials

“In its latest campaign, the SharpPanda APT group employs a forged document linked to G7 to target various governments within the G20 forum,” said the CRIL report.

The campaign’s infection chain starts with a spam email containing an attached MS Office document named “[FINAL] Hiroshima Action Statement for Resilient Global Food Security_trackchanged.docx.”

This deceptive email, with the subject line “[Sending Finalized Text] G7+Partners FASS Meeting,” is distributed to multiple government employees across G20 countries.

The attached document, seemingly genuine, uses remote template injection to retrieve the next stage of the malware from the attackers’ Command-and-Control (C&C) server.
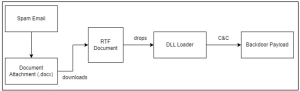
SharpPanda APT
Infection chain. Image: CRIL

The weaponized RTF file within the spam email exploits vulnerabilities in Microsoft Word’s Equation Editor, leveraging a set of specific vulnerabilities (CVE-2018-0802, CVE-2018-0798, and CVE-2017-11882).

These exploits enable the execution of encrypted payloads and shellcode, leading to the establishment of persistence mechanisms within the victims’ systems.

“The emails contain weaponized versions of seemingly genuine official documents, which employ the remote template injection method to retrieve the next stage of the malware from the TA’s Command-and-Control (C&C) server,” the report said.

SharpPanda APT
Opened document attachment from spam email. Image: CRIL

“Upon opening the document, it initiates the download of a new payload from the attacker’s remote server, which is RTF file serving as the next-level payload.”

Upon successful transmission of the victim’s information to the remote server, the technical actors (TAs) meticulously analyze the gathered data.

If the TAs find the victim’s machine to be of interest, the Command-and-Control (C&C) server reciprocates by providing the next stage executable as a response.

“During the final phase of the infection chain, the malicious loader in the SharpPanda APT campaign is specifically designed to download a backdoor module,” said the report.

“However, during our analysis, no response was received from the remote server.”

SparpPanda APT: Recent campaigns

The rise of nation-sponsored threat groups has been a matter of concern for long.

Check Point Research in June 2021 uncovered a surveillance operation by SharpPanda APT targeting a government entity in Southeast Asia.

The attackers utilize spear-phishing techniques and exploit old Microsoft Office vulnerabilities to deploy an unknown backdoor on victim’s machines, the report said.

The operation is believed to be carried out by a Chinese APT group with a history of refining their tools over the past three years.

The group continued to target Southeast Asian governments, particularly those with territorial disputes or strategic infrastructure projects, Check Point researchers found in March 2023.

Sharp Panda’s tools and Tactics, Techniques, and Procedures (TTPs) were observed in the earlier attacks in Southeast Asia.

These traits include the sharing of custom tools among different groups and the division of tasks, where one entity focuses on initiating the infection while another entity specializes in intelligence gathering.

Researchers found that these common traits were associated with Chinese-based APT operations.
Share this:

  • Share on LinkedIn (Opens in new window) LinkedIn
  • Share on Reddit (Opens in new window) Reddit
  • Share on X (Opens in new window) X
  • Share on Facebook (Opens in new window) Facebook
  • More
  • Email a link to a friend (Opens in new window) Email
  • Share on WhatsApp (Opens in new window) WhatsApp

Related

Previous Post

LockBit Claims to Hit Global Zipper Giant YKK, Sets 14-Day Deadline

Next Post

NoEscape Ransomware-as-a-Service (RaaS): Triple-Extortion Affiliate Program Unveiled

Next Post
NoEscape Ransomware-as-a-Service (RaaS)

NoEscape Ransomware-as-a-Service (RaaS): Triple-Extortion Affiliate Program Unveiled

Cyble-Vision


Follow Us On Google News

Categories

Q1 2026 Threat Reports

❮ ❯
  • Privacy Statement
  • Terms of Use
  • Write For Us

© 2026 The Cyber Express - Cybersecurity News and Magazine.

Welcome Back!

Login to your account below

Forgotten Password?

Retrieve your password

Please enter your username or email address to reset your password.

Log In

Add New Playlist

No Result
View All Result
  • Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board

© 2026 The Cyber Express - Cybersecurity News and Magazine.

-
00:00
00:00

Queue

Update Required Flash plugin
-
00:00
00:00



