











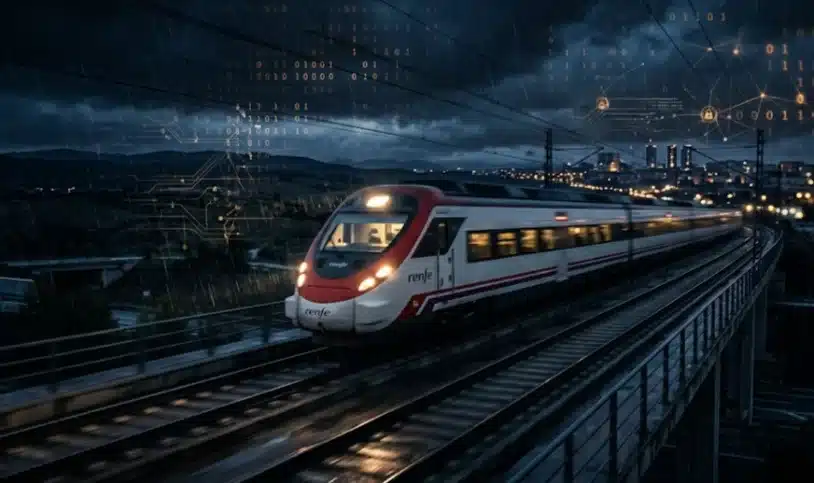
Spain’s state-owned railway operator Renfe confirmed on September 25 that a cyberattack had compromised some of its customers’ data. Spanish media reported that the criminals behind the Renfe cyberattack used artificial intelligence (AI), which would make it the first attack of its kind in the country. Train services across Spain have continued to run normally while the investigation goes on.
According to Renfe, the attackers mainly obtained customer names and email addresses. “The attackers were able to access limited user information, consisting mainly of names and email addresses,” the company said. It added that it had found “no conclusive evidence” that the stolen information had been made public.
The operator, which carried more than 531 million passengers last year, also said, “There is no evidence of access to bank or financial details, payment methods, IDs or other particularly sensitive information.”
Breach Traced to Adif’s Systems
Investigators have linked the cyberattack on Renfe to Adif, the state body that manages Spain’s railway infrastructure. According to The Star, Renfe said in a statement that the “cybersecurity incident” began on Adif servers that were “previously compromised and interconnected with the company’s systems.”
Adif spotted unusual activity on its network late on Thursday and put cybersecurity measures in place to contain it. Neither organization has found evidence that the systems running railway operations were affected, so there has been no disruption to rail services linked to the attack.
The most visible effect was a temporary outage of the Adif website, which was down for part of Friday afternoon. Renfe’s website stayed online.

Weeks of Attempted Intrusions Preceded Renfe Cyberattack
Renfe said the breach followed “several weeks” of attempted attacks on its systems. Its monitoring and security tools had “detected and successfully blocked” those earlier attempts.
Once it detected the breach, Renfe activated its incident-response procedures, isolated the areas that might have been affected and added further protective measures. Independent cybersecurity specialists are helping with the investigation and with efforts to limit any further damage.
Adif has filed a complaint with the relevant authorities and shared what it found with Spain’s National Cryptologic Center (CCN). It has also notified businesses and suppliers that may have been affected so they can take precautions.
Reports of AI Involvement and a Foreign Link
El Mundo cited “sources close to the investigation” who said a criminal organization used “a system similar” to Anthropic’s AI to attack Adif’s website, which was unavailable on September 25. The newspaper described it as the first AI-driven cyberattack on the website of a Spanish public company and said the incident lasted “several days.”
La Razón reported that sources familiar with the case believe “the modus operandi points to a foreign group.”
Wider Concerns Over AI and Hybrid Threats
The cyberattack on Renfe comes as concern grows worldwide about what advanced AI tools can do, following a series of hacking incidents involving models from OpenAI, the developer of ChatGPT, and its rival Anthropic.
Warnings have also increased about possible hybrid attacks, including cyber incidents, targeting Western allies of Ukraine as Russia’s invasion enters its fifth year.
Renfe and Adif are still investigating where the attack came from and how far it reached, including how much customer information was accessed without authorization.