
















• Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
The Cyber Express
  • MagazineDownload
  • Firewall Daily
    • All
    • Bug Bounty & Rewards
    • Dark Web News
    • Data Breach News
    • Hacker News
    • Ransomware News
    • Vulnerabilities
    weekly roundup October 30

    The Cyber Express Weekly Roundup: Binance Hit by $6.3 Billion Security Incident, South Korea Busts AI-Powered Hacking Ring and More

    Binance Data Breach

    Binance Security Incident Affects $6.3 Billion in Crypto Assets, $3 Billion Frozen

    Cyberattacks on Japan

    Three Cyberattack Campaigns Target Japan, Exposing AI’s Growing Role

    Ukrainian ransomware affiliate

    Ransomware Attacks on Hospitals and Businesses Lead to 70-Month Sentence

    FBI seizes Virtualine

    FBI Seizes Bulletproof Hosting Domain Linked to Cybercrime

    ASD Cyber Threat Report

    Australian Data Breach Incidents Up 66% as AI Sharpens Scams

    INJ3CTOR3

    INJ3CTOR3 Malware Steals FreePBX Credentials, Enabling Toll Fraud After Cleanup

    Discoverable Servers

    Discord to Let Google Index Public Server Messages, Raising Privacy Concerns

    Columbia University cyberattack

    Columbia University Settles $16.1M Data Breach Lawsuit After 2025 Cyberattack

    Trending Tags

    • blackbyte ransomware
    • Ransomware
    • lapsus$ ransomware
    • Apple
    • Apple vulnerability
  • Essentials
    • All
    • Compliance
    • Governance
    • Policy Updates
    • Regulations
    ASD Essentials

    The Essential Eight Is Being Replaced: What Australian Organisations Need to Know

    SICW 2026

    AI Is Now Fighting on Both Sides of the Cyber War, Singapore Warns

    Morocco cybersecurity strategy

    Morocco Flags AI Threats, Prioritizes Critical Infrastructure Defense

    European Police Chiefs Convention 2026

    Europe’s Police Chiefs Face Growing Threat of AI-Driven Crime

    AI service security

    Hackers Are Stealing AI Keys. The Cost Can Reach $600,000

    AI security risks

    Sam Altman at UN Security Council: 6 AI Security Risks the World Cannot Ignore

    AI-enabled cyber attacks

    AI Gives Hackers an Edge Defenders Still Can’t Match, NCSC Warns

    Fraudulent SIM cards

    India’s DoT Warns Citizens Over SIM Fraud and IMEI Tampering

    EU cybersecurity incidents

    EU Cybersecurity Response Hampered by Critical Information Gaps

    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
    • All
    • How to
    • What is
    Infostealer Intelligence

    The 2026 Infostealer Intelligence Shortlist: Top 10 Vendors Security Teams Should Know

    Google Chrome

    How to Remove Saved Passwords From Google Chrome (And Why You Should)

    DPDP Rules, Cyble, DPDP Act, Cyble Vantage

    How Cyble’s Front-Row Vantage Can Help You in Complying to India’s DPDP Act

    Cybersecurity Countries

    The Top 8 Countries Leading the Cyber Defense Race in 2025

    link building

    The Link Building Secrets Your Competitors Don’t Want You to Know

    Supply Chain Attack

    Supply Chain Resilience and Physical Security: Lessons for 2025

    Healthcare cybersecurity trends of 2024

    Healthcare Cybersecurity: 2024 Was Tough, 2025 May Be Better

    CEO's Guide to Take-Down Services

    Shield Your Organization: CEO’s Perspective on Take-Down Services

    Azure sign-in Microsoft

    Microsoft Announces Mandatory MFA for Azure Sign-ins to Bolster Cloud Defenses

  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • All
    • Appointments
    • Budgets
    • Mergers & Aquisitions
    • Partnerships
    • Press Release
    • Startups
    Kerala Police Signs MoU With Cyble

    Kerala Police Signs MoU With Cyble to Use Threat Intelligence in Cybercrime Probes

    Gemini 4 Argon

    Gemini 4 Argon Restricted Over Cybersecurity Misuse Risks

    weekly roundup September 18 2026

    The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

    threat intelligence

    Cyble, UAE Cyber Security Council Unite Against Rising Cyber Threats

    Ukraine cybersecurity

    Zelensky Appoints Ihor Klymenko to Lead Ukraine’s Cybersecurity Center

    UK cyberattack rate

    UK Small Firms Bear Brunt of Rising Cyberattacks, Hiscox Finds

    Cyber Yodha Campaign

    Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

    UK Ukraine AI partnership

    Britain Gains Access to Ukraine’s ‘Goldmine’ of Battlefield AI Data

    Hims & Hers lawsuit

    FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices

    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
No Result
View All Result
The Cyber Express
No Result
View All Result

Vietnam-Linked PXA Stealer Campaign Exploits LinkedIn to Target Professionals Globally

Ashish Khaitan by Ashish Khaitan
April 2, 2026
in Firewall Daily, Data Breach News
0
PXA Stealer
585
SHARES
3.2k
VIEWS
Share on LinkedInShare on Twitter

A newly exposed global malware campaign reveals how PXA Stealer has been wielded by Vietnam‑linked actors to siphon sensitive data from professionals across multiple countries using trusted platforms like LinkedIn. First documented in late 2024, this campaign has evolved into a new threat that leverages social engineering, advanced payload delivery, and stealthy execution to outmaneuver traditional defenses.  

Cybersecurity researchers at Cyble have mapped the multi‑stage attack chain, attributing the PXA Stealer campaign with a high degree of confidence to cybercriminals operating from Vietnam. These Vietnam‑linked actors target job seekers and professionals in India, Bangladesh, Sweden, the Netherlands, and the United States, exploiting trust in professional outreach to propagate their malware at scale. 

Fake Recruiter Messages Feed the PXA Stealer Infection Chain 

The campaign typically begins with a direct message on LinkedIn from a compromised or spoofed account posing as a recruiter from a fictitious company called Apex Logistics Group. The message promises remote work opportunities in fields like digital marketing and invites targets to engage, a tactic that lowers suspicion due to the context of career networking. 
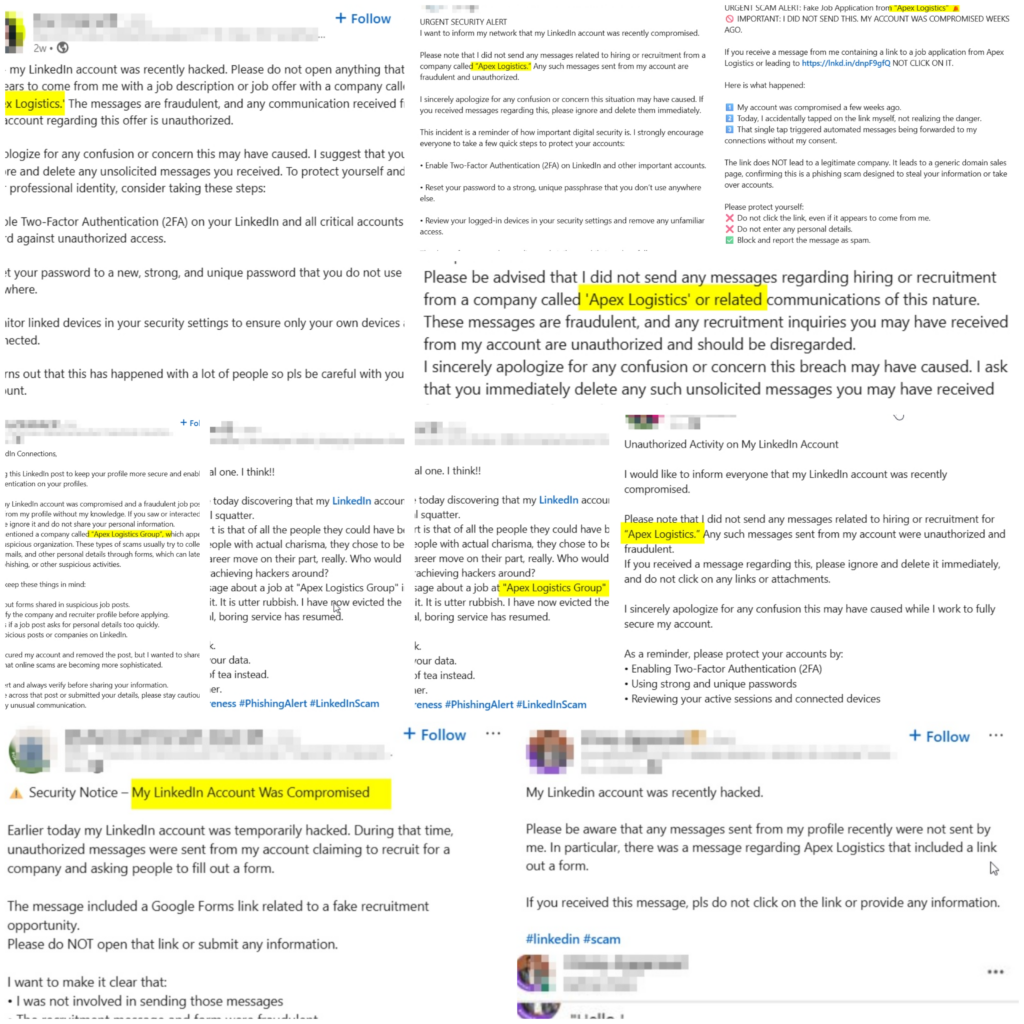
account compromises linked to the Apex Logistics Group
Account compromises linked to the Apex Logistics Group (Source: Cyble)

Once interest is established, victims are asked to complete a Google Form and then redirected through a URL shortener to a Zip archive hosted on cloud storage. That file, labeled with a job‑related name, contains a seemingly legitimate Microsoft Word executable that initiates a DLL sideloading sequence once launched. This technique allows the malicious DLL payload to load under the guise of a trusted binary. 
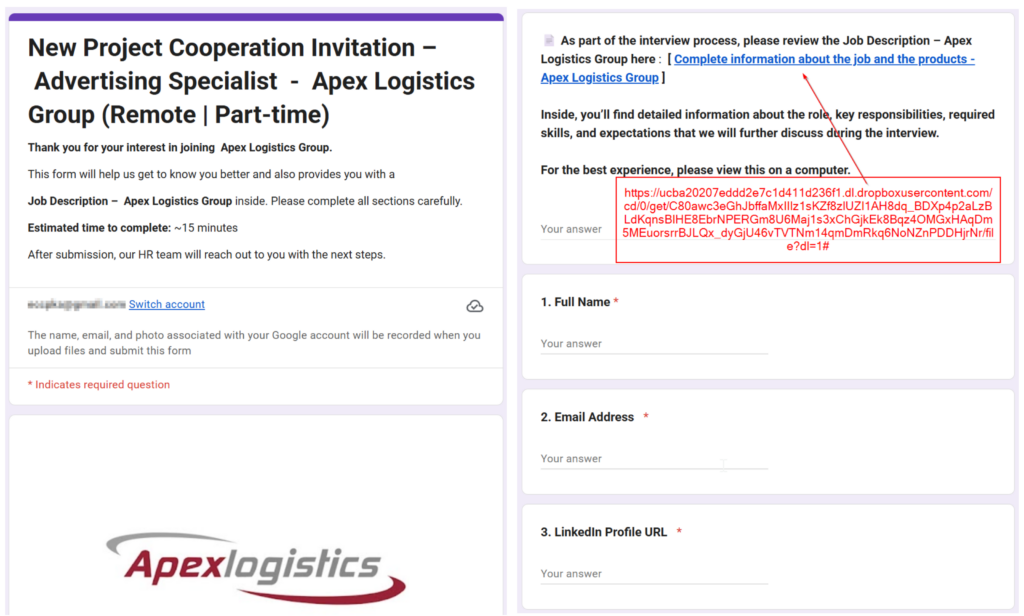
Google Form with hyperlink
Google Form with hyperlink (Source: Cyble)

To bypass detection, threat actors inflate the size of the malicious DLL to roughly 100 MB, far larger than its legitimate counterpart. A form of binary padding designed to slip past scanners that skip oversized files. The final payload, PXA Stealer, then executes solely in memory, leaving minimal traces on disk and greatly impeding forensic analysis. 

Data Exfiltration and Persistence 

Once active on a victim machine, PXA Stealer focuses on harvesting a wide range of sensitive materials. This includes: 

  • Stored browser login credentials, cookies, and session tokens  
  • Cryptocurrency wallet identifiers and associated applications  
  • Two‑factor authentication secrets from authenticator apps  
  • Desktop and email client credentials  

Persistence is established through scheduled tasks disguised as standard system updates, such as a bogus Microsoft Edge update, blending malicious activity into normal operations. Exfiltration of stolen data is facilitated through encrypted Telegram channels and hidden command‑and‑control infrastructure that can masquerade as legitimate services to avoid detection. 

A New Kind of Threat 

Technical analysis of the PXA Stealer campaign shows a steady increase in technical activities since cybersecurity researchers first documented the strain in November 2024. Originally a Python‑based infostealer, the malware has since developed multi‑layer obfuscation, memory‑only execution, and dynamic command infrastructure retrieval via Telegram, traits which complicate detection and mitigation. 
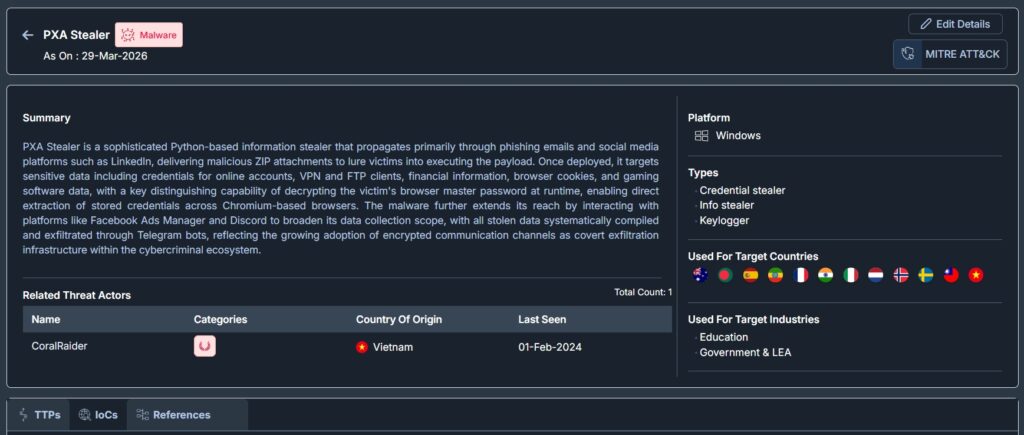
PXA Stealer Malware profile
PXA Stealer Malware profile (Source: Cyble)

Through 2025, researchers observed expanded sideloading vehicles, enhanced obfuscation layers, and broader geographic targeting. By late 2025 and into early 2026, the attackers diversified the social engineering lures beyond job offers to include invitations to view tax forms, legal documents, and software installers. These hooks are designed to increase the likelihood of user interaction, particularly among the professionals most likely to be active on LinkedIn. 

Global Scale and Consequences 

Investigations by multiple cybersecurity groups indicate that PXA Stealer has already impacted tens of thousands of devices worldwide, with estimates of over 94,000 infected systems spanning Europe, Asia, and the Americas. The theft of credentials, including hundreds of thousands of unique passwords and millions of browser cookies, has enabled criminal actors to bypass multi‑factor authentication and escalate unauthorized access quickly. 

Victims range from individual job seekers to organizations in heavily regulated sectors. Companies face not only immediate compromise of systems and accounts but also longer‑term risks, including Business Email Compromise, regulatory breaches under frameworks like GDPR, and reputational harm if employee or customer data is misused.

The PXA Stealer campaign shows how Vietnam‑linked actors exploit LinkedIn and fake recruiters like Apex Logistics Group to steal credentials, crypto wallets, and sensitive data. Organizations need vigilant defenses, including employee training, endpoint protection, MFA, and monitoring for unusual activity. Cyble offers AI-powered threat intelligence that predicts, detects, and neutralizes such attacks in real time. Schedule a demo to see how Cyble protects against threats like PXA Stealer. 

Share this:

  • Share on LinkedIn (Opens in new window) LinkedIn
  • Share on Reddit (Opens in new window) Reddit
  • Share on X (Opens in new window) X
  • Share on Facebook (Opens in new window) Facebook
  • More
  • Email a link to a friend (Opens in new window) Email
  • Share on WhatsApp (Opens in new window) WhatsApp

Related

Tags: Apex Logistics GroupPXA StealerThe Cyber ExpressThe Cyber Express NewsVietnam‑linked actors
Previous Post

FBI Warns of Data Security Risks in Foreign-Developed Mobile Apps

Next Post

The Cyber Express Weekly Roundup: Ransomware, and Supply Chain Breaches Surge

Next Post
The Cyber Express weekly roundup April 2026

The Cyber Express Weekly Roundup: Ransomware, and Supply Chain Breaches Surge

Cyble-Vision


Follow Us On Google News

Categories

Q1 2026 Threat Reports

❮ ❯
  • Privacy Statement
  • Terms of Use
  • Write For Us

© 2026 The Cyber Express - Cybersecurity News and Magazine.

Welcome Back!

Login to your account below

Forgotten Password?

Retrieve your password

Please enter your username or email address to reset your password.

Log In

Add New Playlist

No Result
View All Result
  • Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board

© 2026 The Cyber Express - Cybersecurity News and Magazine.

-
00:00
00:00

Queue

Update Required Flash plugin
-
00:00
00:00



