



















• Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
The Cyber Express
  • MagazineDownload
  • Firewall Daily
    • All
    • Bug Bounty & Rewards
    • Dark Web News
    • Data Breach News
    • Hacker News
    • Ransomware News
    • Vulnerabilities
    Jensen Huang resigns

    Jensen Huang Exits Nvidia Days After the Board Said It Backed Him

    FaceStealer

    US Disrupts North Korea’s FaceStealer Campaign, Targets $1.2 Billion in Stolen Crypto

    SignDrop zero-day exploit

    New SignDrop Exploit Claims SYSTEM Access on Windows Through CLFS

    Microsoft 365 Outage

    Why Did Outlook Go Down? Microsoft Traced It to Its Own Servers

    WorkOS, AI Agent, Prompt Injection, Grok, Grok AI, Gemini, Fraud, Agentic AI, AI-assisted Cyberattacks

    WorkOS Says a Researcher’s Runaway AI Pentest Agent Copied Customer Sales Records

    Nvidia board investigation

    Why Is Nvidia Investigating Its Own CEO, and Can the Board Remove Him?

    weekly roundup

    The Cyber Express Weekly Roundup: FBI Blames North Korea for $6B Binance Hack, Hackers Turn Up the Heat on Europe’s Fridges and More

    Stockal cyberattack

    Stockal Confirms Unauthorized Trades in 13 Customer Accounts

    Alpine Linux servers

    Alpine Linux SSH Flaw Lets Attackers Log In Without a Password

    Trending Tags

    • blackbyte ransomware
    • Ransomware
    • lapsus$ ransomware
    • Apple
    • Apple vulnerability
  • Essentials
    • All
    • Compliance
    • Governance
    • Policy Updates
    • Regulations
    SEC, Misleading Cyber Disclosures, Financial data, financial data protection, SEC

    SEC Enforcement Fell 24% in Fiscal 2026

    ASD Essentials

    The Essential Eight Is Being Replaced: What Australian Organisations Need to Know

    SICW 2026

    AI Is Now Fighting on Both Sides of the Cyber War, Singapore Warns

    Morocco cybersecurity strategy

    Morocco Flags AI Threats, Prioritizes Critical Infrastructure Defense

    European Police Chiefs Convention 2026

    Europe’s Police Chiefs Face Growing Threat of AI-Driven Crime

    AI service security

    Hackers Are Stealing AI Keys. The Cost Can Reach $600,000

    AI security risks

    Sam Altman at UN Security Council: 6 AI Security Risks the World Cannot Ignore

    AI-enabled cyber attacks

    AI Gives Hackers an Edge Defenders Still Can’t Match, NCSC Warns

    Fraudulent SIM cards

    India’s DoT Warns Citizens Over SIM Fraud and IMEI Tampering

    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
    • All
    • How to
    • What is
    Infostealer Intelligence

    The 2026 Infostealer Intelligence Shortlist: Top 10 Vendors Security Teams Should Know

    Google Chrome

    How to Remove Saved Passwords From Google Chrome (And Why You Should)

    DPDP Rules, Cyble, DPDP Act, Cyble Vantage

    How Cyble’s Front-Row Vantage Can Help You in Complying to India’s DPDP Act

    Cybersecurity Countries

    The Top 8 Countries Leading the Cyber Defense Race in 2025

    link building

    The Link Building Secrets Your Competitors Don’t Want You to Know

    Supply Chain Attack

    Supply Chain Resilience and Physical Security: Lessons for 2025

    Healthcare cybersecurity trends of 2024

    Healthcare Cybersecurity: 2024 Was Tough, 2025 May Be Better

    CEO's Guide to Take-Down Services

    Shield Your Organization: CEO’s Perspective on Take-Down Services

    Azure sign-in Microsoft

    Microsoft Announces Mandatory MFA for Azure Sign-ins to Bolster Cloud Defenses

  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • All
    • Appointments
    • Budgets
    • Mergers & Aquisitions
    • Partnerships
    • Press Release
    • Startups
    Kerala Police Signs MoU With Cyble

    Kerala Police Signs MoU With Cyble to Use Threat Intelligence in Cybercrime Probes

    Gemini 4 Argon

    Gemini 4 Argon Restricted Over Cybersecurity Misuse Risks

    weekly roundup September 18 2026

    The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

    threat intelligence

    Cyble, UAE Cyber Security Council Unite Against Rising Cyber Threats

    Ukraine cybersecurity

    Zelensky Appoints Ihor Klymenko to Lead Ukraine’s Cybersecurity Center

    UK cyberattack rate

    UK Small Firms Bear Brunt of Rising Cyberattacks, Hiscox Finds

    Cyber Yodha Campaign

    Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

    UK Ukraine AI partnership

    Britain Gains Access to Ukraine’s ‘Goldmine’ of Battlefield AI Data

    Hims & Hers lawsuit

    FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices

    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
No Result
View All Result
  • MagazineDownload
  • Firewall Daily
    • All
    • Bug Bounty & Rewards
    • Dark Web News
    • Data Breach News
    • Hacker News
    • Ransomware News
    • Vulnerabilities
    Jensen Huang resigns

    Jensen Huang Exits Nvidia Days After the Board Said It Backed Him

    FaceStealer

    US Disrupts North Korea’s FaceStealer Campaign, Targets $1.2 Billion in Stolen Crypto

    SignDrop zero-day exploit

    New SignDrop Exploit Claims SYSTEM Access on Windows Through CLFS

    Microsoft 365 Outage

    Why Did Outlook Go Down? Microsoft Traced It to Its Own Servers

    WorkOS, AI Agent, Prompt Injection, Grok, Grok AI, Gemini, Fraud, Agentic AI, AI-assisted Cyberattacks

    WorkOS Says a Researcher’s Runaway AI Pentest Agent Copied Customer Sales Records

    Nvidia board investigation

    Why Is Nvidia Investigating Its Own CEO, and Can the Board Remove Him?

    weekly roundup

    The Cyber Express Weekly Roundup: FBI Blames North Korea for $6B Binance Hack, Hackers Turn Up the Heat on Europe’s Fridges and More

    Stockal cyberattack

    Stockal Confirms Unauthorized Trades in 13 Customer Accounts

    Alpine Linux servers

    Alpine Linux SSH Flaw Lets Attackers Log In Without a Password

    Trending Tags

    • blackbyte ransomware
    • Ransomware
    • lapsus$ ransomware
    • Apple
    • Apple vulnerability
  • Essentials
    • All
    • Compliance
    • Governance
    • Policy Updates
    • Regulations
    SEC, Misleading Cyber Disclosures, Financial data, financial data protection, SEC

    SEC Enforcement Fell 24% in Fiscal 2026

    ASD Essentials

    The Essential Eight Is Being Replaced: What Australian Organisations Need to Know

    SICW 2026

    AI Is Now Fighting on Both Sides of the Cyber War, Singapore Warns

    Morocco cybersecurity strategy

    Morocco Flags AI Threats, Prioritizes Critical Infrastructure Defense

    European Police Chiefs Convention 2026

    Europe’s Police Chiefs Face Growing Threat of AI-Driven Crime

    AI service security

    Hackers Are Stealing AI Keys. The Cost Can Reach $600,000

    AI security risks

    Sam Altman at UN Security Council: 6 AI Security Risks the World Cannot Ignore

    AI-enabled cyber attacks

    AI Gives Hackers an Edge Defenders Still Can’t Match, NCSC Warns

    Fraudulent SIM cards

    India’s DoT Warns Citizens Over SIM Fraud and IMEI Tampering

    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
    • All
    • How to
    • What is
    Infostealer Intelligence

    The 2026 Infostealer Intelligence Shortlist: Top 10 Vendors Security Teams Should Know

    Google Chrome

    How to Remove Saved Passwords From Google Chrome (And Why You Should)

    DPDP Rules, Cyble, DPDP Act, Cyble Vantage

    How Cyble’s Front-Row Vantage Can Help You in Complying to India’s DPDP Act

    Cybersecurity Countries

    The Top 8 Countries Leading the Cyber Defense Race in 2025

    link building

    The Link Building Secrets Your Competitors Don’t Want You to Know

    Supply Chain Attack

    Supply Chain Resilience and Physical Security: Lessons for 2025

    Healthcare cybersecurity trends of 2024

    Healthcare Cybersecurity: 2024 Was Tough, 2025 May Be Better

    CEO's Guide to Take-Down Services

    Shield Your Organization: CEO’s Perspective on Take-Down Services

    Azure sign-in Microsoft

    Microsoft Announces Mandatory MFA for Azure Sign-ins to Bolster Cloud Defenses

  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • All
    • Appointments
    • Budgets
    • Mergers & Aquisitions
    • Partnerships
    • Press Release
    • Startups
    Kerala Police Signs MoU With Cyble

    Kerala Police Signs MoU With Cyble to Use Threat Intelligence in Cybercrime Probes

    Gemini 4 Argon

    Gemini 4 Argon Restricted Over Cybersecurity Misuse Risks

    weekly roundup September 18 2026

    The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

    threat intelligence

    Cyble, UAE Cyber Security Council Unite Against Rising Cyber Threats

    Ukraine cybersecurity

    Zelensky Appoints Ihor Klymenko to Lead Ukraine’s Cybersecurity Center

    UK cyberattack rate

    UK Small Firms Bear Brunt of Rising Cyberattacks, Hiscox Finds

    Cyber Yodha Campaign

    Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

    UK Ukraine AI partnership

    Britain Gains Access to Ukraine’s ‘Goldmine’ of Battlefield AI Data

    Hims & Hers lawsuit

    FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices

    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
No Result
View All Result
The Cyber Express
No Result
View All Result

Longhorn Cyber Attack Puts Data of 28000 Patients at Risk

The leaked data reportedly includes a vast range of sensitive information such as full names of physicians, patients, treatment details, dates of birth, genders and more.

Ashish Khaitan by Ashish Khaitan
June 26, 2023
in Firewall Daily, Hacker Claims
0
Longhorn Cyber Attack
585
SHARES
3.2k
VIEWS
Share on LinkedInShare on Twitter

Longhorn Imaging, a prominent medical imaging service, has allegedly fallen victim to a cyber attack by the notorious hacker group SiegedSec. 

The group has claimed the Longhorn cyber attack and asserts that they have successfully infiltrated the company’s systems, compromising an extensive database containing more than 280,000 patient records. 

Daily Dark Web, a threat intelligence service that monitors illicit activities on the internet, shared the details of the Longhorn cyber attack. 

In a Twitter post, Daily Dark Web shared a screenshot of the statement made by the threat actor responsible for the Longhorn data breach.
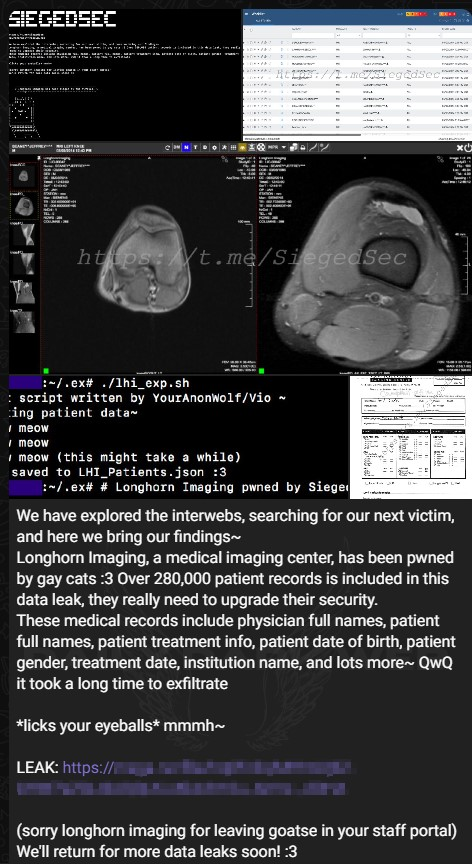
Longhorn data breach
Daily Dark Web on Twitter

The Cyber Express reached out to the US-based medical imaging center to confirm the Longhorn cyber attack claims. However, at the time of writing, we did not receive an official response from the company.

The Longhorn data breach has added more weight to the ongoing concerns about the US medical attacks and the overall security of patient data in the US healthcare sector.

Longhorn data breach and the threat actor’s post 

The statement posted by the threat actor appeared on a dark web forum, typically used by cybercriminals to share stolen data and boast about their exploits. The post included a link to a data leak, suggesting that the compromised patient records from the Longhorn data breach have been stored and made available for unauthorized access.

The leaked data reportedly includes a vast range of sensitive information such as full names of physicians and patients, patient treatment details, dates of birth, genders, treatment dates, institution names, and various other details pertaining to patient healthcare.

The threat actor behind the Longhorn cyber attack on a US-based medical imaging service expressed satisfaction at the exfiltration of this information, hinting at the extensive efforts and time it took to carry out the Longhorn data breach.

The implications of this alleged breach are grave, as the compromised data could potentially be exploited for various nefarious purposes.

Patient records contain highly personal and confidential information, making them a prime target for cybercriminals seeking to engage in identity theft, financial fraud, or even extortion.

Moreover, such breaches can erode patients’ trust in medical service providers, jeopardizing the reputation of Longhorn Imaging and the overall confidence in the healthcare industry’s ability to protect sensitive data.

Cyber attack on Longhorn and US medical center breaches: What’s the next step?

Apart from the latest Longhorn data breach in this case, to combat the ongoing battle against hacker groups targeting medical facilities, UpGuard has shared its “Ultimate Cybersecurity Guide for Healthcare in 2023” guide.

The report highlights the prevalence of data breaches in healthcare organizations and emphasizes the importance of basic cybersecurity practices in preventing such incidents. 

The guide focuses on mitigating cybersecurity risks and enhancing data breach resilience through a tailored cybersecurity program.

It suggests performing a risk assessment to identify areas for improvement and define a risk appetite that sets the maximum level of security risks an organization is willing to tolerate.

It also provides security responses and recommended controls for each stage of a ransomware attack, including phishing prevention, multi-factor authentication, endpoint detection and response, and network segmentation.

The guide explains the difference between regulations and cybersecurity frameworks and highlights the importance of compliance with the Health Insurance Portability and Accountability Act (HIPAA) in the healthcare industry. 

The report also provides an overview of HIPAA’s privacy and security rules and outlines administrative, physical, and technical safeguards necessary for compliance.

UpGuard’s report concludes by emphasizing the need for healthcare organizations to adopt cybersecurity frameworks such as the NIST Cybersecurity Framework and HITRUST to enhance their security posture and meet regulatory requirements like HIPAA.

Media Disclaimer: This report is based on internal and external research obtained through various means. The information provided is for reference purposes only, and users bear full responsibility for their reliance on it. The Cyber Express assumes no liability for the accuracy or consequences of using this information.

Share this:

  • Share on LinkedIn (Opens in new window) LinkedIn
  • Share on Reddit (Opens in new window) Reddit
  • Share on X (Opens in new window) X
  • Share on Facebook (Opens in new window) Facebook
  • More
  • Email a link to a friend (Opens in new window) Email
  • Share on WhatsApp (Opens in new window) WhatsApp

Related

Previous Post

Thai Meteorological Department Cyber Attack, LockBit Sets Deadline

Next Post

A Tale of Two US Audits: Why Does Government Cybersecurity Preparedness Fail Miserably?

Next Post
Government Cybersecurity Preparedness

A Tale of Two US Audits: Why Does Government Cybersecurity Preparedness Fail Miserably?

Q1 2026 Threat Reports

❮ ❯
Cyble-Vision


Follow Us On Google News

Categories

  • Privacy Statement
  • Terms of Use
  • Write For Us

© 2026 The Cyber Express - Cybersecurity News and Magazine.

Welcome Back!

Login to your account below

Forgotten Password?

Retrieve your password

Please enter your username or email address to reset your password.

Log In

Add New Playlist

No Result
View All Result
  • Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board

© 2026 The Cyber Express - Cybersecurity News and Magazine.

-
00:00
00:00

Queue

Update Required Flash plugin
-
00:00
00:00



