



















• Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
The Cyber Express
  • MagazineDownload
  • Firewall Daily
    • All
    • Bug Bounty & Rewards
    • Dark Web News
    • Data Breach News
    • Hacker News
    • Ransomware News
    • Vulnerabilities
    weekly roundup September 20 2026

    The Cyber Express Weekly Cyber Roundup: California Sues OpenAI Over Runaway AI Agents, Java4Shell Threatens Enterprise Apps, and More

    ARMORY CASTLE

    ARMORY CASTLE Chains Second Zero-Day Vulnerability to Seize VMware vCenter

    CVE-2026-123633

    NGINX HTTP/2 Flaws CVE-2026-123633 and CVE-2026-123007 Enable Unauthenticated Remote Code Execution

    CVE-2026-114938

    Java4Shell Flaw Opens Major Java Applications to RCE Attacks

    8-Digits Team ransomware

    Alleged Member of Ransomware Gang That Claimed 70 Million Health Records Extradited to US

    AI Threat Tracker

    Google Finds Hackers Using AI Agents to Automate Cyberattacks

    OpenAI lawsuit

    California Sues OpenAI After Its AI Agents Escaped Testing and Hacked Hugging Face

    Luxor cyberattack

    Hackers Hijack Luxor Mining Software to Divert Bitcoin Mining Rewards

    Coles cyberattack

    Coles Confirms Cyber Incident, Woolworths Investigates Gift Card Complaints

    Trending Tags

    • blackbyte ransomware
    • Ransomware
    • lapsus$ ransomware
    • Apple
    • Apple vulnerability
  • Essentials
    • All
    • Compliance
    • Governance
    • Policy Updates
    • Regulations
    SEC, Misleading Cyber Disclosures, Financial data, financial data protection, SEC

    SEC Enforcement Fell 24% in Fiscal 2026

    ASD Essentials

    The Essential Eight Is Being Replaced: What Australian Organisations Need to Know

    SICW 2026

    AI Is Now Fighting on Both Sides of the Cyber War, Singapore Warns

    Morocco cybersecurity strategy

    Morocco Flags AI Threats, Prioritizes Critical Infrastructure Defense

    European Police Chiefs Convention 2026

    Europe’s Police Chiefs Face Growing Threat of AI-Driven Crime

    AI service security

    Hackers Are Stealing AI Keys. The Cost Can Reach $600,000

    AI security risks

    Sam Altman at UN Security Council: 6 AI Security Risks the World Cannot Ignore

    AI-enabled cyber attacks

    AI Gives Hackers an Edge Defenders Still Can’t Match, NCSC Warns

    Fraudulent SIM cards

    India’s DoT Warns Citizens Over SIM Fraud and IMEI Tampering

    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
    • All
    • How to
    • What is
    Infostealer Intelligence

    The 2026 Infostealer Intelligence Shortlist: Top 10 Vendors Security Teams Should Know

    Google Chrome

    How to Remove Saved Passwords From Google Chrome (And Why You Should)

    DPDP Rules, Cyble, DPDP Act, Cyble Vantage

    How Cyble’s Front-Row Vantage Can Help You in Complying to India’s DPDP Act

    Cybersecurity Countries

    The Top 8 Countries Leading the Cyber Defense Race in 2025

    link building

    The Link Building Secrets Your Competitors Don’t Want You to Know

    Supply Chain Attack

    Supply Chain Resilience and Physical Security: Lessons for 2025

    Healthcare cybersecurity trends of 2024

    Healthcare Cybersecurity: 2024 Was Tough, 2025 May Be Better

    CEO's Guide to Take-Down Services

    Shield Your Organization: CEO’s Perspective on Take-Down Services

    Azure sign-in Microsoft

    Microsoft Announces Mandatory MFA for Azure Sign-ins to Bolster Cloud Defenses

  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • All
    • Appointments
    • Budgets
    • Mergers & Aquisitions
    • Partnerships
    • Press Release
    • Startups
    Kerala Police Signs MoU With Cyble

    Kerala Police Signs MoU With Cyble to Use Threat Intelligence in Cybercrime Probes

    Gemini 4 Argon

    Gemini 4 Argon Restricted Over Cybersecurity Misuse Risks

    weekly roundup September 18 2026

    The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

    threat intelligence

    Cyble, UAE Cyber Security Council Unite Against Rising Cyber Threats

    Ukraine cybersecurity

    Zelensky Appoints Ihor Klymenko to Lead Ukraine’s Cybersecurity Center

    UK cyberattack rate

    UK Small Firms Bear Brunt of Rising Cyberattacks, Hiscox Finds

    Cyber Yodha Campaign

    Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

    UK Ukraine AI partnership

    Britain Gains Access to Ukraine’s ‘Goldmine’ of Battlefield AI Data

    Hims & Hers lawsuit

    FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices

    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
No Result
View All Result
  • MagazineDownload
  • Firewall Daily
    • All
    • Bug Bounty & Rewards
    • Dark Web News
    • Data Breach News
    • Hacker News
    • Ransomware News
    • Vulnerabilities
    weekly roundup September 20 2026

    The Cyber Express Weekly Cyber Roundup: California Sues OpenAI Over Runaway AI Agents, Java4Shell Threatens Enterprise Apps, and More

    ARMORY CASTLE

    ARMORY CASTLE Chains Second Zero-Day Vulnerability to Seize VMware vCenter

    CVE-2026-123633

    NGINX HTTP/2 Flaws CVE-2026-123633 and CVE-2026-123007 Enable Unauthenticated Remote Code Execution

    CVE-2026-114938

    Java4Shell Flaw Opens Major Java Applications to RCE Attacks

    8-Digits Team ransomware

    Alleged Member of Ransomware Gang That Claimed 70 Million Health Records Extradited to US

    AI Threat Tracker

    Google Finds Hackers Using AI Agents to Automate Cyberattacks

    OpenAI lawsuit

    California Sues OpenAI After Its AI Agents Escaped Testing and Hacked Hugging Face

    Luxor cyberattack

    Hackers Hijack Luxor Mining Software to Divert Bitcoin Mining Rewards

    Coles cyberattack

    Coles Confirms Cyber Incident, Woolworths Investigates Gift Card Complaints

    Trending Tags

    • blackbyte ransomware
    • Ransomware
    • lapsus$ ransomware
    • Apple
    • Apple vulnerability
  • Essentials
    • All
    • Compliance
    • Governance
    • Policy Updates
    • Regulations
    SEC, Misleading Cyber Disclosures, Financial data, financial data protection, SEC

    SEC Enforcement Fell 24% in Fiscal 2026

    ASD Essentials

    The Essential Eight Is Being Replaced: What Australian Organisations Need to Know

    SICW 2026

    AI Is Now Fighting on Both Sides of the Cyber War, Singapore Warns

    Morocco cybersecurity strategy

    Morocco Flags AI Threats, Prioritizes Critical Infrastructure Defense

    European Police Chiefs Convention 2026

    Europe’s Police Chiefs Face Growing Threat of AI-Driven Crime

    AI service security

    Hackers Are Stealing AI Keys. The Cost Can Reach $600,000

    AI security risks

    Sam Altman at UN Security Council: 6 AI Security Risks the World Cannot Ignore

    AI-enabled cyber attacks

    AI Gives Hackers an Edge Defenders Still Can’t Match, NCSC Warns

    Fraudulent SIM cards

    India’s DoT Warns Citizens Over SIM Fraud and IMEI Tampering

    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
    • All
    • How to
    • What is
    Infostealer Intelligence

    The 2026 Infostealer Intelligence Shortlist: Top 10 Vendors Security Teams Should Know

    Google Chrome

    How to Remove Saved Passwords From Google Chrome (And Why You Should)

    DPDP Rules, Cyble, DPDP Act, Cyble Vantage

    How Cyble’s Front-Row Vantage Can Help You in Complying to India’s DPDP Act

    Cybersecurity Countries

    The Top 8 Countries Leading the Cyber Defense Race in 2025

    link building

    The Link Building Secrets Your Competitors Don’t Want You to Know

    Supply Chain Attack

    Supply Chain Resilience and Physical Security: Lessons for 2025

    Healthcare cybersecurity trends of 2024

    Healthcare Cybersecurity: 2024 Was Tough, 2025 May Be Better

    CEO's Guide to Take-Down Services

    Shield Your Organization: CEO’s Perspective on Take-Down Services

    Azure sign-in Microsoft

    Microsoft Announces Mandatory MFA for Azure Sign-ins to Bolster Cloud Defenses

  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • All
    • Appointments
    • Budgets
    • Mergers & Aquisitions
    • Partnerships
    • Press Release
    • Startups
    Kerala Police Signs MoU With Cyble

    Kerala Police Signs MoU With Cyble to Use Threat Intelligence in Cybercrime Probes

    Gemini 4 Argon

    Gemini 4 Argon Restricted Over Cybersecurity Misuse Risks

    weekly roundup September 18 2026

    The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

    threat intelligence

    Cyble, UAE Cyber Security Council Unite Against Rising Cyber Threats

    Ukraine cybersecurity

    Zelensky Appoints Ihor Klymenko to Lead Ukraine’s Cybersecurity Center

    UK cyberattack rate

    UK Small Firms Bear Brunt of Rising Cyberattacks, Hiscox Finds

    Cyber Yodha Campaign

    Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

    UK Ukraine AI partnership

    Britain Gains Access to Ukraine’s ‘Goldmine’ of Battlefield AI Data

    Hims & Hers lawsuit

    FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices

    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
No Result
View All Result
The Cyber Express
No Result
View All Result

Fastest Ever: Rorschach Ransomware Encrypts in Less Than 5 Minutes

The partly autonomous Rorschach ransomware was found spreading upon execution on a Domain Controller that moves laterally on other machines within the domain

thecyberexpress by thecyberexpress
June 26, 2023
in Firewall Daily, Ransomware News
0
Rorschach Ransomware
585
SHARES
3.2k
VIEWS
Share on LinkedInShare on Twitter

Security researchers detected a previously unnamed ransomware strain, now dubbed Rorschach, in an attack against a US-based company.

What sets Rorschach ransomware apart from other strains is its high level of customization and technically unique features, making it one of the fastest ransomware strains ever observed in terms of encryption speed.

“Rorschach ransomware appears to be unique, sharing no overlaps that could easily attribute it to any known ransomware strain,” said the report by Check Point.

In addition, it does not bear any kind of branding which is a common practice among ransomware groups.

During the research, Rorschach ransomware was found to have an ‘unusual’ detection evading mechanism. Besides being customizable, Rorschach also performs tasks that other require manual execution including creating a Domain Group Policy (GPO).

The security researchers stated that Rorschach ransomware was the fastest encrypting malware due to its capability to implement itself using several methods.

Instead of the commonly used methods, the report revealed that the Rorschach ransomware was deployed using DLL side-loading of Palo Alto Network’s Cortex XDR Dump Service Tool, a signed commercial security product. This points at a new approach taken by cybercriminals to evade detection.

Fastest and one of the most sophisticated ransomware

Sergey Shykevich, Threat Intelligence Group Manager at Check Point Research highlighted how the technically distinct features in Rorschach ransomware taken from different ransomware families make it different.

Just as a psychological Rorschach test looks different to each person, this new type of ransomware has high levels of technically distinct features taken from different ransomware families – making it special and different from other ransomware families,”  Shykevich told The Cyber Express.

“This is the fastest and one of the most sophisticated ransomware we have seen so far. It speaks to the rapidly changing nature of cyber attacks and the need for companies to deploy a prevention-first solution that can stop Rorschach from encrypting their data,” he added.

Rorschach ransomware explained

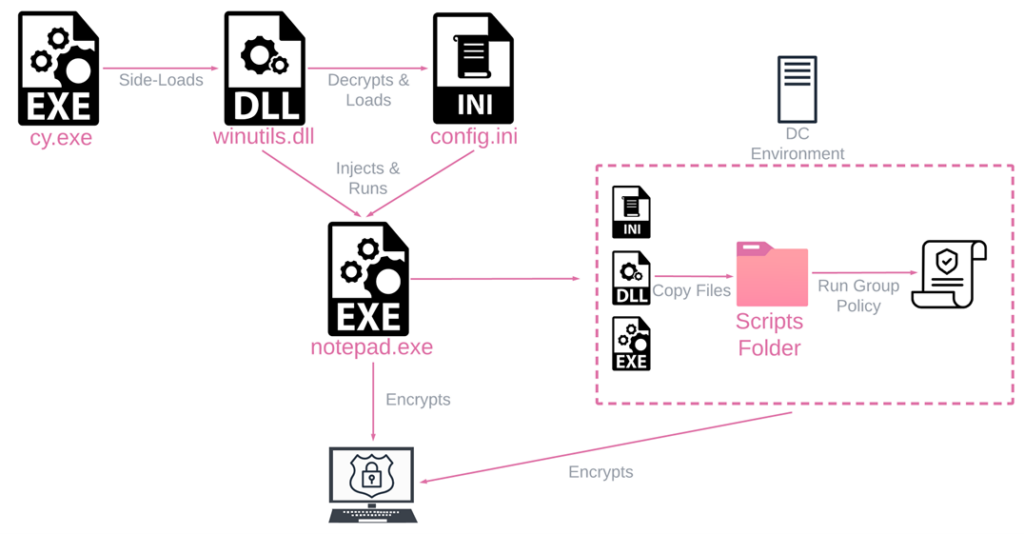
The partly autonomous Rorschach ransomware was found spreading upon execution on a Domain Controller that moves laterally on other machines within the domain.
Rorschach Ransomware

Execution of the Rorschach ransomware (Photo: Check Point)

The Rorschach ransomware holds three files. Cy.exe to side-load winutils.dll, winutils.dll which is its loader that decrypts the files, and config.ini which holds the logic and configuration.

Rorschach ransomware was loaded using a DLL side-loading attack of a Cortex XDR Dump Service Tool which is not commonly used for ransomware.

This suggests that developers of the Rorschach ransomware were attempting to devise a sophisticated tool that evades detection as it is a signed security product that could confuse the victim and experts.

A DLL side-loading attack starts by searching in Windows and then employing a legitimate application to execute the payload. It helps in maintaining persistence, and evading detection to some extent.

Encryption details of the Rorschach ransomware

The hybrid-cryptography encryption scheme of the Rorschach ransomware targets specific files directed by the hacker. It generates a per-victim private key in the form of cryptographically random bytes using the WinAPI CryptGenRandom.

  1. The Rorschach injector was protected with UPX-style packing which depends on manual unpacking.
  2. Rorschach injects into notepad.exe while being guarded by VMProtect which obfuscates its coding.
  3. Rorschach payload makes syscall or direct system calls which are unlike most ransomware however is found in other malware. It finds the syscall numbers for NT APIs, stores them in a table, and calls a stub routine. This obfuscated process further helps it in evading detection.
  4. Its hardcoded configuration with built-in options was obfuscated and was accessible only through reverse engineering.
  5. Some arguments of the Rorschach ransomware were -nomail that would skip creating a ransom note, -at that would set a trigger time slot, -nobk to keep the device wallpaper as is, and -path for encrypting selected paths.

The extra speed of encryption by the Rorschach ransomware is attributed to the implementation of threat scheduling using I/O completion ports.

It was concluded after several red-teaming efforts that while LockBit v.3 took 7 minutes, Rorschach ransomware took approximately 4 minutes and 30 seconds to encrypt files.

Steps followed before encryption

The two system checks followed by the payload before encrypting were GetSystemDefaultUILanguage and GetUserDefaultUILanguage.

The checks searched for the language set by the user. Rorschach ransomware would cease if the language was used by CIS countries. Some of them were :

  1. Armenian
  2. Georgian
  3. Russian
  4. Ukrainian
  5. Belarusian

Similarities between the Rorschach and other ransomware

The Rorschach ransomware has not been associated with a cybercriminal group so far. However, several similarities have been found between Rorschach and other ransomware.

Rorschach Ransomware
The report noted that the ransomware note sent out to the victim was similarly to Yanluowang ransomware notes. However, other variants dropped a note similar to that of DarkSide ransomware notes.

The details of the ransom note found a resemblance to the ransom notes by Yanluowang and DarkSide.

“The ransomware note sent out to the victim was formatted similarly to Yanluowang ransomware notes, although other variants dropped a note that more closely resembled DarkSide ransomware notes (causing some to mistakenly refer to it as DarkSide),” stated the report.

The autonomous execution of the Rorschach ransomware on a Windows domain controller had similarities to that of LockBit 2.0 ransomware.

The hybrid-cryptography scheme of Rorschach bore similarities with Babuk ransomware. It is suspected that the coding for the same along with that of stopping specific processes was taken from Babuk.

Moreover, LockBit’s Russian language used for lists to stop the malware was seen in Rorschach ransomware as well.

The Rorschach personality test

The name Rorschach, researchers reckoned bore semblance to the Rorschach psychological test which involves connecting dots using interpretations and algorithms.

“Each person who examined the ransomware saw something a little bit different, prompting us to name it after the famous psychological test – Rorschach Ransomware,” stated the report.

Share this:

  • Share on LinkedIn (Opens in new window) LinkedIn
  • Share on Reddit (Opens in new window) Reddit
  • Share on X (Opens in new window) X
  • Share on Facebook (Opens in new window) Facebook
  • More
  • Email a link to a friend (Opens in new window) Email
  • Share on WhatsApp (Opens in new window) WhatsApp

Related

Tags: Check Point Researchfastest encryptionnew ransomwareRorschach ransomwareThe Cyber ExpressThe Cyber Express News
Previous Post

LockBit Claims the Olympia Community Unified School District Cyberattack

Next Post

Hard Times for Diamonds: ALPHV Ransomware Hits De Beers Sightholder Dalumi Group

Next Post
Dalumi Group cyber attack

Hard Times for Diamonds: ALPHV Ransomware Hits De Beers Sightholder Dalumi Group

Q1 2026 Threat Reports

❮ ❯
Cyble-Vision


Follow Us On Google News

Categories

  • Privacy Statement
  • Terms of Use
  • Write For Us

© 2026 The Cyber Express - Cybersecurity News and Magazine.

Welcome Back!

Login to your account below

Forgotten Password?

Retrieve your password

Please enter your username or email address to reset your password.

Log In

Add New Playlist

No Result
View All Result
  • Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board

© 2026 The Cyber Express - Cybersecurity News and Magazine.

-
00:00
00:00

Queue

Update Required Flash plugin
-
00:00
00:00



