










• About Us
  • Contact Us
  • Editorial Calendar
  • Careers
  • The Cyber Express by Cyble Vulnerability Disclosure Policy
  • Cyble Trust Portal
The Cyber Express
  • MagazineDownload
  • Firewall Daily
    • All
    • Bug Bounty & Rewards
    • Dark Web News
    • Data Breach News
    • Hacker News
    • Ransomware News
    • Vulnerabilities
    ASD Cyber Threat Report

    Australian Data Breach Incidents Up 66% as AI Sharpens Scams

    INJ3CTOR3

    INJ3CTOR3 Malware Steals FreePBX Credentials, Enabling Toll Fraud After Cleanup

    Discoverable Servers

    Discord to Let Google Index Public Server Messages, Raising Privacy Concerns

    Columbia University cyberattack

    Columbia University Settles $16.1M Data Breach Lawsuit After 2025 Cyberattack

    GMO Internet

    GMO Internet Compensates Users as Cyberattacks Hit Japanese Companies

    cybercrime ring

    South Korea Police Dismantle AI-Driven Cybercrime Ring That Hit 90 Companies

    weekly roundup October 23

    The Cyber Express Weekly Roundup: PHP2Shell Knocks Wikipedia Offline, ASD Retires the Essential Eight and More

    Government impersonation scheme

    Fake Reviews, Deceptive Ads: FTC Targets Alleged Passport Scam

    Operation Serengeti III

    INTERPOL’s Operation Serengeti III Disrupts 10,909 Malicious Networks

    Trending Tags

    • blackbyte ransomware
    • Ransomware
    • lapsus$ ransomware
    • Apple
    • Apple vulnerability
  • Essentials
    • All
    • Compliance
    • Governance
    • Policy Updates
    • Regulations
    ASD Essentials

    The Essential Eight Is Being Replaced: What Australian Organisations Need to Know

    SICW 2026

    AI Is Now Fighting on Both Sides of the Cyber War, Singapore Warns

    Morocco cybersecurity strategy

    Morocco Flags AI Threats, Prioritizes Critical Infrastructure Defense

    European Police Chiefs Convention 2026

    Europe’s Police Chiefs Face Growing Threat of AI-Driven Crime

    AI service security

    Hackers Are Stealing AI Keys. The Cost Can Reach $600,000

    AI security risks

    Sam Altman at UN Security Council: 6 AI Security Risks the World Cannot Ignore

    AI-enabled cyber attacks

    AI Gives Hackers an Edge Defenders Still Can’t Match, NCSC Warns

    Fraudulent SIM cards

    India’s DoT Warns Citizens Over SIM Fraud and IMEI Tampering

    EU cybersecurity incidents

    EU Cybersecurity Response Hampered by Critical Information Gaps

    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
    • All
    • How to
    • What is
    Infostealer Intelligence

    The 2026 Infostealer Intelligence Shortlist: Top 10 Vendors Security Teams Should Know

    Google Chrome

    How to Remove Saved Passwords From Google Chrome (And Why You Should)

    DPDP Rules, Cyble, DPDP Act, Cyble Vantage

    How Cyble’s Front-Row Vantage Can Help You in Complying to India’s DPDP Act

    Cybersecurity Countries

    The Top 8 Countries Leading the Cyber Defense Race in 2025

    link building

    The Link Building Secrets Your Competitors Don’t Want You to Know

    Supply Chain Attack

    Supply Chain Resilience and Physical Security: Lessons for 2025

    Healthcare cybersecurity trends of 2024

    Healthcare Cybersecurity: 2024 Was Tough, 2025 May Be Better

    CEO's Guide to Take-Down Services

    Shield Your Organization: CEO’s Perspective on Take-Down Services

    Azure sign-in Microsoft

    Microsoft Announces Mandatory MFA for Azure Sign-ins to Bolster Cloud Defenses

  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • All
    • Appointments
    • Budgets
    • Mergers & Aquisitions
    • Partnerships
    • Press Release
    • Startups
    Kerala Police Signs MoU With Cyble

    Kerala Police Signs MoU With Cyble to Use Threat Intelligence in Cybercrime Probes

    Gemini 4 Argon

    Gemini 4 Argon Restricted Over Cybersecurity Misuse Risks

    weekly roundup September 18 2026

    The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

    threat intelligence

    Cyble, UAE Cyber Security Council Unite Against Rising Cyber Threats

    Ukraine cybersecurity

    Zelensky Appoints Ihor Klymenko to Lead Ukraine’s Cybersecurity Center

    UK cyberattack rate

    UK Small Firms Bear Brunt of Rising Cyberattacks, Hiscox Finds

    Cyber Yodha Campaign

    Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

    UK Ukraine AI partnership

    Britain Gains Access to Ukraine’s ‘Goldmine’ of Battlefield AI Data

    Hims & Hers lawsuit

    FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices

    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
No Result
View All Result
The Cyber Express
No Result
View All Result
Home Firewall Daily

Millions of WordPress Sites at Risk Due to Essential Addons for Elementor Vulnerability

The vulnerability arises from flaws in two key widgets of the Essential Addons plugin: Countdown and Woo Product Carousel.

Ashish Khaitan by Ashish Khaitan
March 28, 2024
in Firewall Daily, Vulnerabilities
0
Essential Addons For Elementor vulnerability
664
SHARES
3.7k
VIEWS
Share on LinkedInShare on Twitter

A new Essential Addons For Elementor vulnerability has been revealed, affecting over 2 million websites utilizing the popular WordPress plugin. Security researchers have flagged Stored Cross-Site Scripting (XSS) vulnerabilities within this plugin, which could potentially pave the way for attackers to inject malicious scripts into WordPress websites.

The vulnerability stems from flaws identified in two integral widgets incorporated within the Essential Addons plugin, namely the Countdown Widget and the Woo Product Carousel Widget. 

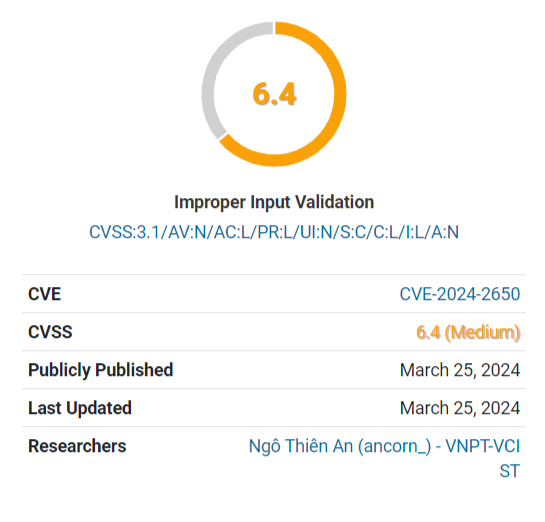
These Elementor vulnerabilities have raised concerns among website owners and developers alike due to their widespread impact. The vulnerability was reported by security researcher Ngô Thiên An (ancorn_) and Wordfence gave it a rating of 6.4 on the vulnerability scale, affecting versions from 5.9.11 and below. 

Decoding the Essential Addons for Elementor Vulnerability

Essential Addons For Elementor serves as an extension to the Elementor WordPress page builder, empowering users to enhance their websites with a ton of features and widgets. However, the recent report of XSS vulnerabilities within this plugin puts millions of users at risk since the plugin has an active installation of 2+ million. 
Essential Addons for Elementor Vulnerability
Source: Wordfence

According to a security advisory published by Wordfence, the vulnerability specifically targets the “Essential Addons for Elementor – Best Elementor Templates, Widgets, Kits & WooCommerce Builders” plugin, up to version 5.9.11. The vulnerability, categorized as “Authenticated (Contributor+) Stored Cross-Site Scripting,” highlights lapses in input sanitization and output escaping mechanisms within the affected widgets.

This vulnerability, assigned a severity score of 6.4 on the Wordfence vulnerability scale, highlights the potential risks associated with improper input validation. Furthermore, the advisory outlines the possibility for authenticated attackers, with contributor-level access or higher, to exploit the vulnerability by injecting arbitrary web scripts into affected pages.

Essential Addons for Elementor Responds to the Vulnerability 

Essential Addons for Elementor Vulnerability
Source: Wordfence

The developers behind Essential Addons for Elementor have addressed the recent vulnerability by releasing a comprehensive security patch. This patch not only tackles the Stored Cross-Site Scripting (XSS) vulnerabilities but also addresses various other flaws within the WordPress plugin.

In their latest patch version 5.9.13, several critical issues have been resolved, including fixes for the EA Table of Contents, ensuring it no longer throws PHP Fatal errors when the Display on option is set to Custom Post Types. Additionally, minor bug fixes and improvements have been implemented to enhance the overall stability and performance of the plugin.

Previous versions, such as 5.9.12 and 5.9.11, also saw fixes to key functionalities. For instance, issues with the EA Pricing Table, EA Advanced Accordion, EA Advanced Tabs, and EA Login Register Form have been addressed, ensuring seamless operation across various features.

Furthermore, compatibility with popular themes and plugins like Fluent Form and Gravity Forms has been improved, minimizing conflicts and enhancing user experience. Alongside security updates, improvements in accessibility support have been made, ensuring that the plugin remains inclusive and user-friendly for all website visitors.

The Stored Cross-Site Scripting (XSS) Pandemic

Stored Cross-Site Scripting (XSS) vulnerabilities pose a threat to website security, enabling attackers to execute malicious scripts within the browsers of unsuspecting visitors. Such attacks could potentially lead to the theft of session cookies, thereby granting unauthorized access to sensitive website functionalities.

XSS vulnerabilities are prevalent in web applications and often result from inadequate input sanitization and output escaping mechanisms. These vulnerabilities have taken a toll on WordPress users recently with many plugins having inadequate security settings, allowing threat actors to exploit the vulnerability and initiate remote code execution. 

According to Wordfence, the Essential Addons for Elementor vulnerability “makes it possible for authenticated attackers, with contributor access or higher, to inject arbitrary web scripts in pages that will execute whenever a user accesses an injected page.”

Rank Math plugin
Source: Wordfence

Previously, Wordfence reported the same vulnerability within the Rank Math plugin. Researcher Ngô Thiên An (ancorn_) uncovered the vulnerability within the Rank Math plugin, which impacts versions up to and including 1.0.214. The vulnerability is associated with the plugin’s management of attributes within the HowTo block.

This lapse in input sanitization and output escaping means that authenticated attackers with contributor-level access or higher can inject arbitrary web scripts. These scripts have the potential to execute whenever a user interacts with the compromised page, posing a risk to user sessions and sensitive data.

Media Disclaimer: This report is based on internal and external research obtained through various means. The information provided is for reference purposes only, and users bear full responsibility for their reliance on it. The Cyber Express assumes no liability for the accuracy or consequences of using this information.

Share this:

  • Share on LinkedIn (Opens in new window) LinkedIn
  • Share on Reddit (Opens in new window) Reddit
  • Share on X (Opens in new window) X
  • Share on Facebook (Opens in new window) Facebook
  • More
  • Email a link to a friend (Opens in new window) Email
  • Share on WhatsApp (Opens in new window) WhatsApp

Related

Tags: Elementor vulnerabilitiesEssential Addons For Elementor vulnerabilityStored Cross-Site ScriptingThe Cyber ExpressThe Cyber Express NewsXSS vulnerabilities
Previous Post

How To Get a Job in Cyber Security? Step By Step Guide

Next Post

The Comeback of WarzoneRAT: Analyzing the Latest Multi-Stage Attacks

Next Post
WarzoneRAT malware

The Comeback of WarzoneRAT: Analyzing the Latest Multi-Stage Attacks

Q1 2026 Threat Reports

❮ ❯
Cyble-Vision


Follow Us On Google News

Latest Cyber News

ASD Cyber Threat Report
Cyber News

Australian Data Breach Incidents Up 66% as AI Sharpens Scams

October 28, 2026
INJ3CTOR3
Firewall Daily

INJ3CTOR3 Malware Steals FreePBX Credentials, Enabling Toll Fraud After Cleanup

October 28, 2026
Discoverable Servers
Firewall Daily

Discord to Let Google Index Public Server Messages, Raising Privacy Concerns

October 28, 2026
Tailscale SSH
Cyber News

Tailscale Investigates Serious SSH Privilege Escalation Issues After Tailworm Report

October 27, 2026

Categories

Web Stories

Do This on Telegram, Your Bank Account Will Become Zero
If You Install the iOS 18 Beta, Your iPhone Could Be Hacked
Cricket World Cup Ticketing Systems Under Cybersecurity
Cyber Threats and Online Ticket Scams During the NBA Finals
Biometric Data Security: Protecting Sensitive Information

About

The Cyber Express

#1 Trending Cybersecurity News and Magazine

The Cyber Express is a handbook for all stakeholders of the internet that provides information security professionals with the latest news, updates and knowledge they need to combat cyber threats.


Contact

For editorial queries: [email protected]

For marketing and Sales: [email protected]


Quick Links

  • About Us
  • Contact Us
  • Editorial Calendar
  • Careers
  • The Cyber Express by Cyble Vulnerability Disclosure Policy
  • Cyble Trust Portal

Our Address

We’re remote friendly, with office locations around the world:

San Francisco, Atlanta, Rome,
Dubai, Mumbai, Bangalore, Hyderabad,  Singapore, Jakarta, Sydney, and Melbourne


Headquarters:

The Cyber Express LLC
10080 North Wolfe Road, Suite SW3-200, Cupertino, CA, US 95014


India Office:

Cyber Express Media Network
HD-021, 4th Floor, C Wing, Building No.4. Nesco IT Park, WE Highway, Goregaon East, Mumbai, Maharashtra, India – 4000063

  • Privacy Statement
  • Terms of Use
  • Write For Us

© 2026 The Cyber Express - Cybersecurity News and Magazine.

Welcome Back!

Login to your account below

Forgotten Password?

Retrieve your password

Please enter your username or email address to reset your password.

Log In

Add New Playlist

No Result
View All Result
  • Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board

© 2026 The Cyber Express - Cybersecurity News and Magazine.

Are you sure want to unlock this post?
Unlock left : 0
Are you sure want to cancel subscription?
-
00:00
00:00

Queue

Update Required Flash plugin
-
00:00
00:00
Do This on Telegram, Your Bank Account Will Become Zero If You Install the iOS 18 Beta, Your iPhone Could Be Hacked Cricket World Cup Ticketing Systems Under Cybersecurity Cyber Threats and Online Ticket Scams During the NBA Finals Biometric Data Security: Protecting Sensitive Information