










• About Us
  • Contact Us
  • Editorial Calendar
  • Careers
  • The Cyber Express by Cyble Vulnerability Disclosure Policy
  • Cyble Trust Portal
The Cyber Express
  • MagazineDownload
  • Firewall Daily
    • All
    • Bug Bounty & Rewards
    • Dark Web News
    • Data Breach News
    • Hacker News
    • Ransomware News
    • Vulnerabilities
    GMO Internet

    GMO Internet Compensates Users as Cyberattacks Hit Japanese Companies

    cybercrime ring

    South Korea Police Dismantle AI-Driven Cybercrime Ring That Hit 90 Companies

    weekly roundup October 23

    The Cyber Express Weekly Roundup: PHP2Shell Knocks Wikipedia Offline, ASD Retires the Essential Eight and More

    Government impersonation scheme

    Fake Reviews, Deceptive Ads: FTC Targets Alleged Passport Scam

    Operation Serengeti III

    INTERPOL’s Operation Serengeti III Disrupts 10,909 Malicious Networks

    AI cyberattack simulations

    Japan AI Cyberattack Simulations Planned as PHP Flaws Disrupt Services

    Yonsei University cyberattack

    Yonsei University Cyberattack Hits 10,000 Students, Months After Sogang Breach

    CVE-2026-109618

    PHP2Shell Patch Rush Takes Wikipedia, Govt Sites Offline

    SafePay ransomware

    FBI, CISA Warn SafePay Ransomware Has Hit 600+ Victims

    Trending Tags

    • blackbyte ransomware
    • Ransomware
    • lapsus$ ransomware
    • Apple
    • Apple vulnerability
  • Essentials
    • All
    • Compliance
    • Governance
    • Policy Updates
    • Regulations
    ASD Essentials

    The Essential Eight Is Being Replaced: What Australian Organisations Need to Know

    SICW 2026

    AI Is Now Fighting on Both Sides of the Cyber War, Singapore Warns

    Morocco cybersecurity strategy

    Morocco Flags AI Threats, Prioritizes Critical Infrastructure Defense

    European Police Chiefs Convention 2026

    Europe’s Police Chiefs Face Growing Threat of AI-Driven Crime

    AI service security

    Hackers Are Stealing AI Keys. The Cost Can Reach $600,000

    AI security risks

    Sam Altman at UN Security Council: 6 AI Security Risks the World Cannot Ignore

    AI-enabled cyber attacks

    AI Gives Hackers an Edge Defenders Still Can’t Match, NCSC Warns

    Fraudulent SIM cards

    India’s DoT Warns Citizens Over SIM Fraud and IMEI Tampering

    EU cybersecurity incidents

    EU Cybersecurity Response Hampered by Critical Information Gaps

    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
    • All
    • How to
    • What is
    Infostealer Intelligence

    The 2026 Infostealer Intelligence Shortlist: Top 10 Vendors Security Teams Should Know

    Google Chrome

    How to Remove Saved Passwords From Google Chrome (And Why You Should)

    DPDP Rules, Cyble, DPDP Act, Cyble Vantage

    How Cyble’s Front-Row Vantage Can Help You in Complying to India’s DPDP Act

    Cybersecurity Countries

    The Top 8 Countries Leading the Cyber Defense Race in 2025

    link building

    The Link Building Secrets Your Competitors Don’t Want You to Know

    Supply Chain Attack

    Supply Chain Resilience and Physical Security: Lessons for 2025

    Healthcare cybersecurity trends of 2024

    Healthcare Cybersecurity: 2024 Was Tough, 2025 May Be Better

    CEO's Guide to Take-Down Services

    Shield Your Organization: CEO’s Perspective on Take-Down Services

    Azure sign-in Microsoft

    Microsoft Announces Mandatory MFA for Azure Sign-ins to Bolster Cloud Defenses

  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • All
    • Appointments
    • Budgets
    • Mergers & Aquisitions
    • Partnerships
    • Press Release
    • Startups
    Kerala Police Signs MoU With Cyble

    Kerala Police Signs MoU With Cyble to Use Threat Intelligence in Cybercrime Probes

    Gemini 4 Argon

    Gemini 4 Argon Restricted Over Cybersecurity Misuse Risks

    weekly roundup September 18 2026

    The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

    threat intelligence

    Cyble, UAE Cyber Security Council Unite Against Rising Cyber Threats

    Ukraine cybersecurity

    Zelensky Appoints Ihor Klymenko to Lead Ukraine’s Cybersecurity Center

    UK cyberattack rate

    UK Small Firms Bear Brunt of Rising Cyberattacks, Hiscox Finds

    Cyber Yodha Campaign

    Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

    UK Ukraine AI partnership

    Britain Gains Access to Ukraine’s ‘Goldmine’ of Battlefield AI Data

    Hims & Hers lawsuit

    FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices

    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
No Result
View All Result
The Cyber Express
No Result
View All Result
Home Cyber News

What CISA KEV Is and Isn’t – and a Tool to Help Guide Security Teams

Paul Shread by Paul Shread
February 6, 2026
in Cyber News, Firewall Daily, Vulnerabilities
0
What CISA KEV Is and Isn’t - and a Tool to Help Guide Security Teams

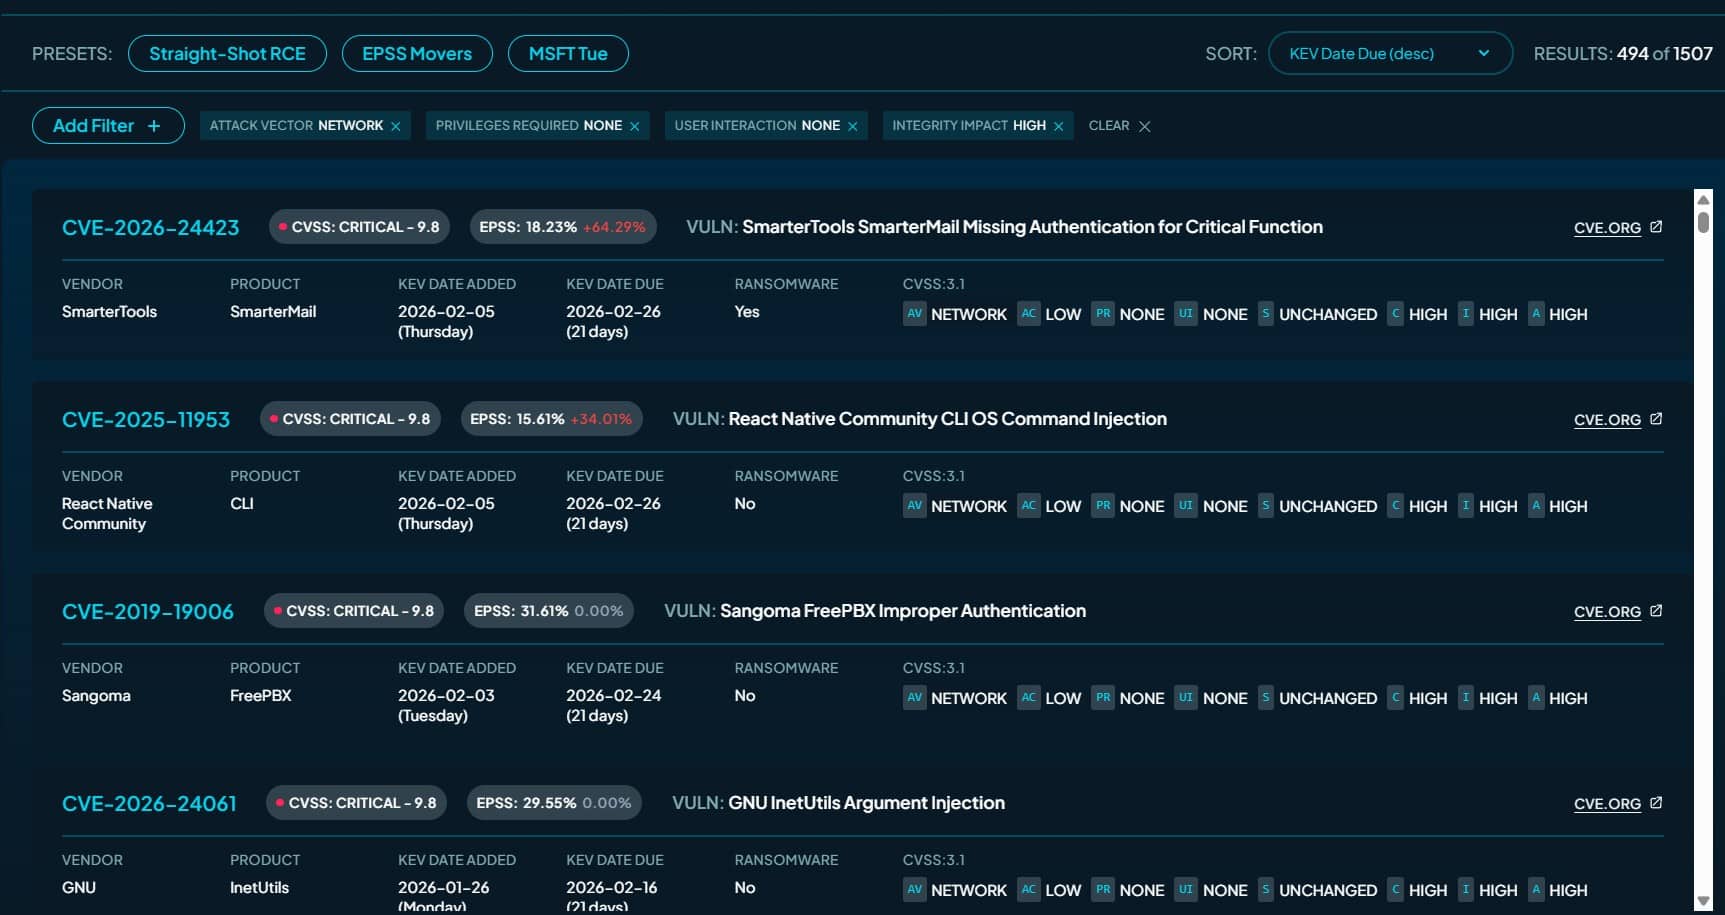
A look at "straight-shot RCE" vulnerabilities (runZero)

627
SHARES
3.5k
VIEWS
Share on LinkedInShare on Twitter

A new paper gives an insider’s perspective into CISA’s Known Exploited Vulnerability catalog – and also offers a free tool to help security teams use the CISA KEV catalog more effectively.

The paper, by former CISA KEV Section Chief and current runZero VP of Security Research Tod Beardsley, applies commonly used enrichment signals like CVSS, EPSS and SSVC, public exploit tooling from Metasploit and Nuclei, MITRE ATT&CK mappings, and “time-sequenced relationships” to help security teams prioritize vulnerabilities based on urgency.

The paper’s findings led to the development of KEV Collider, a web application and dataset “that encourages readers to explore, recombine, and validate KEV enrichment data to better leverage the KEV in their daily operations,” the paper said.

One interesting finding in the paper is that only 32% of CISA KEV vulnerabilities are “immediately exploitable for initial access.”

CISA KEV Is Not a List of the Worst Vulnerabilities

CISA KEV is not a list of the worst vulnerabilities, and the criteria for inclusion in the KEV catalog is perhaps surprisingly narrow.

“The KEV is often misunderstood as a government-curated list of the most severe vulnerabilities ever discovered, or as a catalog of hyper-critical remote code execution flaws actively being used by foreign adversaries against U.S. government systems,” the paper said. “This casual interpretation is incorrect on several counts. While KEV-listed vulnerabilities do represent confirmed exploitation, the catalog exists primarily as an operational prioritization tool rather than as a comprehensive inventory of exploited vulnerabilities.”

Inclusion in the KEV Catalog is limited to vulnerabilities that meet four conditions:

  • The vulnerability must have an assigned Common Vulnerabilities and Exposures (CVE) identifier.
  • There must be a reasonable mitigation. “This means that vulnerabilities with no realistic path to mitigation will not reach the KEV,” the paper said. The lack of a straightforward fix has kept CVE-2022-21894, aka “BlackLotus,” off the list even though the NSA has provided mitigation guidance.
  • There must be evidence of exploitation. “This exploitation must be observed by CISA, either directly or through trusted reporting channels,” the paper said.
  • The vulnerability must be relevant to the U.S. Federal Civilian Executive Branch (FCEB).

CISA KEV is not the only list of known exploited vulnerabilities, the paper said. Another is the VulnCheck KEV, which is three times bigger than CISA KEV. “It often adds vulnerabilities to its KEV in closer-to-real-time as exploitation evidence surfaces, sometimes beating the CISA KEV as first to publish exploitation notifications,” the paper said – and would also be an interesting place to apply the paper’s criteria.

CISA KEV isn’t a list of the most severe vulnerabilities: “the vulnerabilities there are not all unauthenticated, remotely exploitable, initial intrusion vulnerabilities,” the paper said.

Looking at just the last 12 vulnerabilities added to the KEV catalog in December, only four met the criteria for a “straight shot RCE bug.” Those criteria are:

  • Access Vector of “Network” (as opposed to “Adjacent,” “Local,” or “Physical”)
  • Privileges Required of “None” (as opposed to “Low” or “High”)
  • User Interaction of “None” (as opposed to “Required”)
  • Integrity Impact of “High” (as opposed to “None” or “Low”)

“These are the vulnerabilities that listen on an internet socket, don’t require a login, don’t require the victim to act, and the attacker ends up with total control over the affected system,” the paper said.

Interestingly, the four straight-shot RCE vulnerabilities are all rated Critical, while the rest are rated High or Medium.

Out of 1,488 KEV vulnerabilities as of January 14, 2026, only 483, or 32%, “are useful for immediate initial access,” the paper said. Using the Straight-Shot RCE filter in KEV Collider, 494 of 1,507 KEV vulnerabilities in the catalog as of Feb. 6 qualify, or 32.7

Looking at EPSS scores suggests that some of the vulnerabilities have a low probability of being exploited again in the future. There are 545 KEV vulnerabilities with very high EPSS scores – and 353 in the sub-10% category.

Examining Metasploit Framework exploits, 464 KEV vulnerabilities were associated with at least one Metasploit module. “This means that just about a third of all KEVs are trivially exploitable today, as Metasploit modules are free, easy to use, and well-understood by attackers and defenders alike,” the paper said.

There were 398 Nuclei templates “suitable for testing KEV vulnerabilities,” and 235 vulnerabilities with both Metasploit and Nuclei exploits.

The paper also looked at the correlation of MITRE ATT&CK mappings with Metasploit and Nuclei exploit development and found that vulnerabilities associated with T1190 (Exploit Public-Facing Application) and T1059 (Command and Scripting Interpreter) “are more likely to attract the attention of public exploit developers.”

Also read: CISA Silently Updates Vulnerabilities Exploited by Ransomware Groups

Perfect Vulnerability Coverage ‘Unrealistic’

The paper noted that “perfect vulnerability coverage is an increasingly unrealistic goal, particularly when organizations are constrained by finite tooling, staffing, or budget. This is even true when the focus is narrowed to merely the CISA KEV catalog.”

“Many KEVs now affect assets that are difficult to inventory, difficult to scan, or difficult to patch using conventional enterprise tooling,” and can’t be covered by a single product.

The paper’s goal is to help security practitioners “reason about uncertainty and prioritize effort when full coverage is unattainable. In practice, organizations must decide how to sequence remediation, where to apply detection and monitoring first, and when to escalate resource allocation to meet particularly aggressive deadlines.”

All source JSON files used by the KEV Collider application are available in a public GitHub repository.
Share this:

  • Share on LinkedIn (Opens in new window) LinkedIn
  • Share on Reddit (Opens in new window) Reddit
  • Share on X (Opens in new window) X
  • Share on Facebook (Opens in new window) Facebook
  • More
  • Email a link to a friend (Opens in new window) Email
  • Share on WhatsApp (Opens in new window) WhatsApp

Related

Tags: CISACISA KEVcybersecurityKnown exploited vulnerabilities CISAThe Cyber ExpressThe Cyber Express NewsThreat IntelligenceVulnerabilities
Previous Post

The Cyber Express Weekly Roundup: Global Cybersecurity Incidents and Policy Shifts

Next Post

Illinois Man Charged in Massive Snapchat Hacking Scheme Targeting Hundreds of Women

Next Post
Snapchat hacking investigation

Illinois Man Charged in Massive Snapchat Hacking Scheme Targeting Hundreds of Women

Q1 2026 Threat Reports

❮ ❯
Cyble-Vision


Follow Us On Google News

Latest Cyber News

GMO Internet
Firewall Daily

GMO Internet Compensates Users as Cyberattacks Hit Japanese Companies

October 26, 2026
cybercrime ring
Firewall Daily

South Korea Police Dismantle AI-Driven Cybercrime Ring That Hit 90 Companies

October 26, 2026
weekly roundup October 23
Firewall Daily

The Cyber Express Weekly Roundup: PHP2Shell Knocks Wikipedia Offline, ASD Retires the Essential Eight and More

October 25, 2026
Government impersonation scheme
Firewall Daily

Fake Reviews, Deceptive Ads: FTC Targets Alleged Passport Scam

October 25, 2026

Categories

Web Stories

Do This on Telegram, Your Bank Account Will Become Zero
If You Install the iOS 18 Beta, Your iPhone Could Be Hacked
Cricket World Cup Ticketing Systems Under Cybersecurity
Cyber Threats and Online Ticket Scams During the NBA Finals
Biometric Data Security: Protecting Sensitive Information

About

The Cyber Express

#1 Trending Cybersecurity News and Magazine

The Cyber Express is a handbook for all stakeholders of the internet that provides information security professionals with the latest news, updates and knowledge they need to combat cyber threats.


Contact

For editorial queries: [email protected]

For marketing and Sales: [email protected]


Quick Links

  • About Us
  • Contact Us
  • Editorial Calendar
  • Careers
  • The Cyber Express by Cyble Vulnerability Disclosure Policy
  • Cyble Trust Portal

Our Address

We’re remote friendly, with office locations around the world:

San Francisco, Atlanta, Rome,
Dubai, Mumbai, Bangalore, Hyderabad,  Singapore, Jakarta, Sydney, and Melbourne


Headquarters:

The Cyber Express LLC
10080 North Wolfe Road, Suite SW3-200, Cupertino, CA, US 95014


India Office:

Cyber Express Media Network
HD-021, 4th Floor, C Wing, Building No.4. Nesco IT Park, WE Highway, Goregaon East, Mumbai, Maharashtra, India – 4000063

  • Privacy Statement
  • Terms of Use
  • Write For Us

© 2026 The Cyber Express - Cybersecurity News and Magazine.

Welcome Back!

Login to your account below

Forgotten Password?

Retrieve your password

Please enter your username or email address to reset your password.

Log In

Add New Playlist

No Result
View All Result
  • Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board

© 2026 The Cyber Express - Cybersecurity News and Magazine.

Are you sure want to unlock this post?
Unlock left : 0
Are you sure want to cancel subscription?
-
00:00
00:00

Queue

Update Required Flash plugin
-
00:00
00:00
Do This on Telegram, Your Bank Account Will Become Zero If You Install the iOS 18 Beta, Your iPhone Could Be Hacked Cricket World Cup Ticketing Systems Under Cybersecurity Cyber Threats and Online Ticket Scams During the NBA Finals Biometric Data Security: Protecting Sensitive Information