






























Fake Traffic Challan Texts Are Stealing UPI PINs From Android Users in India
The malware also uses Firebase Remote Config, which lets operators switch command servers and turn features on or off remotely ...

The malware also uses Firebase Remote Config, which lets operators switch command servers and turn features on or off remotely ...
OverlayPhantom Android banking trojan abuses Accessibility Services, phishing overlays, and screen streaming to steal credentials.
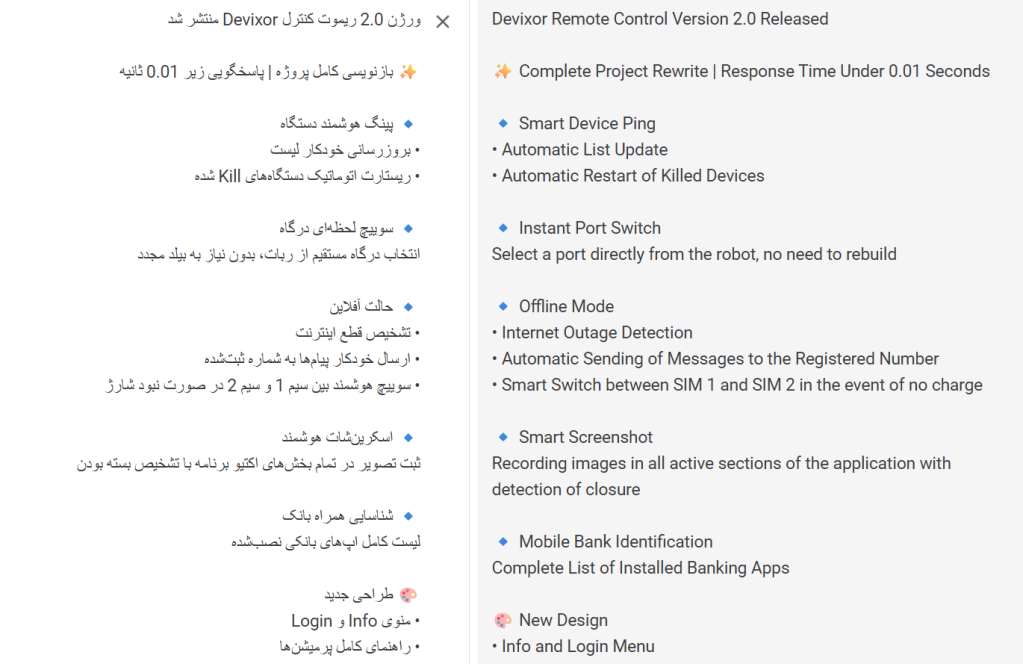
A new Android banking malware can launch ransomware attacks in addition to more typical activities like credential theft and user ...

Security researchers have identified a new Android banking trojan that does much more than steal banking credentials. It can also ...
Cyble uncovered RedHook, a stealthy Android banking trojan targeting Vietnamese users via phishing sites mimicking trusted financial and government entities.

TsarBot is a new Android banking trojan that uses overlay attacks and other tactics to target more than 750 financial ...

Cyble researchers have uncovered a sophisticated new Cerberus Android malware variant dubbed 'ErrorFather' that evaded detection by antivirus tools.
In recent months, cybersecurity analysts have observed a troubling increase in the activity of Golddigger and Gigabud Android banking trojan. Since ...

Researchers have observed a significant increase in attempts to spread the Anatsa Banking Trojan under the veil of legitimate-looking PDF ...

At its core, Antidot masquerades as a legitimate Google Play update application, luring unsuspecting users into its trap.





