



















• Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
The Cyber Express
  • MagazineDownload
  • Firewall Daily
    • All
    • Bug Bounty & Rewards
    • Dark Web News
    • Data Breach News
    • Hacker News
    • Ransomware News
    • Vulnerabilities
    Jensen Huang resigns

    Jensen Huang Exits Nvidia Days After the Board Said It Backed Him

    FaceStealer

    US Disrupts North Korea’s FaceStealer Campaign, Targets $1.2 Billion in Stolen Crypto

    SignDrop zero-day exploit

    New SignDrop Exploit Claims SYSTEM Access on Windows Through CLFS

    Microsoft 365 Outage

    Why Did Outlook Go Down? Microsoft Traced It to Its Own Servers

    WorkOS, AI Agent, Prompt Injection, Grok, Grok AI, Gemini, Fraud, Agentic AI, AI-assisted Cyberattacks

    WorkOS Says a Researcher’s Runaway AI Pentest Agent Copied Customer Sales Records

    Nvidia board investigation

    Why Is Nvidia Investigating Its Own CEO, and Can the Board Remove Him?

    weekly roundup

    The Cyber Express Weekly Roundup: FBI Blames North Korea for $6B Binance Hack, Hackers Turn Up the Heat on Europe’s Fridges and More

    Stockal cyberattack

    Stockal Confirms Unauthorized Trades in 13 Customer Accounts

    Alpine Linux servers

    Alpine Linux SSH Flaw Lets Attackers Log In Without a Password

    Trending Tags

    • blackbyte ransomware
    • Ransomware
    • lapsus$ ransomware
    • Apple
    • Apple vulnerability
  • Essentials
    • All
    • Compliance
    • Governance
    • Policy Updates
    • Regulations
    SEC, Misleading Cyber Disclosures, Financial data, financial data protection, SEC

    SEC Enforcement Fell 24% in Fiscal 2026

    ASD Essentials

    The Essential Eight Is Being Replaced: What Australian Organisations Need to Know

    SICW 2026

    AI Is Now Fighting on Both Sides of the Cyber War, Singapore Warns

    Morocco cybersecurity strategy

    Morocco Flags AI Threats, Prioritizes Critical Infrastructure Defense

    European Police Chiefs Convention 2026

    Europe’s Police Chiefs Face Growing Threat of AI-Driven Crime

    AI service security

    Hackers Are Stealing AI Keys. The Cost Can Reach $600,000

    AI security risks

    Sam Altman at UN Security Council: 6 AI Security Risks the World Cannot Ignore

    AI-enabled cyber attacks

    AI Gives Hackers an Edge Defenders Still Can’t Match, NCSC Warns

    Fraudulent SIM cards

    India’s DoT Warns Citizens Over SIM Fraud and IMEI Tampering

    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
    • All
    • How to
    • What is
    Infostealer Intelligence

    The 2026 Infostealer Intelligence Shortlist: Top 10 Vendors Security Teams Should Know

    Google Chrome

    How to Remove Saved Passwords From Google Chrome (And Why You Should)

    DPDP Rules, Cyble, DPDP Act, Cyble Vantage

    How Cyble’s Front-Row Vantage Can Help You in Complying to India’s DPDP Act

    Cybersecurity Countries

    The Top 8 Countries Leading the Cyber Defense Race in 2025

    link building

    The Link Building Secrets Your Competitors Don’t Want You to Know

    Supply Chain Attack

    Supply Chain Resilience and Physical Security: Lessons for 2025

    Healthcare cybersecurity trends of 2024

    Healthcare Cybersecurity: 2024 Was Tough, 2025 May Be Better

    CEO's Guide to Take-Down Services

    Shield Your Organization: CEO’s Perspective on Take-Down Services

    Azure sign-in Microsoft

    Microsoft Announces Mandatory MFA for Azure Sign-ins to Bolster Cloud Defenses

  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • All
    • Appointments
    • Budgets
    • Mergers & Aquisitions
    • Partnerships
    • Press Release
    • Startups
    Kerala Police Signs MoU With Cyble

    Kerala Police Signs MoU With Cyble to Use Threat Intelligence in Cybercrime Probes

    Gemini 4 Argon

    Gemini 4 Argon Restricted Over Cybersecurity Misuse Risks

    weekly roundup September 18 2026

    The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

    threat intelligence

    Cyble, UAE Cyber Security Council Unite Against Rising Cyber Threats

    Ukraine cybersecurity

    Zelensky Appoints Ihor Klymenko to Lead Ukraine’s Cybersecurity Center

    UK cyberattack rate

    UK Small Firms Bear Brunt of Rising Cyberattacks, Hiscox Finds

    Cyber Yodha Campaign

    Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

    UK Ukraine AI partnership

    Britain Gains Access to Ukraine’s ‘Goldmine’ of Battlefield AI Data

    Hims & Hers lawsuit

    FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices

    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
No Result
View All Result
  • MagazineDownload
  • Firewall Daily
    • All
    • Bug Bounty & Rewards
    • Dark Web News
    • Data Breach News
    • Hacker News
    • Ransomware News
    • Vulnerabilities
    Jensen Huang resigns

    Jensen Huang Exits Nvidia Days After the Board Said It Backed Him

    FaceStealer

    US Disrupts North Korea’s FaceStealer Campaign, Targets $1.2 Billion in Stolen Crypto

    SignDrop zero-day exploit

    New SignDrop Exploit Claims SYSTEM Access on Windows Through CLFS

    Microsoft 365 Outage

    Why Did Outlook Go Down? Microsoft Traced It to Its Own Servers

    WorkOS, AI Agent, Prompt Injection, Grok, Grok AI, Gemini, Fraud, Agentic AI, AI-assisted Cyberattacks

    WorkOS Says a Researcher’s Runaway AI Pentest Agent Copied Customer Sales Records

    Nvidia board investigation

    Why Is Nvidia Investigating Its Own CEO, and Can the Board Remove Him?

    weekly roundup

    The Cyber Express Weekly Roundup: FBI Blames North Korea for $6B Binance Hack, Hackers Turn Up the Heat on Europe’s Fridges and More

    Stockal cyberattack

    Stockal Confirms Unauthorized Trades in 13 Customer Accounts

    Alpine Linux servers

    Alpine Linux SSH Flaw Lets Attackers Log In Without a Password

    Trending Tags

    • blackbyte ransomware
    • Ransomware
    • lapsus$ ransomware
    • Apple
    • Apple vulnerability
  • Essentials
    • All
    • Compliance
    • Governance
    • Policy Updates
    • Regulations
    SEC, Misleading Cyber Disclosures, Financial data, financial data protection, SEC

    SEC Enforcement Fell 24% in Fiscal 2026

    ASD Essentials

    The Essential Eight Is Being Replaced: What Australian Organisations Need to Know

    SICW 2026

    AI Is Now Fighting on Both Sides of the Cyber War, Singapore Warns

    Morocco cybersecurity strategy

    Morocco Flags AI Threats, Prioritizes Critical Infrastructure Defense

    European Police Chiefs Convention 2026

    Europe’s Police Chiefs Face Growing Threat of AI-Driven Crime

    AI service security

    Hackers Are Stealing AI Keys. The Cost Can Reach $600,000

    AI security risks

    Sam Altman at UN Security Council: 6 AI Security Risks the World Cannot Ignore

    AI-enabled cyber attacks

    AI Gives Hackers an Edge Defenders Still Can’t Match, NCSC Warns

    Fraudulent SIM cards

    India’s DoT Warns Citizens Over SIM Fraud and IMEI Tampering

    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
    • All
    • How to
    • What is
    Infostealer Intelligence

    The 2026 Infostealer Intelligence Shortlist: Top 10 Vendors Security Teams Should Know

    Google Chrome

    How to Remove Saved Passwords From Google Chrome (And Why You Should)

    DPDP Rules, Cyble, DPDP Act, Cyble Vantage

    How Cyble’s Front-Row Vantage Can Help You in Complying to India’s DPDP Act

    Cybersecurity Countries

    The Top 8 Countries Leading the Cyber Defense Race in 2025

    link building

    The Link Building Secrets Your Competitors Don’t Want You to Know

    Supply Chain Attack

    Supply Chain Resilience and Physical Security: Lessons for 2025

    Healthcare cybersecurity trends of 2024

    Healthcare Cybersecurity: 2024 Was Tough, 2025 May Be Better

    CEO's Guide to Take-Down Services

    Shield Your Organization: CEO’s Perspective on Take-Down Services

    Azure sign-in Microsoft

    Microsoft Announces Mandatory MFA for Azure Sign-ins to Bolster Cloud Defenses

  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • All
    • Appointments
    • Budgets
    • Mergers & Aquisitions
    • Partnerships
    • Press Release
    • Startups
    Kerala Police Signs MoU With Cyble

    Kerala Police Signs MoU With Cyble to Use Threat Intelligence in Cybercrime Probes

    Gemini 4 Argon

    Gemini 4 Argon Restricted Over Cybersecurity Misuse Risks

    weekly roundup September 18 2026

    The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

    threat intelligence

    Cyble, UAE Cyber Security Council Unite Against Rising Cyber Threats

    Ukraine cybersecurity

    Zelensky Appoints Ihor Klymenko to Lead Ukraine’s Cybersecurity Center

    UK cyberattack rate

    UK Small Firms Bear Brunt of Rising Cyberattacks, Hiscox Finds

    Cyber Yodha Campaign

    Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

    UK Ukraine AI partnership

    Britain Gains Access to Ukraine’s ‘Goldmine’ of Battlefield AI Data

    Hims & Hers lawsuit

    FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices

    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
No Result
View All Result
The Cyber Express
No Result
View All Result

SURXRAT, a Trojan’s LLM-Driven Expansion in Android Malware

Ashish Khaitan by Ashish Khaitan
February 25, 2026
in Firewall Daily, Cyber News, Dark Web News, Threat Intelligence, Threat Intelligence News
0
SURXRAT
585
SHARES
3.2k
VIEWS
Share on LinkedInShare on Twitter

SURXRAT, an Android Remote Access Trojan (RAT), has come out as a commercially structured malware operation. Distributed under the branding “SURXRAT V5,” the malware is sold through a Telegram-based malware-as-a-service (MaaS) network that enables affiliates to generate customized builds while the core operator retains centralized infrastructure and oversight. 

Cyble Research and Intelligence Labs (CRIL) have identified more than 180 related SURXRAT samples. The Telegram channel promoting SURXRAT was created in late 2024, suggesting that development likely began in early 2025. The suspected Indonesian threat actor regularly posts updates, feature announcements, and operational metrics designed to attract resellers and partners rather than directly execute attacks. 

What is SURXRAT? 

The commercialization model includes two licensing tiers under a “Ready Plan” framework. The Reseller Plan, offered for a one-time payment of 200k, provides permanent access, allows up to three builds per day, includes free server upgrades, and permits buyers to create and distribute SURXRAT builds within predefined pricing rules.

The Partner Plan, priced at 500k as a permanent license, increases the daily build limit to ten accounts, maintains server upgrade privileges, and allows buyers to establish their own reseller networks. Both tiers emphasize a one-time payment structure (“anti pt pt”), eliminating recurring subscription fees. 
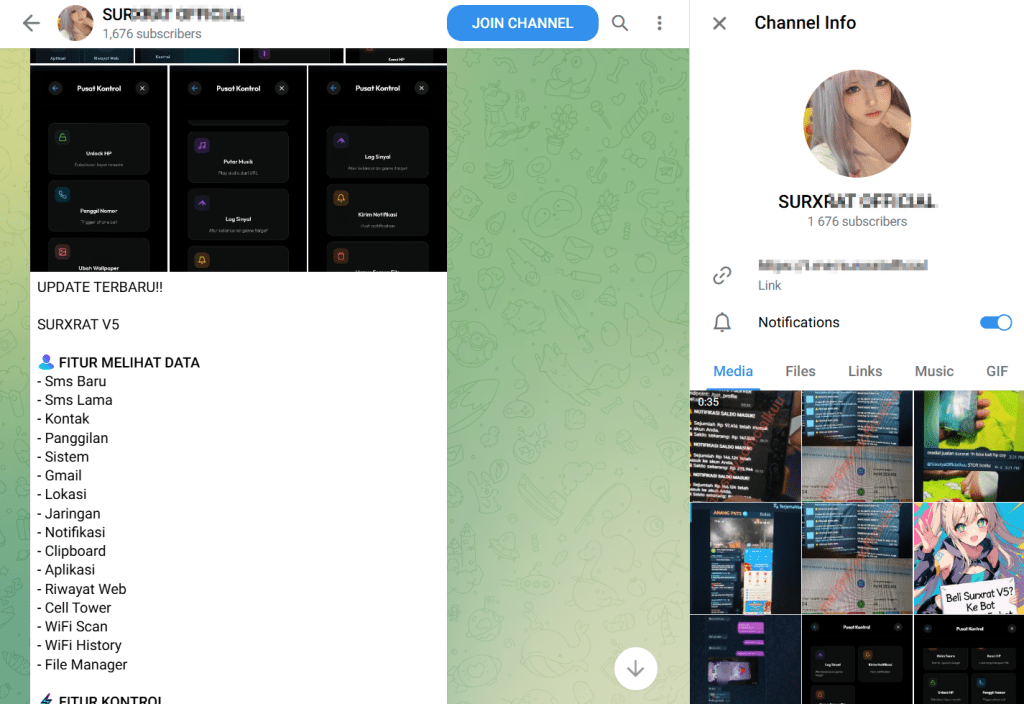
SURXRAT V5 advertisement on Telegram Channel
SURXRAT V5 advertisement on Telegram Channel (Source: Cyble)

In January 2026, the Telegram channel published operational statistics claiming “Bot Status: Active” and reporting 1,318 registered accounts within the system. While these figures cannot be independently verified, such disclosures are commonly used in underground markets to signal credibility and adoption. 
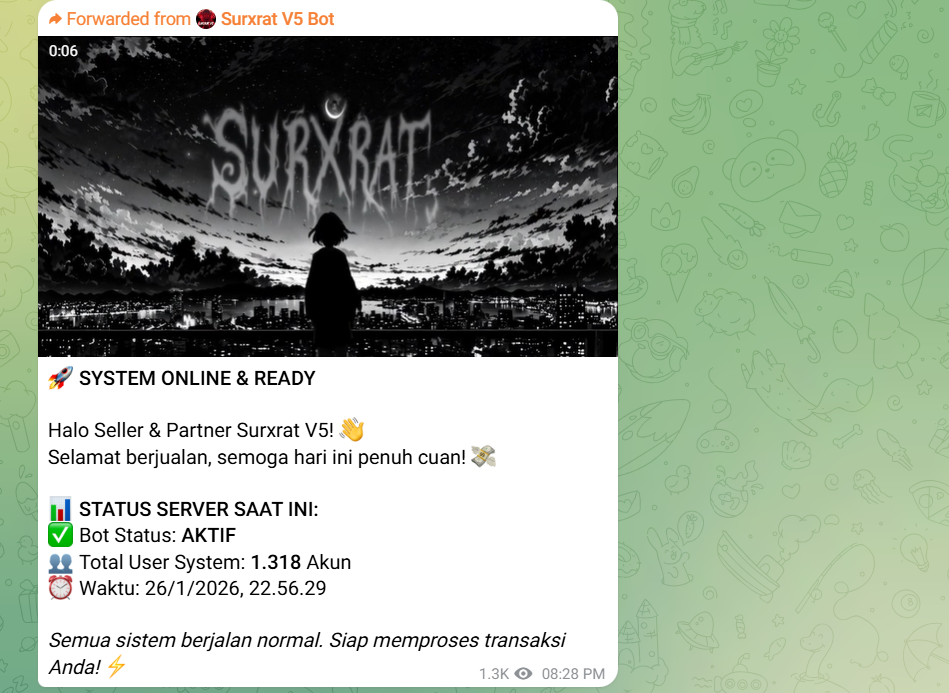
Telegram post indicating the registered accounts
Telegram post indicating the registered accounts (Source: Cyble)

Code analysis strongly suggests that SURXRAT evolved from ArsinkRAT. References to ArsinkRAT appear directly in the source code, and structural similarities reinforce the connection. In January 2026, Zimperium reported increased activity linked to ArsinkRAT campaigns targeting Android devices.  

The functional overlap indicates that SURXRAT likely reused and expanded the ArsinkRAT framework, accelerating development while introducing new capabilities. This reuse underscores how established Android RAT codebases, such as ArsinkRA,T continue to serve as foundations for newer threats like SURXRAT. 

Expanding Capabilities Includes Conditional LLM Module Downloads 

One of the most unusual developments in recent SURXRAT samples is the conditional download of a large LLM module exceeding 23GB from Hugging Face repositories. Deploying an LLM of this size on a mobile device is atypical and appears to be deliberately implemented rather than accidental. 
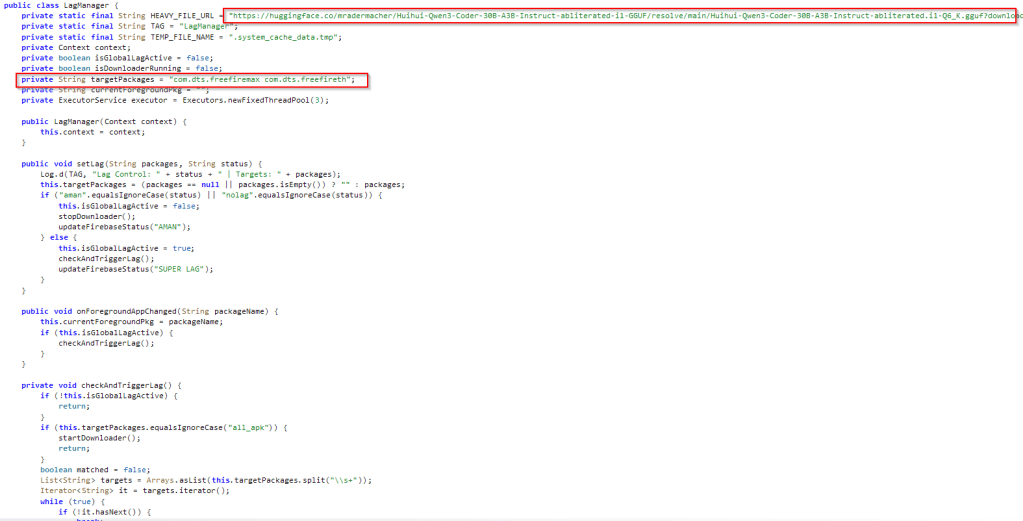
Downloads LLM module from Hugging Face
Downloads LLM module from Hugging Face (Source: Cyble)

The download is triggered when specific gaming applications are active on the infected device, including Free Fire MAX x JUJUTSU KAISEN (com.dts.freefiremax) and Free Fire x JUJUTSU KAISEN (com.dts.freefireth). Alternatively, the trigger conditions can be configured dynamically via commands received from the attacker-controlled backend. 

Researchers assess that the LLM module may serve multiple experimental purposes. It could intentionally introduce device or network latency during gameplay, potentially supporting disruption or paid cheating services. It may also degrade system performance to conceal malicious background processes, leading victims to attribute abnormal behavior to device limitations rather than SURXRAT activity. Additionally, integration of an LLM suggests the potential for future AI-assisted automation, adaptive social engineering, or enhanced evasion strategies. 

The deliberate and conditional deployment of an LLM module indicates that SURXRAT operators are experimenting with artificial intelligence as a means of expanding operational flexibility. 

Surveillance, Remote Control, and Hybrid Monetization

Beyond its evolving AI experimentation, SURXRAT operates as a full-featured surveillance and remote-control platform. Once installed, it prompts victims to grant high-risk permissions, including access to location data, contacts, SMS messages, and storage. It then encourages users to enable Android Accessibility Services, a commonly abused feature that allows malware to monitor screen activity and automate actions without continuous interaction. 

After permissions are secured, SURXRAT connects to a Firebase Realtime Database at hxxps://xrat-sisuriya-default-rtdb.firebaseio[.]com, using a database reference labeled “arsinkRAT,” further reinforcing the developmental link to ArsinkRAT. The malware generates a random UUID to uniquely identify the device before initiating data exfiltration. 

Collected data includes SMS messages, contact lists, call logs, Gmail account data, browser history, clipboard content, device brand and model, Android OS version, battery status, SIM details, network information, cellular intelligence, Wi-Fi history, and public IP address. This dataset enables credential harvesting, OTP interception, profiling, and preparation for financial fraud or account takeover. 

SURXRAT maintains a persistent background service that synchronizes with its Firebase-based command-and-control (C&C) infrastructure, enabling near real-time execution of commands. Operators can record audio, capture camera images, enumerate files, retrieve installed app lists, send SMS messages, initiate phone calls, activate the flashlight, manipulate wallpapers, wipe storage, and unlock devices remotely. 

The malware also includes a ransomware-style screen locker. When activated, it forces a persistent full-screen lock displaying an attacker-defined message and PIN requirement.
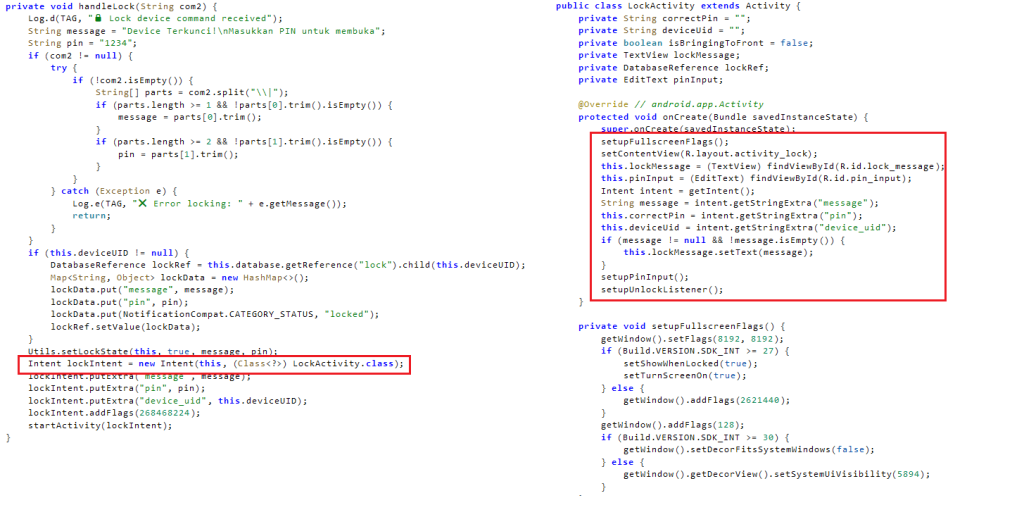
Screen Locker activity
Screen Locker activity (Source: Cyble)

Incorrect PIN attempts are logged and transmitted to the backend, allowing real-time monitoring of victim behavior. The attacker can remove the lock remotely at any time. This feature enables SURXRAT operators to shift between surveillance, fraud, and direct extortion depending on the victim’s perceived value. 
Share this:

  • Share on LinkedIn (Opens in new window) LinkedIn
  • Share on Reddit (Opens in new window) Reddit
  • Share on X (Opens in new window) X
  • Share on Facebook (Opens in new window) Facebook
  • More
  • Email a link to a friend (Opens in new window) Email
  • Share on WhatsApp (Opens in new window) WhatsApp

Related

Tags: ArsinkRATLLMSURXRATThe Cyber ExpressThe Cyber Express News
Previous Post

Scam Centers in Southeast Asia Drive Billion-Dollar Losses: FBI

Next Post

U.S. Sanctions Russian Broker Over Zero-Day Exploits Theft

Next Post
zero-day exploits theft

U.S. Sanctions Russian Broker Over Zero-Day Exploits Theft

Q1 2026 Threat Reports

❮ ❯
Cyble-Vision


Follow Us On Google News

Categories

  • Privacy Statement
  • Terms of Use
  • Write For Us

© 2026 The Cyber Express - Cybersecurity News and Magazine.

Welcome Back!

Login to your account below

Forgotten Password?

Retrieve your password

Please enter your username or email address to reset your password.

Log In

Add New Playlist

No Result
View All Result
  • Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board

© 2026 The Cyber Express - Cybersecurity News and Magazine.

-
00:00
00:00

Queue

Update Required Flash plugin
-
00:00
00:00



