

















• Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
The Cyber Express
  • MagazineDownload
  • Firewall Daily
    • All
    • Bug Bounty & Rewards
    • Dark Web News
    • Data Breach News
    • Hacker News
    • Ransomware News
    • Vulnerabilities
    Polymarket hack

    Polymarket Users Lost Money Without Clicking Anything. Here’s How

    cybersecurity task force

    South Korea President Eyes Cybersecurity Task Force After North Korea-Linked Crypto Heist

    supermarket cyberattack

    Why Would Anyone Hack a Supermarket Freezer? Europe Is Finding Out

    Emergency alert app cyberattacks

    Russia and Ukraine Emergency Apps Hacked With Fake Threat Alerts

    Binance hack

    FBI Blames North Korea for $6B Binance Hack as Recovery Hits 95%

    weekly roundup October 30

    The Cyber Express Weekly Roundup: Binance Hit by $6.3 Billion Security Incident, South Korea Busts AI-Powered Hacking Ring and More

    Binance Data Breach

    Binance Security Incident Affects $6.3 Billion in Crypto Assets, $3 Billion Frozen

    Cyberattacks on Japan

    Three Cyberattack Campaigns Target Japan, Exposing AI’s Growing Role

    Ukrainian ransomware affiliate

    Ransomware Attacks on Hospitals and Businesses Lead to 70-Month Sentence

    Trending Tags

    • blackbyte ransomware
    • Ransomware
    • lapsus$ ransomware
    • Apple
    • Apple vulnerability
  • Essentials
    • All
    • Compliance
    • Governance
    • Policy Updates
    • Regulations
    ASD Essentials

    The Essential Eight Is Being Replaced: What Australian Organisations Need to Know

    SICW 2026

    AI Is Now Fighting on Both Sides of the Cyber War, Singapore Warns

    Morocco cybersecurity strategy

    Morocco Flags AI Threats, Prioritizes Critical Infrastructure Defense

    European Police Chiefs Convention 2026

    Europe’s Police Chiefs Face Growing Threat of AI-Driven Crime

    AI service security

    Hackers Are Stealing AI Keys. The Cost Can Reach $600,000

    AI security risks

    Sam Altman at UN Security Council: 6 AI Security Risks the World Cannot Ignore

    AI-enabled cyber attacks

    AI Gives Hackers an Edge Defenders Still Can’t Match, NCSC Warns

    Fraudulent SIM cards

    India’s DoT Warns Citizens Over SIM Fraud and IMEI Tampering

    EU cybersecurity incidents

    EU Cybersecurity Response Hampered by Critical Information Gaps

    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
    • All
    • How to
    • What is
    Infostealer Intelligence

    The 2026 Infostealer Intelligence Shortlist: Top 10 Vendors Security Teams Should Know

    Google Chrome

    How to Remove Saved Passwords From Google Chrome (And Why You Should)

    DPDP Rules, Cyble, DPDP Act, Cyble Vantage

    How Cyble’s Front-Row Vantage Can Help You in Complying to India’s DPDP Act

    Cybersecurity Countries

    The Top 8 Countries Leading the Cyber Defense Race in 2025

    link building

    The Link Building Secrets Your Competitors Don’t Want You to Know

    Supply Chain Attack

    Supply Chain Resilience and Physical Security: Lessons for 2025

    Healthcare cybersecurity trends of 2024

    Healthcare Cybersecurity: 2024 Was Tough, 2025 May Be Better

    CEO's Guide to Take-Down Services

    Shield Your Organization: CEO’s Perspective on Take-Down Services

    Azure sign-in Microsoft

    Microsoft Announces Mandatory MFA for Azure Sign-ins to Bolster Cloud Defenses

  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • All
    • Appointments
    • Budgets
    • Mergers & Aquisitions
    • Partnerships
    • Press Release
    • Startups
    Kerala Police Signs MoU With Cyble

    Kerala Police Signs MoU With Cyble to Use Threat Intelligence in Cybercrime Probes

    Gemini 4 Argon

    Gemini 4 Argon Restricted Over Cybersecurity Misuse Risks

    weekly roundup September 18 2026

    The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

    threat intelligence

    Cyble, UAE Cyber Security Council Unite Against Rising Cyber Threats

    Ukraine cybersecurity

    Zelensky Appoints Ihor Klymenko to Lead Ukraine’s Cybersecurity Center

    UK cyberattack rate

    UK Small Firms Bear Brunt of Rising Cyberattacks, Hiscox Finds

    Cyber Yodha Campaign

    Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

    UK Ukraine AI partnership

    Britain Gains Access to Ukraine’s ‘Goldmine’ of Battlefield AI Data

    Hims & Hers lawsuit

    FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices

    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
No Result
View All Result
  • MagazineDownload
  • Firewall Daily
    • All
    • Bug Bounty & Rewards
    • Dark Web News
    • Data Breach News
    • Hacker News
    • Ransomware News
    • Vulnerabilities
    Polymarket hack

    Polymarket Users Lost Money Without Clicking Anything. Here’s How

    cybersecurity task force

    South Korea President Eyes Cybersecurity Task Force After North Korea-Linked Crypto Heist

    supermarket cyberattack

    Why Would Anyone Hack a Supermarket Freezer? Europe Is Finding Out

    Emergency alert app cyberattacks

    Russia and Ukraine Emergency Apps Hacked With Fake Threat Alerts

    Binance hack

    FBI Blames North Korea for $6B Binance Hack as Recovery Hits 95%

    weekly roundup October 30

    The Cyber Express Weekly Roundup: Binance Hit by $6.3 Billion Security Incident, South Korea Busts AI-Powered Hacking Ring and More

    Binance Data Breach

    Binance Security Incident Affects $6.3 Billion in Crypto Assets, $3 Billion Frozen

    Cyberattacks on Japan

    Three Cyberattack Campaigns Target Japan, Exposing AI’s Growing Role

    Ukrainian ransomware affiliate

    Ransomware Attacks on Hospitals and Businesses Lead to 70-Month Sentence

    Trending Tags

    • blackbyte ransomware
    • Ransomware
    • lapsus$ ransomware
    • Apple
    • Apple vulnerability
  • Essentials
    • All
    • Compliance
    • Governance
    • Policy Updates
    • Regulations
    ASD Essentials

    The Essential Eight Is Being Replaced: What Australian Organisations Need to Know

    SICW 2026

    AI Is Now Fighting on Both Sides of the Cyber War, Singapore Warns

    Morocco cybersecurity strategy

    Morocco Flags AI Threats, Prioritizes Critical Infrastructure Defense

    European Police Chiefs Convention 2026

    Europe’s Police Chiefs Face Growing Threat of AI-Driven Crime

    AI service security

    Hackers Are Stealing AI Keys. The Cost Can Reach $600,000

    AI security risks

    Sam Altman at UN Security Council: 6 AI Security Risks the World Cannot Ignore

    AI-enabled cyber attacks

    AI Gives Hackers an Edge Defenders Still Can’t Match, NCSC Warns

    Fraudulent SIM cards

    India’s DoT Warns Citizens Over SIM Fraud and IMEI Tampering

    EU cybersecurity incidents

    EU Cybersecurity Response Hampered by Critical Information Gaps

    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
    • All
    • How to
    • What is
    Infostealer Intelligence

    The 2026 Infostealer Intelligence Shortlist: Top 10 Vendors Security Teams Should Know

    Google Chrome

    How to Remove Saved Passwords From Google Chrome (And Why You Should)

    DPDP Rules, Cyble, DPDP Act, Cyble Vantage

    How Cyble’s Front-Row Vantage Can Help You in Complying to India’s DPDP Act

    Cybersecurity Countries

    The Top 8 Countries Leading the Cyber Defense Race in 2025

    link building

    The Link Building Secrets Your Competitors Don’t Want You to Know

    Supply Chain Attack

    Supply Chain Resilience and Physical Security: Lessons for 2025

    Healthcare cybersecurity trends of 2024

    Healthcare Cybersecurity: 2024 Was Tough, 2025 May Be Better

    CEO's Guide to Take-Down Services

    Shield Your Organization: CEO’s Perspective on Take-Down Services

    Azure sign-in Microsoft

    Microsoft Announces Mandatory MFA for Azure Sign-ins to Bolster Cloud Defenses

  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • All
    • Appointments
    • Budgets
    • Mergers & Aquisitions
    • Partnerships
    • Press Release
    • Startups
    Kerala Police Signs MoU With Cyble

    Kerala Police Signs MoU With Cyble to Use Threat Intelligence in Cybercrime Probes

    Gemini 4 Argon

    Gemini 4 Argon Restricted Over Cybersecurity Misuse Risks

    weekly roundup September 18 2026

    The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

    threat intelligence

    Cyble, UAE Cyber Security Council Unite Against Rising Cyber Threats

    Ukraine cybersecurity

    Zelensky Appoints Ihor Klymenko to Lead Ukraine’s Cybersecurity Center

    UK cyberattack rate

    UK Small Firms Bear Brunt of Rising Cyberattacks, Hiscox Finds

    Cyber Yodha Campaign

    Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

    UK Ukraine AI partnership

    Britain Gains Access to Ukraine’s ‘Goldmine’ of Battlefield AI Data

    Hims & Hers lawsuit

    FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices

    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
No Result
View All Result
The Cyber Express
No Result
View All Result

Stolen VPN Credentials Most Common Ransomware Attack Vector

Paul Shread by Paul Shread
January 9, 2026
in Cyber News, Firewall Daily
0
Stolen VPN Credentials Most Common Ransomware Attack Vector

Credit: Anete Lusina/Pexels

585
SHARES
3.2k
VIEWS
Share on LinkedInShare on Twitter

Compromised VPN credentials are the most common initial access vector for ransomware attacks, according to a new report.

Nearly half of ransomware attacks in the third quarter abused compromised VPN credentials as the initial access point, according to research from Beazley Security, the cybersecurity arm of Beazley Insurance.

Nearly a quarter of initial access attacks came from external service exploitation, while remote desktop service (RDS) credential compromises, supply chain attacks and social engineering accounted for 6% each (chart below).
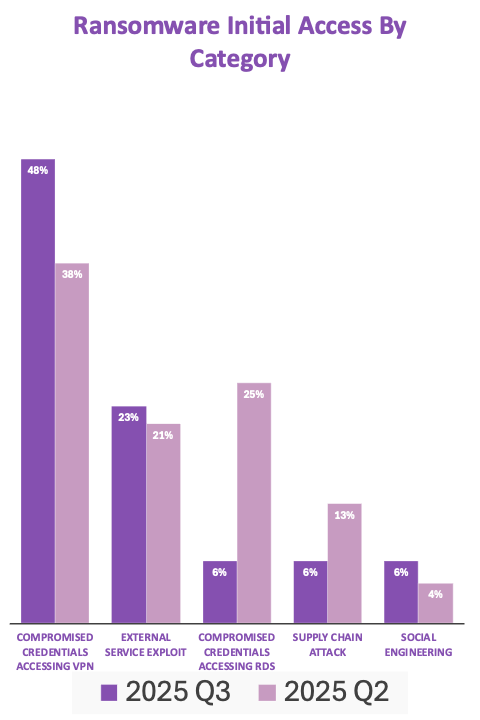
Stolen VPN Credentials Most Common Ransomware Attack Vector
Initial access vectors in ransomware attacks (Beazley Security)

“This trend underscores the importance of ensuring that multifactor authentication (MFA) is configured and protecting remote access solutions and that security teams maintain awareness and compensating controls for any accounts where MFA exceptions have been put in place,” the report said.

In addition to the critical need for MFA, the report also underscores the importance of dark web monitoring services  for leaked credentials, which are often a precursor to much bigger cyberattacks.

SonicWall Compromises Led Attacks on VPN Credentials

A “prolonged campaign” targeting SonicWall devices by the Akira ransomware group was responsible for some of the 10-point increase in the percentage of VPN attacks. “Adding to SonicWall’s misery this quarter was a significant breach of their cloud service, including sensitive configuration backups of client SonicWall devices,” the report added.

Akira, Qilin and INC were by far the most active ransomware groups in the third quarter, Beazley said – and all three exploit VPN and remote desktop credentials.

Akira “typically gains initial access by exploiting weaknesses in VPN appliances and remote services,” the report said. In the third quarter, they used credential stuffing and brute force attacks to target unpatched systems and weak credentials.

Akira accounted for 39% of Beazley Security incident response cases in the third quarter.

Akira “consistently gained access by using valid credentials in credential stuffing attacks against SonicWall SSLVPN services, exploiting weak access controls such as absent MFA and insufficient lockout policies on the device,” the report said.

Qilin’s initial access techniques include phishing emails, malicious attachments, and brute forcing weak credentials or stolen credentials in remote desktop protocol (RDP) and VPN services.

INC Ransomware uses a combination of phishing, credential theft, and exploitation of exposed enterprise appliances for initial access. “Beazley Security responders observed the group leverage valid, compromised credentials to access victim environments via VPN and Remote Desktop,” the report said.

Cisco, Citrix Vulnerabilities, SEO Poisoning Also Exploited

Critical vulnerabilities in Cisco and Citrix NetScaler were also targeted by attackers in the third quarter.

In one campaign, a sophisticated threat actor leveraged CVE-2025-20333 and CVE-2025-20363 in Cisco ASA VPN components to gain unauthorized access into environments, Beazley said. Another campaign targeted a critical SNMP flaw (CVE-2025-20352) in Cisco IOS.‍

Threat actors also targeted Citrix NetScaler vulnerabilities CVE-2025-7775 and CVE-2025-5777. The latter has been dubbed “Citrix Bleed 2” because of similarities to 2023’s “Citrix Bleed” vulnerability (CVE-2023-4966).

A “smaller yet noteworthy subset” of ransomware attacks gained access via search engine optimization (SEO) poisoning attacks and malicious advertisements, used for initial access in some Rhysida ransomware attacks.

“This technique places threat actor-controlled websites at the top of otherwise trusted search results, tricking users into downloading fake productivity and administrative tools such as PDF editors,” the report said. “These tools can be trojanized with various malware payloads, depending on threat actor objectives, and can potentially give threat actors a foothold directly on the endpoint in a network. The attack is effective because it bypasses other traditional social engineering protections like email filters that prevent phishing attacks.”

Share this:

  • Share on LinkedIn (Opens in new window) LinkedIn
  • Share on Reddit (Opens in new window) Reddit
  • Share on X (Opens in new window) X
  • Share on Facebook (Opens in new window) Facebook
  • More
  • Email a link to a friend (Opens in new window) Email
  • Share on WhatsApp (Opens in new window) WhatsApp

Related

Tags: cyberattacksRansomwareransomware attackThe Cyber ExpressThe Cyber Express NewsThreat IntelligenceVPN attacksVulnerabilities
Previous Post

Critical 7-Zip Vulnerability CVE-2025-11001 Prompts NHS Cyber Alert

Next Post

Salesforce Warns that Customer Data May Have Been Accessed Through Gainsight App

Next Post
Salesforce Warns that Customer Data May Have Been Accessed Through Gainsight App

Salesforce Warns that Customer Data May Have Been Accessed Through Gainsight App

Q1 2026 Threat Reports

❮ ❯
Cyble-Vision


Follow Us On Google News

Categories

  • Privacy Statement
  • Terms of Use
  • Write For Us

© 2026 The Cyber Express - Cybersecurity News and Magazine.

Welcome Back!

Login to your account below

Forgotten Password?

Retrieve your password

Please enter your username or email address to reset your password.

Log In

Add New Playlist

No Result
View All Result
  • Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board

© 2026 The Cyber Express - Cybersecurity News and Magazine.

-
00:00
00:00

Queue

Update Required Flash plugin
-
00:00
00:00



