



















• Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
The Cyber Express
  • MagazineDownload
  • Firewall Daily
    • All
    • Bug Bounty & Rewards
    • Dark Web News
    • Data Breach News
    • Hacker News
    • Ransomware News
    • Vulnerabilities
    weekly roundup

    The Cyber Express Weekly Roundup: FBI Blames North Korea for $6B Binance Hack, Hackers Turn Up the Heat on Europe’s Fridges and More

    Stockal cyberattack

    Stockal Confirms Unauthorized Trades in 13 Customer Accounts

    Alpine Linux servers

    Alpine Linux SSH Flaw Lets Attackers Log In Without a Password

    Queens Public Library ransomware attack

    Ransomware Just Took New York’s Queens Library Offline, and It’s Not the First

    Amadeus cybersecurity incident

    Airline Data Breach Widens as Singapore Airlines Reports 46,000 Affected Records

    refrigeration cyberattacks

    After Supermarket Freezers, Hackers Turn Up the Heat on France’s Blood Supply

    university supercomputer hacking

    Two Canadians Accused of Turning US University Supercomputers Into Crypto Miners

    investment fraud

    Europol Seizes 100+ Servers Running Fake Trading Platforms

    UTA cyberattack

    UTA Investigates Suspected Cyberattack After MachForms Service Disruption

    Trending Tags

    • blackbyte ransomware
    • Ransomware
    • lapsus$ ransomware
    • Apple
    • Apple vulnerability
  • Essentials
    • All
    • Compliance
    • Governance
    • Policy Updates
    • Regulations
    ASD Essentials

    The Essential Eight Is Being Replaced: What Australian Organisations Need to Know

    SICW 2026

    AI Is Now Fighting on Both Sides of the Cyber War, Singapore Warns

    Morocco cybersecurity strategy

    Morocco Flags AI Threats, Prioritizes Critical Infrastructure Defense

    European Police Chiefs Convention 2026

    Europe’s Police Chiefs Face Growing Threat of AI-Driven Crime

    AI service security

    Hackers Are Stealing AI Keys. The Cost Can Reach $600,000

    AI security risks

    Sam Altman at UN Security Council: 6 AI Security Risks the World Cannot Ignore

    AI-enabled cyber attacks

    AI Gives Hackers an Edge Defenders Still Can’t Match, NCSC Warns

    Fraudulent SIM cards

    India’s DoT Warns Citizens Over SIM Fraud and IMEI Tampering

    EU cybersecurity incidents

    EU Cybersecurity Response Hampered by Critical Information Gaps

    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
    • All
    • How to
    • What is
    Infostealer Intelligence

    The 2026 Infostealer Intelligence Shortlist: Top 10 Vendors Security Teams Should Know

    Google Chrome

    How to Remove Saved Passwords From Google Chrome (And Why You Should)

    DPDP Rules, Cyble, DPDP Act, Cyble Vantage

    How Cyble’s Front-Row Vantage Can Help You in Complying to India’s DPDP Act

    Cybersecurity Countries

    The Top 8 Countries Leading the Cyber Defense Race in 2025

    link building

    The Link Building Secrets Your Competitors Don’t Want You to Know

    Supply Chain Attack

    Supply Chain Resilience and Physical Security: Lessons for 2025

    Healthcare cybersecurity trends of 2024

    Healthcare Cybersecurity: 2024 Was Tough, 2025 May Be Better

    CEO's Guide to Take-Down Services

    Shield Your Organization: CEO’s Perspective on Take-Down Services

    Azure sign-in Microsoft

    Microsoft Announces Mandatory MFA for Azure Sign-ins to Bolster Cloud Defenses

  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • All
    • Appointments
    • Budgets
    • Mergers & Aquisitions
    • Partnerships
    • Press Release
    • Startups
    Kerala Police Signs MoU With Cyble

    Kerala Police Signs MoU With Cyble to Use Threat Intelligence in Cybercrime Probes

    Gemini 4 Argon

    Gemini 4 Argon Restricted Over Cybersecurity Misuse Risks

    weekly roundup September 18 2026

    The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

    threat intelligence

    Cyble, UAE Cyber Security Council Unite Against Rising Cyber Threats

    Ukraine cybersecurity

    Zelensky Appoints Ihor Klymenko to Lead Ukraine’s Cybersecurity Center

    UK cyberattack rate

    UK Small Firms Bear Brunt of Rising Cyberattacks, Hiscox Finds

    Cyber Yodha Campaign

    Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

    UK Ukraine AI partnership

    Britain Gains Access to Ukraine’s ‘Goldmine’ of Battlefield AI Data

    Hims & Hers lawsuit

    FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices

    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
No Result
View All Result
  • MagazineDownload
  • Firewall Daily
    • All
    • Bug Bounty & Rewards
    • Dark Web News
    • Data Breach News
    • Hacker News
    • Ransomware News
    • Vulnerabilities
    weekly roundup

    The Cyber Express Weekly Roundup: FBI Blames North Korea for $6B Binance Hack, Hackers Turn Up the Heat on Europe’s Fridges and More

    Stockal cyberattack

    Stockal Confirms Unauthorized Trades in 13 Customer Accounts

    Alpine Linux servers

    Alpine Linux SSH Flaw Lets Attackers Log In Without a Password

    Queens Public Library ransomware attack

    Ransomware Just Took New York’s Queens Library Offline, and It’s Not the First

    Amadeus cybersecurity incident

    Airline Data Breach Widens as Singapore Airlines Reports 46,000 Affected Records

    refrigeration cyberattacks

    After Supermarket Freezers, Hackers Turn Up the Heat on France’s Blood Supply

    university supercomputer hacking

    Two Canadians Accused of Turning US University Supercomputers Into Crypto Miners

    investment fraud

    Europol Seizes 100+ Servers Running Fake Trading Platforms

    UTA cyberattack

    UTA Investigates Suspected Cyberattack After MachForms Service Disruption

    Trending Tags

    • blackbyte ransomware
    • Ransomware
    • lapsus$ ransomware
    • Apple
    • Apple vulnerability
  • Essentials
    • All
    • Compliance
    • Governance
    • Policy Updates
    • Regulations
    ASD Essentials

    The Essential Eight Is Being Replaced: What Australian Organisations Need to Know

    SICW 2026

    AI Is Now Fighting on Both Sides of the Cyber War, Singapore Warns

    Morocco cybersecurity strategy

    Morocco Flags AI Threats, Prioritizes Critical Infrastructure Defense

    European Police Chiefs Convention 2026

    Europe’s Police Chiefs Face Growing Threat of AI-Driven Crime

    AI service security

    Hackers Are Stealing AI Keys. The Cost Can Reach $600,000

    AI security risks

    Sam Altman at UN Security Council: 6 AI Security Risks the World Cannot Ignore

    AI-enabled cyber attacks

    AI Gives Hackers an Edge Defenders Still Can’t Match, NCSC Warns

    Fraudulent SIM cards

    India’s DoT Warns Citizens Over SIM Fraud and IMEI Tampering

    EU cybersecurity incidents

    EU Cybersecurity Response Hampered by Critical Information Gaps

    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
    • All
    • How to
    • What is
    Infostealer Intelligence

    The 2026 Infostealer Intelligence Shortlist: Top 10 Vendors Security Teams Should Know

    Google Chrome

    How to Remove Saved Passwords From Google Chrome (And Why You Should)

    DPDP Rules, Cyble, DPDP Act, Cyble Vantage

    How Cyble’s Front-Row Vantage Can Help You in Complying to India’s DPDP Act

    Cybersecurity Countries

    The Top 8 Countries Leading the Cyber Defense Race in 2025

    link building

    The Link Building Secrets Your Competitors Don’t Want You to Know

    Supply Chain Attack

    Supply Chain Resilience and Physical Security: Lessons for 2025

    Healthcare cybersecurity trends of 2024

    Healthcare Cybersecurity: 2024 Was Tough, 2025 May Be Better

    CEO's Guide to Take-Down Services

    Shield Your Organization: CEO’s Perspective on Take-Down Services

    Azure sign-in Microsoft

    Microsoft Announces Mandatory MFA for Azure Sign-ins to Bolster Cloud Defenses

  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • All
    • Appointments
    • Budgets
    • Mergers & Aquisitions
    • Partnerships
    • Press Release
    • Startups
    Kerala Police Signs MoU With Cyble

    Kerala Police Signs MoU With Cyble to Use Threat Intelligence in Cybercrime Probes

    Gemini 4 Argon

    Gemini 4 Argon Restricted Over Cybersecurity Misuse Risks

    weekly roundup September 18 2026

    The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

    threat intelligence

    Cyble, UAE Cyber Security Council Unite Against Rising Cyber Threats

    Ukraine cybersecurity

    Zelensky Appoints Ihor Klymenko to Lead Ukraine’s Cybersecurity Center

    UK cyberattack rate

    UK Small Firms Bear Brunt of Rising Cyberattacks, Hiscox Finds

    Cyber Yodha Campaign

    Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

    UK Ukraine AI partnership

    Britain Gains Access to Ukraine’s ‘Goldmine’ of Battlefield AI Data

    Hims & Hers lawsuit

    FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices

    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
No Result
View All Result
The Cyber Express
No Result
View All Result

Russian APT28 Exploit Zero-Day Hours After Microsoft Discloses Office Vulnerability

Mihir Bagwe by Mihir Bagwe
February 2, 2026
in Vulnerability News, Threat Actors, Threat Intelligence, Vulnerabilities
0
APT28, Russia, Microsoft Office, Word, CERT-UA, Backdoor, SVR Exploiting Unpatched Vulnerabilities, Russia SVR, SVR, Vulnerabilities, Vulnerability Management, Patch Management
585
SHARES
3.2k
VIEWS
Share on LinkedInShare on Twitter

Ukraine’s cyber defenders warn Russian hackers weaponized a Microsoft zero-day within 24 hours of public disclosure, targeting government agencies with malicious documents delivering Covenant framework backdoors.

Russian state-sponsored hacking group APT28 used a critical Microsoft Office zero-day vulnerability, tracked as CVE-2026-21509, in less than a day after the vendor publicly disclosed the flaw, launching targeted attacks against Ukrainian government agencies and European Union institutions.

Ukraine’s Computer Emergency Response Team detected exploitation attempts that began on January 27—just one day after Microsoft published details about CVE-2026-21509.

Microsoft had acknowledged active exploitation when it disclosed the flaw on January 26, but details pertaining to the threat actors were withheld and it is still unclear if it is the same or some other exploitation campaign that the vendor meant. However, the speed at which APT28 deployed customized attacks shows the narrow window defenders have to patch critical vulnerabilities.

Also read: APT28’s Recent Campaign Combined Steganography, Cloud C2 into a Modular Infection Chain

Cyble Annual Threat Landscape Report, Annual Threat Landscape Report, Cyble Annual Threat Landscape Report 2025, Threat Landscape Report 2025, Cyble, Ransomware, Hacktivism, AI attacks, Vulnerabilities, APT, ICS Vulnerabilities

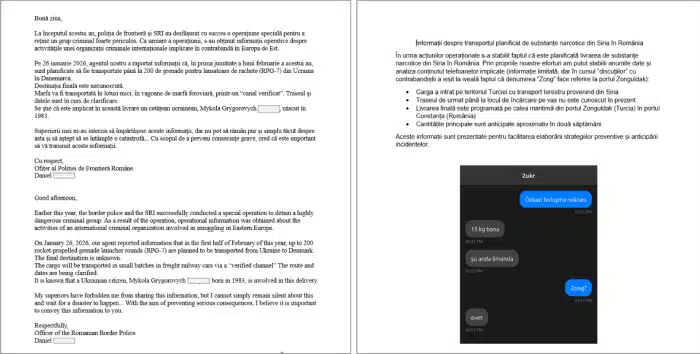
CERT-UA discovered a malicious DOC file titled “Consultation_Topics_Ukraine(Final).doc” containing the CVE-2026-21509 exploit on January 29. Metadata revealed attackers created the document on January 27 at 07:43 UTC. The file masqueraded as materials related to Committee of Permanent Representatives to the European Union consultations on Ukraine’s situation.
APT28, Russia, Microsoft Office, Word, CERT-UA, Backdoor
Word file laced with malware (Source: CERT-UA)

On the same day, attackers impersonated Ukraine’s Ukrhydrometeorological Center, distributing emails with an attached DOC file named “BULLETEN_H.doc” to more than 60 email addresses. Recipients primarily included Ukrainian central executive government agencies, representing a coordinated campaign against critical government infrastructure.

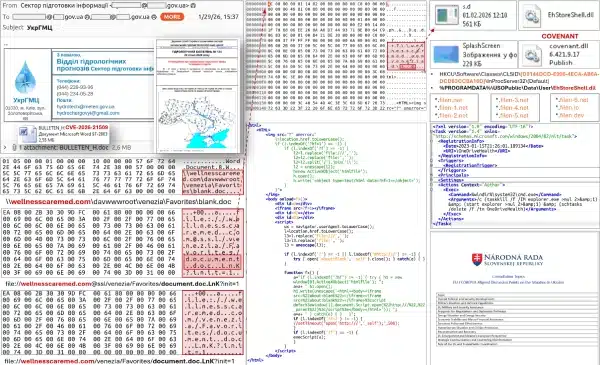
The attack chain begins when victims open malicious documents using Microsoft Office. The exploit establishes network connections to external resources using the WebDAV protocol—a file sharing protocol that extends HTTP to enable collaborative editing. The connection downloads a shortcut file containing program code designed to retrieve and execute additional malicious payloads.
CVE 2026 21509
Exploit chain. (Source CERT-UA)

Successful execution creates a DLL file “EhStoreShell.dll” disguised as a legitimate “Enhanced Storage Shell Extension” library, along with an image file “SplashScreen.png” containing shellcode. Attackers implement COM hijacking by modifying Windows registry values for a specific CLSID identifier, a technique that allows malicious code to execute when legitimate Windows components load.

The malware creates a scheduled task named “OneDriveHealth” that executes periodically. When triggered, the task terminates and relaunches the Windows Explorer process. Because of the COM hijacking modification, Explorer automatically loads the malicious EhStoreShell.dll file, which then executes shellcode from the image file to deploy the Covenant framework on compromised systems.

Covenant is a post-exploitation framework similar to Cobalt Strike that provides attackers persistent command-and-control access. In this campaign, APT28 configured Covenant to use Filen.io, a legitimate cloud storage service, as command-and-control infrastructure. This technique, called living-off-the-land, makes malicious traffic appear legitimate and harder to detect.

CERT-UA discovered three additional malicious documents using similar exploits in late January 2026. Analysis of embedded URL structures and other technical indicators revealed these documents targeted organizations in EU countries. In one case, attackers registered a domain name on January 30, 2026—the same day they deployed it in attacks—demonstrating the operation’s speed and agility.

“It is obvious that in the near future, including due to the inertia of the process or impossibility of users updating the Microsoft Office suite and/or using recommended protection mechanisms, the number of cyberattacks using the described vulnerability will begin to increase,” CERT-UA warned in its advisory.

Microsoft released an emergency fix for CVE-2026-21509, but many organizations struggle to rapidly deploy patches across enterprise environments. The vulnerability affects multiple Microsoft Office products, creating a broad attack surface that threat actors will continue exploiting as long as unpatched systems remain accessible.

Read: Microsoft Releases Emergency Fix for Exploited Office Zero-Day

CERT-UA attributes the campaign to UAC-0001, the agency’s designation for APT28, also known as Fancy Bear or Forest Blizzard. The group operates on behalf of Russia’s GRU military intelligence agency and has conducted extensive operations targeting Ukraine since Russia’s 2022 invasion. APT28 previously exploited Microsoft vulnerabilities within hours of disclosure, demonstrating consistent capability to rapidly weaponize newly discovered flaws.

CERT-UA recommends organizations immediately implement mitigation measures outlined in Microsoft’s advisory, particularly Windows registry modifications that prevent exploitation. The agency specifically urges blocking or monitoring network connections to Filen cloud storage infrastructure, providing lists of domain names and IP addresses in its indicators of compromise section.
Share this:

  • Share on LinkedIn (Opens in new window) LinkedIn
  • Share on Reddit (Opens in new window) Reddit
  • Share on X (Opens in new window) X
  • Share on Facebook (Opens in new window) Facebook
  • More
  • Email a link to a friend (Opens in new window) Email
  • Share on WhatsApp (Opens in new window) WhatsApp

Related

Tags: APT28BackdoorCERT-UAMicrosoft OfficeRussiaWord
Previous Post

Britain and Japan Join Forces on Cybersecurity and Strategic Minerals

Next Post

Benefits of Executive Monitoring Platforms for Business Growth

Next Post
executive monitoring platforms

Benefits of Executive Monitoring Platforms for Business Growth

Q1 2026 Threat Reports

❮ ❯
Cyble-Vision


Follow Us On Google News

Categories

  • Privacy Statement
  • Terms of Use
  • Write For Us

© 2026 The Cyber Express - Cybersecurity News and Magazine.

Welcome Back!

Login to your account below

Forgotten Password?

Retrieve your password

Please enter your username or email address to reset your password.

Log In

Add New Playlist

No Result
View All Result
  • Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board

© 2026 The Cyber Express - Cybersecurity News and Magazine.

-
00:00
00:00

Queue

Update Required Flash plugin
-
00:00
00:00



