
















• Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
The Cyber Express
  • MagazineDownload
  • Firewall Daily
    • All
    • Bug Bounty & Rewards
    • Dark Web News
    • Data Breach News
    • Hacker News
    • Ransomware News
    • Vulnerabilities
    weekly roundup October 30

    The Cyber Express Weekly Roundup: Binance Hit by $6.3 Billion Security Incident, South Korea Busts AI-Powered Hacking Ring and More

    Binance Data Breach

    Binance Security Incident Affects $6.3 Billion in Crypto Assets, $3 Billion Frozen

    Cyberattacks on Japan

    Three Cyberattack Campaigns Target Japan, Exposing AI’s Growing Role

    Ukrainian ransomware affiliate

    Ransomware Attacks on Hospitals and Businesses Lead to 70-Month Sentence

    FBI seizes Virtualine

    FBI Seizes Bulletproof Hosting Domain Linked to Cybercrime

    ASD Cyber Threat Report

    Australian Data Breach Incidents Up 66% as AI Sharpens Scams

    INJ3CTOR3

    INJ3CTOR3 Malware Steals FreePBX Credentials, Enabling Toll Fraud After Cleanup

    Discoverable Servers

    Discord to Let Google Index Public Server Messages, Raising Privacy Concerns

    Columbia University cyberattack

    Columbia University Settles $16.1M Data Breach Lawsuit After 2025 Cyberattack

    Trending Tags

    • blackbyte ransomware
    • Ransomware
    • lapsus$ ransomware
    • Apple
    • Apple vulnerability
  • Essentials
    • All
    • Compliance
    • Governance
    • Policy Updates
    • Regulations
    ASD Essentials

    The Essential Eight Is Being Replaced: What Australian Organisations Need to Know

    SICW 2026

    AI Is Now Fighting on Both Sides of the Cyber War, Singapore Warns

    Morocco cybersecurity strategy

    Morocco Flags AI Threats, Prioritizes Critical Infrastructure Defense

    European Police Chiefs Convention 2026

    Europe’s Police Chiefs Face Growing Threat of AI-Driven Crime

    AI service security

    Hackers Are Stealing AI Keys. The Cost Can Reach $600,000

    AI security risks

    Sam Altman at UN Security Council: 6 AI Security Risks the World Cannot Ignore

    AI-enabled cyber attacks

    AI Gives Hackers an Edge Defenders Still Can’t Match, NCSC Warns

    Fraudulent SIM cards

    India’s DoT Warns Citizens Over SIM Fraud and IMEI Tampering

    EU cybersecurity incidents

    EU Cybersecurity Response Hampered by Critical Information Gaps

    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
    • All
    • How to
    • What is
    Infostealer Intelligence

    The 2026 Infostealer Intelligence Shortlist: Top 10 Vendors Security Teams Should Know

    Google Chrome

    How to Remove Saved Passwords From Google Chrome (And Why You Should)

    DPDP Rules, Cyble, DPDP Act, Cyble Vantage

    How Cyble’s Front-Row Vantage Can Help You in Complying to India’s DPDP Act

    Cybersecurity Countries

    The Top 8 Countries Leading the Cyber Defense Race in 2025

    link building

    The Link Building Secrets Your Competitors Don’t Want You to Know

    Supply Chain Attack

    Supply Chain Resilience and Physical Security: Lessons for 2025

    Healthcare cybersecurity trends of 2024

    Healthcare Cybersecurity: 2024 Was Tough, 2025 May Be Better

    CEO's Guide to Take-Down Services

    Shield Your Organization: CEO’s Perspective on Take-Down Services

    Azure sign-in Microsoft

    Microsoft Announces Mandatory MFA for Azure Sign-ins to Bolster Cloud Defenses

  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • All
    • Appointments
    • Budgets
    • Mergers & Aquisitions
    • Partnerships
    • Press Release
    • Startups
    Kerala Police Signs MoU With Cyble

    Kerala Police Signs MoU With Cyble to Use Threat Intelligence in Cybercrime Probes

    Gemini 4 Argon

    Gemini 4 Argon Restricted Over Cybersecurity Misuse Risks

    weekly roundup September 18 2026

    The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

    threat intelligence

    Cyble, UAE Cyber Security Council Unite Against Rising Cyber Threats

    Ukraine cybersecurity

    Zelensky Appoints Ihor Klymenko to Lead Ukraine’s Cybersecurity Center

    UK cyberattack rate

    UK Small Firms Bear Brunt of Rising Cyberattacks, Hiscox Finds

    Cyber Yodha Campaign

    Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

    UK Ukraine AI partnership

    Britain Gains Access to Ukraine’s ‘Goldmine’ of Battlefield AI Data

    Hims & Hers lawsuit

    FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices

    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
No Result
View All Result
The Cyber Express
No Result
View All Result

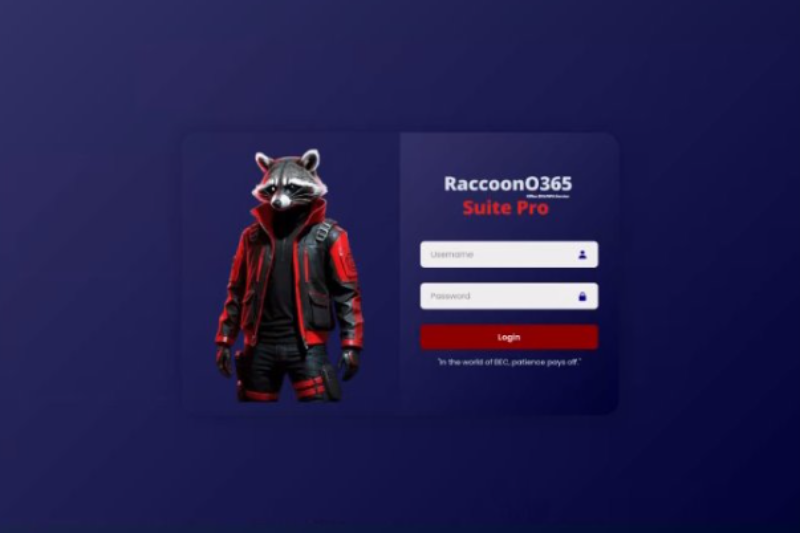
Microsoft, Cloudflare Disrupt RaccoonO365 Phishing-as-a-Service Operation Targeting MS 365

Mihir Bagwe by Mihir Bagwe
September 17, 2025
in Cyber News
0
RaccoonO365, Microsoft, Cloudflare

Image Credit: Microsoft

585
SHARES
3.2k
VIEWS
Share on LinkedInShare on Twitter

Microsoft and Cloudflare dealt a major blow against RaccoonO365, a subscription-based phishing-as-a-service (PhaaS) platform that has fueled thousands of credential theft campaigns since mid-2024. In a joint operation announced this week, Microsoft seized 338 domains tied to the network, while Cloudflare moved to dismantle its proxy infrastructure and Worker accounts—actions that together have forced the service offline.

What RaccoonO365 Was Selling

RaccoonO365 wasn’t just another phishing kit—it was a subscription model designed to make phishing almost effortless. By paying for access, customers could instantly deploy polished phishing pages that convincingly imitated Microsoft 365 login portals, HR notices, or tax forms. The service also came with backend infrastructure to handle stolen credentials and session cookies, making it a full end-to-end solution for cybercriminals.

That “as-a-service” element is what made it dangerous. Unlike bespoke phishing campaigns that required technical chops, RaccoonO365’s kits were plug-and-play. Even a novice could subscribe, configure a campaign with pre-made lures, and start harvesting usernames and passwords in minutes. In effect, it turned phishing into a commodity market.

The Global Impact

The numbers tell the story. Since July 2024, RaccoonO365 kits have been used to steal at least 5,000 Microsoft credentials across 94 countries. Campaigns were broad and opportunistic. One of the most significant was a tax-themed phishing wave that targeted over 2,300 U.S. organizations by impersonating tax authorities, Microsoft said. Healthcare was another major vertical. At least 20 U.S. healthcare providers were hit, exposing sensitive patient and corporate data to potential compromise.

The service’s kits also came with technical features that made them harder to detect and take down. Operators built in browser fingerprinting, CAPTCHA challenges, and scripts to block developer tools. Stolen cookies could be replayed to bypass multi-factor authentication, giving attackers persistence inside corporate accounts.

How the Disruption Happened

The takedown was a two-pronged effort. Microsoft, after filing a civil lawsuit in late August, obtained authorization to seize 338 domains directly tied to RaccoonO365. These domains hosted the fake login portals and were essential for tricking victims into handing over credentials.

At the same time, Cloudflare went after the infrastructure that allowed those portals to thrive. By disabling hundreds of Worker accounts and related proxy services, Cloudflare shut down the actor’s ability to mask backend servers and rotate domains. This marked a strategic change in approach: instead of whack-a-mole takedowns of single sites, Cloudflare targeted the backbone that kept the operation agile.

Cloudflare put it bluntly: by raising RaccoonO365’s operational costs, they’ve made the free tier “too expensive” for cybercriminals.

A Familiar Pattern in Cybercrime

The RaccoonO365 takedown echoes past disruptions against other phishing-as-a-service ecosystems. In 2021, researchers exposed BulletProofLink, another subscription-based kit operation that offered custom templates and hosting to customers. In 2023, the 16Shop platform was taken down in a global operation after targeting PayPal, Apple, and Amazon users.

The trend is clear. Phishing has gone professional. Services like RaccoonO365 cater to a marketplace of buyers, some of whom are small-time scammers while others may be part of larger organized groups. This professionalization means phishing scales faster, spreads wider, and adapts quickly when infrastructure is taken down.

The numbers from Microsoft and Cloudflare show just how global these schemes have become. With victims in nearly 100 countries and verticals ranging from finance to healthcare, RaccoonO365 had the reach of a multinational enterprise—except its product was stolen credentials.

What Matters

Credential theft remains one of the most common entry points for attacks like business email compromise (BEC) and ransomware. Phishing-as-a-service accelerates that risk because it industrializes the process. A hospital IT manager or a finance team in a small business might not be directly aware of RaccoonO365, but the phishing email in their inbox could very well have been generated by it.

By seizing domains and dismantling infrastructure, Microsoft and Cloudflare have temporarily blunted a major source of credential theft. But history suggests that such services often re-emerge under new branding or infrastructure. The success of the takedown lies less in eliminating the threat entirely and more in raising costs and buying defenders time.

The Bigger Picture

Phishing may seem like old news compared to ransomware or nation-state espionage, but its persistence is telling. Social engineering remains one of the most effective tools for attackers because it targets the human layer of security. RaccoonO365 thrived because it removed friction for cybercriminals and played on trust in familiar brands like Microsoft.

The collaboration between Microsoft and Cloudflare shows the growing role of private sector alliances in tackling cybercrime infrastructure. Law enforcement wasn’t central to this takedown—cloud providers and platform owners took matters into their own hands, leveraging legal and technical measures to directly disrupt criminal supply chains.

Whether RaccoonO365’s operators attempt a comeback remains to be seen. But the message was straight-forward. The ecosystem that supports phishing as a service is in the crosshairs, and tech giants are increasingly willing to act when their platforms are abused at scale.

Also read: FBI Seizes Key Domains Behind LummaC2 Malware Used in Global Credential Theft

Share this:

  • Share on LinkedIn (Opens in new window) LinkedIn
  • Share on Reddit (Opens in new window) Reddit
  • Share on X (Opens in new window) X
  • Share on Facebook (Opens in new window) Facebook
  • More
  • Email a link to a friend (Opens in new window) Email
  • Share on WhatsApp (Opens in new window) WhatsApp

Related

Tags: CloudflareMicrosoftphishing as a serviceRaccoonO365
Previous Post

CrowdStrike Among Those Hit in NPM Attack Campaign

Next Post

Russia-Linked Hybrid Campaign Targeted 2024 Elections: Romanian Prosecutor General

Next Post
Alex Florenta, Romanian Prosecutor General

Russia-Linked Hybrid Campaign Targeted 2024 Elections: Romanian Prosecutor General

Cyble-Vision


Follow Us On Google News

Categories

Q1 2026 Threat Reports

❮ ❯
  • Privacy Statement
  • Terms of Use
  • Write For Us

© 2026 The Cyber Express - Cybersecurity News and Magazine.

Welcome Back!

Login to your account below

Forgotten Password?

Retrieve your password

Please enter your username or email address to reset your password.

Log In

Add New Playlist

No Result
View All Result
  • Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board

© 2026 The Cyber Express - Cybersecurity News and Magazine.

-
00:00
00:00

Queue

Update Required Flash plugin
-
00:00
00:00


