• About Us
  • Contact Us
  • Editorial Calendar
  • Careers
  • The Cyber Express by Cyble Vulnerability Disclosure Policy
  • Cyble Trust Portal
The Cyber Express
  • MagazineDownload
  • Firewall Daily
    • All
    • Bug Bounty & Rewards
    • Dark Web News
    • Data Breach News
    • Hacker News
    • Ransomware News
    • Vulnerabilities
    Operation Serengeti III

    INTERPOL’s Operation Serengeti III Disrupts 10,909 Malicious Networks

    AI cyberattack simulations

    Japan AI Cyberattack Simulations Planned as PHP Flaws Disrupt Services

    Yonsei University cyberattack

    Yonsei University Cyberattack Hits 10,000 Students, Months After Sogang Breach

    CVE-2026-109618

    PHP2Shell Patch Rush Takes Wikipedia, Govt Sites Offline

    SafePay ransomware

    FBI, CISA Warn SafePay Ransomware Has Hit 600+ Victims

    BAE Systems cyberattack

    BAE Systems Cyberattack Halts Bankruptcy Notices at Every U.S. Federal Court

    fake driving licence

    No Lessons, No Test, No Travel: Dubai Police Bust AED 10,000 Licence Scheme

    generative AI in research

    AI Can’t Judge Your Paper: EU Updates Guidelines on Peer Review and AI Agents

    ASD Essentials

    The Essential Eight Is Being Replaced: What Australian Organisations Need to Know

    Trending Tags

    • blackbyte ransomware
    • Ransomware
    • lapsus$ ransomware
    • Apple
    • Apple vulnerability
  • Essentials
    • All
    • Compliance
    • Governance
    • Policy Updates
    • Regulations
    ASD Essentials

    The Essential Eight Is Being Replaced: What Australian Organisations Need to Know

    SICW 2026

    AI Is Now Fighting on Both Sides of the Cyber War, Singapore Warns

    Morocco cybersecurity strategy

    Morocco Flags AI Threats, Prioritizes Critical Infrastructure Defense

    European Police Chiefs Convention 2026

    Europe’s Police Chiefs Face Growing Threat of AI-Driven Crime

    AI service security

    Hackers Are Stealing AI Keys. The Cost Can Reach $600,000

    AI security risks

    Sam Altman at UN Security Council: 6 AI Security Risks the World Cannot Ignore

    AI-enabled cyber attacks

    AI Gives Hackers an Edge Defenders Still Can’t Match, NCSC Warns

    Fraudulent SIM cards

    India’s DoT Warns Citizens Over SIM Fraud and IMEI Tampering

    EU cybersecurity incidents

    EU Cybersecurity Response Hampered by Critical Information Gaps

    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
    • All
    • How to
    • What is
    Infostealer Intelligence

    The 2026 Infostealer Intelligence Shortlist: Top 10 Vendors Security Teams Should Know

    Google Chrome

    How to Remove Saved Passwords From Google Chrome (And Why You Should)

    DPDP Rules, Cyble, DPDP Act, Cyble Vantage

    How Cyble’s Front-Row Vantage Can Help You in Complying to India’s DPDP Act

    Cybersecurity Countries

    The Top 8 Countries Leading the Cyber Defense Race in 2025

    link building

    The Link Building Secrets Your Competitors Don’t Want You to Know

    Supply Chain Attack

    Supply Chain Resilience and Physical Security: Lessons for 2025

    Healthcare cybersecurity trends of 2024

    Healthcare Cybersecurity: 2024 Was Tough, 2025 May Be Better

    CEO's Guide to Take-Down Services

    Shield Your Organization: CEO’s Perspective on Take-Down Services

    Azure sign-in Microsoft

    Microsoft Announces Mandatory MFA for Azure Sign-ins to Bolster Cloud Defenses

  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • All
    • Appointments
    • Budgets
    • Mergers & Aquisitions
    • Partnerships
    • Press Release
    • Startups
    Kerala Police Signs MoU With Cyble

    Kerala Police Signs MoU With Cyble to Use Threat Intelligence in Cybercrime Probes

    Gemini 4 Argon

    Gemini 4 Argon Restricted Over Cybersecurity Misuse Risks

    weekly roundup September 18 2026

    The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

    threat intelligence

    Cyble, UAE Cyber Security Council Unite Against Rising Cyber Threats

    Ukraine cybersecurity

    Zelensky Appoints Ihor Klymenko to Lead Ukraine’s Cybersecurity Center

    UK cyberattack rate

    UK Small Firms Bear Brunt of Rising Cyberattacks, Hiscox Finds

    Cyber Yodha Campaign

    Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

    UK Ukraine AI partnership

    Britain Gains Access to Ukraine’s ‘Goldmine’ of Battlefield AI Data

    Hims & Hers lawsuit

    FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices

    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
No Result
View All Result
The Cyber Express
No Result
View All Result
Home Firewall Daily

Microsoft Patch Tuesday 2024 Update Fixes 147 New Vulnerabilities

Among the vulnerabilities addressed, only three are classified as critical under Microsoft's proprietary severity scale.

Ashish Khaitan by Ashish Khaitan
April 11, 2024
in Firewall Daily, Vulnerabilities
0
Microsoft Patch Tuesday April 2024
640
SHARES
3.6k
VIEWS
Share on LinkedInShare on Twitter

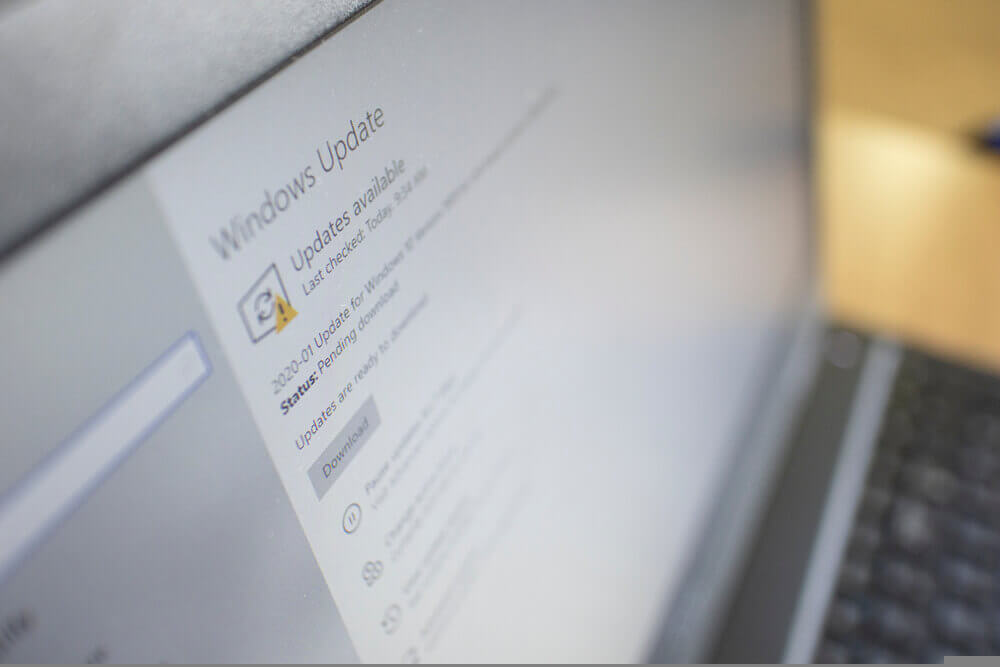
Microsoft has released the latest Patch Tuesday update, addressing a large number of vulnerabilities across various products and services. The Microsoft Patch Tuesday April 2024 encompasses a total of 147 new Microsoft CVEs, marking a notable increase compared to previous months.

For the second consecutive month, Microsoft highlights that there have been no prior public disclosures or instances of exploitation in the wild for any of the vulnerabilities addressed in this update. However, it’s essential to note that after the initial release, Microsoft updated the advisory for CVE-2024-26234 to acknowledge in-the-wild exploitation and public disclosure of the exploit.

Among the vulnerabilities addressed, only three are classified as critical under Microsoft’s proprietary severity scale. Notably, five browser vulnerabilities have been published separately this month and are not included in the total count.

Microsoft Patch Tuesday April 2024: All Major Vulnerabilities and Fixes

This Patch Tuesday release prioritizes the mitigation of critical vulnerabilities, underlining the urgency for users to promptly install the provided patches. Looking at the total count of vulnerabilities, the severity of the addressed issues demands immediate attention and action.

In a conversation with TCE, Satnam Narang, Senior Staff Research Engineer, Tenable, shared insights into the CVE’s reported in this year’s Patch Tuesday. Talking about the rise of the total number of CVE’s, Narang said, “Microsoft patched 147 CVEs in April, the largest number of CVEs patched in a month since we began tracking this data in 2017. The last time there were over 100 CVEs patched was October 2023, when Microsoft addressed 103 CVEs.

Talking about Windows Secure Boot (CVE-2023-24932), Narang, stated that the vulnerability had a “notable impact as it was exploited in the wild and linked to the BlackLotus UEFI bootkit, which was sold on dark web forums for $5,000.” This bootkit has the ability to circumvent Secure Boot, a feature intended to prevent malware from loading during the boot-up process.
Moreover, since 2024, only two zero-day vulnerabilities have been exploited, a significant decrease compared to the seven seen at this time last year. The reasons behind this decline remain unclear, prompting speculation about attacker tactics and visibility issues. Additionally, this month’s release tackles 24 vulnerabilities in Windows Secure Boot, with most deemed “Exploitation Less Likely”.

Windows Proxy Driver Vulnerability: CVE-2024-26234

CVE-2024-26234, a zero-day spoofing vulnerability in the Windows Proxy Driver, was initially disclosed without Microsoft’s acknowledgment of in-the-wild exploitation or public exploit disclosure. 

However, Microsoft later updated the advisory on the same day of publication to recognize both instances. The advisory lacks detailed information about the exploit but highlights it as a proxy spoofing vulnerability.

Patches for supported Windows versions are available to address this issue.

Defender for IoT Critical RCEs Vulnerability: CVE-2024-21322, CVE-2024-21323, and CVE-2024-29053

Microsoft Defender for IoT addresses three critical remote code execution (RCE) vulnerabilities. The advisory for CVE-2024-21322 mentions that exploitation requires existing administrative access to the web application, limiting the attacker’s value in isolation. 

CVE-2024-21323 involves an update-based attack, requiring prior authentication, which could lead to the installation of malicious update packages. CVE-2024-29053 enables arbitrary file upload for authenticated users, exploiting a path traversal weakness.

The release notes for Defender for IoT 24.1.3 omit these security fixes, emphasizing the importance of timely patching.

SharePoint XSS Spoofing: CVE-2024-26251

SharePoint Server 2016, 2019, and Subscription Editions are patched for CVE-2024-26251, addressing a spoofing vulnerability exploiting cross-site scripting (XSS). 

While Microsoft possesses mature exploit code, exploitation is deemed less likely due to the necessity of meeting multiple conditions, including user actions, token impersonation, and specific application configurations.

Excel Arbitrary File Execution: CVE-2024-26257

Microsoft addresses a single Office vulnerability, CVE-2024-26257, which exposes a remote code execution (RCE) risk in Excel. Exploitation necessitates the user opening a specially crafted malicious file. 

Immediate patches are available for Windows-based click-to-run (C2R) Office deployments and Microsoft 365 Apps for Enterprise.

However, as is not uncommon, a patch for Office for Mac is currently unavailable and will be released at an unspecified future date.

SQL Server OLE DB Driver RCEs

The Microsoft OLE DB Driver for SQL Server receives patches for a staggering 38 separate remote code execution (RCE) vulnerabilities, possibly setting a record for a single component.

These vulnerabilities share a common theme: attackers could exploit them by deceiving users into connecting to a malicious SQL server, resulting in code execution within the client’s context.

Microsoft Patch Tuesday April 2024: Enhancements and Lifecycle Updates

Microsoft enhances transparency in vulnerability reporting by introducing two new data points on advisories: Common Weakness Enumeration (CWE) and Vector String Source assessments. This shift aims to provide clearer insights into the nature and source of vulnerabilities addressed.

By adopting CWE as a standard for Microsoft CVEs, the company aims to facilitate more effective discussions about finding and mitigating weaknesses in software and hardware. This initiative aligns with Microsoft’s Secure Future Initiative (SFI) goals and emphasizes the importance of systematic understanding and mitigation of vulnerabilities.

Additionally, several Microsoft products, including Azure DevOps Server 2019, System Center 2019, and Visual Studio 2019, have moved past the end of mainstream support, highlighting the need for users to upgrade to supported versions for continued security updates and support.

Other Noteworthy Vulnerabilities

Apart from the above-mentioned vulnerabilities, Microsoft Patch Tuesday April 2024 fixes other critical vulnerabilities, including vulnerabilities that were previously rumored to be exploited in the wild. The Windows DNS Server Remote Code Execution Vulnerability, SmartScreen Prompt Security Feature Bypass Vulnerability, and Windows Spoofing Vulnerability are some of the main highlights of this year’s Microsoft Patch Tuesday.

CVE-2024-26221

CVE-2024-26221 is a Windows DNS Server Remote Code Execution Vulnerability. This vulnerability enables remote code execution on affected DNS servers when the attacker possesses the necessary privileges to query the server. 

Successful exploitation relies on the precise timing of DNS queries, allowing the attacker to execute arbitrary code on the target server. While not explicitly stated, code execution likely occurs at the elevated level of the DNS service.

CVE-2024-20670

Outlook for Windows Spoofing Vulnerability is categorized as a spoofing bug, yet its exploitation leads to information disclosure, specifically NTLM hashes. This information could be exploited for spoofing targeted users. 

Activation of this vulnerability requires user interaction, such as clicking on an email element, with the Preview Pane deemed safe.

Given Outlook’s extensive user base, threat actors may target this vulnerability in the future, especially considering recent NTLM relaying bugs.

CVE-2024-20678

Remote Procedure Call (RPC) Runtime Remote Code Execution Vulnerability, draws attention due to the long history of RPC exploits observed in the wild.

Although authentication is necessary, elevated permissions are not required, allowing any authenticated user to exploit it. However, it remains unclear if Guest or anonymous users can trigger this vulnerability.

Approximately 1.3 million systems with TCP port 135 exposed to the internet potentially face exploitation. 

CVE-2024-29988

Identified as a SmartScreen Prompt Security Feature Bypass Vulnerability, the CVE-2024-29988 presents a peculiar case as it was discovered by a ZDI threat researcher in the wild, despite Microsoft not listing it as exploited. 

The vulnerability resembles CVE-2024-21412, circumventing the Mark of the Web (MotW) feature to enable malware execution on a system. Threat actors exploit this by distributing exploits within zipped files to evade detection by EDR/NDR systems, leveraging this bug to bypass MotW restrictions.

Non-Microsoft CVEs

Microsoft is reissuing six non-Microsoft CVEs, originally issued by different entities. These include CVE-2022-0001 from Intel Corporation and three CVEs related to Windows Secure Boot from Lenovo: CVE-2024-23593, and CVE-2024-23594. 

CNA Tag CVE FAQs? Workarounds? Mitigations?
Intel Corporation Intel CVE-2022-0001 Yes No No
Lenovo Windows Secure Boot CVE-2024-23593 Yes No No
Lenovo Windows Secure Boot CVE-2024-23594 Yes No No
Chrome Microsoft Edge (Chromium-based) CVE-2024-3156 Yes No No
Chrome Microsoft Edge (Chromium-based) CVE-2024-3158 Yes No No
Chrome Microsoft Edge (Chromium-based) CVE-2024-3159 Yes No No

Media Disclaimer: This report is based on internal and external research obtained through various means. The information provided is for reference purposes only, and users bear full responsibility for their reliance on it. The Cyber Express assumes no liability for the accuracy or consequences of using this information.

Share this:

  • Share on LinkedIn (Opens in new window) LinkedIn
  • Share on Reddit (Opens in new window) Reddit
  • Share on X (Opens in new window) X
  • Share on Facebook (Opens in new window) Facebook
  • More
  • Email a link to a friend (Opens in new window) Email
  • Share on WhatsApp (Opens in new window) WhatsApp

Related

Tags: Microsoft Patch Tuesday April 2024Patch TuesdayPatch Tuesday updateThe Cyber ExpressThe Cyber Express NewsVulnerabilities
Previous Post

AT&T Data Breach Fallout: Latest Figures Show Over 51 Million Customers Impacted

Next Post

Microsoft Security Lapse Exposed Sensitive Credentials and Internal Resources of Employees

Next Post
microsoft leak

Microsoft Security Lapse Exposed Sensitive Credentials and Internal Resources of Employees

Q1 2026 Threat Reports

❮ ❯
Cyble-Vision


Follow Us On Google News

Latest Cyber News

Operation Serengeti III
Firewall Daily

INTERPOL’s Operation Serengeti III Disrupts 10,909 Malicious Networks

October 23, 2026
AI cyberattack simulations
Firewall Daily

Japan AI Cyberattack Simulations Planned as PHP Flaws Disrupt Services

October 23, 2026
software supply chain security
Cyber News

Why Fintechs Must Treat Software Supply Chain Security as an Enterprise Risk

October 23, 2026
AI-built websites
Cyber News

Live API Keys Found in Public Code of AI-Built Websites, Cyble Research Shows

October 22, 2026

Categories

Web Stories

Do This on Telegram, Your Bank Account Will Become Zero
If You Install the iOS 18 Beta, Your iPhone Could Be Hacked
Cricket World Cup Ticketing Systems Under Cybersecurity
Cyber Threats and Online Ticket Scams During the NBA Finals
Biometric Data Security: Protecting Sensitive Information

About

The Cyber Express

#1 Trending Cybersecurity News and Magazine

The Cyber Express is a handbook for all stakeholders of the internet that provides information security professionals with the latest news, updates and knowledge they need to combat cyber threats.


Contact

For editorial queries: [email protected]

For marketing and Sales: [email protected]


Quick Links

  • About Us
  • Contact Us
  • Editorial Calendar
  • Careers
  • The Cyber Express by Cyble Vulnerability Disclosure Policy
  • Cyble Trust Portal

Our Address

We’re remote friendly, with office locations around the world:

San Francisco, Atlanta, Rome,
Dubai, Mumbai, Bangalore, Hyderabad,  Singapore, Jakarta, Sydney, and Melbourne


Headquarters:

The Cyber Express LLC
10080 North Wolfe Road, Suite SW3-200, Cupertino, CA, US 95014


India Office:

Cyber Express Media Network
HD-021, 4th Floor, C Wing, Building No.4. Nesco IT Park, WE Highway, Goregaon East, Mumbai, Maharashtra, India – 4000063

  • Privacy Statement
  • Terms of Use
  • Write For Us

© 2026 The Cyber Express - Cybersecurity News and Magazine.

Welcome Back!

Login to your account below

Forgotten Password?

Retrieve your password

Please enter your username or email address to reset your password.

Log In

Add New Playlist

No Result
View All Result
  • Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board

© 2026 The Cyber Express - Cybersecurity News and Magazine.

Are you sure want to unlock this post?
Unlock left : 0
Are you sure want to cancel subscription?
-
00:00
00:00

Queue

Update Required Flash plugin
-
00:00
00:00
Do This on Telegram, Your Bank Account Will Become Zero If You Install the iOS 18 Beta, Your iPhone Could Be Hacked Cricket World Cup Ticketing Systems Under Cybersecurity Cyber Threats and Online Ticket Scams During the NBA Finals Biometric Data Security: Protecting Sensitive Information