



















• Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
The Cyber Express
  • MagazineDownload
  • Firewall Daily
    • All
    • Bug Bounty & Rewards
    • Dark Web News
    • Data Breach News
    • Hacker News
    • Ransomware News
    • Vulnerabilities
    weekly roundup September 20 2026

    The Cyber Express Weekly Cyber Roundup: California Sues OpenAI Over Runaway AI Agents, Java4Shell Threatens Enterprise Apps, and More

    ARMORY CASTLE

    ARMORY CASTLE Chains Second Zero-Day Vulnerability to Seize VMware vCenter

    CVE-2026-123633

    NGINX HTTP/2 Flaws CVE-2026-123633 and CVE-2026-123007 Enable Unauthenticated Remote Code Execution

    CVE-2026-114938

    Java4Shell Flaw Opens Major Java Applications to RCE Attacks

    8-Digits Team ransomware

    Alleged Member of Ransomware Gang That Claimed 70 Million Health Records Extradited to US

    AI Threat Tracker

    Google Finds Hackers Using AI Agents to Automate Cyberattacks

    OpenAI lawsuit

    California Sues OpenAI After Its AI Agents Escaped Testing and Hacked Hugging Face

    Luxor cyberattack

    Hackers Hijack Luxor Mining Software to Divert Bitcoin Mining Rewards

    Coles cyberattack

    Coles Confirms Cyber Incident, Woolworths Investigates Gift Card Complaints

    Trending Tags

    • blackbyte ransomware
    • Ransomware
    • lapsus$ ransomware
    • Apple
    • Apple vulnerability
  • Essentials
    • All
    • Compliance
    • Governance
    • Policy Updates
    • Regulations
    SEC, Misleading Cyber Disclosures, Financial data, financial data protection, SEC

    SEC Enforcement Fell 24% in Fiscal 2026

    ASD Essentials

    The Essential Eight Is Being Replaced: What Australian Organisations Need to Know

    SICW 2026

    AI Is Now Fighting on Both Sides of the Cyber War, Singapore Warns

    Morocco cybersecurity strategy

    Morocco Flags AI Threats, Prioritizes Critical Infrastructure Defense

    European Police Chiefs Convention 2026

    Europe’s Police Chiefs Face Growing Threat of AI-Driven Crime

    AI service security

    Hackers Are Stealing AI Keys. The Cost Can Reach $600,000

    AI security risks

    Sam Altman at UN Security Council: 6 AI Security Risks the World Cannot Ignore

    AI-enabled cyber attacks

    AI Gives Hackers an Edge Defenders Still Can’t Match, NCSC Warns

    Fraudulent SIM cards

    India’s DoT Warns Citizens Over SIM Fraud and IMEI Tampering

    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
    • All
    • How to
    • What is
    Infostealer Intelligence

    The 2026 Infostealer Intelligence Shortlist: Top 10 Vendors Security Teams Should Know

    Google Chrome

    How to Remove Saved Passwords From Google Chrome (And Why You Should)

    DPDP Rules, Cyble, DPDP Act, Cyble Vantage

    How Cyble’s Front-Row Vantage Can Help You in Complying to India’s DPDP Act

    Cybersecurity Countries

    The Top 8 Countries Leading the Cyber Defense Race in 2025

    link building

    The Link Building Secrets Your Competitors Don’t Want You to Know

    Supply Chain Attack

    Supply Chain Resilience and Physical Security: Lessons for 2025

    Healthcare cybersecurity trends of 2024

    Healthcare Cybersecurity: 2024 Was Tough, 2025 May Be Better

    CEO's Guide to Take-Down Services

    Shield Your Organization: CEO’s Perspective on Take-Down Services

    Azure sign-in Microsoft

    Microsoft Announces Mandatory MFA for Azure Sign-ins to Bolster Cloud Defenses

  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • All
    • Appointments
    • Budgets
    • Mergers & Aquisitions
    • Partnerships
    • Press Release
    • Startups
    Kerala Police Signs MoU With Cyble

    Kerala Police Signs MoU With Cyble to Use Threat Intelligence in Cybercrime Probes

    Gemini 4 Argon

    Gemini 4 Argon Restricted Over Cybersecurity Misuse Risks

    weekly roundup September 18 2026

    The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

    threat intelligence

    Cyble, UAE Cyber Security Council Unite Against Rising Cyber Threats

    Ukraine cybersecurity

    Zelensky Appoints Ihor Klymenko to Lead Ukraine’s Cybersecurity Center

    UK cyberattack rate

    UK Small Firms Bear Brunt of Rising Cyberattacks, Hiscox Finds

    Cyber Yodha Campaign

    Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

    UK Ukraine AI partnership

    Britain Gains Access to Ukraine’s ‘Goldmine’ of Battlefield AI Data

    Hims & Hers lawsuit

    FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices

    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
No Result
View All Result
  • MagazineDownload
  • Firewall Daily
    • All
    • Bug Bounty & Rewards
    • Dark Web News
    • Data Breach News
    • Hacker News
    • Ransomware News
    • Vulnerabilities
    weekly roundup September 20 2026

    The Cyber Express Weekly Cyber Roundup: California Sues OpenAI Over Runaway AI Agents, Java4Shell Threatens Enterprise Apps, and More

    ARMORY CASTLE

    ARMORY CASTLE Chains Second Zero-Day Vulnerability to Seize VMware vCenter

    CVE-2026-123633

    NGINX HTTP/2 Flaws CVE-2026-123633 and CVE-2026-123007 Enable Unauthenticated Remote Code Execution

    CVE-2026-114938

    Java4Shell Flaw Opens Major Java Applications to RCE Attacks

    8-Digits Team ransomware

    Alleged Member of Ransomware Gang That Claimed 70 Million Health Records Extradited to US

    AI Threat Tracker

    Google Finds Hackers Using AI Agents to Automate Cyberattacks

    OpenAI lawsuit

    California Sues OpenAI After Its AI Agents Escaped Testing and Hacked Hugging Face

    Luxor cyberattack

    Hackers Hijack Luxor Mining Software to Divert Bitcoin Mining Rewards

    Coles cyberattack

    Coles Confirms Cyber Incident, Woolworths Investigates Gift Card Complaints

    Trending Tags

    • blackbyte ransomware
    • Ransomware
    • lapsus$ ransomware
    • Apple
    • Apple vulnerability
  • Essentials
    • All
    • Compliance
    • Governance
    • Policy Updates
    • Regulations
    SEC, Misleading Cyber Disclosures, Financial data, financial data protection, SEC

    SEC Enforcement Fell 24% in Fiscal 2026

    ASD Essentials

    The Essential Eight Is Being Replaced: What Australian Organisations Need to Know

    SICW 2026

    AI Is Now Fighting on Both Sides of the Cyber War, Singapore Warns

    Morocco cybersecurity strategy

    Morocco Flags AI Threats, Prioritizes Critical Infrastructure Defense

    European Police Chiefs Convention 2026

    Europe’s Police Chiefs Face Growing Threat of AI-Driven Crime

    AI service security

    Hackers Are Stealing AI Keys. The Cost Can Reach $600,000

    AI security risks

    Sam Altman at UN Security Council: 6 AI Security Risks the World Cannot Ignore

    AI-enabled cyber attacks

    AI Gives Hackers an Edge Defenders Still Can’t Match, NCSC Warns

    Fraudulent SIM cards

    India’s DoT Warns Citizens Over SIM Fraud and IMEI Tampering

    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
    • All
    • How to
    • What is
    Infostealer Intelligence

    The 2026 Infostealer Intelligence Shortlist: Top 10 Vendors Security Teams Should Know

    Google Chrome

    How to Remove Saved Passwords From Google Chrome (And Why You Should)

    DPDP Rules, Cyble, DPDP Act, Cyble Vantage

    How Cyble’s Front-Row Vantage Can Help You in Complying to India’s DPDP Act

    Cybersecurity Countries

    The Top 8 Countries Leading the Cyber Defense Race in 2025

    link building

    The Link Building Secrets Your Competitors Don’t Want You to Know

    Supply Chain Attack

    Supply Chain Resilience and Physical Security: Lessons for 2025

    Healthcare cybersecurity trends of 2024

    Healthcare Cybersecurity: 2024 Was Tough, 2025 May Be Better

    CEO's Guide to Take-Down Services

    Shield Your Organization: CEO’s Perspective on Take-Down Services

    Azure sign-in Microsoft

    Microsoft Announces Mandatory MFA for Azure Sign-ins to Bolster Cloud Defenses

  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • All
    • Appointments
    • Budgets
    • Mergers & Aquisitions
    • Partnerships
    • Press Release
    • Startups
    Kerala Police Signs MoU With Cyble

    Kerala Police Signs MoU With Cyble to Use Threat Intelligence in Cybercrime Probes

    Gemini 4 Argon

    Gemini 4 Argon Restricted Over Cybersecurity Misuse Risks

    weekly roundup September 18 2026

    The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

    threat intelligence

    Cyble, UAE Cyber Security Council Unite Against Rising Cyber Threats

    Ukraine cybersecurity

    Zelensky Appoints Ihor Klymenko to Lead Ukraine’s Cybersecurity Center

    UK cyberattack rate

    UK Small Firms Bear Brunt of Rising Cyberattacks, Hiscox Finds

    Cyber Yodha Campaign

    Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

    UK Ukraine AI partnership

    Britain Gains Access to Ukraine’s ‘Goldmine’ of Battlefield AI Data

    Hims & Hers lawsuit

    FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices

    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
No Result
View All Result
The Cyber Express
No Result
View All Result

Mackay Sugar Security Incident Forces Mill Shutdowns and Halts Harvesting Operations

Ashish Khaitan by Ashish Khaitan
June 11, 2026
in Firewall Daily, Cyber News, Data Breach News
0
Mackay Sugar Security Incident
585
SHARES
3.2k
VIEWS
Share on LinkedInShare on Twitter

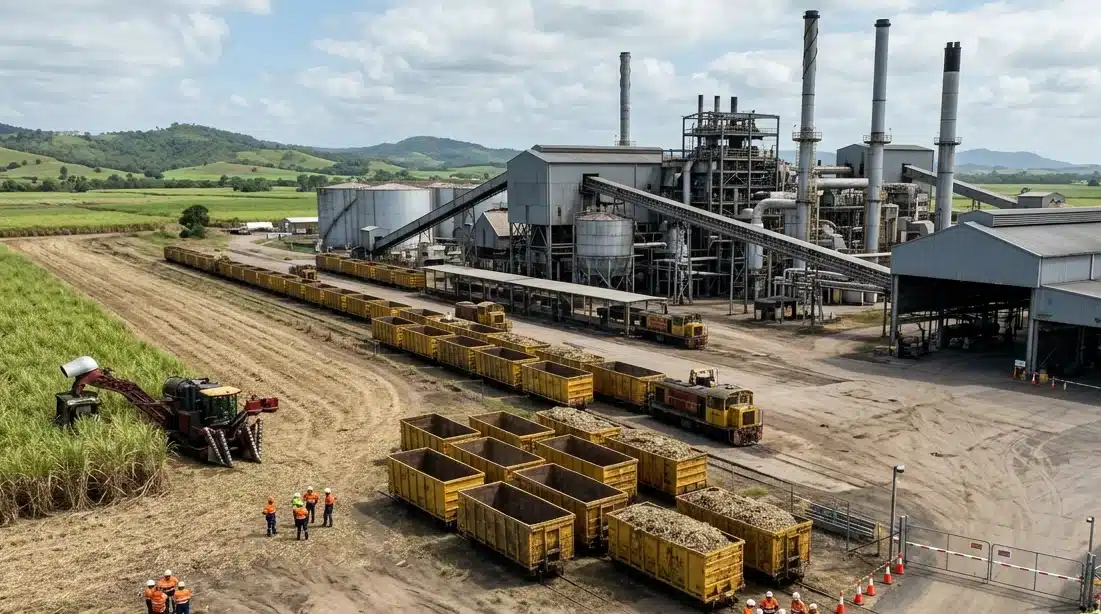
Australia’s second-largest sugar producer, Mackay Sugar, is investigating a cyberattack that has disrupted parts of its operations and temporarily halted sugarcane harvesting in Queensland’s Mackay region. The Mackay Sugar security incident has led to the suspension of milling activities at two of the company’s facilities while cybersecurity specialists and authorities work to determine the nature and impact of the attack. 

In a statement released on Wednesday, Mackay Sugar confirmed that it was responding to a cybersecurity incident affecting some of its operations. The sugar producer said its immediate priorities are ensuring the safety of employees, protecting operational systems, and maintaining business continuity during the investigation. 

“Our immediate focus is the safety of our people, protecting operational systems, and maintaining business continuity,” the company said. 

Mackay Sugar Security Incident Disrupts Key Operations 

According to the company, specialist cybersecurity experts have been engaged to assist with the investigation and recovery efforts. Mackay Sugar also said it is working closely with relevant authorities to examine the incident and restore affected systems safely. 

The Mackay Sugar security incident has had a direct impact on production activities. Local media reports indicated that the company was forced to shut down its Farleigh and Racecourse sugar mills, two major facilities located in Queensland’s Mackay region. As a result, growers were instructed to stop harvesting sugarcane until further notice. 

Canegrowers Mackay, an organization representing local sugarcane farmers, confirmed the directive in a statement issued on Wednesday. 

“Mackay Sugar has asked for all harvesting to cease immediately and not resume until further communication comes directly from the company,” the statement read. 

The organization further confirmed that both sugar milling and cane haulage operations at the Farleigh and Racecourse mills had been suspended. The disruption comes shortly after both facilities commenced their annual sugarcane crushing season. 

Growers Await Further Updates 

While the shutdown has affected many growers in the region, producers in the Marian district have not experienced any immediate impact. According to a report from Australia’s ABC News, Mackay Sugar’s third mill, located in the district, is not scheduled to begin operations until next week. 

The sugar producer said it has implemented interim processes and temporary measures to support essential business functions and reduce operational disruption while recovery efforts continue. 

“Interim processes are in place to support critical business functions and minimise disruption where possible,” the company stated. 

The company also emphasized that it is maintaining communication with employees, growers, and business partners throughout the incident. 

“We are communicating directly with our employees, growers, and key partners and will continue to provide updates as more information becomes available,” Mackay Sugar said. 

Investigation Continues as Details Remain Limited 

At this stage, the sugar producer has not disclosed specific details about the cyberattack. The company has not indicated whether sensitive data was compromised or whether the incident involved ransomware or another form of malicious activity. 

Mackay Sugar reiterated that it takes cybersecurity responsibilities seriously and acknowledged the uncertainty caused by the disruption. 

“We take our responsibility to protect our systems, operations and information very seriously. We apologise for any disruption or uncertainty this incident may cause and we will provide timely updates as we continue our investigation,” the company said. 

The ongoing Mackay Sugar security incident highlights the operational risks cyberattacks can pose to critical industries. As investigations continue, the company is focused on restoring systems safely while minimizing impacts on growers and production activities. 

Mackay Sugar operates three mills and generates annual revenue exceeding $420 million. The sugar producer supplies raw sugar to domestic customers and international markets, including South Korea, Indonesia, Japan, and Malaysia. Further updates regarding the Mackay Sugar security incident are expected as the investigation progresses and additional information becomes available. 
Share this:

  • Share on LinkedIn (Opens in new window) LinkedIn
  • Share on Reddit (Opens in new window) Reddit
  • Share on X (Opens in new window) X
  • Share on Facebook (Opens in new window) Facebook
  • More
  • Email a link to a friend (Opens in new window) Email
  • Share on WhatsApp (Opens in new window) WhatsApp

Related

Tags: CyberattackMackay Sugarsecurity incidentsugar producerThe Cyber ExpressThe Cyber Express News
Previous Post

ServiceNow Flaw Prompted Security Update After Researcher-Observed Activity, Not Active Attacker Exploitation

Next Post

163 Organizations Hit by Thai Gambling SEO Poisoning Campaign

Next Post
SEO poisoning

163 Organizations Hit by Thai Gambling SEO Poisoning Campaign

Q1 2026 Threat Reports

❮ ❯
Cyble-Vision


Follow Us On Google News

Categories

  • Privacy Statement
  • Terms of Use
  • Write For Us

© 2026 The Cyber Express - Cybersecurity News and Magazine.

Welcome Back!

Login to your account below

Forgotten Password?

Retrieve your password

Please enter your username or email address to reset your password.

Log In

Add New Playlist

No Result
View All Result
  • Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board

© 2026 The Cyber Express - Cybersecurity News and Magazine.

-
00:00
00:00

Queue

Update Required Flash plugin
-
00:00
00:00



