• About Us
  • Contact Us
  • Editorial Calendar
  • Careers
  • The Cyber Express by Cyble Vulnerability Disclosure Policy
  • Cyble Trust Portal
The Cyber Express
  • MagazineDownload
  • Firewall Daily
    • All
    • Bug Bounty & Rewards
    • Dark Web News
    • Data Breach News
    • Hacker News
    • Ransomware News
    • Vulnerabilities
    The Cyber Express weekly roundup September

    The Cyber Express Weekly Roundup: Iranian Bounty, Airline Data Leak, and AI-Model Prompt Injection

    Springfield cyberattack

    Springfield Schools Prepare for Return After Cyberattack Disruption

    Agentic AI Harnesses

    ASD Urges Organizations to Secure the Layer Behind Agentic AI, Here’s Why

    Patch Tuesday September 2026

    Microsoft Patch Tuesday Hits Record 974 CVEs, Two Exploited

    Airline, Data Leak,

    Exposed Database Left 220Mn Airline Passenger, Crew Records Open to the Internet

    Liquid Network security incident

    Liquid Network Hackers Demand Bug Fix Before Returning $320M BTC

    Mathspace data breach

    Mathspace Breach Impacts More Than 1 Million Users in Australia, NZ

    post-quantum cryptography

    G7, CISA Urge Urgent Shift to Post-Quantum Cryptography

    $10 Million Reward for Amir Yaryab

    US Puts $10 Million Bounty on Alleged Iranian Cyber Chief

    Trending Tags

    • blackbyte ransomware
    • Ransomware
    • lapsus$ ransomware
    • Apple
    • Apple vulnerability
  • Essentials
    • All
    • Compliance
    • Governance
    • Policy Updates
    • Regulations
    Cyber Resilience Act, CRA, EU, EU Sanctions, Iran, Chinese Hacking,

    EU’s 24-Hr Vulnerability Reporting Rules Take Effect Friday, a Year Before the Rest of the Cyber Resilience Act

    outage communications

    CISA, FBI Urge Clearer Communication During Major Outages

    A session cookie depicted as a key being stolen from a browser window while a two-factor authentication prompt sits bypassed, illustrating Claude session hijacking by infostealer malware.

    Anthropic Warns Commodity Infostealers Are Hijacking Claude Sessions to Drain Paid Usage

    Social Media Ban

    New Zealand Moves to Ban Social Media for Under-16s

    Prompt Injection, Grok, Grok AI, Gemini, Fraud, Agentic AI, AI-assisted Cyberattacks

    Encrypted Prompts Defeat Grok and Gemini Guardrails; Chat Histories Stolen

    India online safety rules

    India Tightens Social Media Rules to Protect Children Online

    global crypto investment scam

    Dutch Police Arrest Key Suspect in €100M Global Crypto Investment Scam

    Australia-India PACTS

    Australia-India PACTS to Deepen Cybersecurity and Tech Collaboration

    FBI Warns of Malicious Traffic

    FBI Warns of a Hidden Web Tactic Fueling Phishing and Ransomware

    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
    • All
    • How to
    • What is
    Google Chrome

    How to Remove Saved Passwords From Google Chrome (And Why You Should)

    DPDP Rules, Cyble, DPDP Act, Cyble Vantage

    How Cyble’s Front-Row Vantage Can Help You in Complying to India’s DPDP Act

    Cybersecurity Countries

    The Top 8 Countries Leading the Cyber Defense Race in 2025

    link building

    The Link Building Secrets Your Competitors Don’t Want You to Know

    Supply Chain Attack

    Supply Chain Resilience and Physical Security: Lessons for 2025

    Healthcare cybersecurity trends of 2024

    Healthcare Cybersecurity: 2024 Was Tough, 2025 May Be Better

    CEO's Guide to Take-Down Services

    Shield Your Organization: CEO’s Perspective on Take-Down Services

    Azure sign-in Microsoft

    Microsoft Announces Mandatory MFA for Azure Sign-ins to Bolster Cloud Defenses

    Signal Proxy, Signal, Signal Ban in Russia, Signal Ban in Venezuela, Bypass Signal Ban, How to Activate Signal Proxy, Signal Proxy Server

    How to Set Up Signal Proxy to Help Bypass Censorship in Russia and Venezuela

  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • All
    • Appointments
    • Budgets
    • Mergers & Aquisitions
    • Partnerships
    • Press Release
    • Startups
    Cyber Yodha Campaign

    Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

    UK Ukraine AI partnership

    Britain Gains Access to Ukraine’s ‘Goldmine’ of Battlefield AI Data

    Hims & Hers lawsuit

    FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices

    Australia-India PACTS

    Australia-India PACTS to Deepen Cybersecurity and Tech Collaboration

    Sunil Varkey

    Sunil Varkey Joins Hexaware Technologies as EVP & CISO

    AI Chip, Chip Security Act

    Congress Wants a GPS Tracker on Every Advanced AI Chip America Exports

    Prompt Injection, Grok, Grok AI, Gemini, Fraud, Agentic AI, AI-assisted Cyberattacks

    Agentic AI Run Fraud Campaigns Earning 4.5 Times More: Interpol

    Stryker, Stryker Cyberattack, CISA, Handala

    Stryker Says Cyberattack Disrupted Processing, Manufacturing and Shipping

    INC Ransom, Western Critical Infrastructure, Critical infrastructure, Russian GRU, Russian Threat Actor, Sandworm, APT44, Energy Supply Chain, Energy Infrastructure

    INC Ransom’s Franchise Model Is Putting Critical Infrastructure on the Chopping Block

    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
No Result
View All Result
  • MagazineDownload
  • Firewall Daily
    • All
    • Bug Bounty & Rewards
    • Dark Web News
    • Data Breach News
    • Hacker News
    • Ransomware News
    • Vulnerabilities
    The Cyber Express weekly roundup September

    The Cyber Express Weekly Roundup: Iranian Bounty, Airline Data Leak, and AI-Model Prompt Injection

    Springfield cyberattack

    Springfield Schools Prepare for Return After Cyberattack Disruption

    Agentic AI Harnesses

    ASD Urges Organizations to Secure the Layer Behind Agentic AI, Here’s Why

    Patch Tuesday September 2026

    Microsoft Patch Tuesday Hits Record 974 CVEs, Two Exploited

    Airline, Data Leak,

    Exposed Database Left 220Mn Airline Passenger, Crew Records Open to the Internet

    Liquid Network security incident

    Liquid Network Hackers Demand Bug Fix Before Returning $320M BTC

    Mathspace data breach

    Mathspace Breach Impacts More Than 1 Million Users in Australia, NZ

    post-quantum cryptography

    G7, CISA Urge Urgent Shift to Post-Quantum Cryptography

    $10 Million Reward for Amir Yaryab

    US Puts $10 Million Bounty on Alleged Iranian Cyber Chief

    Trending Tags

    • blackbyte ransomware
    • Ransomware
    • lapsus$ ransomware
    • Apple
    • Apple vulnerability
  • Essentials
    • All
    • Compliance
    • Governance
    • Policy Updates
    • Regulations
    Cyber Resilience Act, CRA, EU, EU Sanctions, Iran, Chinese Hacking,

    EU’s 24-Hr Vulnerability Reporting Rules Take Effect Friday, a Year Before the Rest of the Cyber Resilience Act

    outage communications

    CISA, FBI Urge Clearer Communication During Major Outages

    A session cookie depicted as a key being stolen from a browser window while a two-factor authentication prompt sits bypassed, illustrating Claude session hijacking by infostealer malware.

    Anthropic Warns Commodity Infostealers Are Hijacking Claude Sessions to Drain Paid Usage

    Social Media Ban

    New Zealand Moves to Ban Social Media for Under-16s

    Prompt Injection, Grok, Grok AI, Gemini, Fraud, Agentic AI, AI-assisted Cyberattacks

    Encrypted Prompts Defeat Grok and Gemini Guardrails; Chat Histories Stolen

    India online safety rules

    India Tightens Social Media Rules to Protect Children Online

    global crypto investment scam

    Dutch Police Arrest Key Suspect in €100M Global Crypto Investment Scam

    Australia-India PACTS

    Australia-India PACTS to Deepen Cybersecurity and Tech Collaboration

    FBI Warns of Malicious Traffic

    FBI Warns of a Hidden Web Tactic Fueling Phishing and Ransomware

    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
    • All
    • How to
    • What is
    Google Chrome

    How to Remove Saved Passwords From Google Chrome (And Why You Should)

    DPDP Rules, Cyble, DPDP Act, Cyble Vantage

    How Cyble’s Front-Row Vantage Can Help You in Complying to India’s DPDP Act

    Cybersecurity Countries

    The Top 8 Countries Leading the Cyber Defense Race in 2025

    link building

    The Link Building Secrets Your Competitors Don’t Want You to Know

    Supply Chain Attack

    Supply Chain Resilience and Physical Security: Lessons for 2025

    Healthcare cybersecurity trends of 2024

    Healthcare Cybersecurity: 2024 Was Tough, 2025 May Be Better

    CEO's Guide to Take-Down Services

    Shield Your Organization: CEO’s Perspective on Take-Down Services

    Azure sign-in Microsoft

    Microsoft Announces Mandatory MFA for Azure Sign-ins to Bolster Cloud Defenses

    Signal Proxy, Signal, Signal Ban in Russia, Signal Ban in Venezuela, Bypass Signal Ban, How to Activate Signal Proxy, Signal Proxy Server

    How to Set Up Signal Proxy to Help Bypass Censorship in Russia and Venezuela

  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • All
    • Appointments
    • Budgets
    • Mergers & Aquisitions
    • Partnerships
    • Press Release
    • Startups
    Cyber Yodha Campaign

    Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

    UK Ukraine AI partnership

    Britain Gains Access to Ukraine’s ‘Goldmine’ of Battlefield AI Data

    Hims & Hers lawsuit

    FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices

    Australia-India PACTS

    Australia-India PACTS to Deepen Cybersecurity and Tech Collaboration

    Sunil Varkey

    Sunil Varkey Joins Hexaware Technologies as EVP & CISO

    AI Chip, Chip Security Act

    Congress Wants a GPS Tracker on Every Advanced AI Chip America Exports

    Prompt Injection, Grok, Grok AI, Gemini, Fraud, Agentic AI, AI-assisted Cyberattacks

    Agentic AI Run Fraud Campaigns Earning 4.5 Times More: Interpol

    Stryker, Stryker Cyberattack, CISA, Handala

    Stryker Says Cyberattack Disrupted Processing, Manufacturing and Shipping

    INC Ransom, Western Critical Infrastructure, Critical infrastructure, Russian GRU, Russian Threat Actor, Sandworm, APT44, Energy Supply Chain, Energy Infrastructure

    INC Ransom’s Franchise Model Is Putting Critical Infrastructure on the Chopping Block

    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
No Result
View All Result
The Cyber Express
No Result
View All Result
Home Cyber News

High-Risk ICS Vulnerability Exposes ICONICS and Mitsubishi Electric Products to Data Breaches

Samiksha Jain by Samiksha Jain
October 23, 2024
in Cyber News, Firewall Daily, Vulnerabilities
0
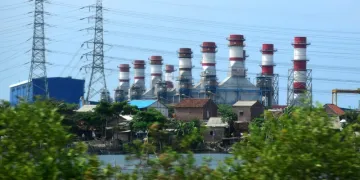
ICONICS and Mitsubishi Electric

Source: Pixabay

1.1k
SHARES
5.9k
VIEWS
Share on LinkedInShare on Twitter

The Cybersecurity and Infrastructure Security Agency (CISA), on October 22, 2024, issued a new advisory targeting Industrial Control Systems (ICS). One of the most significant vulnerabilities highlighted in the advisory involves the product suites from ICONICS and Mitsubishi Electric.

These advisories are designed to inform ICS users and administrators of security vulnerabilities, exploits, and emerging threats that may affect their critical infrastructure.

Executive Summary of the ICS Advisory

The vulnerability in question is categorized under CVE-2024-7587 with a CVSS v3.1 base score of 7.8, reflecting its high severity. With a low complexity of attack, this vulnerability presents a serious concern for users of ICONICS Suite, including products like GENESIS64, Hyper Historian, AnalytiX, and MobileHMI (version 10.97.3 and earlier), as well as Mitsubishi Electric’s MC Works64 across all versions.

If successfully exploited, this vulnerability could lead to data breaches, unauthorized data tampering, and in the worst-case scenario, denial-of-service (DoS) conditions.

Understanding the ICONICS and Mitsubishi Electric Vulnerability

At the core of the issue is incorrect default permissions (CWE-276), which allow unauthorized users to gain access to critical data. This could result in the disclosure of confidential information, manipulation of sensitive data, or potential denial-of-service events due to misconfigured access permissions.

While this vulnerability is not exploitable remotely, meaning it requires local access to the system, the impact is considerable, especially given that both ICONICS and Mitsubishi Electric products are widely deployed across industries worldwide, particularly within the critical manufacturing sector.
Affected Products

The advisory lists specific products impacted by this vulnerability:

  • ICONICS Suite, which includes the products GENESIS64, Hyper Historian, AnalytiX, and MobileHMI, version 10.97.3 and earlier.
  • Mitsubishi Electric MC Works64, which is affected across all versions.

Risk Evaluation

The vulnerability presents a moderate to high risk due to the potential for critical consequences. While the vulnerability is not exploitable remotely and does require local access, the incorrect default permissions open the door to data tampering, information disclosure, and service interruptions. Given the growing reliance on ICS across industries, such vulnerabilities can pose serious challenges to operational continuity and data integrity.

Technical Breakdown

The issue stems from default permissions being improperly assigned. Specifically, unauthorized users could potentially gain excessive access to directories that store critical data. This poses a threat not just to individual systems but also to interconnected ICS environments where even localized breaches can ripple across entire infrastructures.

The assigned CVSS vector string for this vulnerability is (CVSS:3.1/AV:L/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H).

This breakdown reflects the fact that the attack requires local access (AV) and has a low complexity (AC), with the potential to significantly compromise the system’s confidentiality, integrity, and availability.

Mitigations

To address this vulnerability, ICONICS and Mitsubishi Electric recommend several mitigation strategies for their users. For ICONICS products, the following steps are critical:

  1. Use Version 10.97.3 CFR1 or Later: For new systems, upgrade to this version or later, which is not vulnerable to the issue.
  2. For Existing Systems: If using version 10.97.3 or earlier, avoid installing the included GenBroker32. Instead, download and install the latest version of GenBroker32 from ICONICS.
  3. Verify and Correct Folder Permissions: Administrators should review the permissions for the C:\ProgramData\ICONICS folder. If the folder provides access to the “Everyone” group, remove this permission by following a step-by-step process outlined in the advisory.

For Mitsubishi Electric MC Works64, the same principles of permissions review and security patching apply. Administrators are encouraged to:

  • Regularly apply security patches as they become available.
  • Continuously monitor access permissions and ensure that overly broad permissions (like “Everyone” access) are removed.

Proactive Defense Recommendations from CISA

CISA offers a wealth of resources to help ICS users defend against vulnerabilities like CVE-2024-7587. It is critical for organizations to take a proactive approach to cybersecurity, incorporating defense-in-depth strategies that include:

  • Conducting a risk assessment and proper impact analysis before deploying mitigation strategies.
  • Regularly reviewing and implementing best practices for ICS cybersecurity, such as those outlined in CISA’s Improving Industrial Control Systems Cybersecurity with Defense-in-Depth Strategies document.
  • Monitoring the ICS webpage at CISA for the latest security advisories, guidance, and technical resources.

Importance of Reporting and Vigilance

While no public exploitation of this vulnerability has been reported to CISA so far, the agency urges organizations to remain vigilant. Should any malicious activity be suspected, organizations are advised to follow their established incident response procedures and report findings to CISA for correlation and tracking. Early detection and quick action can significantly reduce the potential impact of vulnerabilities within critical infrastructure systems.

By following the steps outlined in this advisory, users can reduce the risk of exploitation and ensure the resilience of their ICS infrastructure against potential threats.

Share this:

  • Share on LinkedIn (Opens in new window) LinkedIn
  • Share on Reddit (Opens in new window) Reddit
  • Share on X (Opens in new window) X
  • Share on Facebook (Opens in new window) Facebook
  • More
  • Email a link to a friend (Opens in new window) Email
  • Share on WhatsApp (Opens in new window) WhatsApp

Related

Tags: CISAICONICS and Mitsubishi Electric VulnerabilityICONICS SuiteICS AdvisoryIndustrial Control SystemsThe Cyber ExpressThe Cyber Express NewsVulnerability
Previous Post

Multiple High-Severity Vulnerabilities Found in Bitdefender Products: Patch Now

Next Post

Cybersecurity Meets Play: UCF’s Horse Plinko Prepares Students for Real-World Threats

Next Post
Horse Plinko Cyber Competition

Cybersecurity Meets Play: UCF’s Horse Plinko Prepares Students for Real-World Threats

Q1 2026 Threat Reports

❮ ❯
Cyble-Vision


Follow Us On Google News

Latest Cyber News

The Cyber Express weekly roundup September
Firewall Daily

The Cyber Express Weekly Roundup: Iranian Bounty, Airline Data Leak, and AI-Model Prompt Injection

September 11, 2026
Springfield cyberattack
Firewall Daily

Springfield Schools Prepare for Return After Cyberattack Disruption

September 11, 2026
Agentic AI Harnesses
Cyber News

ASD Urges Organizations to Secure the Layer Behind Agentic AI, Here’s Why

September 11, 2026
PaperCut, PaperCut Compromise
Cyber News

AI Agents Compromised 440 PaperCut Servers, Researchers Say

September 10, 2026

Categories

Web Stories

Do This on Telegram, Your Bank Account Will Become Zero
If You Install the iOS 18 Beta, Your iPhone Could Be Hacked
Cricket World Cup Ticketing Systems Under Cybersecurity
Cyber Threats and Online Ticket Scams During the NBA Finals
Biometric Data Security: Protecting Sensitive Information

About

The Cyber Express

#1 Trending Cybersecurity News and Magazine

The Cyber Express is a handbook for all stakeholders of the internet that provides information security professionals with the latest news, updates and knowledge they need to combat cyber threats.


Contact

For editorial queries: [email protected]

For marketing and Sales: [email protected]


Quick Links

  • About Us
  • Contact Us
  • Editorial Calendar
  • Careers
  • The Cyber Express by Cyble Vulnerability Disclosure Policy
  • Cyble Trust Portal

Our Address

We’re remote friendly, with office locations around the world:

San Francisco, Atlanta, Rome,
Dubai, Mumbai, Bangalore, Hyderabad,  Singapore, Jakarta, Sydney, and Melbourne


Headquarters:

The Cyber Express LLC
10080 North Wolfe Road, Suite SW3-200, Cupertino, CA, US 95014


India Office:

Cyber Express Media Network
HD-021, 4th Floor, C Wing, Building No.4. Nesco IT Park, WE Highway, Goregaon East, Mumbai, Maharashtra, India – 4000063

  • Privacy Statement
  • Terms of Use
  • Write For Us

© 2026 The Cyber Express - Cybersecurity News and Magazine.

Welcome Back!

Login to your account below

Forgotten Password?

Retrieve your password

Please enter your username or email address to reset your password.

Log In

Add New Playlist

No Result
View All Result
  • Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board

© 2026 The Cyber Express - Cybersecurity News and Magazine.

Are you sure want to unlock this post?
Unlock left : 0
Are you sure want to cancel subscription?
-
00:00
00:00

Queue

Update Required Flash plugin
-
00:00
00:00
Do This on Telegram, Your Bank Account Will Become Zero If You Install the iOS 18 Beta, Your iPhone Could Be Hacked Cricket World Cup Ticketing Systems Under Cybersecurity Cyber Threats and Online Ticket Scams During the NBA Finals Biometric Data Security: Protecting Sensitive Information