






















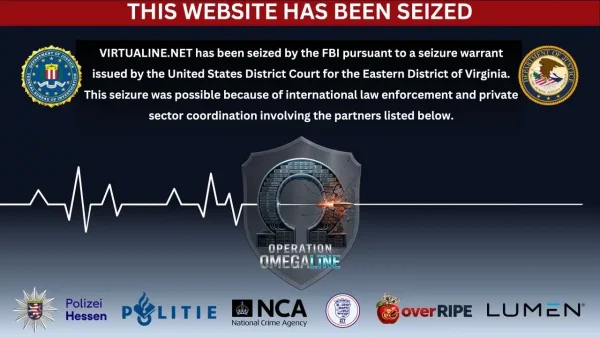
The FBI seizes Virtualine domain in a court-authorized operation alongside the U.S. Department of Justice , disrupting a so-called bulletproof hosting service accused of facilitating cybercrime, the distribution of child sexual abuse material (CSAM), and international money laundering. Before the seizure, Virtualine.net allegedly provided hosting infrastructure to criminal operations and continued supporting certain services despite repeated abuse notifications from law enforcement agencies and other organizations.
The seizure followed a court-authorized operation against Virtualine, which also operated under the names Secury, Massgod, Spamhouse, Lanedo and Omegatech.
According to court records, the service offered hosting, server solutions and domain purchasing options while advertising its ability to protect customers from law enforcement intervention.
FBI Seizes Virtualine Over Alleged Cybercrime Activity
Theophani K. Stamos, First Assistant U.S. Attorney for the Eastern District of Virginia, and Darren B. Cox, Assistant Director in Charge of the FBI Washington Field Office, announced the seizure of Virtualine.net.
Authorities said the domain had been used to facilitate multiple forms of criminal activity, including advertising sexually explicit images of minors, the intentional disclosure of nonconsensual intimate images involving adults and minors, and international money laundering.
Virtualine marketed its services on cybercrime forums, where it openly promoted hosting options for users engaged in illegal activities. In September 2024, the service told a user on Exploit.in that its infrastructure could be used for activities including phishing, carding, email spam and port scanning, while claiming to prohibit child sexual abuse material and terrorism-related content.

However, court records allege that Virtualine knowingly hosted a criminal online forum, identified as Vendor 1, that allowed users to post and sell access to nude, sexually suggestive and sexually explicit images and videos involving minors and adults.
Hosting Provider Allegedly Ignored Repeated Abuse Reports
The investigation found that Virtualine continued hosting Vendor 1 despite receiving multiple notifications about sexually explicit images and videos of minors.
According to court records, Virtualine assigned an IP address to Vendor 1 around December 2025, with notifications about the material beginning in January 2026. Reports came from law enforcement agencies in Germany, Canada and Australia, the U.S. National Center for Missing and Exploited Children (NCMEC), and an attorney representing a victim.
Despite these notifications, Virtualine allegedly continued providing hosting services to the forum.
The records also state that Virtualine worked directly with Vendor 1 to develop another website that allowed customers to upload illicit content and download it after making a purchase. Authorities said Virtualine continued hosting this website and had received at least one abuse complaint concerning sexually explicit images of children found on the platform.
Vendor 1 also promoted a hack-for-hire service, through which customers could pay hackers to gain unauthorized access to victims’ online accounts and obtain explicit images and videos.
Virtualine Advertised Measures to Evade Law Enforcement
Beyond its hosting services, Virtualine allegedly offered customers additional protection designed to keep criminal infrastructure operational when authorities intervened.
In March 2026, the provider advertised an “additional protection plan” that it said could be activated after receiving an official request from law enforcement agencies. Under the arrangement, Virtualine would move a customer’s criminal infrastructure to another shell company not affiliated with the provider, after which the server would be reactivated.
The alleged practice illustrates how bulletproof hosting services can be used to maintain online criminal operations by moving infrastructure when enforcement or abuse complaints threaten existing arrangements.
Virtualine also promoted its tolerance of abuse on underground forums. In a June 2025 post on HackForums, it claimed to have ignored more abuse reports than other providers.
Cryptocurrency Payments Linked to Money Laundering
Investigators also examined Virtualine’s payment arrangements and their alleged role in concealing criminal proceeds.
According to court records, Virtualine accepted payments through Bitcoin, including specific unhosted Bitcoin addresses that allowed customers to make direct payments without their funds being flagged as illicit.
The service received payments from criminal customers, some of which investigators could trace directly to various criminal groups. Virtualine then allegedly laundered the funds further to conceal their origin.
Authorities identified international money laundering as one of the criminal activities facilitated through the service.
International Cooperation Behind Virtualine Takedown
The FBI’s Washington Field Office led the investigation, with significant assistance from Germany’s Polizei Hessen, the Netherlands’ Politie Midden-Nederland and the United Kingdom’s National Crime Agency.
Private-sector partners OverRIPE and Lumen also assisted, while the Justice Department’s Office of International Affairs provided additional support.
Assistant U.S. Attorneys Laura D. Withers and Stefanie A. Schwartz are representing the government in the matter.
The seizure of Virtualine.net disrupts a hosting service that authorities allege provided infrastructure and financial services to support criminal activity. The case also highlights the role of international law enforcement cooperation in targeting providers accused of enabling cybercrime across multiple jurisdictions.

Ray ID: 8f3a2c1b9d4e5f6a · Performance & security by Cloudflare
site-verification-ok