



















• Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
The Cyber Express
  • MagazineDownload
  • Firewall Daily
    • All
    • Bug Bounty & Rewards
    • Dark Web News
    • Data Breach News
    • Hacker News
    • Ransomware News
    • Vulnerabilities
    CVE-2026-114938

    Java4Shell Flaw Opens Major Java Applications to RCE Attacks

    8-Digits Team ransomware

    Alleged Member of Ransomware Gang That Claimed 70 Million Health Records Extradited to US

    AI Threat Tracker

    Google Finds Hackers Using AI Agents to Automate Cyberattacks

    OpenAI lawsuit

    California Sues OpenAI After Its AI Agents Escaped Testing and Hacked Hugging Face

    Luxor cyberattack

    Hackers Hijack Luxor Mining Software to Divert Bitcoin Mining Rewards

    Coles cyberattack

    Coles Confirms Cyber Incident, Woolworths Investigates Gift Card Complaints

    Jensen Huang resigns

    Jensen Huang Exits Nvidia Days After the Board Said It Backed Him

    FaceStealer

    US Disrupts North Korea’s FaceStealer Campaign, Targets $1.2 Billion in Stolen Crypto

    SignDrop zero-day exploit

    New SignDrop Exploit Claims SYSTEM Access on Windows Through CLFS

    Trending Tags

    • blackbyte ransomware
    • Ransomware
    • lapsus$ ransomware
    • Apple
    • Apple vulnerability
  • Essentials
    • All
    • Compliance
    • Governance
    • Policy Updates
    • Regulations
    SEC, Misleading Cyber Disclosures, Financial data, financial data protection, SEC

    SEC Enforcement Fell 24% in Fiscal 2026

    ASD Essentials

    The Essential Eight Is Being Replaced: What Australian Organisations Need to Know

    SICW 2026

    AI Is Now Fighting on Both Sides of the Cyber War, Singapore Warns

    Morocco cybersecurity strategy

    Morocco Flags AI Threats, Prioritizes Critical Infrastructure Defense

    European Police Chiefs Convention 2026

    Europe’s Police Chiefs Face Growing Threat of AI-Driven Crime

    AI service security

    Hackers Are Stealing AI Keys. The Cost Can Reach $600,000

    AI security risks

    Sam Altman at UN Security Council: 6 AI Security Risks the World Cannot Ignore

    AI-enabled cyber attacks

    AI Gives Hackers an Edge Defenders Still Can’t Match, NCSC Warns

    Fraudulent SIM cards

    India’s DoT Warns Citizens Over SIM Fraud and IMEI Tampering

    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
    • All
    • How to
    • What is
    Infostealer Intelligence

    The 2026 Infostealer Intelligence Shortlist: Top 10 Vendors Security Teams Should Know

    Google Chrome

    How to Remove Saved Passwords From Google Chrome (And Why You Should)

    DPDP Rules, Cyble, DPDP Act, Cyble Vantage

    How Cyble’s Front-Row Vantage Can Help You in Complying to India’s DPDP Act

    Cybersecurity Countries

    The Top 8 Countries Leading the Cyber Defense Race in 2025

    link building

    The Link Building Secrets Your Competitors Don’t Want You to Know

    Supply Chain Attack

    Supply Chain Resilience and Physical Security: Lessons for 2025

    Healthcare cybersecurity trends of 2024

    Healthcare Cybersecurity: 2024 Was Tough, 2025 May Be Better

    CEO's Guide to Take-Down Services

    Shield Your Organization: CEO’s Perspective on Take-Down Services

    Azure sign-in Microsoft

    Microsoft Announces Mandatory MFA for Azure Sign-ins to Bolster Cloud Defenses

  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • All
    • Appointments
    • Budgets
    • Mergers & Aquisitions
    • Partnerships
    • Press Release
    • Startups
    Kerala Police Signs MoU With Cyble

    Kerala Police Signs MoU With Cyble to Use Threat Intelligence in Cybercrime Probes

    Gemini 4 Argon

    Gemini 4 Argon Restricted Over Cybersecurity Misuse Risks

    weekly roundup September 18 2026

    The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

    threat intelligence

    Cyble, UAE Cyber Security Council Unite Against Rising Cyber Threats

    Ukraine cybersecurity

    Zelensky Appoints Ihor Klymenko to Lead Ukraine’s Cybersecurity Center

    UK cyberattack rate

    UK Small Firms Bear Brunt of Rising Cyberattacks, Hiscox Finds

    Cyber Yodha Campaign

    Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

    UK Ukraine AI partnership

    Britain Gains Access to Ukraine’s ‘Goldmine’ of Battlefield AI Data

    Hims & Hers lawsuit

    FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices

    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
No Result
View All Result
  • MagazineDownload
  • Firewall Daily
    • All
    • Bug Bounty & Rewards
    • Dark Web News
    • Data Breach News
    • Hacker News
    • Ransomware News
    • Vulnerabilities
    CVE-2026-114938

    Java4Shell Flaw Opens Major Java Applications to RCE Attacks

    8-Digits Team ransomware

    Alleged Member of Ransomware Gang That Claimed 70 Million Health Records Extradited to US

    AI Threat Tracker

    Google Finds Hackers Using AI Agents to Automate Cyberattacks

    OpenAI lawsuit

    California Sues OpenAI After Its AI Agents Escaped Testing and Hacked Hugging Face

    Luxor cyberattack

    Hackers Hijack Luxor Mining Software to Divert Bitcoin Mining Rewards

    Coles cyberattack

    Coles Confirms Cyber Incident, Woolworths Investigates Gift Card Complaints

    Jensen Huang resigns

    Jensen Huang Exits Nvidia Days After the Board Said It Backed Him

    FaceStealer

    US Disrupts North Korea’s FaceStealer Campaign, Targets $1.2 Billion in Stolen Crypto

    SignDrop zero-day exploit

    New SignDrop Exploit Claims SYSTEM Access on Windows Through CLFS

    Trending Tags

    • blackbyte ransomware
    • Ransomware
    • lapsus$ ransomware
    • Apple
    • Apple vulnerability
  • Essentials
    • All
    • Compliance
    • Governance
    • Policy Updates
    • Regulations
    SEC, Misleading Cyber Disclosures, Financial data, financial data protection, SEC

    SEC Enforcement Fell 24% in Fiscal 2026

    ASD Essentials

    The Essential Eight Is Being Replaced: What Australian Organisations Need to Know

    SICW 2026

    AI Is Now Fighting on Both Sides of the Cyber War, Singapore Warns

    Morocco cybersecurity strategy

    Morocco Flags AI Threats, Prioritizes Critical Infrastructure Defense

    European Police Chiefs Convention 2026

    Europe’s Police Chiefs Face Growing Threat of AI-Driven Crime

    AI service security

    Hackers Are Stealing AI Keys. The Cost Can Reach $600,000

    AI security risks

    Sam Altman at UN Security Council: 6 AI Security Risks the World Cannot Ignore

    AI-enabled cyber attacks

    AI Gives Hackers an Edge Defenders Still Can’t Match, NCSC Warns

    Fraudulent SIM cards

    India’s DoT Warns Citizens Over SIM Fraud and IMEI Tampering

    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
    • All
    • How to
    • What is
    Infostealer Intelligence

    The 2026 Infostealer Intelligence Shortlist: Top 10 Vendors Security Teams Should Know

    Google Chrome

    How to Remove Saved Passwords From Google Chrome (And Why You Should)

    DPDP Rules, Cyble, DPDP Act, Cyble Vantage

    How Cyble’s Front-Row Vantage Can Help You in Complying to India’s DPDP Act

    Cybersecurity Countries

    The Top 8 Countries Leading the Cyber Defense Race in 2025

    link building

    The Link Building Secrets Your Competitors Don’t Want You to Know

    Supply Chain Attack

    Supply Chain Resilience and Physical Security: Lessons for 2025

    Healthcare cybersecurity trends of 2024

    Healthcare Cybersecurity: 2024 Was Tough, 2025 May Be Better

    CEO's Guide to Take-Down Services

    Shield Your Organization: CEO’s Perspective on Take-Down Services

    Azure sign-in Microsoft

    Microsoft Announces Mandatory MFA for Azure Sign-ins to Bolster Cloud Defenses

  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • All
    • Appointments
    • Budgets
    • Mergers & Aquisitions
    • Partnerships
    • Press Release
    • Startups
    Kerala Police Signs MoU With Cyble

    Kerala Police Signs MoU With Cyble to Use Threat Intelligence in Cybercrime Probes

    Gemini 4 Argon

    Gemini 4 Argon Restricted Over Cybersecurity Misuse Risks

    weekly roundup September 18 2026

    The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

    threat intelligence

    Cyble, UAE Cyber Security Council Unite Against Rising Cyber Threats

    Ukraine cybersecurity

    Zelensky Appoints Ihor Klymenko to Lead Ukraine’s Cybersecurity Center

    UK cyberattack rate

    UK Small Firms Bear Brunt of Rising Cyberattacks, Hiscox Finds

    Cyber Yodha Campaign

    Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

    UK Ukraine AI partnership

    Britain Gains Access to Ukraine’s ‘Goldmine’ of Battlefield AI Data

    Hims & Hers lawsuit

    FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices

    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
No Result
View All Result
The Cyber Express
No Result
View All Result

New EU Vulnerability Platform GCVE Goes Live, Reducing Reliance on Global Systems

Ashish Khaitan by Ashish Khaitan
January 21, 2026
in Firewall Daily, Cyber News, Vulnerabilities
0
EU vulnerability database GCVE
585
SHARES
3.2k
VIEWS
Share on LinkedInShare on Twitter

Europe’s long-running conversation about digital autonomy quietly crossed a milestone with the launch of a new public vulnerability platform. The EU Vulnerability Database, created under the GCVE initiative, is now live. This signals a deliberate shift in how software weaknesses are identified, cataloged, and shared across Europe.  

The GCVE project, short for Global Cybersecurity Vulnerability Enumeration, has delivered a free, publicly accessible platform at db.gcve.eu. The primary objective of the platform is to reduce reliance on U.S.-centric vulnerability infrastructure and enhance Europe’s digital sovereignty.  

Why GCVE Emerged When It Did 

The immediate catalyst was a brief but impactful scare surrounding the possible discontinuation of the Common Vulnerabilities and Exposures (CVE) program in 2025. Even though the CVE system has long been treated as a foundational layer of global cybersecurity, the mere risk of interruption exposed how fragile that assumption really was.  

Across Europe, the incident prompted vendors, researchers, and policymakers to ask an uncomfortable question: what happens if the numbering system everyone depends on suddenly becomes unavailable or constrained? 

GCVE formed in response, not as a rejection of CVE, but as a hedge against single-point dependency. The EU vulnerability database is the practical outcome of that realization, offering an alternative that is structurally decentralized rather than centrally approved. 

A Decentralized Model by Design 

Unlike traditional models, where vulnerability identifiers are assigned through a central authority, GCVE operates using a Global Numbering Authority (GNA) framework. This allows participating organizations to assign and publish vulnerability identifiers autonomously. There is no waiting period for central approval and no bottleneck that can stall disclosure during critical response windows. 

The platform aggregates data from more than 25 distinct sources, including public vulnerability directories and GNA contributors. All incoming data is normalized, structured, and indexed, so it can be searched consistently across ecosystems.

In practical terms, this means a vulnerability disclosed through GitHub Security Advisories, a national CERT, or another recognized directory can coexist in a single EU vulnerability database without losing context or traceability. 

What the Database Actually Shows 

The Cyber Express team analyzed the platform and found that the GCVE dashboard reveals how broad that aggregation already is. Recent activity lists vulnerabilities from multiple origins, including GitHub advisories such as GHSA-QHWV-3XRQ-PJMJ, GHSA-M2W5-7XHV-W6FH, GHSA-X439-WRMP-CJ57, and dozens more. Alongside them appear traditional identifiers like CVE-2025-14559, CVE-2026-1035, and CVE-2026-24026 through CVE-2026-24020, pulled from cvelistv5 sources. 
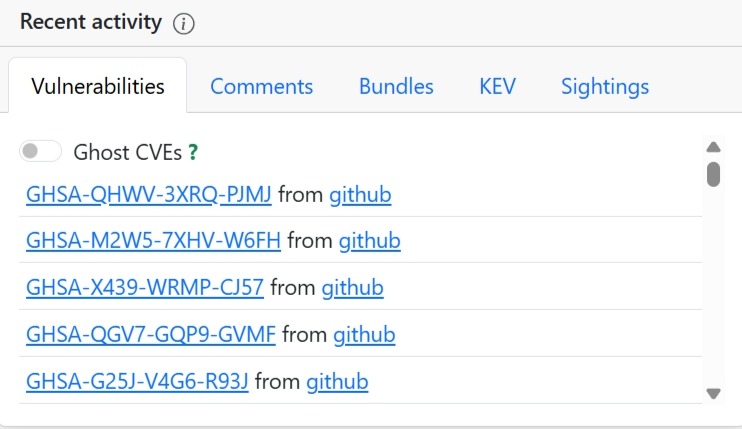
EU vulnerability database dashboard
EU vulnerability database dashboard (Source: GCVE)

The dashboard tracks more than identifiers. Weekly observations, comments, bundles, known exploited vulnerabilities (KEV), sightings, and even “ghost CVEs” are surfaced to show how issues evolve after disclosure. A rolling, month-long evolution view highlights how frequently vulnerabilities are seen, confirmed, exploited, or accompanied by proof-of-concept code. 

Concrete examples illustrate the breadth of historical and current coverage. Widely known issues like CVE-2021-44228 (Log4Shell), CVE-2019-19781, CVE-2018-13379, and CVE-2017-17215 appear alongside recent entries such as CVE-2025-14847, CVE-2025-55182, CVE-2025-68613, and CVE-2025-59374. Older vulnerabilities, CVE-2015-2051 or CVE-2017-18368, sit next to newly published 2026 identifiers, reinforcing that the EU vulnerability database is designed for continuity, not just novelty. 

Integration Over Isolation 

GCVE’s architects appear keenly aware that a database alone does not change behavior. To that end, the platform exposes an open API intended for direct integration into compliance tooling, risk management platforms, and security operations workflows.

This matters for Europe’s computer security incident response teams, software vendors, researchers, and open-source maintainers, who often juggle multiple data feeds just to maintain situational awareness. 

By consolidating vulnerability intelligence without enforcing a single authority, GCVE positions itself as connective tissue rather than a replacement organ. The model assumes coexistence with existing systems while ensuring Europe retains the ability to operate independently if needed. 
Share this:

  • Share on LinkedIn (Opens in new window) LinkedIn
  • Share on Reddit (Opens in new window) Reddit
  • Share on X (Opens in new window) X
  • Share on Facebook (Opens in new window) Facebook
  • More
  • Email a link to a friend (Opens in new window) Email
  • Share on WhatsApp (Opens in new window) WhatsApp

Related

Tags: EU vulnerability databaseEuropeGCVEThe Cyber ExpressThe Cyber Express News
Previous Post

Cyber Resilience in Healthcare: Lessons from 2025 and Priorities for 2026

Next Post

NCSC Warns of Rising Russian-Aligned Hacktivist Attacks on UK Organisations

Next Post
Russian-aligned hacktivist groups

NCSC Warns of Rising Russian-Aligned Hacktivist Attacks on UK Organisations

Q1 2026 Threat Reports

❮ ❯
Cyble-Vision


Follow Us On Google News

Categories

  • Privacy Statement
  • Terms of Use
  • Write For Us

© 2026 The Cyber Express - Cybersecurity News and Magazine.

Welcome Back!

Login to your account below

Forgotten Password?

Retrieve your password

Please enter your username or email address to reset your password.

Log In

Add New Playlist

No Result
View All Result
  • Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board

© 2026 The Cyber Express - Cybersecurity News and Magazine.

-
00:00
00:00

Queue

Update Required Flash plugin
-
00:00
00:00



