• About Us
  • Contact Us
  • Editorial Calendar
  • Careers
  • The Cyber Express by Cyble Vulnerability Disclosure Policy
  • Cyble Trust Portal
The Cyber Express
  • MagazineDownload
  • Firewall Daily
    • All
    • Bug Bounty & Rewards
    • Dark Web News
    • Data Breach News
    • Hacker News
    • Ransomware News
    • Vulnerabilities
    weekly roundup September 18 2026

    The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

    Contagious Interview, WaterPlum, North Korea

    Four Countries Attribute “Contagious Interview” Fake-Job Malware Campaign to North Korea’s WaterPlum

    CVE-2026-76460

    Cisco ISE Vulnerability With CVSS 10.0 Score Under Active Attack

    Thinkng Bull Cyberattack

    South Korea Math Academy Hit by Cyberattack, Student Data at Risk

    Iranian cyber actors

    Fake Apps, Real Spies: How Iran Tracks Dissidents Through Telegram

    EU KIDS Act

    Children Under 13 Could Be Barred From Social Media Under New EU Plan

    threat intelligence

    Cyble, UAE Cyber Security Council Unite Against Rising Cyber Threats

    CVE-2026-90894

    New Parallels Desktop Flaw Lets Local Users Seize Root Control of Macs

    GUARD Act

    US House Passes Bill to Help Police Track Down Scammers Targeting Seniors

    Trending Tags

    • blackbyte ransomware
    • Ransomware
    • lapsus$ ransomware
    • Apple
    • Apple vulnerability
  • Essentials
    • All
    • Compliance
    • Governance
    • Policy Updates
    • Regulations
    EU KIDS Act

    Children Under 13 Could Be Barred From Social Media Under New EU Plan

    GUARD Act

    US House Passes Bill to Help Police Track Down Scammers Targeting Seniors

    Emergency Security Protocol

    EU Plans ‘Article 4’-Style Security Protocol for Cyberattacks and Hybrid Threats

    Cyber Resilience Act, CRA, EU, EU Sanctions, Iran, Chinese Hacking,

    EU’s 24-Hr Vulnerability Reporting Rules Take Effect Friday, a Year Before the Rest of the Cyber Resilience Act

    outage communications

    CISA, FBI Urge Clearer Communication During Major Outages

    A session cookie depicted as a key being stolen from a browser window while a two-factor authentication prompt sits bypassed, illustrating Claude session hijacking by infostealer malware.

    Anthropic Warns Commodity Infostealers Are Hijacking Claude Sessions to Drain Paid Usage

    Social Media Ban

    New Zealand Moves to Ban Social Media for Under-16s

    Prompt Injection, Grok, Grok AI, Gemini, Fraud, Agentic AI, AI-assisted Cyberattacks

    Encrypted Prompts Defeat Grok and Gemini Guardrails; Chat Histories Stolen

    India online safety rules

    India Tightens Social Media Rules to Protect Children Online

    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
    • All
    • How to
    • What is
    Google Chrome

    How to Remove Saved Passwords From Google Chrome (And Why You Should)

    DPDP Rules, Cyble, DPDP Act, Cyble Vantage

    How Cyble’s Front-Row Vantage Can Help You in Complying to India’s DPDP Act

    Cybersecurity Countries

    The Top 8 Countries Leading the Cyber Defense Race in 2025

    link building

    The Link Building Secrets Your Competitors Don’t Want You to Know

    Supply Chain Attack

    Supply Chain Resilience and Physical Security: Lessons for 2025

    Healthcare cybersecurity trends of 2024

    Healthcare Cybersecurity: 2024 Was Tough, 2025 May Be Better

    CEO's Guide to Take-Down Services

    Shield Your Organization: CEO’s Perspective on Take-Down Services

    Azure sign-in Microsoft

    Microsoft Announces Mandatory MFA for Azure Sign-ins to Bolster Cloud Defenses

    Signal Proxy, Signal, Signal Ban in Russia, Signal Ban in Venezuela, Bypass Signal Ban, How to Activate Signal Proxy, Signal Proxy Server

    How to Set Up Signal Proxy to Help Bypass Censorship in Russia and Venezuela

  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • All
    • Appointments
    • Budgets
    • Mergers & Aquisitions
    • Partnerships
    • Press Release
    • Startups
    weekly roundup September 18 2026

    The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

    threat intelligence

    Cyble, UAE Cyber Security Council Unite Against Rising Cyber Threats

    Ukraine cybersecurity

    Zelensky Appoints Ihor Klymenko to Lead Ukraine’s Cybersecurity Center

    UK cyberattack rate

    UK Small Firms Bear Brunt of Rising Cyberattacks, Hiscox Finds

    Cyber Yodha Campaign

    Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

    UK Ukraine AI partnership

    Britain Gains Access to Ukraine’s ‘Goldmine’ of Battlefield AI Data

    Hims & Hers lawsuit

    FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices

    Australia-India PACTS

    Australia-India PACTS to Deepen Cybersecurity and Tech Collaboration

    Sunil Varkey

    Sunil Varkey Joins Hexaware Technologies as EVP & CISO

    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
No Result
View All Result
  • MagazineDownload
  • Firewall Daily
    • All
    • Bug Bounty & Rewards
    • Dark Web News
    • Data Breach News
    • Hacker News
    • Ransomware News
    • Vulnerabilities
    weekly roundup September 18 2026

    The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

    Contagious Interview, WaterPlum, North Korea

    Four Countries Attribute “Contagious Interview” Fake-Job Malware Campaign to North Korea’s WaterPlum

    CVE-2026-76460

    Cisco ISE Vulnerability With CVSS 10.0 Score Under Active Attack

    Thinkng Bull Cyberattack

    South Korea Math Academy Hit by Cyberattack, Student Data at Risk

    Iranian cyber actors

    Fake Apps, Real Spies: How Iran Tracks Dissidents Through Telegram

    EU KIDS Act

    Children Under 13 Could Be Barred From Social Media Under New EU Plan

    threat intelligence

    Cyble, UAE Cyber Security Council Unite Against Rising Cyber Threats

    CVE-2026-90894

    New Parallels Desktop Flaw Lets Local Users Seize Root Control of Macs

    GUARD Act

    US House Passes Bill to Help Police Track Down Scammers Targeting Seniors

    Trending Tags

    • blackbyte ransomware
    • Ransomware
    • lapsus$ ransomware
    • Apple
    • Apple vulnerability
  • Essentials
    • All
    • Compliance
    • Governance
    • Policy Updates
    • Regulations
    EU KIDS Act

    Children Under 13 Could Be Barred From Social Media Under New EU Plan

    GUARD Act

    US House Passes Bill to Help Police Track Down Scammers Targeting Seniors

    Emergency Security Protocol

    EU Plans ‘Article 4’-Style Security Protocol for Cyberattacks and Hybrid Threats

    Cyber Resilience Act, CRA, EU, EU Sanctions, Iran, Chinese Hacking,

    EU’s 24-Hr Vulnerability Reporting Rules Take Effect Friday, a Year Before the Rest of the Cyber Resilience Act

    outage communications

    CISA, FBI Urge Clearer Communication During Major Outages

    A session cookie depicted as a key being stolen from a browser window while a two-factor authentication prompt sits bypassed, illustrating Claude session hijacking by infostealer malware.

    Anthropic Warns Commodity Infostealers Are Hijacking Claude Sessions to Drain Paid Usage

    Social Media Ban

    New Zealand Moves to Ban Social Media for Under-16s

    Prompt Injection, Grok, Grok AI, Gemini, Fraud, Agentic AI, AI-assisted Cyberattacks

    Encrypted Prompts Defeat Grok and Gemini Guardrails; Chat Histories Stolen

    India online safety rules

    India Tightens Social Media Rules to Protect Children Online

    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
    • All
    • How to
    • What is
    Google Chrome

    How to Remove Saved Passwords From Google Chrome (And Why You Should)

    DPDP Rules, Cyble, DPDP Act, Cyble Vantage

    How Cyble’s Front-Row Vantage Can Help You in Complying to India’s DPDP Act

    Cybersecurity Countries

    The Top 8 Countries Leading the Cyber Defense Race in 2025

    link building

    The Link Building Secrets Your Competitors Don’t Want You to Know

    Supply Chain Attack

    Supply Chain Resilience and Physical Security: Lessons for 2025

    Healthcare cybersecurity trends of 2024

    Healthcare Cybersecurity: 2024 Was Tough, 2025 May Be Better

    CEO's Guide to Take-Down Services

    Shield Your Organization: CEO’s Perspective on Take-Down Services

    Azure sign-in Microsoft

    Microsoft Announces Mandatory MFA for Azure Sign-ins to Bolster Cloud Defenses

    Signal Proxy, Signal, Signal Ban in Russia, Signal Ban in Venezuela, Bypass Signal Ban, How to Activate Signal Proxy, Signal Proxy Server

    How to Set Up Signal Proxy to Help Bypass Censorship in Russia and Venezuela

  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • All
    • Appointments
    • Budgets
    • Mergers & Aquisitions
    • Partnerships
    • Press Release
    • Startups
    weekly roundup September 18 2026

    The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

    threat intelligence

    Cyble, UAE Cyber Security Council Unite Against Rising Cyber Threats

    Ukraine cybersecurity

    Zelensky Appoints Ihor Klymenko to Lead Ukraine’s Cybersecurity Center

    UK cyberattack rate

    UK Small Firms Bear Brunt of Rising Cyberattacks, Hiscox Finds

    Cyber Yodha Campaign

    Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

    UK Ukraine AI partnership

    Britain Gains Access to Ukraine’s ‘Goldmine’ of Battlefield AI Data

    Hims & Hers lawsuit

    FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices

    Australia-India PACTS

    Australia-India PACTS to Deepen Cybersecurity and Tech Collaboration

    Sunil Varkey

    Sunil Varkey Joins Hexaware Technologies as EVP & CISO

    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board
No Result
View All Result
The Cyber Express
No Result
View All Result
Home Cyber News

Alphv/BlackCat SEC Complaint: A Desperate Move, Pressure Tactic, or Exploiting Regulations?

This act compels us to examine the motivations and evolving strategies of cybercriminal groups in their relentless pursuit of illicit gains.

Avantika by Avantika
July 9, 2025
in Cyber News, Firewall Daily
0
BlackCat ransomware group
650
SHARES
3.6k
VIEWS
Share on LinkedInShare on Twitter

Filing a complaint with The U.S. Securities and Exchange Commission (SEC) in the event of a company’s non-disclosure of a cyberattack is primarily rooted in the principles of transparency, investor protection, and maintaining the integrity of the financial markets. However, what could it mean when a hacker group decides to meticulously fill out the SEC complaint form and post it on their leak site?

In a strikingly unconventional tactic, the infamous Alphv/BlackCat ransomware group filed a complaint with the U.S. Securities and Exchange Commission (SEC), accusing one of their claimed victims, MeridianLink, a California-based provider of digital lending and data verification solutions, of not adhering to a four-day rule for disclosing a cyberattack—a rule not yet in effect.

This move, a far cry from their usual modus operandi of covert operations and ransom demands, begs the question: What drives a hacker group to engage with a regulatory body traditionally allied with investors and market integrity?

At first glance, it may appear as an ironic twist – cybercriminals assuming the role of regulatory watchdogs. But a deeper analysis suggests a possible strategic ploy, a sign of desperation or an innovative tactic to amplify pressure for ransom.

This act, which witnessed a new form of exerting pressure and extortion by manipulating regulations designed for protection, compels us to examine the motivations and evolving strategies of cybercriminal groups in their relentless pursuit of illicit gains.

On November 7, 2023, BlackCat/APLHV claimed to breach the network of MeridianLink and extracted sensitive data. Following the MeridianLink data breach, the hacker collective demanded a ransom, setting a 24-hour deadline for payment to prevent the release of the stolen information.
blackcat sec
The message posted by BlackCat ransomware group after claiming a cyberattack on MeridianLink. (Source: FalconFeeds/Twitter)

Although initial communications were established, BlackCat/APLHV claims that MeridianLink has since failed to engage in further dialogue to negotiate the terms for the data’s security.

The company’s apparent silence on negotiation may have driven the hacker group to file a complaint with the SEC.

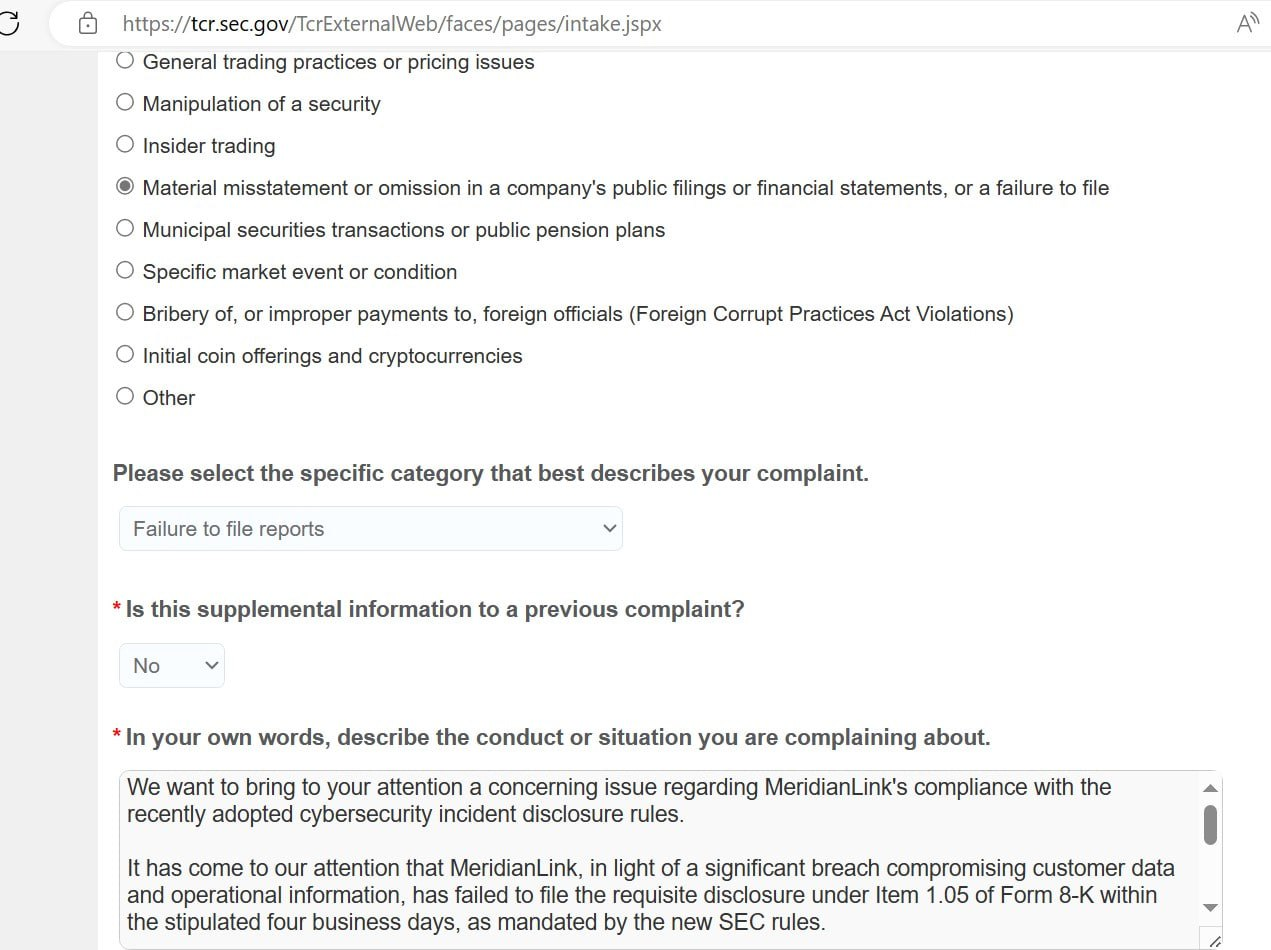
In the form they submitted, the hacker group highlighted, “We want to bring to your attention a concerning issue regarding MeridianLink’s compliance with the recently adopted cybersecurity incident disclosure rules.

“It has come to our attention that MeridianLink, in light of a significant breach compromising customer data and operational information, has failed to file the requisite disclosure under Item 1.05 of Form 8-K within the stipulated four business days, as mandated by the new SEC rules,” they wrote further.

The statement “failed to file the requisite disclosure under Item 1.05 of Form 8-K within the stipulated four business days, as mandated by the new SEC rules” refers to an accusation that a company, in this case, MeridianLink, did not comply with a specific reporting requirement set forth by the U.S. Securities and Exchange Commission (SEC).
sec blackcat
The SEC complaint filed by BlackCat against MeridianLink. (Source: @vxunderground/Twitter)

Soon after, MeridianLink confirmed the cyberattack. A spokesperson from MeridianLink shared with The Cyber Express details about the cybersecurity incident, stating, “MeridianLink recently identified a cybersecurity incident.”

They continued, stating, “Based on our investigation to date, we have identified no evidence of unauthorized access to our production platforms, and the incident has caused minimal business interruption. If we determine that any consumer personal information was involved in this incident, we will provide notifications, as required by law.”

Form 8-K serves as a formal notification mechanism for informing shareholders of U.S. publicly traded companies and the Securities and Exchange Commission about certain events that could be significant to stakeholders or may require regulatory attention.

The SEC approved the final rules on cybersecurity, risk management, strategy, governance, and incident disclosure on July 26, 2023. These enhanced cybersecurity disclosure regulations officially came into effect on September 5, 2023, referred to as the “Final Rules.”  

“With respect to compliance with the incident disclosure requirements in Item 1.05 of Form 8-K and in Form 6-K, all registrants other than smaller reporting companies must begin complying on December 18, 2023. As discussed above, smaller reporting companies are being given an additional 180 days from the non-smaller reporting company compliance date before they must begin complying with Item 1.05 of Form 8-K, on June 15, 2024,” stated the official report.

According to the report, starting December 18, 2023, all registrants—excluding smaller reporting companies—are obliged to follow the incident disclosure regulations.

This indicates that impacted companies have until December to comply with the newly established rules for reporting cybersecurity incidents. Several cybersecurity experts, who took to social media following the abrupt reaction by Alphv/BlackCat ransomware group, pointed this out.

“ALPHV claims the breach was November 7 MeridianLink says November 10. The amended SEC requirement says *material* incidents must be reported four business days after determining the incident is material. Compliance isn’t required until December 18th anyway,” tweeted Steve Werby, an information security strategist with 20 years of experience.

In conversation with The Cyber Express, Steve Werby shared his interpretation of the BlackCat hacker group’s stunt. He believes that the group’s decision to file a complaint with the SEC may not have been expected to change MeridianLink’s stance on the ransom but rather serves as a stark warning to future targets of the group, indicating that paying the ransom might be their sole escape from being publicly named and facing regulatory consequences.

Werby stated, “Since BlackCat’s threat of leaking the exfiltrated data didn’t result in a willingness to pay the requested ransom, it’s unlikely that they thought the SEC complaint would alter MeridianLink’s decision. It’s likely that the action was intended to signal to future BlackCat victims that ransom payment is the right choice. Perhaps with a dash of vengeance.”

Interestingly, the move to report “non-compliance” could backfire significantly.

A Cyber Threat Researcher from the cybersecurity and threat intelligence firm Cyble shared a perspective on the BlackCat ransomware group’s recent SEC filing. The researcher emphasized that this act is actually a display of boldness and a form of blackmail.

The researcher elaborated, “It’s not desperation, but rather flaunting and blackmail. The gangs see themselves as somebody who calls all the shots, and the victims have to submit to their demands.”

Further, they highlighted a potential unintended consequence of this tactic. “By reporting to the SEC, they might inadvertently prompt the government to implement stricter regulations. This could make it harder to pay ransoms, essentially undermining the primary motivation of ransomware gangs – getting paid.”

“This move is likely to backfire on them. It’s a positive development for the victims, as increased regulation will make the operations of ransomware groups more challenging,” they concluded.

Another viewpoint suggests that the hackers’ actions represent an attempt to manipulate the SEC’s cybersecurity regulations to their advantage.

Jamil Farshchi, EVP and Chief Information Security Officer (CISO) at Equifax, interprets this move as an aggressive tactic following unsuccessful ransom negotiations. By leveraging the SEC’s rules, which require companies to disclose significant cyber incidents, the hackers aim to exert additional pressure on their targets.

Farshchi explained, “It’s almost certainly a retaliatory response after not receiving a ransom.”

This statement indicates that the filing with the SEC could be a direct consequence of the ransomware group’s frustration over unmet demands.

He further added, “They are trying to weaponize the SEC cyber rules to incentivize future victims to pay the ransom.”

This tactic involves exploiting the regulatory requirements as a tool of coercion, pushing companies to pay ransoms to avoid the ramifications of public disclosure and potential regulatory scrutiny. Such a strategy could significantly impact companies, forcing them to weigh the risks of non-compliance with SEC rules against the consequences of yielding to the hackers’ demands.

BlackCat’s decision to file a complaint and publicly put it out also seems like a calculated strategy to instil fear among senior executives of companies, as pointed out by Greg Linares, a cybersecurity expert and white hat hacker.

“I definitely see it as a leverage tactic to induce fear among C-levels,” Linares told The Cyber Express.

He suggests that this tactic might have been chosen based on a vulnerability identified during the negotiation process with the victim company.

Expanding on the impact of this move, he added, “We don’t know why they potentially did this tactic, maybe it was based on a weakness discovered during negotiations, however I do know CISOs definitely took notice.”

Linares noted the significant attention the incident garnered on social media, predicting its potential influence on similar groups. “And with as much attention it received on social media, it likely will be replicated by other ransomware groups elsewhere in the near future.”

Discussing the implications for corporate cybersecurity strategies, Linares advised, “I think everyone should review their material reporting process, ransomware response, and tabletop exercises involving this plus other additional avenues of extortion.”

A dark web researcher at Cyble offered further insights into BlackCat’s strategy, describing it as a high-pressure tactic. According to the researcher, this move isn’t just about coercion; it’s also a calculated play for legitimacy.

“This seems to be a desperate attempt to pressure the victim into compliance,” they said.

Further, the researcher speculated on the group’s expectations: “It appears they hoped that the mere mention of an SEC notification would cause panic and prompt a swift response and possibly a quick settlement from the victim.”

Deciphering BlackCat’s Motives

The BlackCat ransomware group’s decision to file a complaint with the SEC represents a significant departure from traditional ransomware tactics, as conventional methods may meet increasing resistance.

One possible interpretation of BlackCat’s actions is that companies are becoming more resilient and less willing to agree to ransom demands. This shift could be a result of enhanced cybersecurity measures, better awareness, or the realization that paying the ransom offers no guarantee against data exposure. Companies are increasingly aware of the unreliability of hackers.

The realization that paying the ransom doesn’t necessarily safeguard against data exposure or future attacks, has left many companies in a dilemma. Faced with this new resilience, ransomware groups like BlackCat might be exploring more desperate and innovative tactics to exert pressure and secure payment.

The move also reflects the complications introduced by tighter regulations in cybersecurity. The requirement for companies to disclose cyberattacks to regulatory bodies like the SEC adds a new layer to the ransomware game. BlackCat’s decision to exploit these regulations indicates their awareness of the legal and reputational pressures that can be used as leverage against their targets.

Despite the uncertainty of securing a ransom, BlackCat’s approach has undoubtedly achieved the desired attention. This publicity, while not directly lucrative, enhances their notoriety and may serve as a warning to future targets.

In conclusion, BlackCat’s unusual tactic of engaging with the SEC is a move that speaks volumes about the current state of cybercrime. It suggests possible desperation on the part of hackers facing stiffer corporate resistance and complex regulatory landscapes. It also reflects an understanding that the promise of ransom payment is becoming increasingly unreliable.

Share this:

  • Share on LinkedIn (Opens in new window) LinkedIn
  • Share on Reddit (Opens in new window) Reddit
  • Share on X (Opens in new window) X
  • Share on Facebook (Opens in new window) Facebook
  • More
  • Email a link to a friend (Opens in new window) Email
  • Share on WhatsApp (Opens in new window) WhatsApp

Related

Tags: Alphv/BlackCat SEC ComplaintBlackCat ransomware groupcybersecurity newsSEC ComplaintThe Cyber ExpressThe Cyber Express News
Previous Post

Digital Dangers in Medicine: Hackers’ Terrifying Obsession with the Healthcare Industry

Next Post

5 Best Practices for Implementing Firewalls in Industrial Control Systems

Next Post
ics industrial control system

5 Best Practices for Implementing Firewalls in Industrial Control Systems

Q1 2026 Threat Reports

❮ ❯
Cyble-Vision


Follow Us On Google News

Latest Cyber News

weekly roundup September 18 2026
Firewall Daily

The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

September 18, 2026
Contagious Interview, WaterPlum, North Korea
Cyber News

Four Countries Attribute “Contagious Interview” Fake-Job Malware Campaign to North Korea’s WaterPlum

September 18, 2026
CVE-2026-76460
Firewall Daily

Cisco ISE Vulnerability With CVSS 10.0 Score Under Active Attack

September 18, 2026
Thinkng Bull Cyberattack
Firewall Daily

South Korea Math Academy Hit by Cyberattack, Student Data at Risk

September 18, 2026

Categories

Web Stories

Do This on Telegram, Your Bank Account Will Become Zero
If You Install the iOS 18 Beta, Your iPhone Could Be Hacked
Cricket World Cup Ticketing Systems Under Cybersecurity
Cyber Threats and Online Ticket Scams During the NBA Finals
Biometric Data Security: Protecting Sensitive Information

About

The Cyber Express

#1 Trending Cybersecurity News and Magazine

The Cyber Express is a handbook for all stakeholders of the internet that provides information security professionals with the latest news, updates and knowledge they need to combat cyber threats.


Contact

For editorial queries: [email protected]

For marketing and Sales: [email protected]


Quick Links

  • About Us
  • Contact Us
  • Editorial Calendar
  • Careers
  • The Cyber Express by Cyble Vulnerability Disclosure Policy
  • Cyble Trust Portal

Our Address

We’re remote friendly, with office locations around the world:

San Francisco, Atlanta, Rome,
Dubai, Mumbai, Bangalore, Hyderabad,  Singapore, Jakarta, Sydney, and Melbourne


Headquarters:

The Cyber Express LLC
10080 North Wolfe Road, Suite SW3-200, Cupertino, CA, US 95014


India Office:

Cyber Express Media Network
HD-021, 4th Floor, C Wing, Building No.4. Nesco IT Park, WE Highway, Goregaon East, Mumbai, Maharashtra, India – 4000063

  • Privacy Statement
  • Terms of Use
  • Write For Us

© 2026 The Cyber Express - Cybersecurity News and Magazine.

Welcome Back!

Login to your account below

Forgotten Password?

Retrieve your password

Please enter your username or email address to reset your password.

Log In

Add New Playlist

No Result
View All Result
  • Magazine
  • Firewall Daily
  • Essentials
    • Regulations
    • Compliance
    • Governance
    • Policy Updates
  • Knowledge Hub
  • Features
    • Cyber Warfare
    • Espionage
    • Workforce
      • Learning & Development
  • Business
    • Startups
    • Mergers & Aquisitions
    • Partnerships
    • Appointments
    • Budgets
    • Research
      • Whitepapers
      • Sponsored Content
      • Market Reports
    • Interviews
      • Podcast
  • Events
    • Conference
    • Webinar
    • Endorsed Events
  • Advisory Board

© 2026 The Cyber Express - Cybersecurity News and Magazine.

Are you sure want to unlock this post?
Unlock left : 0
Are you sure want to cancel subscription?
-
00:00
00:00

Queue

Update Required Flash plugin
-
00:00
00:00
Do This on Telegram, Your Bank Account Will Become Zero If You Install the iOS 18 Beta, Your iPhone Could Be Hacked Cricket World Cup Ticketing Systems Under Cybersecurity Cyber Threats and Online Ticket Scams During the NBA Finals Biometric Data Security: Protecting Sensitive Information