






























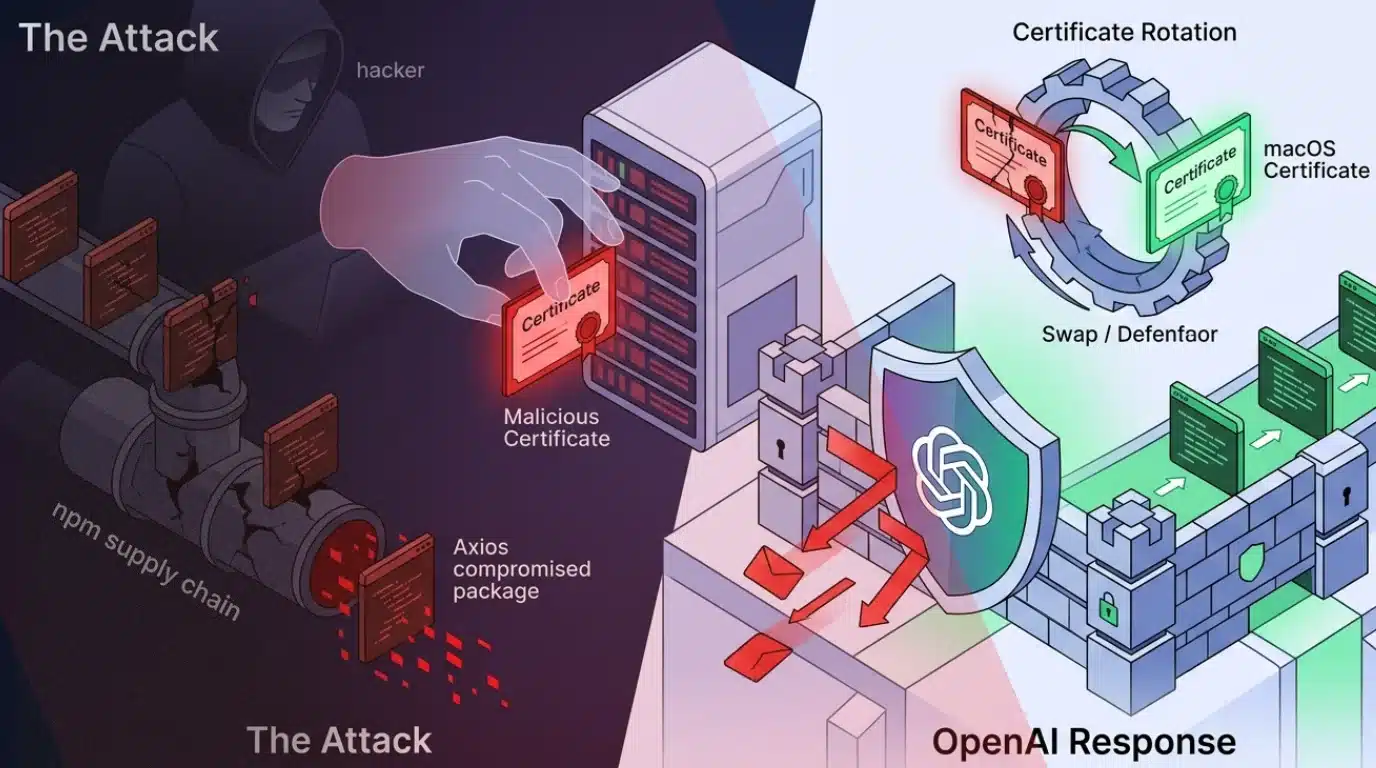
OpenAI Responds to Axios npm Supply Chain Attack, Rotates macOS Certificates
The company confirmed that no malicious applications signed with its certificate have been identified so far.

The company confirmed that no malicious applications signed with its certificate have been identified so far.
On Monday, the Axios npm supply chain attack came to light where malicious packages had been inserted into one of ...

Trust Wallet users had $8.5 million in crypto assets stolen in a cyberattack linked to the second wave of the ...

A new Shai-Hulud supply chain attack has hit nearly 500 npm packages with a total of 132 million monthly downloads. ...

More than 20 CrowdStrike NPM packages were among nearly 200 NPM packages hit by a sophisticated supply chain attack. The ...

A massive NPM supply chain attack that hit about 10% of all cloud environments yielded little for the hackers who ...

Supply chain attacks burst into consciousness with the SolarWinds and Kaseya breaches of 2020-2021, and if anything, risk has increased ...

As Versa Director is used by ISPs and MSPs, any exposed vulnerability could lead to a supply chain attack.

A medium severity vulnerability with a few dozen exposures can lead to great damage when nation-state actors target ISPs and ...

The injected malware's primary function involves attempting to create unauthorized administrative user accounts on affected websites.





